Cask Audit 2
CertiK reviewed Cask (Cask Audit 2) on 18 Dec 2022: 17 findings, 0 critical; 4 marked fixed, 13 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings17
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 9 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 4 | 0 | 4 |
HighCentralization Risks in CaskChainlinkTopup.solOpen
In the contract `CaskChainlinkTopup` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 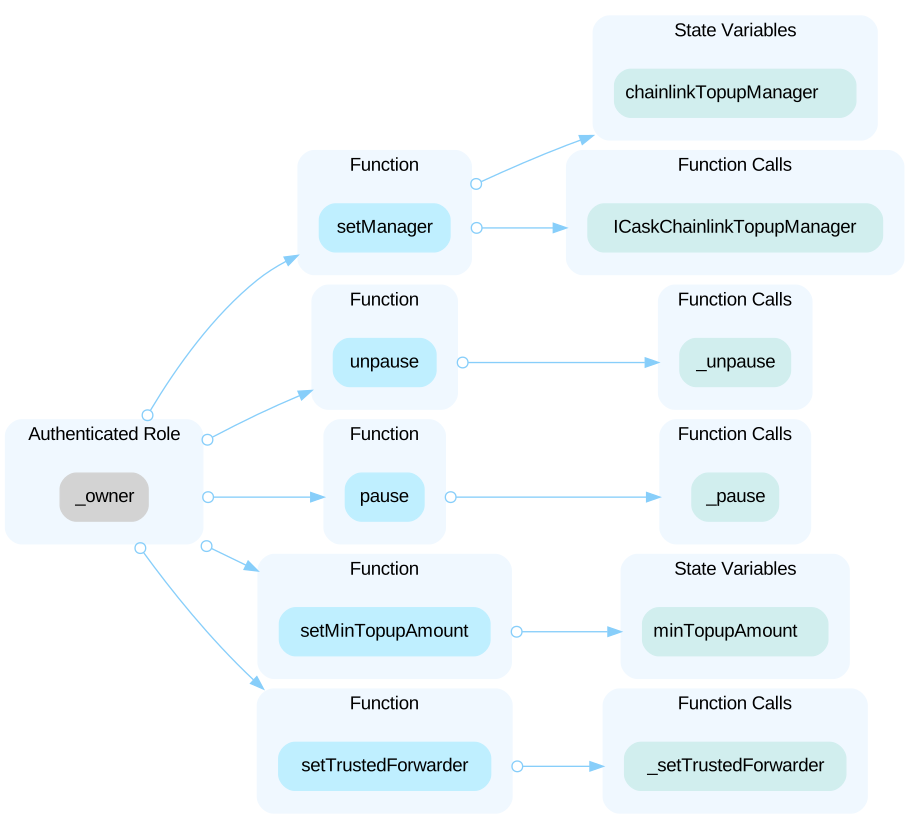
HighCentralization Risks in CaskChainlinkTopupManagerOpen
In the contract `CaskChainlinkTopupManager` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and allow/disallow registries, withdraw any token from contract, and set important parameters and addresses. 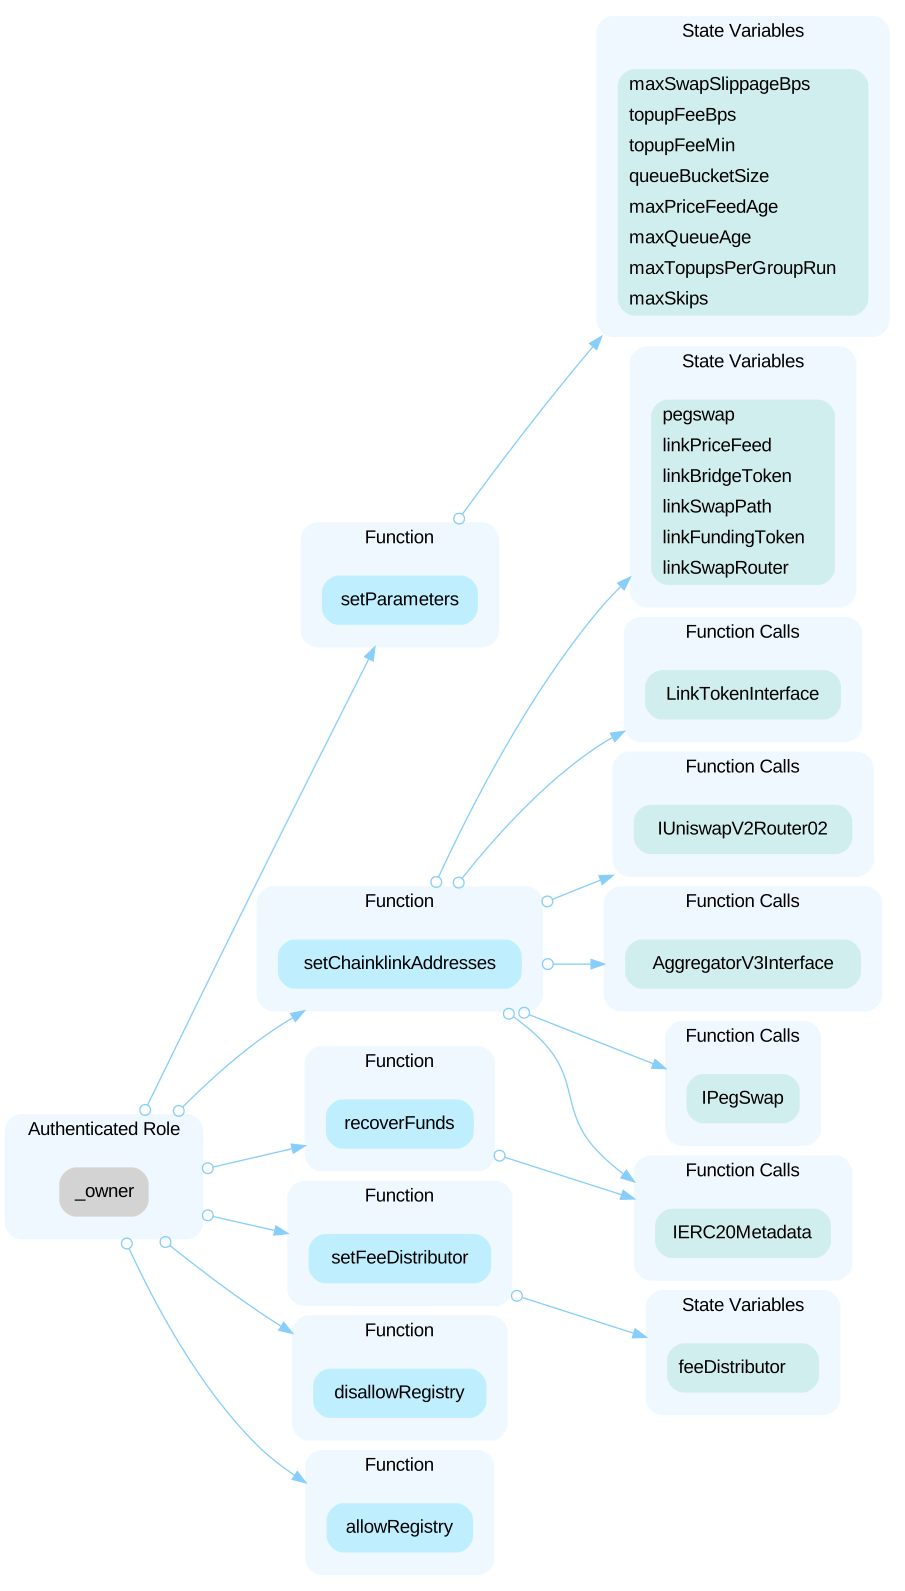
HighCentralization Risks in CaskDCA.solOpen
In the contract `CaskDCA` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, and set the DCA manager, the assets Merkle root, the trusted forwarder, and the DCA restrictions. 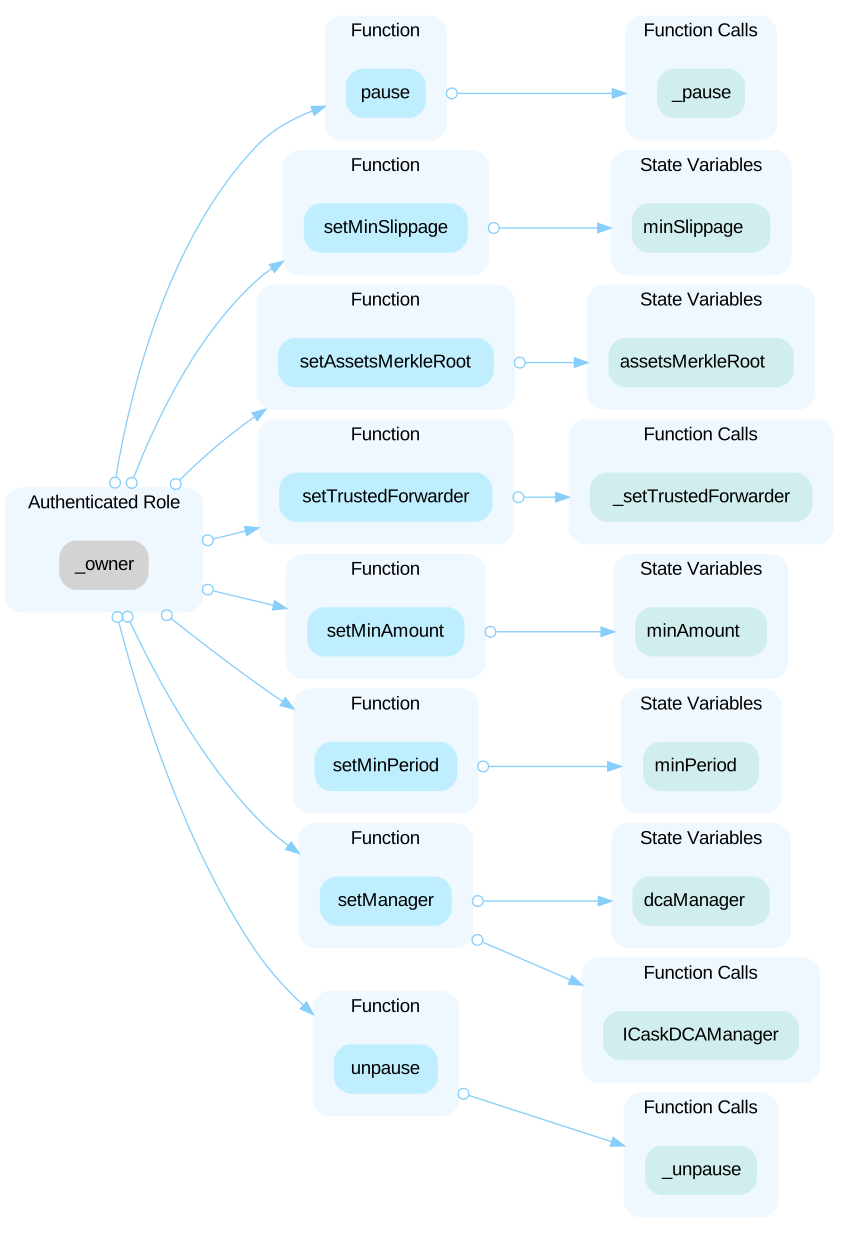
HighCentralization Risks in CaskDCAManager.solOpen
In the contract `CaskDCAManager` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, set/unset blacklistAssets, fee distributor, parameters, and recover ERC-20Funds. 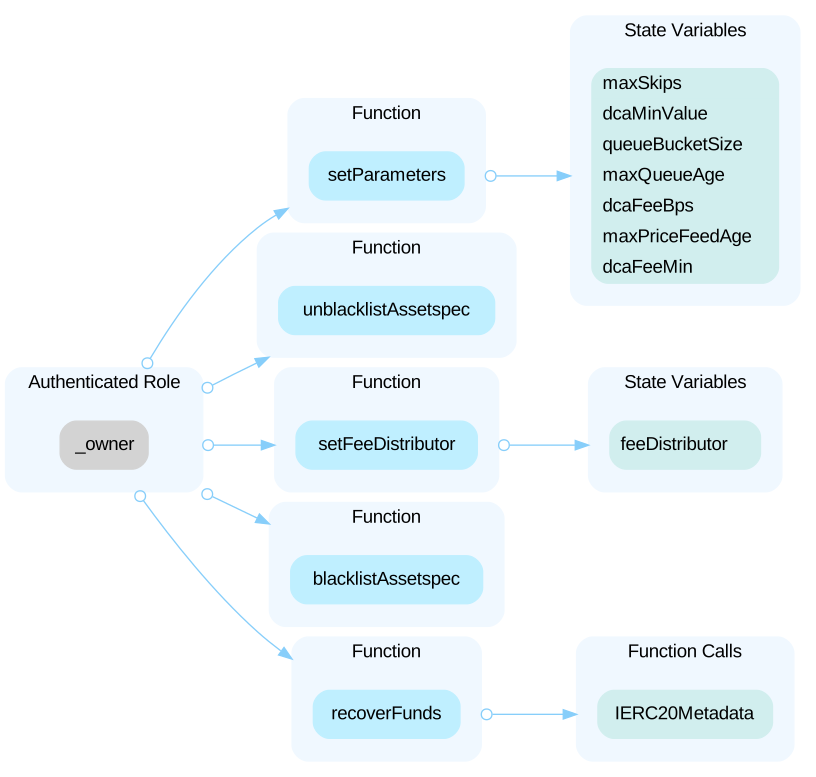
HighCentralization Risks in CaskJobQueue.solOpen
In the contract `CaskJobQueue` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the max queue age, and bucket size, and arbitrarily set the queue position 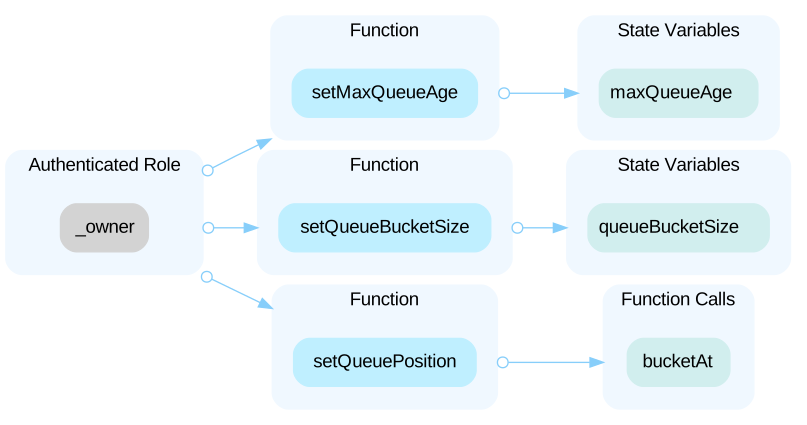
HighCentralization Risks in CaskP2P.solOpen
In the contract `CaskP2P` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the contract state variables. 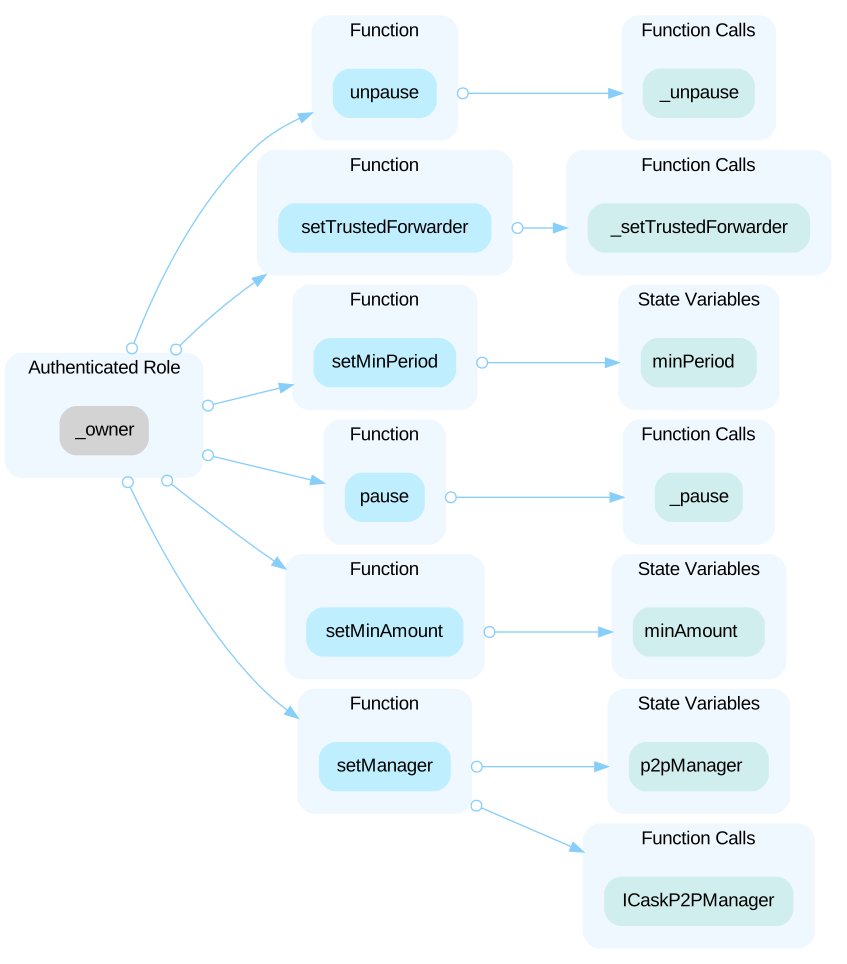
HighCentralization Risks in CaskP2PManager.solOpen
In the contract `CaskP2PManager` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update contract state variables. 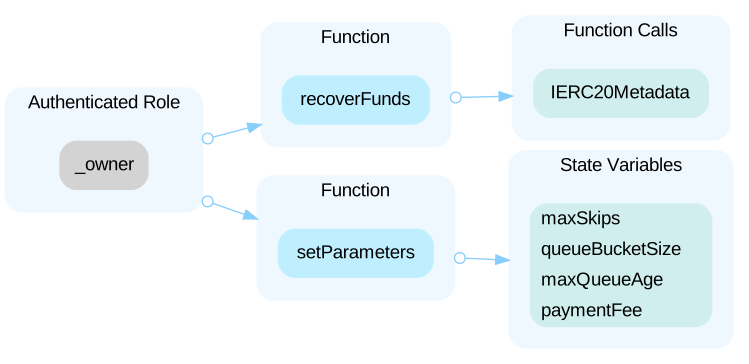 In the contract `CaskP2PManager` the role `_owner`, derived from `CaskJobQueue`, has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update contract state variables. 
HighCentralization Risks in Subscription Related ContOpen
In the contract `CaskSubscriptionManager` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause/unpause the contract and set important parameters. 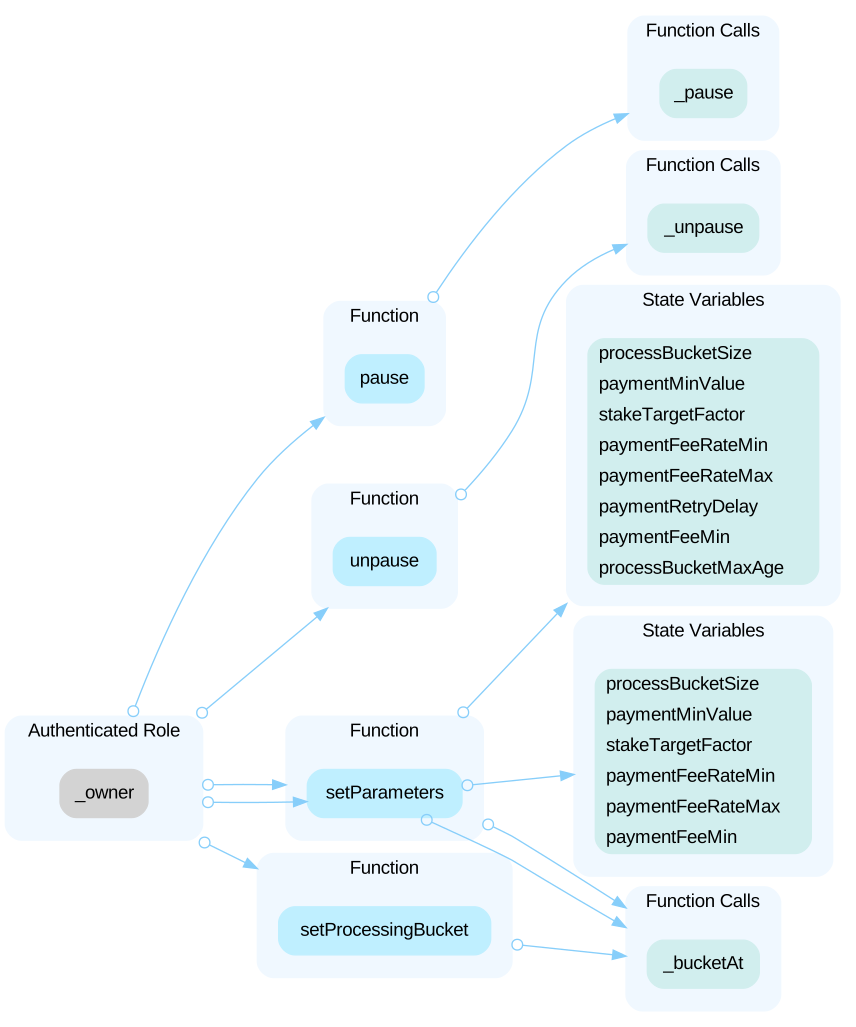 ----- In the contract `CaskSubscriptionPlans` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause/unpause the contract and set important addresses such as trusted forwarder, manager, etc. 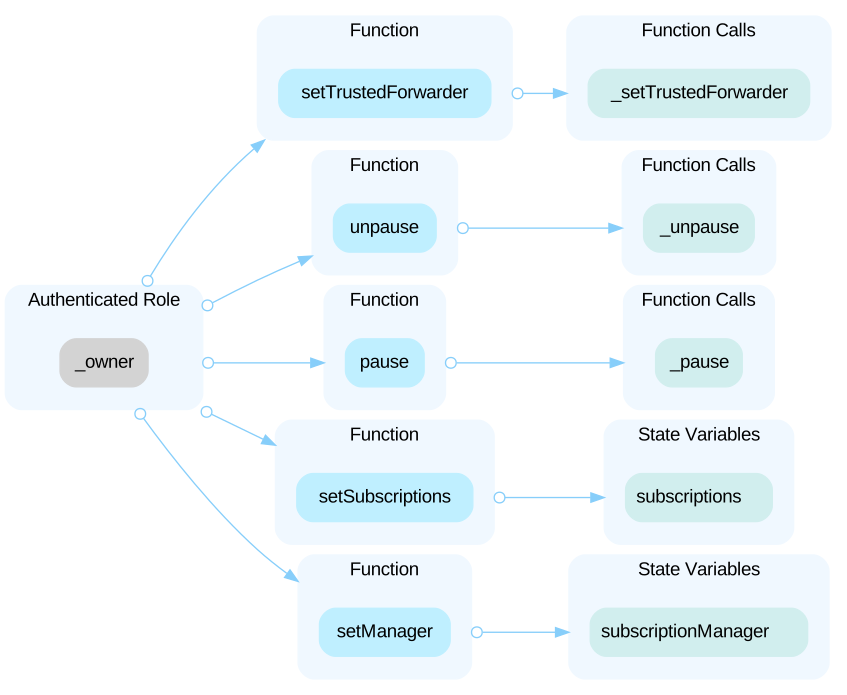 ----- In the contract `CaskSubscriptions` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause/unpause the contract and arbitrarily set trusted forwarder and manager. 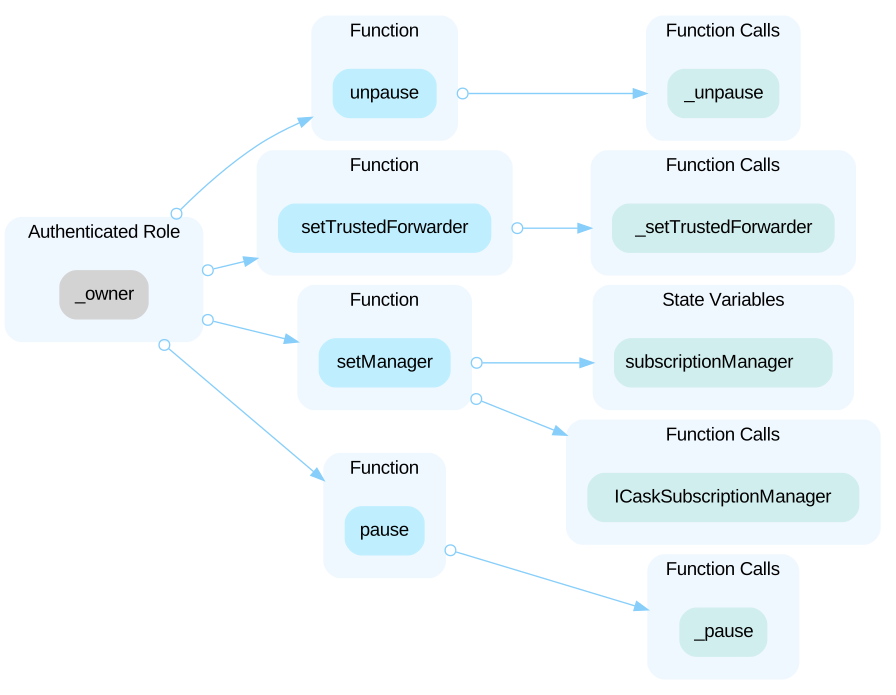
HighCentralized Control of Contract UpgradeOpen
Casks are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
LowDivide Before MultiplyOpen
Performing integer division before multiplication truncates the low bits, losing the precision of calculation. The function will be reverted if `(planData.period / 1 days)` is zero. ```solidity=165 uint256 loadFactor = 365 / (planData.period / 1 days); ``` ```solidity=166 uint256 noFeeTarget = subscriptions.getProviderSubscriptionCount(subscription.provider, false, 0) * stakeTargetFactor * loadFactor; ``` --- ```solidity=169 paymentFeeRateAdjusted = paymentFeeRateMax - (paymentFeeRateMax * (stakedBalance / noFeeTarget)); ```
Show 3 more
LowMissing sanity checks on Fee settingOpen
The fees for the linked contracts can be updated, while the upper limit is either missing or set to 100%.
LowThird Party DependencyOpen
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=41 IERC20Metadata public linkBridgeToken; ``` - The contract `CaskChainlinkTopupManager` interacts with third party contract with `IERC20Metadata` interface via `linkBridgeToken`. --- ```solidity=42 LinkTokenInterface public linkFundingToken; ``` - The contract `CaskChainlinkTopupManager` interacts with third party contract with `LinkTokenInterface` interface via `linkFundingToken`. --- ```solidity=43 AggregatorV3Interface public linkPriceFeed; ``` - The contract `CaskChainlinkTopupManager` interacts with third party contract with `AggregatorV3Interface` interface via `linkPriceFeed`. --- ```solidity=45 IUniswapV2Router02 public linkSwapRouter; ``` - The contract `CaskChainlinkTopupManager` interacts with third party contract with `IUniswapV2Router02` interface via `linkSwapRouter`. --- ```solidity=46 IPegSwap public pegswap; ``` - The contract `CaskChainlinkTopupManager` interacts with third party contract with `IPegSwap` interface via `pegswap`. --- ```solidity=30 address _asset, ``` - The function `CaskTreasury.withdrawTo` interacts with third party contract with `IERC20` interface via `_asset`. --- ```solidity=48 address _contract ``` - The function `CaskTreasury.claim` interacts with third party contract with `IClaimable` interface via `_contract`. --- ```solidity=26 IERC20 public rewardToken; ``` - The contract `CaskVestedEscrow` interacts with third party contract with `IERC20` interface via `rewardToken`. --- ```solidity=421 address _asset, ``` - The function `CaskDCAManager.recoverFunds` interacts with third party contract with `IERC20Metadata` interface via `_asset`. --- ```solidity=134 address _asset, ``` - The function `CaskP2PManager.recoverFunds` interacts with third party contract with `IERC20Metadata` interface via `_asset`.
LowUnknown Trusted Forwarder ImplementationOpen
The variable `_forwarder` serves as a 3rd party forwarder to help it identify the address of the Transaction Signer. The contract `CaskChainlinkTopup` override the `_msgSender()` function to get the `msg.sender` from `BaseRelayRecipient`. The scope of the audit treats these 3rd party forwarders as black boxes and assumes their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts. Reference: [EIP-2771](https://eips.ethereum.org/EIPS/eip-2771)
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (10)
- contracts/subscriptions/CaskSubscriptionManager.sol
- contracts/dca/CaskDCA.sol
- contracts/chainlink_topup/CaskChainlinkTopup.sol
- contracts/p2p/CaskP2PManager.sol
- contracts/p2p/CaskP2P.sol
- contracts/subscriptions/CaskSubscriptions.sol
- contracts/chainlink_topup/CaskChainlinkTopupManager.sol
- contracts/subscriptions/CaskSubscriptionPlans.sol
- contracts/job_queue/CaskJobQueue.sol
- contracts/dca/CaskDCAManager.sol
Part of Cask’s security record
 Cask
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us