Fitburn (Audit)
CertiK reviewed FitBurn AI (Fitburn (Audit)) on 5 May 2023: 15 findings, 0 critical; 12 marked fixed, 1 acknowledged, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings15
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 4 |
| Low | 0 | 1 | 8 |
HighCentralization Related RisksOpen
In the contract `AbstractFactory` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 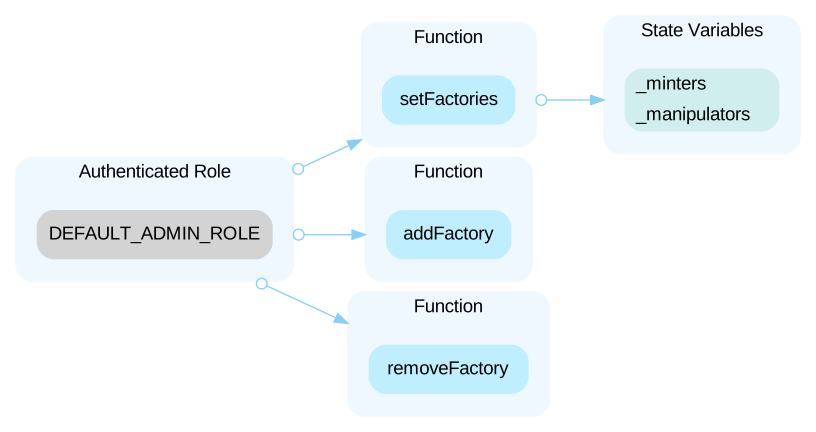 In the contract `ContractManager` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 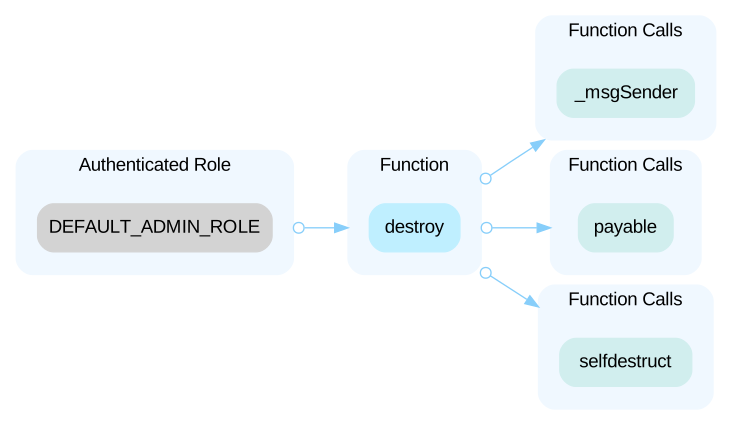 In the contract `ERC20Factory` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 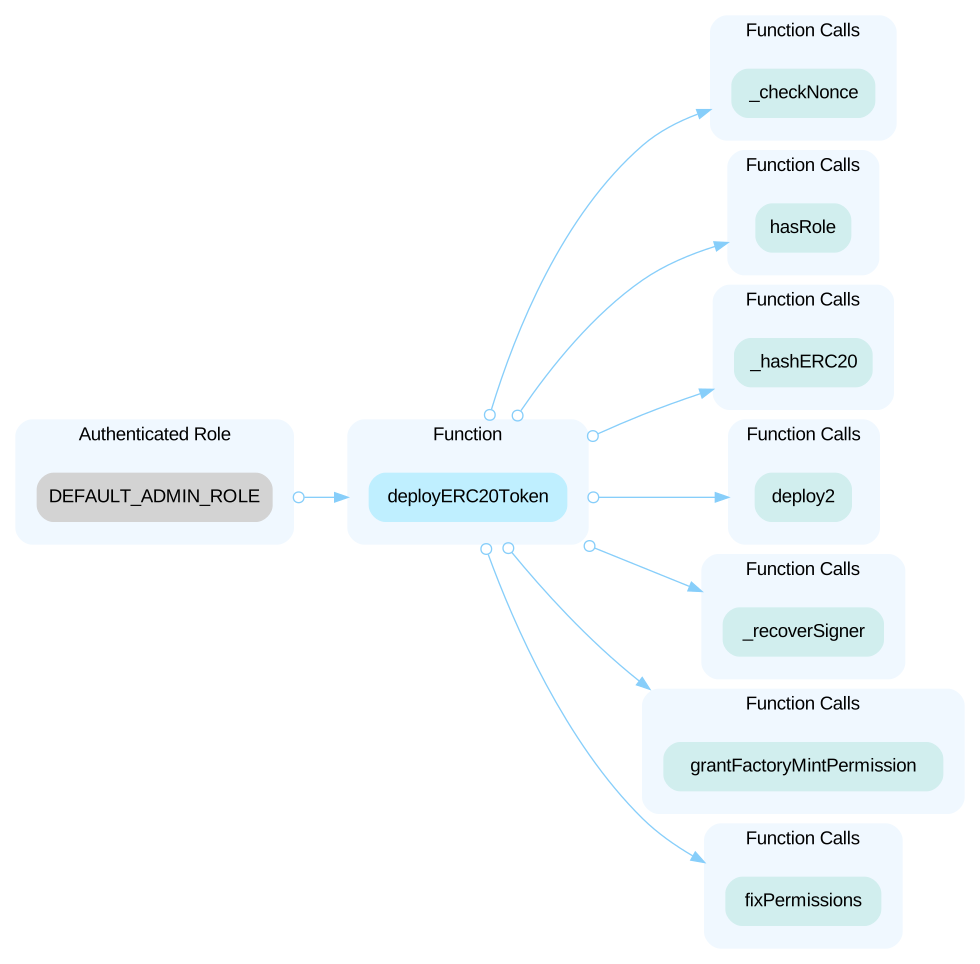 In the contract `ERC721Factory` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 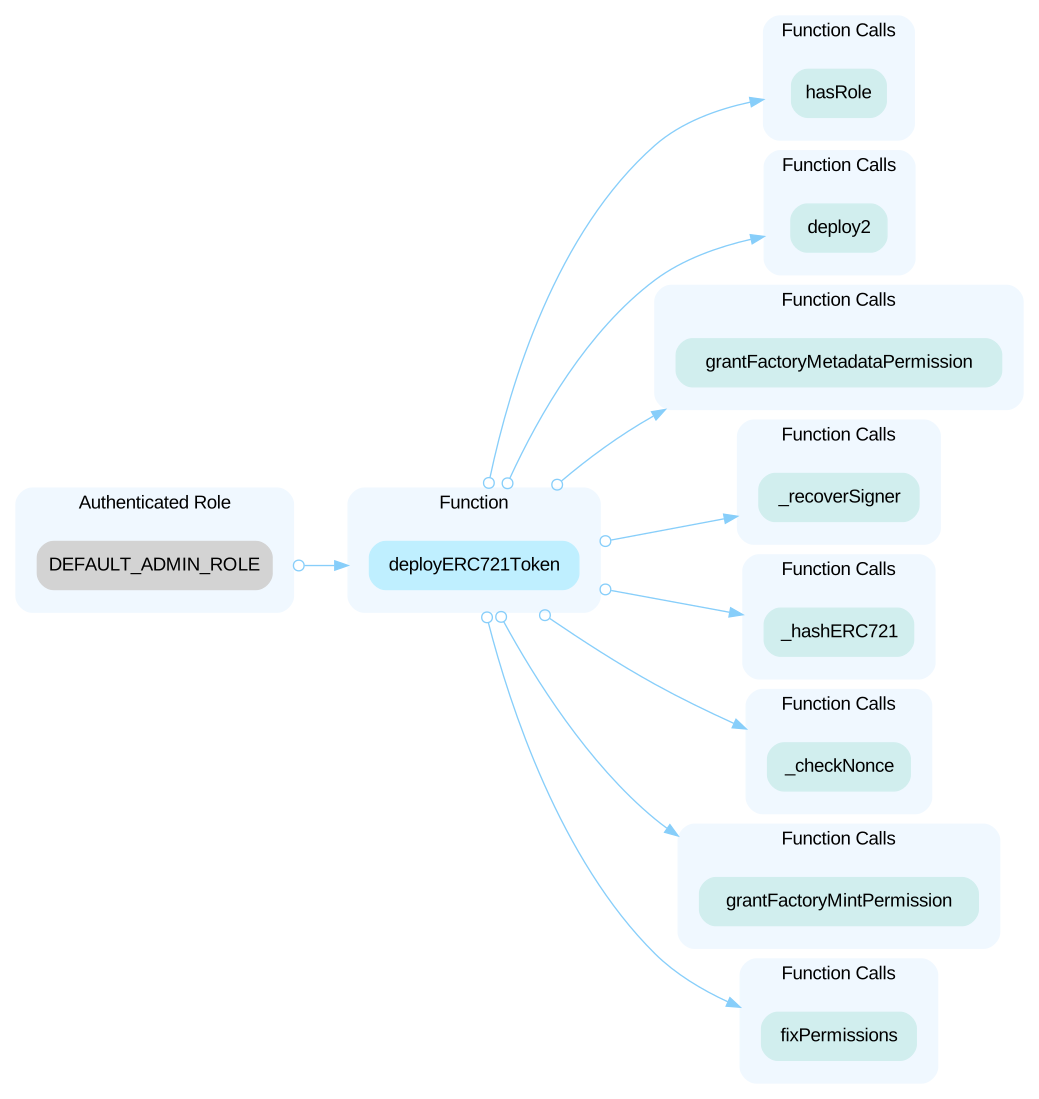 In the contract `VestingFactory` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 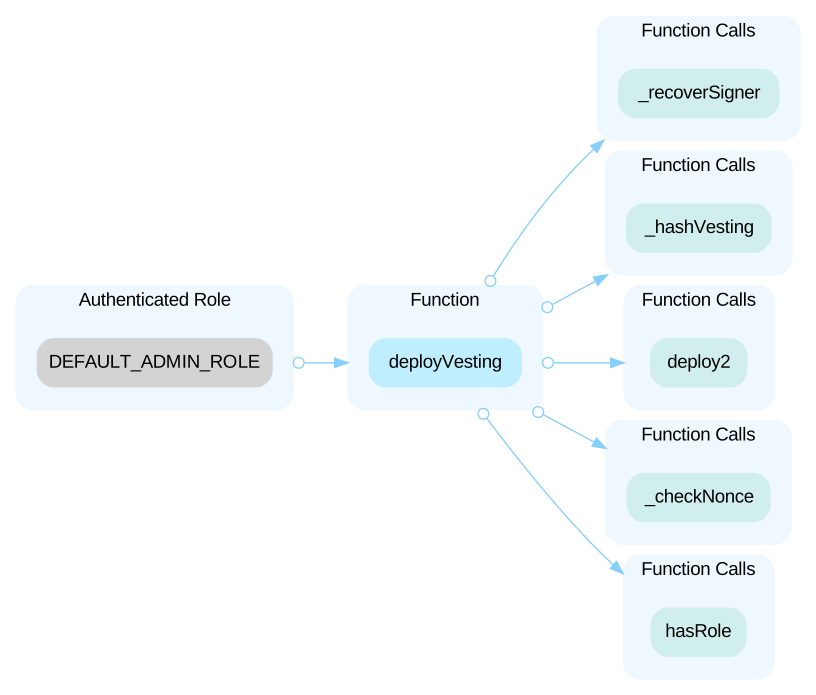 In the contract `ERC721BlacklistUpgradeable` the role `METADATA_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `METADATA_ROLE` account may allow the hacker to take advantage of this authority. 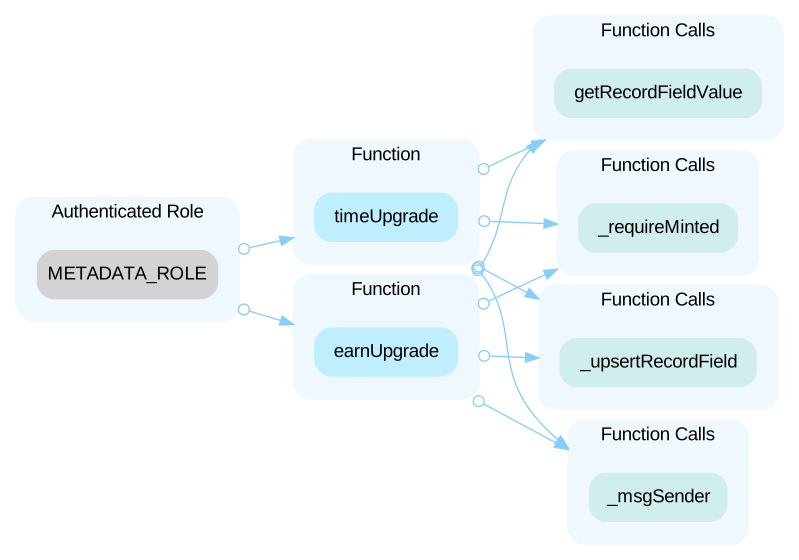 In the contract `ERC721BlacklistUpgradeableRentableRandom` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority. 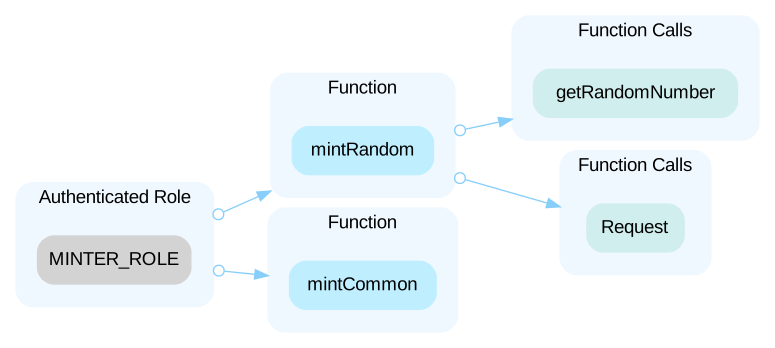 In the contract `ERC721Simple` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority. 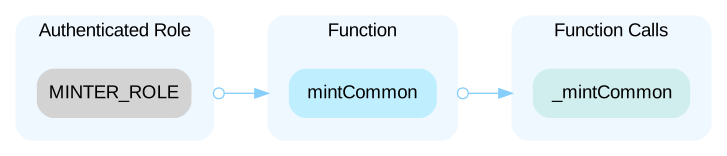 In the contract `ERC721BlacklistUpgradeableRentableRandomBesu` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority. 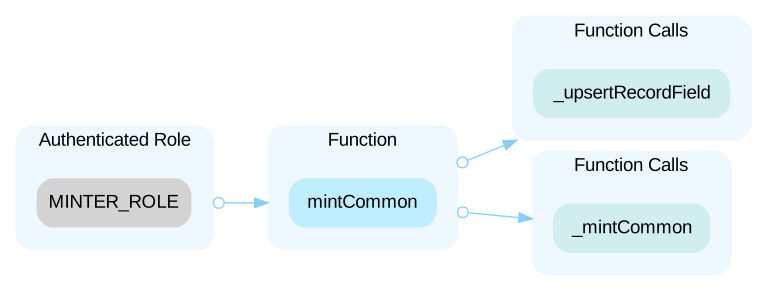 In the contract `Exchange` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority. 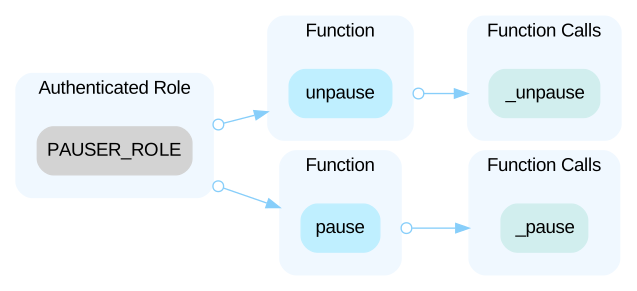 In the contract `Staking` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 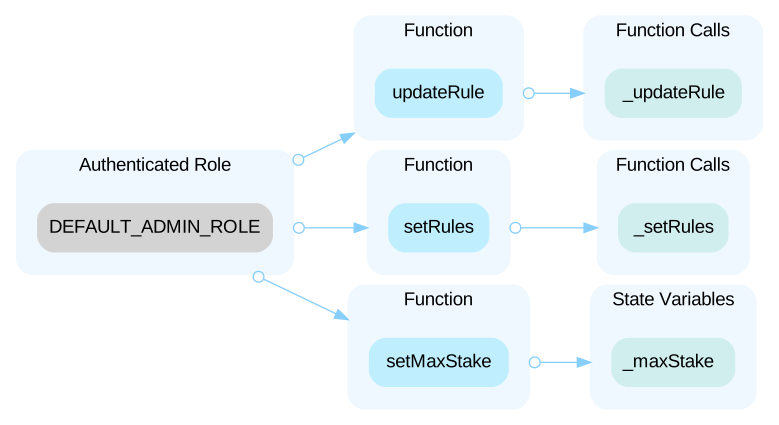 In the contract `Staking` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority. 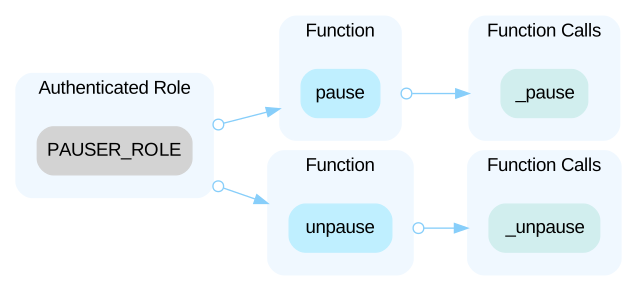
HighCentralization Related Risks in VestingOpen
In the contract `AbstractVesting` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 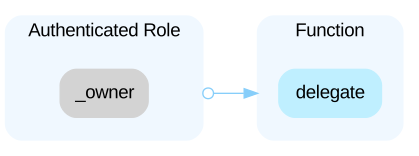 In the contract `AbstractVesting` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority. 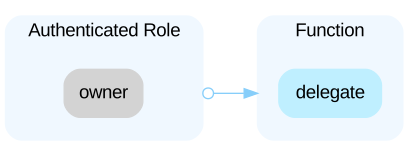
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (48)
- contracts/ERC721/interfaces/IERC721Upgradeable.sol
- contracts/ERC721/ERC721BlacklistUpgradeableRentableRandom.sol
- contracts/Mechanics/Staking/interfaces/IStaking.sol
- contracts/ContractManager/ERC20Factory.sol
- contracts/ERC721/ERC721Blacklist.sol
- contracts/ERC721/random/ERC721BlacklistUpgradeableRentableRandomGemunion.sol
- contracts/ERC721/random/ERC721BlacklistUpgradeableRentableRandomBinance.sol
- contracts/ERC721/random/ERC721BlacklistUpgradeableRentableRandomHardhat.sol
- contracts/Mechanics/Vesting/Marketing.sol
- contracts/ERC721/ERC721BlacklistUpgradeableRentable.sol
- contracts/ContractManager/ContractManager.sol
- contracts/Mechanics/Vesting/PreSeedSale.sol
- contracts/ContractManager/AbstractFactory.sol
- contracts/interfaces/IAccessList.sol
- contracts/ERC1155/ERC1155Simple.sol
- contracts/ERC721/random/ERC721BlacklistUpgradeableRentableRandomBesu.sol
- contracts/ERC721/ERC721BlacklistUpgradeable.sol
- contracts/ERC721/interfaces/IERC721Random.sol
- contracts/ERC721/ERC721Simple.sol
- contracts/ERC1155/interfaces/IERC1155Simple.sol
- contracts/Exchange/ExchangeGrade.sol
- contracts/Exchange/ExchangeClaim.sol
- contracts/Mechanics/Vesting/PublicSale.sol
- contracts/ERC20/ERC20Blacklist.sol
- contracts/Mechanics/Rarity/Rarity.sol
- contracts/ERC721/random/ERC721BlacklistUpgradeableRentableRandomBinanceTestnet.sol
- contracts/ContractManager/VestingFactory.sol
- contracts/Exchange/ExchangeCore.sol
- contracts/ERC20/ERC20Simple.sol
- contracts/Exchange/ExchangeUtils.sol
- contracts/Mechanics/Vesting/Team.sol
- contracts/Exchange/Exchange.sol
- contracts/ERC721/interfaces/IERC721Simple.sol
- contracts/ContractManager/ERC721Factory.sol
- contracts/utils/errors.sol
- contracts/Mechanics/Vesting/Partnership.sol
- contracts/utils/InterfaceIdCalculator.sol
- contracts/Mechanics/Vesting/AbstractVesting.sol
- contracts/Mechanics/Vesting/PrivateSale.sol
- contracts/utils/constants.sol
- contracts/Mechanics/Vesting/SeedSale.sol
- contracts/Exchange/ExchangeRentable.sol
- contracts/ERC721/interfaces/IERC721Metadata.sol
- contracts/Exchange/interfaces/IAsset.sol
- contracts/Exchange/SignatureValidator.sol
- contracts/Mechanics/Vesting/Advisors.sol
- contracts/utils/TopUp.sol
- contracts/Mechanics/Staking/Staking.sol
Part of FitBurn AI’s security record
 FitBurn AI
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us