Lee Group - Audit
CertiK reviewed Billion Box (Lee Group - Audit) on 8 Mar 2023: 11 findings, 0 critical; 4 marked fixed, 7 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings11
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 4 | 0 | 3 |
HighCentralization Risks in Peripheral ContractsOpen
In the contract `PortionBoxTicket` the role `MINTER` has authority over the functions shown in the diagram below. The `DEFAULT_ADMIN_ROLE` has the authority to assign `MINTER` roles. Any compromise to the `MINTER` or `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and arbitrarily mint ticket NFTs. 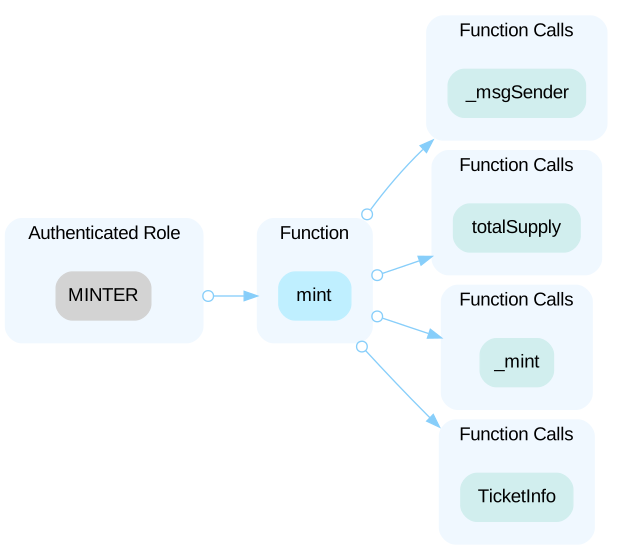 --------------------- In the contract `TokenSplitter` the role `DEFAULT_ADMIN_ROLE` has authority over the function `setReceivers()`. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set the recipients of the surplus prize token that is not reserved. 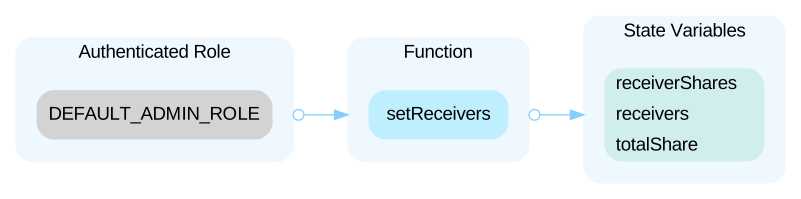 ------------------------ In the contract `TokenSwapper` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the `targetToken` and `paths`, which could lead to stolen funds and/or disrupt normal transactions. 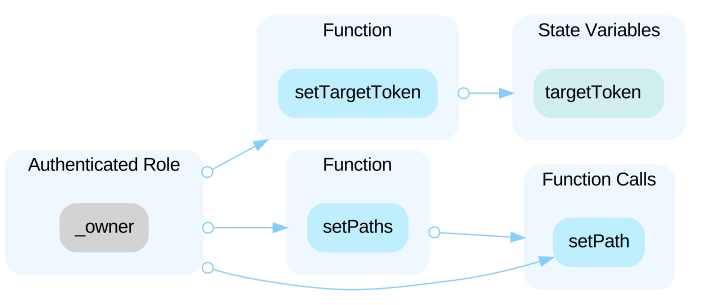
HighCentralization Risks in PortionBox.solOpen
In the contract `PortionBox` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and arbitrarily change critical state variables. 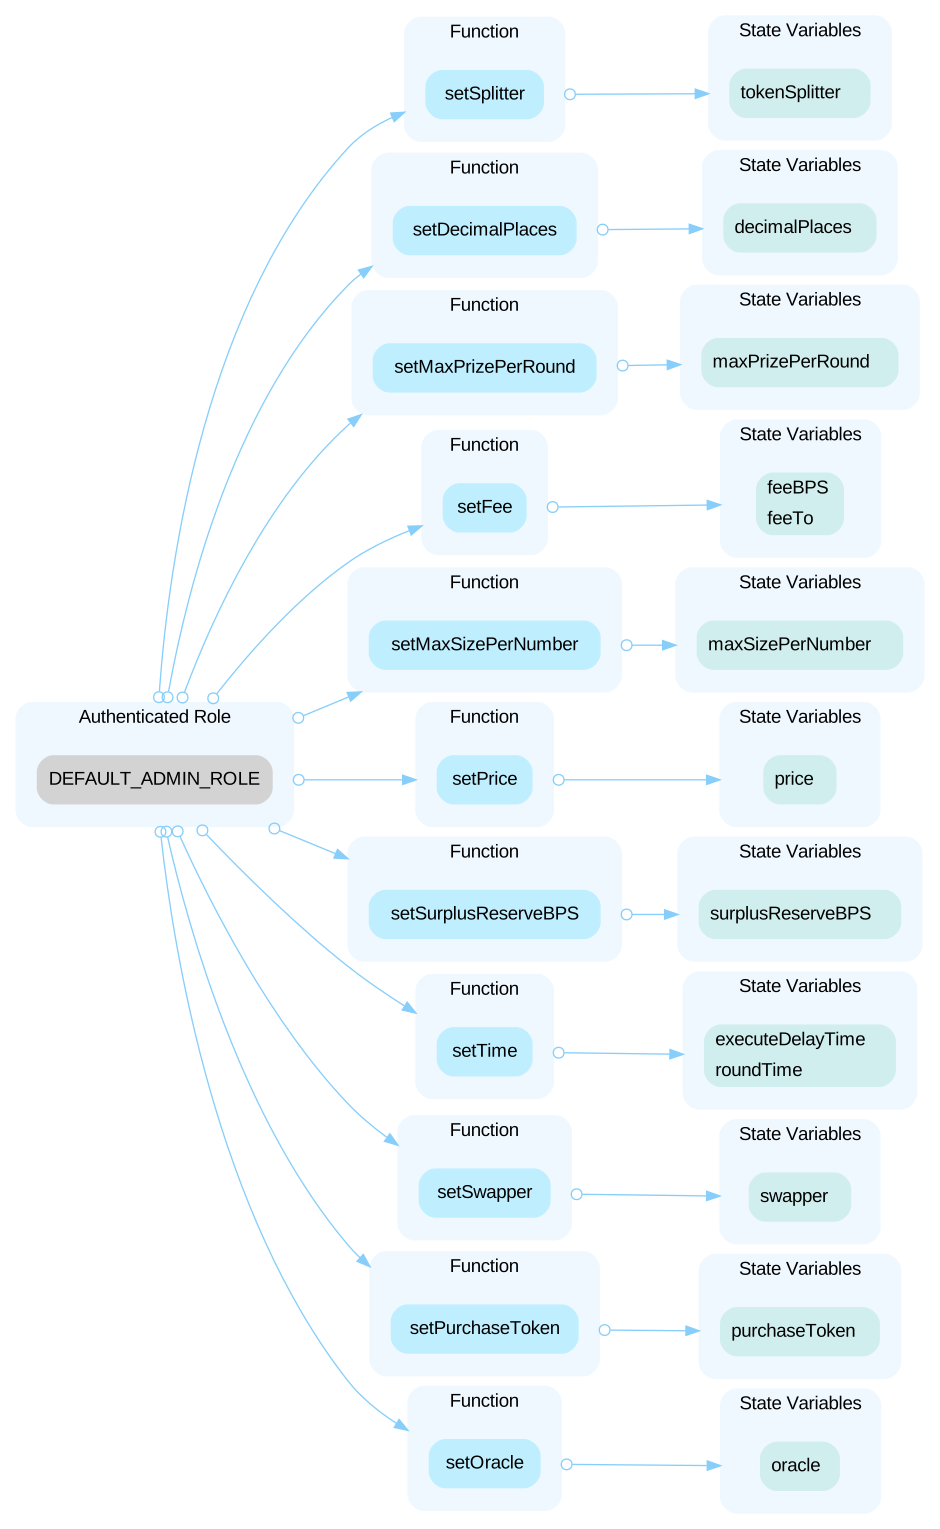 In the contract `PortionBox` the role `OPERATOR` has authority over the functions shown in the diagram below. Any compromise to the `OPERATOR` account may allow the hacker to take advantage of this authority and start the first round and new rounds before the expected cron job. 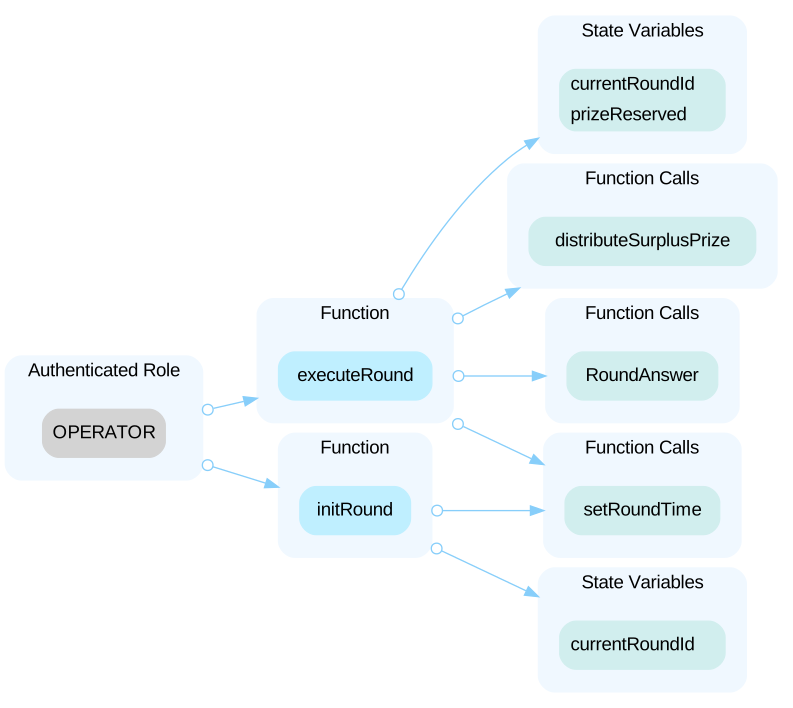
HighCentralized Control of Contract UpgradeOpen
ProtionBox is an upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
LowIncompatibility with Deflationary TokensOpen
In contract `PortionBox`, the `purchaseToken` should not be deflationary token. When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f ```solidity=376 purchaseToken.transferFrom(_msgSender(), address(this), amount); ``` - In function buy(), purchaseToken is transferred in by `amount`. ```solidity=58 if (fromLeft > 0) { from.transfer(_msgSender(), fromLeft); } ``` - In function buyWithETH() and buyWithToken(), the `purchaseToken` needed is defined by `amountOut`, but the actual amount received by `PortionBox` would be less if using deflationary token, because of the transfer from `TokenSwapper` to `PortionBox`. ```solidity=377 prizeReserved += amount; ``` - In function `addReserve`, the `amount` is directly added to `prizeReserved` without compensating the potential transfer fees.
LowPotential Lack of Randomness on Lottery ResultOpen
The PortionBox allows users to bet on the selected decimal places of the price on a given token. We'd like to point out that the possibility of every number may not be equal. For example, for BUSD/USD pricefeed, the first decimal place is very unlikely to be 5.
LowThird Party DependencyOpen
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new addresses, etc. The contracts depends on: 1. Chainlink Aggregator for token price, which is used as input to calculate lottery result. 2. External Uniswap-like swapper to exchange native token and ERC20 token to `purchaseToken`. 3. External ERC20 tokens for normal token transactions.
LowUnprotected InitializerOpen
Contract `PortionBox` does not protect their initializers. An attacker can call the initializer and assume ownership of the logic contract, whereby she can perform privileged operations that trick unsuspecting users into believing that he is the owner of the upgradeable contract. ```solidity=37 contract PortionBox is ERC165, IPortionBox, Initializable, AccessControlUpgradeable, ReentrancyGuardUpgradeable { ``` - `PortionBox` is an upgradeable contract that does not protect its initializer. ```solidity=146 function initialize( ``` - `initialize` is an unprotected initializer function.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (5)
- token-splitter/TokenSplitter.sol
- price-decimal-oracle/PriceDecimalOracle.sol
- portion-box/PortionBox.sol
- token-swapper/TokenSwapper.sol
- portion-box/PortionBoxTicket.sol
Part of Billion Box’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us