Cheelee
CertiK reviewed Cheelee on 7 Feb 2023: 14 findings, 0 critical; 11 marked fixed, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings14
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 10 |
HighCentralization Risks in `CHEEL.sol` and `LEE.sol`Open
In the contract `CHEEL` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint a large amount of tokens to an address he/she controls, as well as burn any amount of tokens from any address. 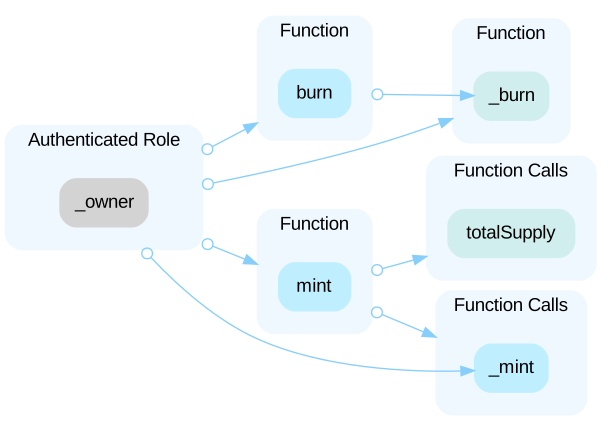 ---- In the contract `LEE` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint a large amount of tokens to an address he/she controls, as well as burn any amount of tokens from any address. 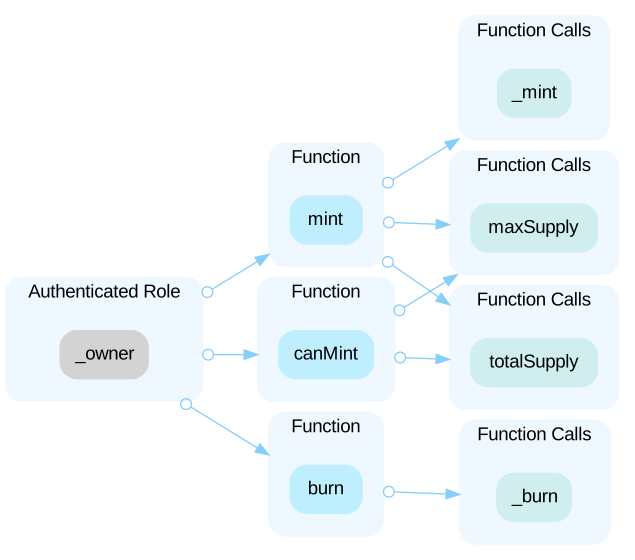
HighCentralization Risks in `MultiVesting.sol`Open
In the contract `MultiVesting` the role `_oldBeneficiary` has authority over the functions shown in the diagram below. Any compromise to the `_oldBeneficiary` account may allow the hacker to take advantage of this authority and set the `_beneficiaryAddress` to an address he/she controls, which will eventually receive tokens from the contract. 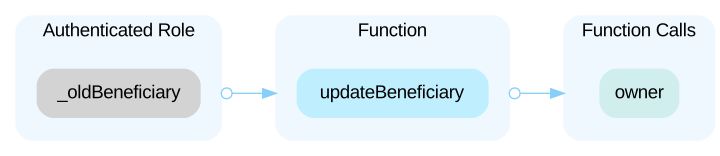 ---- In the contract `MultiVesting` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and wipe the contract of all tokens using the `emergancyVest()` function, as well as set the address of the `seller` to an address he/she controls. 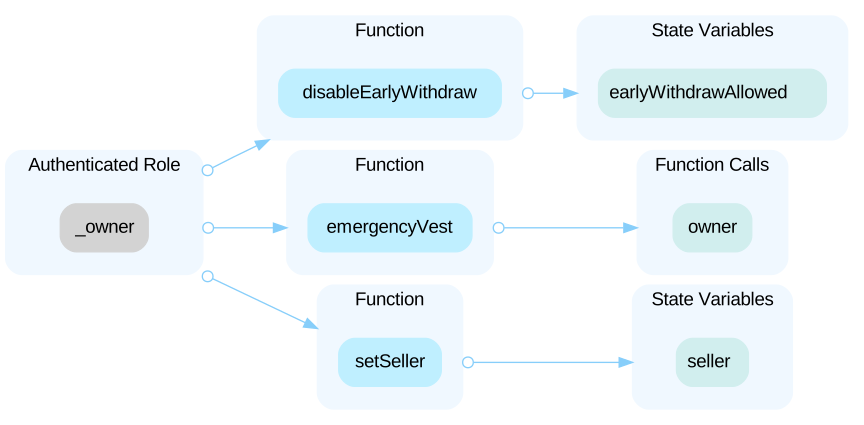 ---- In the contract `MultiVesting` the role `seller` has authority over the functions shown in the diagram below. Any compromise to the `seller` account may allow the hacker to take advantage of this authority and call the `vest()` function with the `_beneficiaryAddress` set to addresses he/she controls, which will eventually receive tokens from the contract. 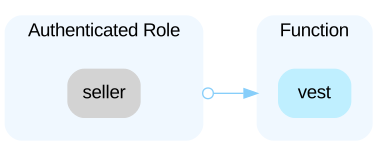
HighCentralization Risks in `NFT.sol` and `NFTSale.soOpen
In the contract `NFT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and create an unlimited amount of NFT's to send to addresses he/she controls, change the URIs of NFTs, which points to a location where a user can find the token's JSON description, and provided privileged roles to addresses he/she controls. 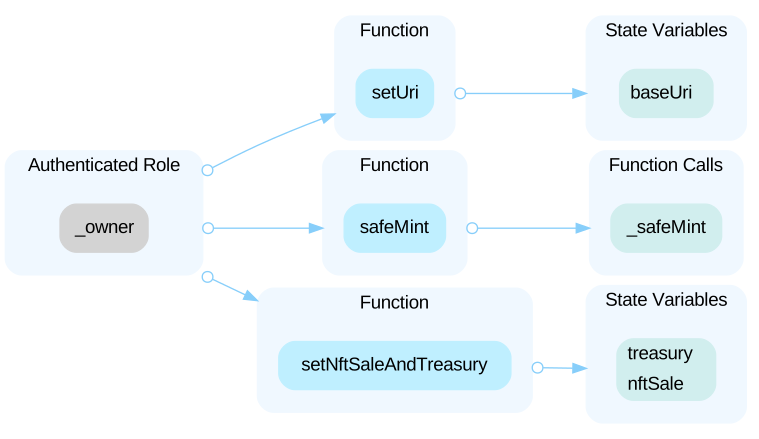 In the contract `NFT` the roles `nftSale` and `treasury` have authority over the functions shown in the diagram below. Any compromise to the `nftSale` and `treasury` accounts may allow the hacker to take advantage of this authority and create an unlimited amount of NFT's to send to addresses he/she controls. 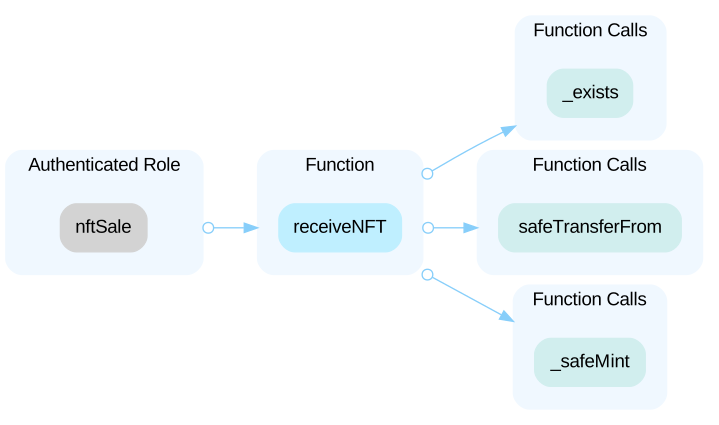 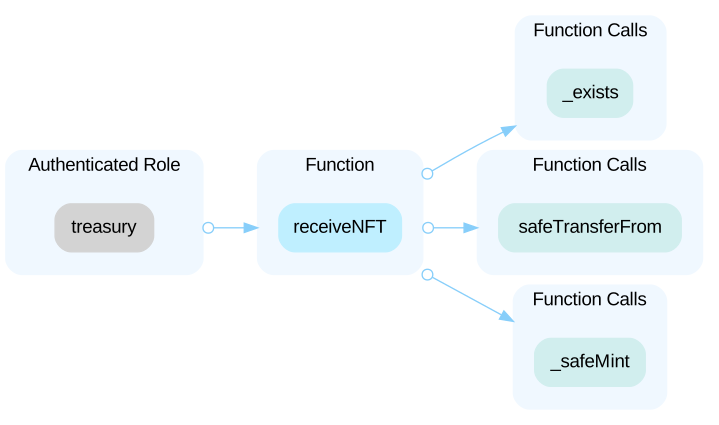 ---- In the contract `NFTSale` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and wipe the contract of all its ether, change the `pricePerToken` to a value he/she could benefit from, pause purchasing and/or redeeming, which disrupts contract functionality, change the `signer` to an addresses he/she controls to redeem unlimited tokens, and lastly change the values of `redeemSupply` and `purchaseSupply`, which could also disrupt contract functionality. 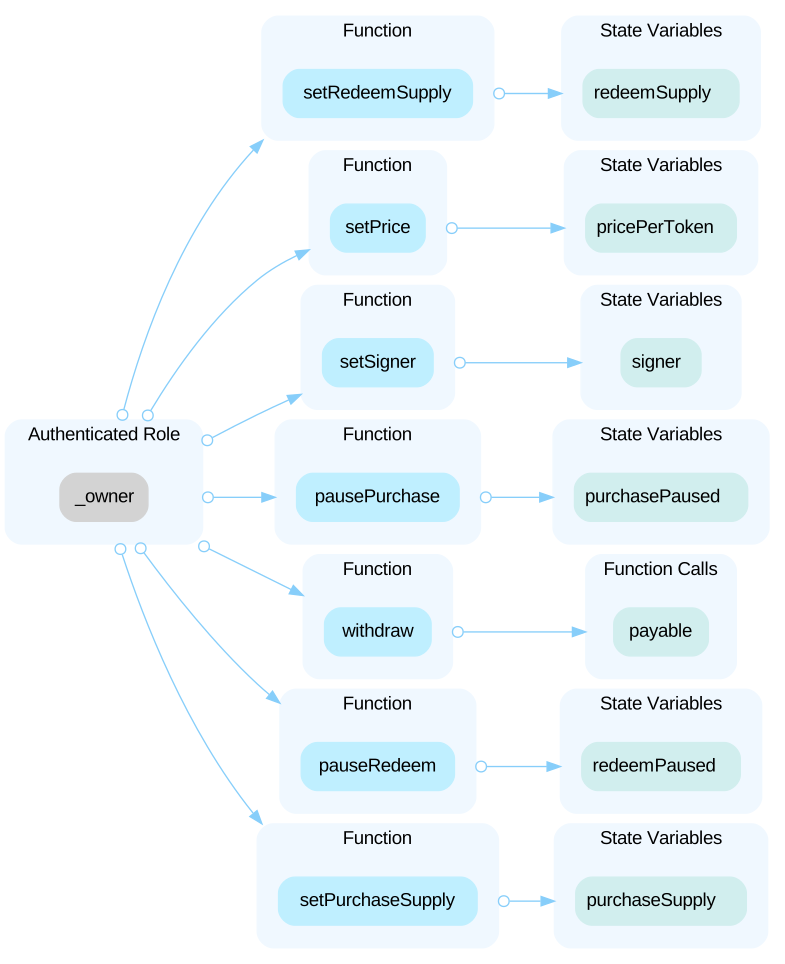
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (10)
- contracts/LEE.sol
- contracts/interfaces/CustomNFT.sol
- contracts/Staking.sol
- contracts/interfaces/IERC20Mintable.sol
- contracts/NFTSale.sol
- contracts/interfaces/IVesting.sol
- contracts/CHEEL.sol
- contracts/Treasury.sol
- contracts/MultiVesting.sol
- contracts/NFT.sol
Part of Cheelee’s security record
 Cheelee
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us