RAI Finance
CertiK reviewed RAI Finance on 26 Oct 2022: 12 findings, 1 critical; 7 marked fixed, 2 acknowledged, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings12
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 1 | 0 |
| High | 3 | 0 | 2 |
| Medium | 0 | 1 | 1 |
| Low | 0 | 0 | 4 |
HighCalling `removeModule` Should Be LimitedOpen
The `manager` can call `removeModule` at any time, if `PortfolioModule` is removed, `PortfolioModule.redeem` can not be called on this `portfolio`, users can not `redeem` their assets. So limit calling `removeModule` is necessary.
HighCentralization Risk in PortfolioFactory.solOpen
In the contract, `PortfolioFactory`, the role, `_owner`, has the authority over the functions shown in the diagram below. Any compromise to the privileged account which has access to `_owner` may allow the hacker to take advantage of this and [fixme]. 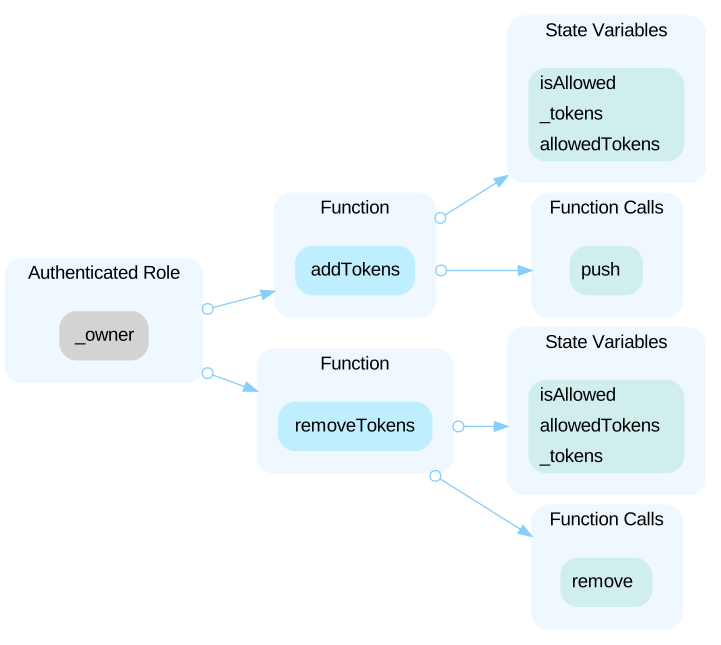
HighMalicious Users Can Create And Manipulate `PortfoOpen
Everyone can call `PortfolioFactory.create` to create a `Portfolio` with specified `manager`. The `manager` can call `ManagerModule.trade` to swap one token to another token, malicious users can get profit from this `trade`, but the assets of `Portfolio` are lost. An example looks like `Sandwich Attacks`, the `manager` calls the function `ManagerModule.trade` with meager `_minReceiveQuantity` value, and sandwich attack himself to get profit.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (31)
- contracts/interfaces/IModule.sol
- contracts/ManagerModule.sol
- contracts/interfaces/ISOFIProxy.sol
- contracts/IntegrationRegistry.sol
- contracts/PortfolioModule.sol
- contracts/protocol-viewers/PortfolioViewer.sol
- contracts/interfaces/IManagerIssuanceHook.sol
- contracts/interfaces/IController.sol
- contracts/interfaces/IPortfolioModule.sol
- contracts/lib/AddressArrayUtils.sol
- contracts/interfaces/IIntegrationRegistry.sol
- contracts/PortfolioFactory.sol
- contracts/SOFITrading.sol
- contracts/protocol-viewers/ERC20Viewer.sol
- contracts/lib/UniSushiV2Library.sol
- contracts/protocol-viewers/ProtocolViewer.sol
- contracts/SOFIProxy.sol
- contracts/interfaces/IPortfolio.sol
- contracts/interfaces/ISOFIProxyAdapter.sol
- contracts/lib/PreciseUnitMath.sol
- contracts/lib/Invoke.sol
- contracts/SOFIProxyAdapter.sol
- contracts/lib/ExplicitERC20.sol
- contracts/lib/Position.sol
- contracts/Portfolio.sol
- contracts/lib/ModuleBase.sol
- contracts/interfaces/IWETH.sol
- contracts/UniswapV2ExchangeAdapter.sol
- contracts/Controller.sol
- contracts/lib/ResourceIdentifier.sol
- contracts/SimpleERC20.sol
Part of RAI Finance’s security record
 RAI Finance
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us