Flokifi II
CertiK reviewed FlokiFi (Flokifi II) on 8 Oct 2023: 11 findings, 0 critical; 9 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings11
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 1 | 0 | 8 |
HighCentralization Related RisksOpen
In the contract `Whitelist` the role `WHITELIST_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `WHITELIST_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 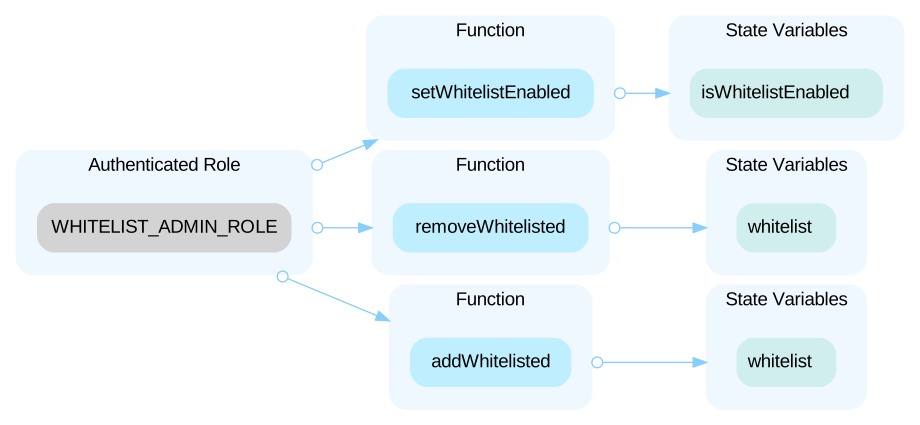 In the contract `PricingModuleV1` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 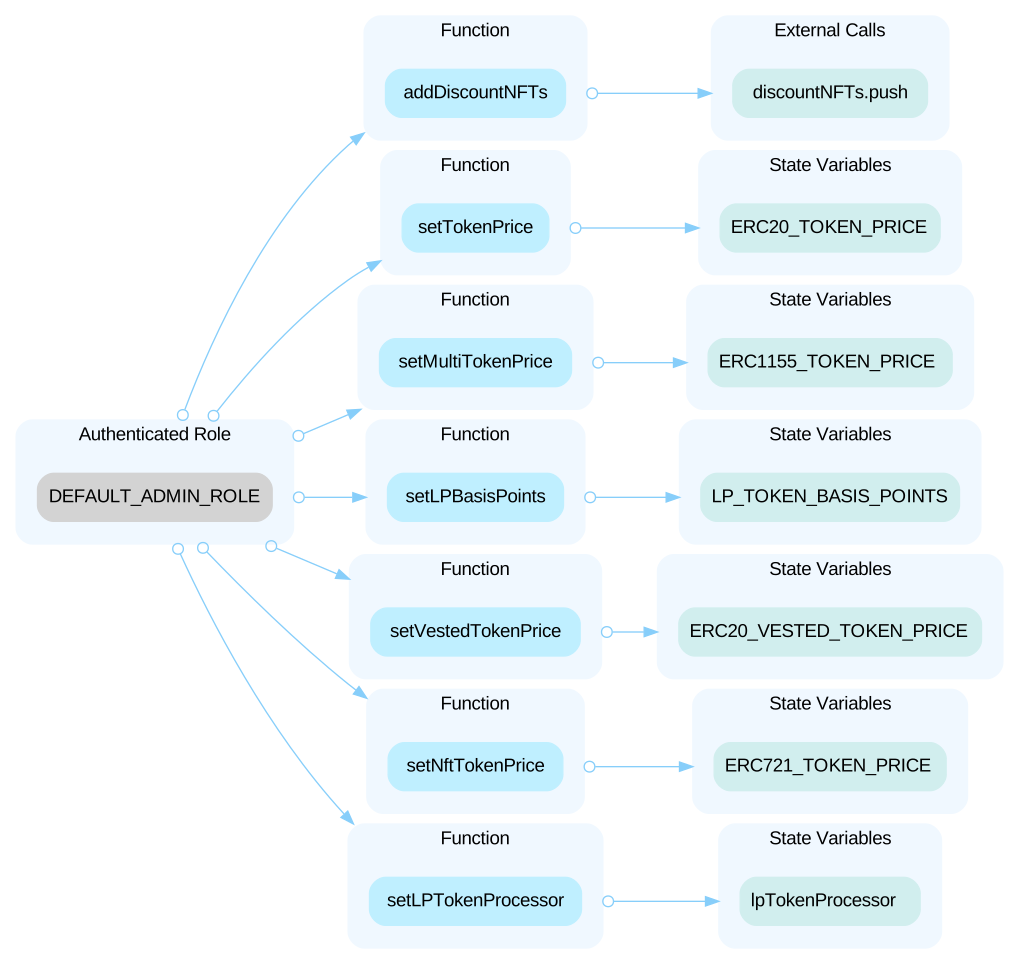 In the contract `ChainlinkPriceConsumer` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 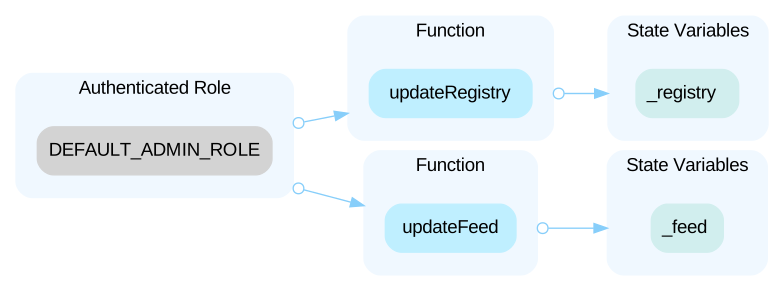 In the contract `ChainlinkPriceConsumer` the role `ORACLE_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ORACLE_MANAGER_ROLE` account may allow the hacker to take advantage of this authority. 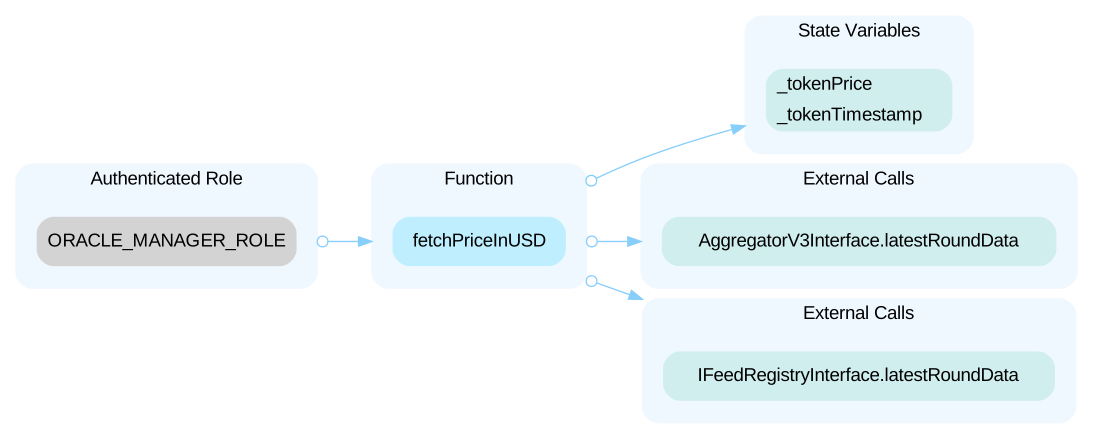 In the contract `DiaPriceConsumer` the role `ORACLE_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ORACLE_MANAGER_ROLE` account may allow the hacker to take advantage of this authority . 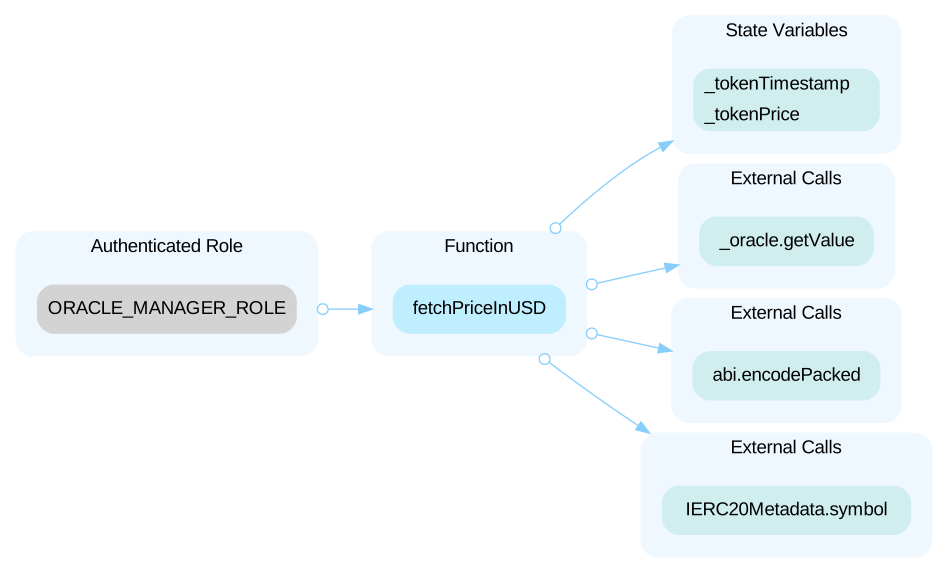 In the contract `ManualPriceConsumer` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority . 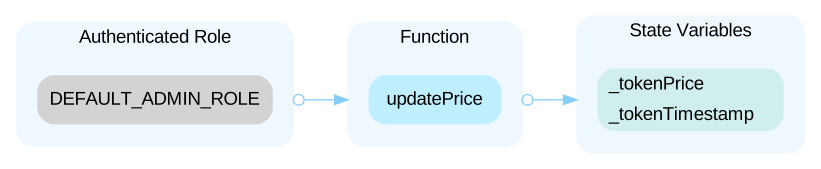 In the contract `PriceOracleManagerV1` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority . 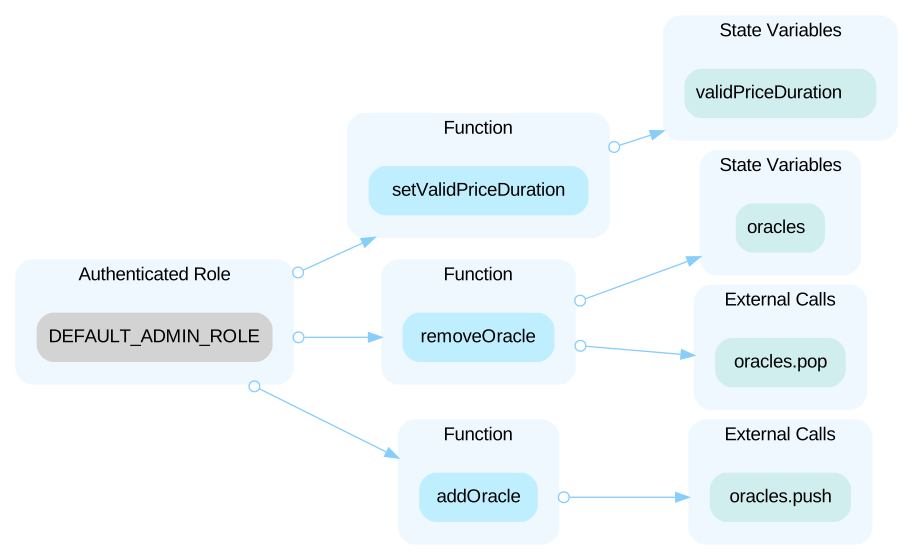 In the contract `PriceOracleManagerV1` the role `ORACLE_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ORACLE_MANAGER_ROLE` account may allow the hacker to take advantage of this authority . 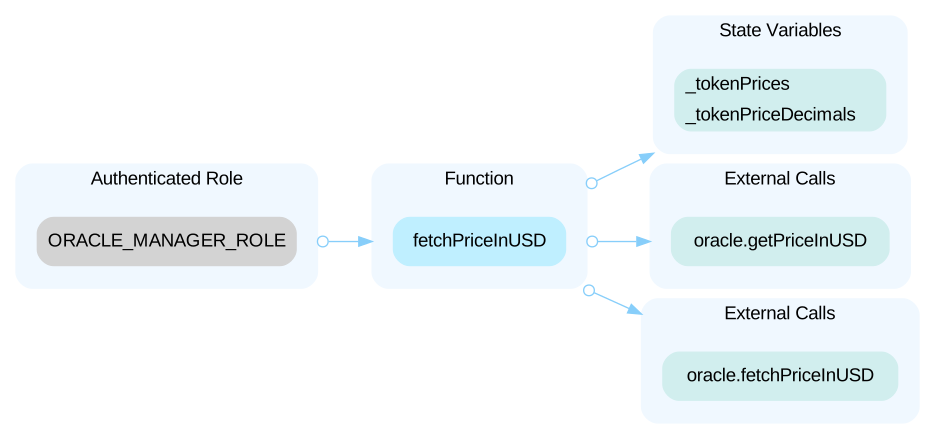 In the contract `PythPriceConsumer` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 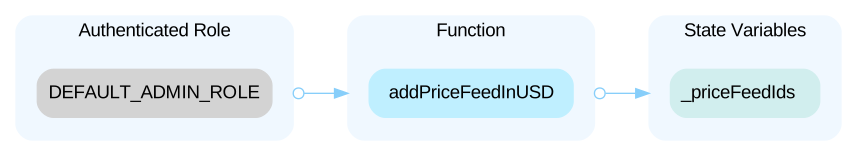 In the contract `PythPriceConsumer` the role `ORACLE_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ORACLE_MANAGER_ROLE` account may allow the hacker to take advantage of this authority. 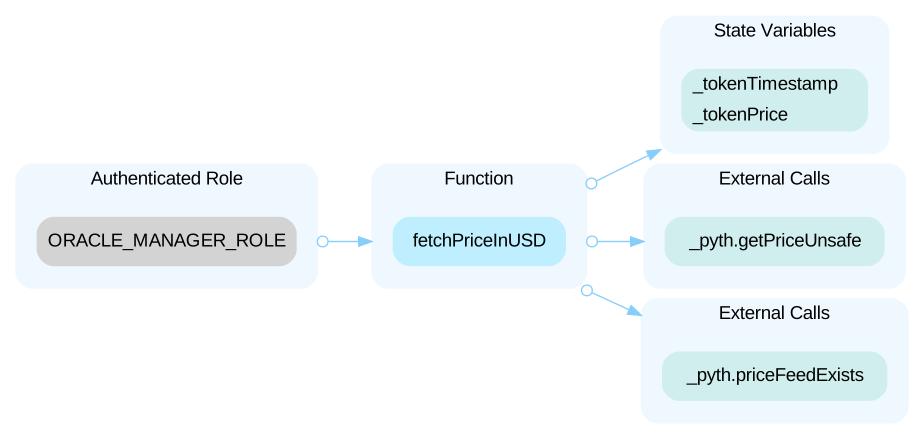 In the contract `VaultDeployer` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 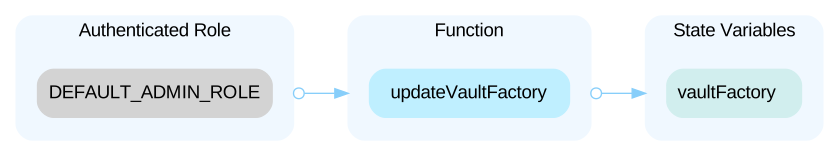 In the contract `VaultDeployer` the role `_fromfactory` has authority over the functions shown in the diagram below. Any compromise to the `_fromfactory` account may allow the hacker to take advantage of this authority. 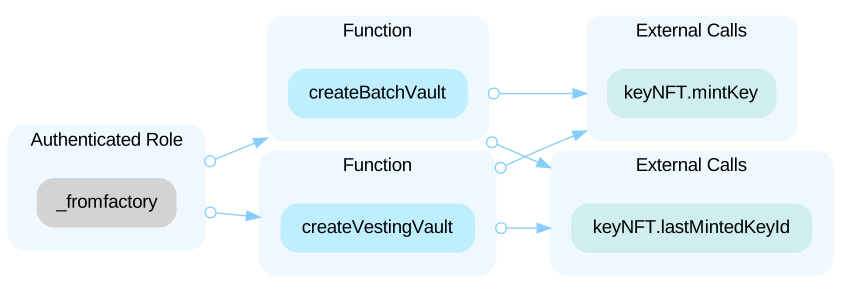 In the contract `VaultDeployer` the role `vaultFactory` has authority over the functions s
LowThird Party DependencyOpen
The contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. In PriceOracleManagerV1 ```solidity function fetchPriceInUSD(address token) external override onlyRole(ORACLE_MANAGER_ROLE) { for (uint256 i = 0; i < oracles.length; i++) { IPriceConsumer oracle = IPriceConsumer(oracles[i]); uint256 minTimestamp = block.timestamp - validPriceDuration; try oracle.fetchPriceInUSD(token, minTimestamp) { (uint256 price, uint256 decimals, uint256 timestamp) = oracle.getPriceInUSD(token); if (block.timestamp - timestamp > validPriceDuration) { // too old, look at the next oracle continue; } _tokenPrices[token] = price; _tokenPriceDecimals[token] = decimals; } catch { // oracle failed, look at the next oracle continue; } } } ``` In the function `fetchPriceInUSD()`, as long as the update time of the price returned by the Oracle is less than validPriceDuration, the price returned by the Oracle may be utilized. As a result, users might manipulate the Oracle to enable the function to use potentially exploitable Oracle instances. Due to the `fetchPriceInUSD()` function being accessible only to the `ORACLE_MANAGER_ROLE`, the likelihood of this scenario occurring is relatively low.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (31)
- contracts/locker/interfaces/ILPTokenProcessorV1.sol
- contracts/common/interfaces/IVaultKey.sol
- contracts/locker/VaultDeployer.sol
- contracts/locker/vault/FungibleVestingVault.sol
- contracts/locker/interfaces/IVaultFactory.sol
- contracts/locker/interfaces/ILPTokenProcessorV2.sol
- contracts/locker/interfaces/IPricingModule.sol
- contracts/common/oracles/DiaPriceConsumer.sol
- contracts/common/oracles/PriceOracleManagerV1.sol
- contracts/common/interfaces/IERC20.sol
- contracts/common/utils/Whitelist.sol
- contracts/common/oracles/ManualPriceConsumer.sol
- contracts/locker/interfaces/IPaymentModule.sol
- contracts/locker/interfaces/IVaultDeployer.sol
- contracts/common/oracles/ChainlinkPriceConsumer.sol
- contracts/locker/vault/Vault.sol
- contracts/common/interfaces/INonfungiblePositionManager.sol
- contracts/locker/payment/PricingModuleV1.sol
- contracts/common/interfaces/IUniswapPair.sol
- contracts/locker/vault/MultiVault.sol
- contracts/locker/VaultKey.sol
- contracts/common/oracles/PythPriceConsumer.sol
- contracts/locker/payment/LPTokenProcessorV1.sol
- contracts/locker/payment/PaymentModuleV1.sol
- contracts/locker/VaultFactory.sol
- contracts/common/interfaces/IPriceConsumer.sol
- contracts/locker/payment/LPTokenProcessorV2.sol
- contracts/locker/interfaces/IDepositHandler.sol
- contracts/common/interfaces/ISwapRouterV3.sol
- contracts/common/interfaces/IPriceOracleManager.sol
- contracts/locker/interfaces/IVault.sol
Part of FlokiFi’s security record
 FlokiFi
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us