
FlokiFi security record
As of 3 Nov 2026, FlokiFi has 3 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 6 Nov 2023. Those reports list no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits3
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Flokifi Staking | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Flokifi II | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Flokifi | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings48
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 6 | 0 | 5 |
| Medium | 0 | 0 | 5 |
| Low | 6 | 0 | 26 |
HighCentralization Risks in FlokiStakingPool.solFlokifi Staking · CertiK · 6 Nov 2023Open
In the contract `FlokiStakingPool` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: - `extendRewardsDuration()`, to extend the duration of the reward. - `initializeStaking()`, to initialize the staking. - `recoverERC20()`, to transfer erc20 tokens to the owner except the staking/reward token. - `transferOwnership()`, to transfer ownership to new owner. 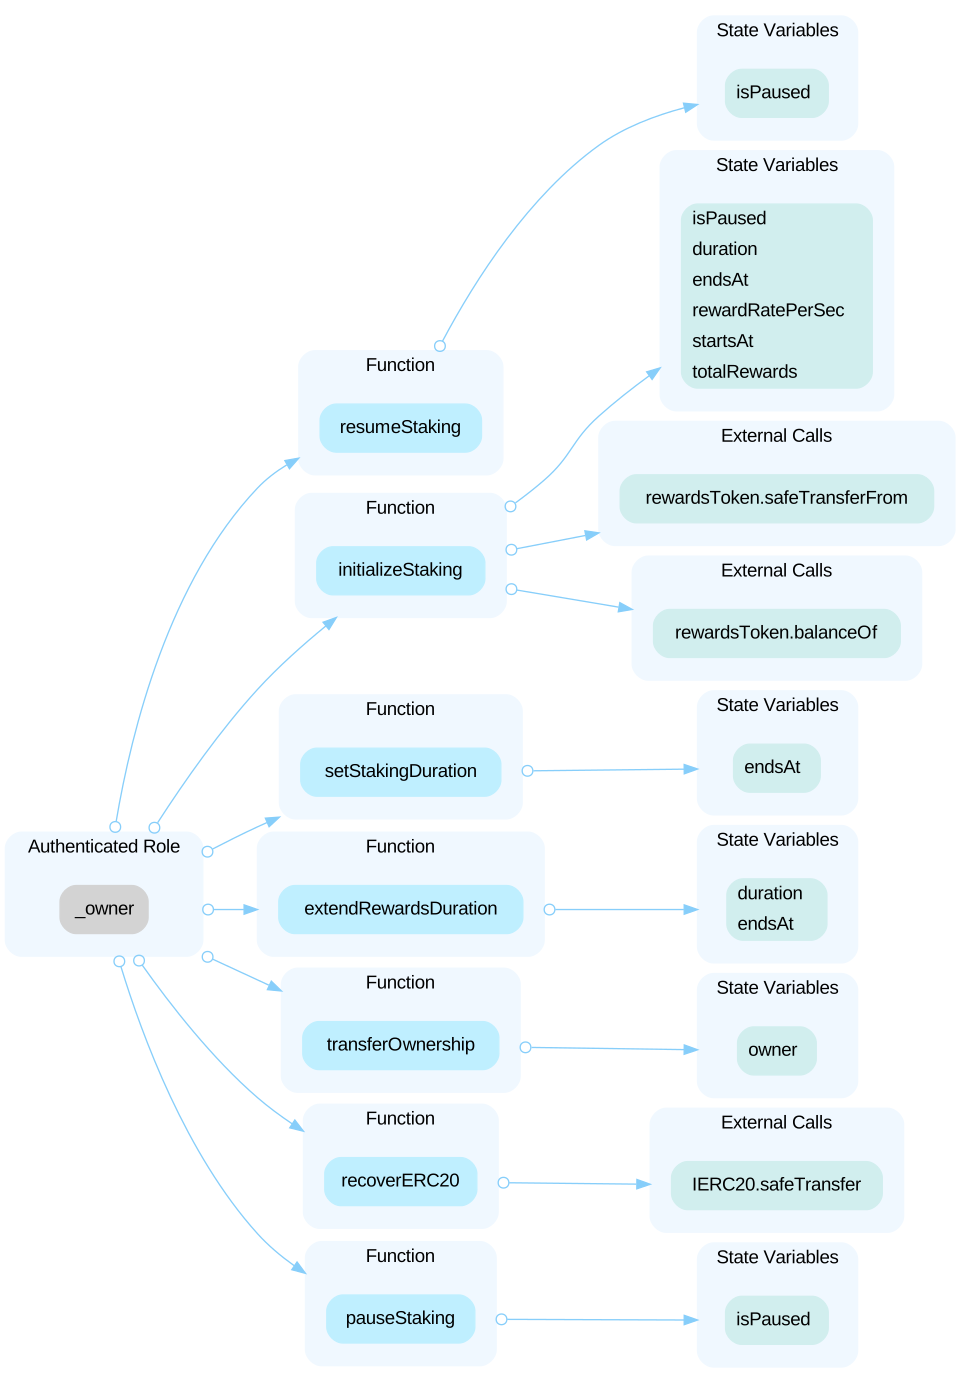
Open the reportHighInitial Token DistributionFlokifi Staking · CertiK · 6 Nov 2023Open
All of the xFLOKI tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportHighCentralization Related RisksFlokifi II · CertiK · 8 Oct 2023Open
In the contract `Whitelist` the role `WHITELIST_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `WHITELIST_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 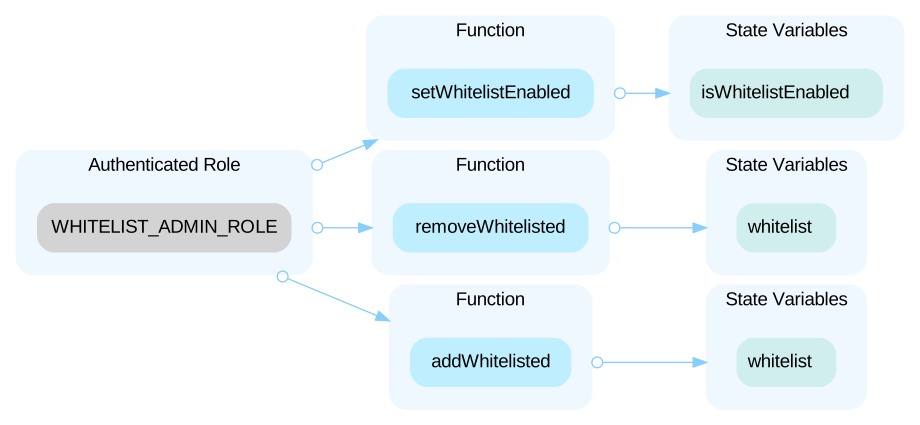 In the contract `PricingModuleV1` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 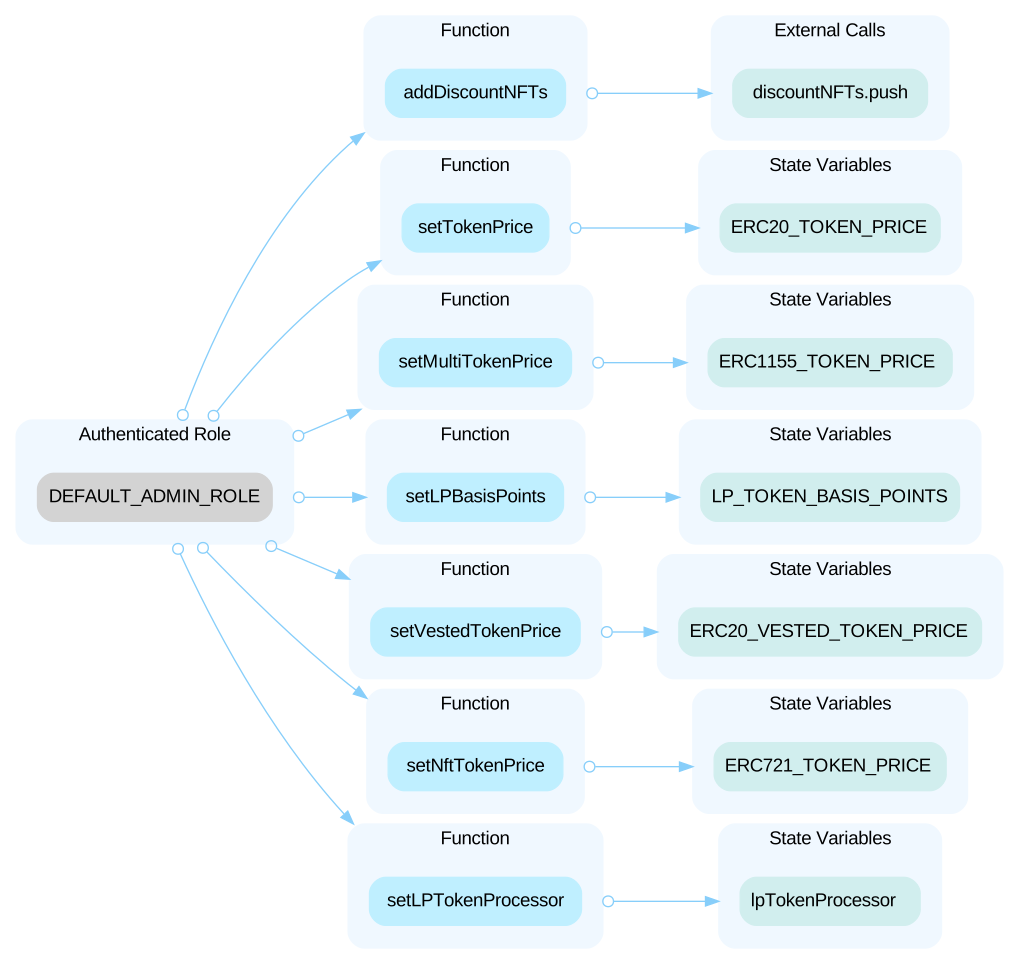 In the contract `ChainlinkPriceConsumer` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 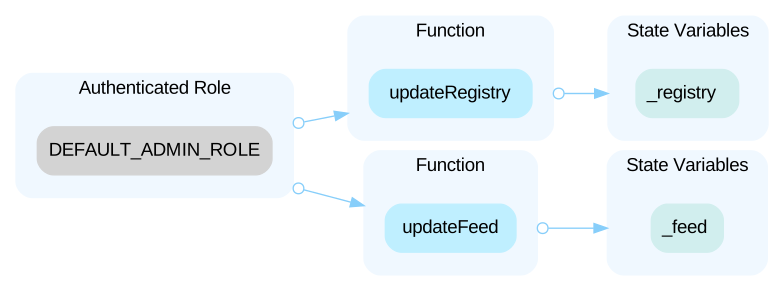 In the contract `ChainlinkPriceConsumer` the role `ORACLE_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ORACLE_MANAGER_ROLE` account may allow the hacker to take advantage of this authority. 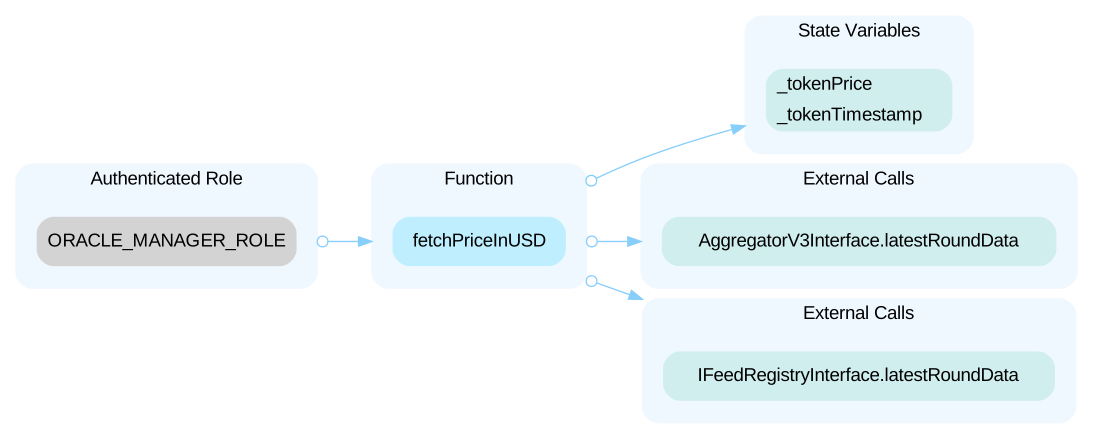 In the contract `DiaPriceConsumer` the role `ORACLE_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ORACLE_MANAGER_ROLE` account may allow the hacker to take advantage of this authority . 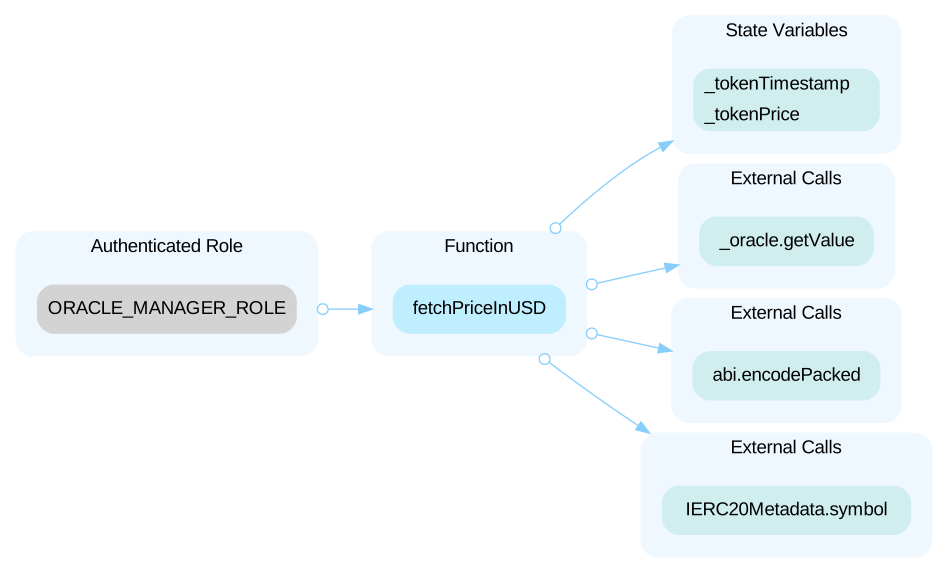 In the contract `ManualPriceConsumer` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority . 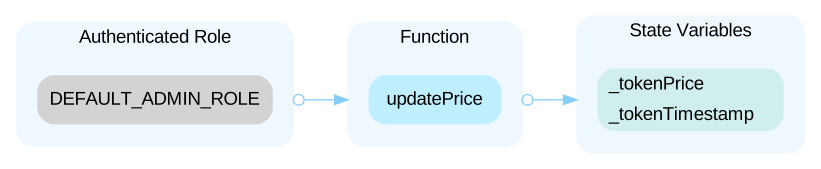 In the contract `PriceOracleManagerV1` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority . 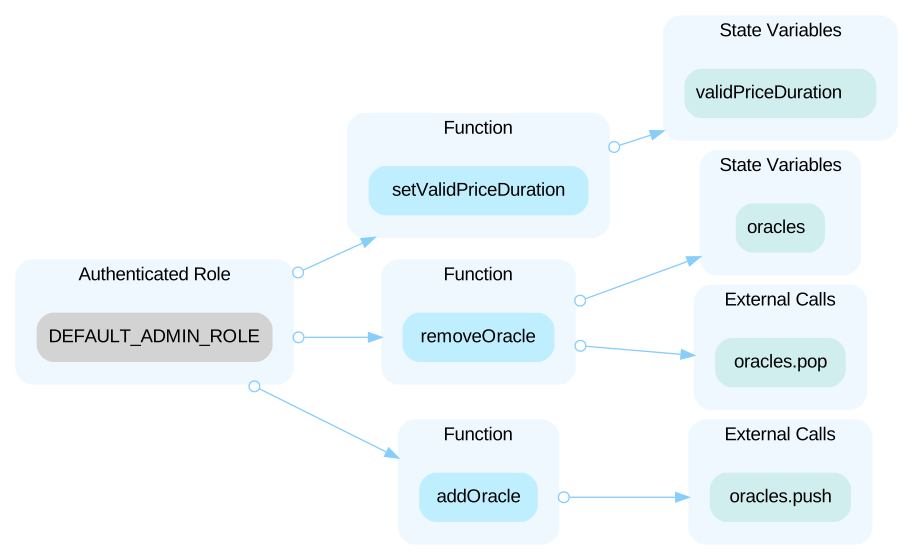 In the contract `PriceOracleManagerV1` the role `ORACLE_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ORACLE_MANAGER_ROLE` account may allow the hacker to take advantage of this authority . 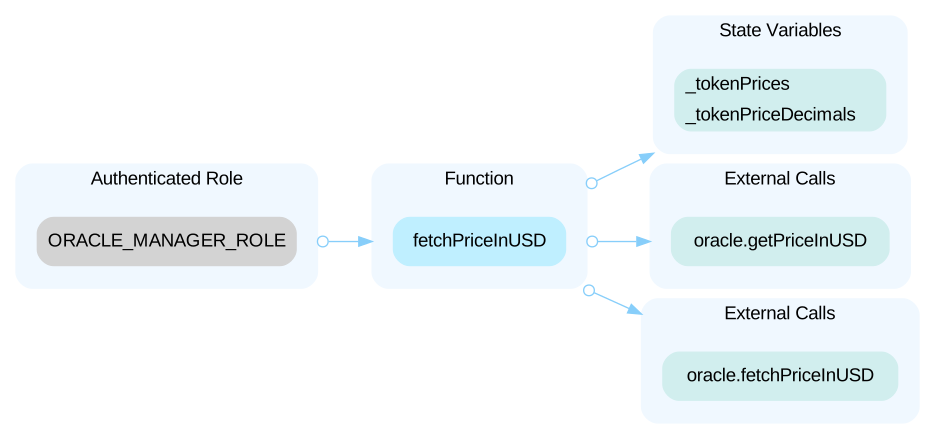 In the contract `PythPriceConsumer` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 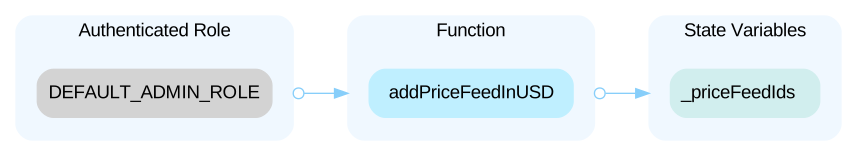 In the contract `PythPriceConsumer` the role `ORACLE_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ORACLE_MANAGER_ROLE` account may allow the hacker to take advantage of this authority. 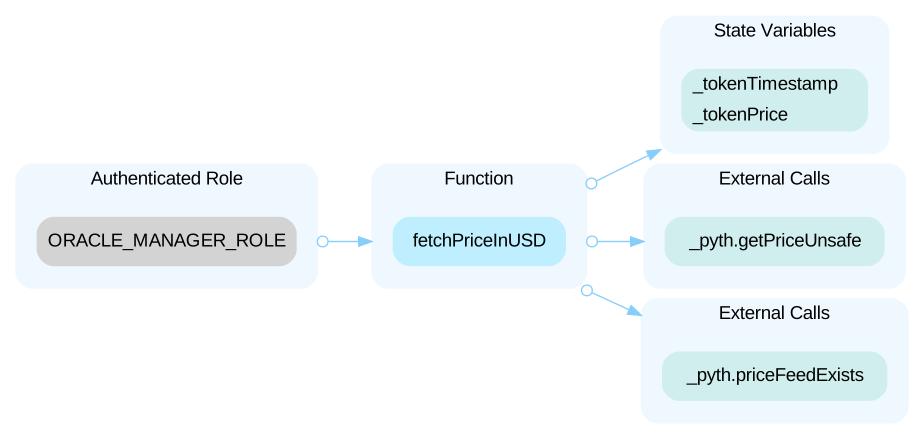 In the contract `VaultDeployer` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 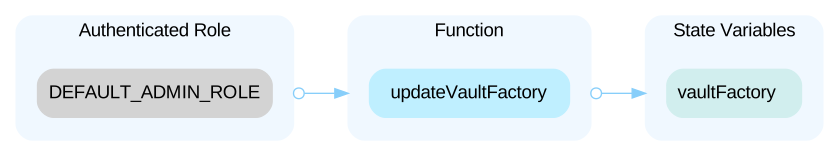 In the contract `VaultDeployer` the role `_fromfactory` has authority over the functions shown in the diagram below. Any compromise to the `_fromfactory` account may allow the hacker to take advantage of this authority. 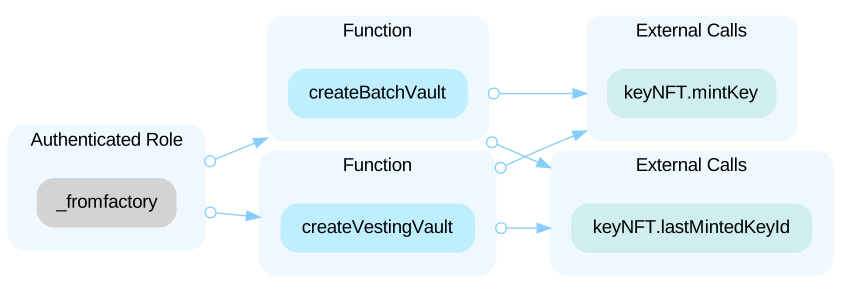 In the contract `VaultDeployer` the role `vaultFactory` has authority over the functions s
Open the reportHighCentralization Related Risks in `DEFAULT_ADMIN_ROFlokifi · CertiK · 14 Mar 2023Open
In the contract `PaymentModuleV1`, the role `DEFAULT_ADMIN_ROLE` has authority over the following functions: - function setLPTokenProcessor(), to set the `lpTokenProcessor`. - function setPricingModule(), to set the `pricingModule`. - function setTreasury(), to set the `treasury`. In the contract `LPTokenProcessorV1`, the role `DEFAULT_ADMIN_ROLE` has authority over the following functions: - function setSellDelay(), to set the `_sellDelay`. In the contract `PricingModuleV1`, the role `DEFAULT_ADMIN_ROLE` has authority over the following functions: - function setLPTokenProcessor(), to set the `lpTokenProcessor`. - function setTokenPrice(), to set the `TOKEN_PRICE`. - function setVestedTokenPrice(), to set the `VESTED_TOKEN_PRICE`. - function setLPBasisPoints(), to set the `LP_TOKEN_BASIS_POINTS`. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority.
Open the reportHighCentralization Related Risks in `LP_ADMIN_ROLE`Flokifi · CertiK · 14 Mar 2023Open
In the contract `LPTokenProcessorV1`, the role `LP_ADMIN_ROLE` has authority over the following functions: - function adminWithdraw(), to withdraw any amount of the ETHs and tokens in the contract to the `LP_ADMIN_ROLE`. - function setMaxSellBatchSize(), to set the `_maxSellBatchSize`. Any compromise to the `LP_ADMIN_ROLE` account may allow a hacker to take advantage of this authority.
Open the reportHighCentralization Related Risks in the contract `VauFlokifi · CertiK · 14 Mar 2023Open
In the contract `VaultFactory`, the role `owner` has authority over the following functions: - function setKeyAddress(), to set the `keyNFT`. - function updatePaymentModule(), to set the `paymentModule`. Any compromise to the `owner` account may allow a hacker to take advantage of this authority.
Open the reportLowThird Party DependencyFlokifi II · CertiK · 8 Oct 2023Open
The contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. In PriceOracleManagerV1 ```solidity function fetchPriceInUSD(address token) external override onlyRole(ORACLE_MANAGER_ROLE) { for (uint256 i = 0; i < oracles.length; i++) { IPriceConsumer oracle = IPriceConsumer(oracles[i]); uint256 minTimestamp = block.timestamp - validPriceDuration; try oracle.fetchPriceInUSD(token, minTimestamp) { (uint256 price, uint256 decimals, uint256 timestamp) = oracle.getPriceInUSD(token); if (block.timestamp - timestamp > validPriceDuration) { // too old, look at the next oracle continue; } _tokenPrices[token] = price; _tokenPriceDecimals[token] = decimals; } catch { // oracle failed, look at the next oracle continue; } } } ``` In the function `fetchPriceInUSD()`, as long as the update time of the price returned by the Oracle is less than validPriceDuration, the price returned by the Oracle may be utilized. As a result, users might manipulate the Oracle to enable the function to use potentially exploitable Oracle instances. Due to the `fetchPriceInUSD()` function being accessible only to the `ORACLE_MANAGER_ROLE`, the likelihood of this scenario occurring is relatively low.
Open the reportLowFinancial ModelsFlokifi · CertiK · 14 Mar 2023Open
In this project, investors could create vaults and deposit ERC20, ERC721, or ERC1155 assets in the `VaultFactory` contract, fees would be charged and these assets would be locked for a period of time, however, it is still unclear how the investors would profit from this project, and we would like the client to provide with more information about it.
Open the reportLowPotential Sandwich AttacksFlokifi · CertiK · 14 Mar 2023Open
A sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (before the transaction being attacked) a transaction to purchase one of the assets and make profits by back running (after the transaction is attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `router.removeLiquidity()` - `router.swapExactTokensForETH()`
Open the reportLowThird Party DependencyFlokifi · CertiK · 14 Mar 2023Open
The contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=20 IUniswapV2Router01 public router; ``` - The contract `LPTokenProcessorV1` interacts with third-party contract with `IUniswapV2Router01` interface via `router`.
Open the reportShow 2 more
LowUnknown implementationsFlokifi · CertiK · 14 Mar 2023Open
There are several unknown implementations in `PricingModuleV1` and `Vault`. - gemstoneNFT.tokenOfOwnerByIndex - genesisNFT.tokenOfOwnerByIndex - vaultKeyContract.ownerOf The scope of the audit treats 3rd party entities as black boxes and assumes their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts.
Open the reportLowUnused Return ValueFlokifi · CertiK · 14 Mar 2023Open
The return value of an external call is not stored in a local or state variable. ```solidity=134 lpToken.approve(address(router), lpBalance); ``` --- ```solidity=137 router.removeLiquidityETH( lpToken.token1(), lpBalance, 0, 0, address(this), block.timestamp ); ``` --- ```solidity=148 router.removeLiquidityETH( lpToken.token0(), lpBalance, 0, 0, address(this), block.timestamp ); ``` --- ```solidity=159 router.removeLiquidity( lpToken.token0(), lpToken.token1(), lpBalance, 0, 0, address(this), block.timestamp ); ``` --- ```solidity=182 token.approve(address(router), tokenBalance); ``` --- ```solidity=183 try router.swapExactTokensForETH( tokenBalance, 0, path, address(this), block.timestamp ) returns (uint256[] memory /* amounts */) { } catch (bytes memory /* lowLevelData */) { } ``` --- ```solidity=179 lpToken.approve(address(router), lpTokenAmount); ``` --- ```solidity=185 router.removeLiquidityETH(lpToken.token1(), lpTokenAmount, 0, 0, address(this), block.timestamp); ``` --- ```solidity=195 router.removeLiquidityETH(lpToken.token0(), lpTokenAmount, 0, 0, address(this), block.timestamp); ``` --- ```solidity=205 router.removeLiquidity( lpToken.token0(), lpToken.token1(), lpTokenAmount, 0, 0, address(this), block.timestamp ); ``` --- ```solidity=246 token.approve(address(router), sourceAmount); ``` --- ```solidity=248 try router.swapExactTokensForETH(sourceAmount, 0, path, address(this), block.timestamp) returns ( uint256[] memory /* amounts */ ) {} catch ( bytes memory /* lowLevelData */ ) { return false; } ``` --- ```solidity=264 try router.swapExactETHForTokens{ value: ETHGained }(0, path, receiver, block.timestamp) returns ( uint256[] memory /* amounts */ ) {} catch ( bytes memory /* lowLevelData */ ) { return false; } ``` --- ```solidity=171 try gemstoneNFT.tokenOfOwnerByIndex(user, 0) returns (uint256) { return true; } catch ( bytes memory /* lowLevelData */ ) {} ``` --- ```solidity=177 try genesisNFT.tokenOfOwnerByIndex(user, 0) returns (uint256) { return true; } catch ( bytes memory /* lowLevelData */ ) {} ```
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="flokifi"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us