Biswap v3 amm (audit)
CertiK reviewed Biswap (Biswap v3 amm (audit)) on 5 Sep 2023: 24 findings, 0 critical; 16 marked fixed, 8 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings24
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 6 |
| Low | 6 | 0 | 10 |
HighCentralization related RisksOpen
In the contract `BiswapFactoryV3` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority . 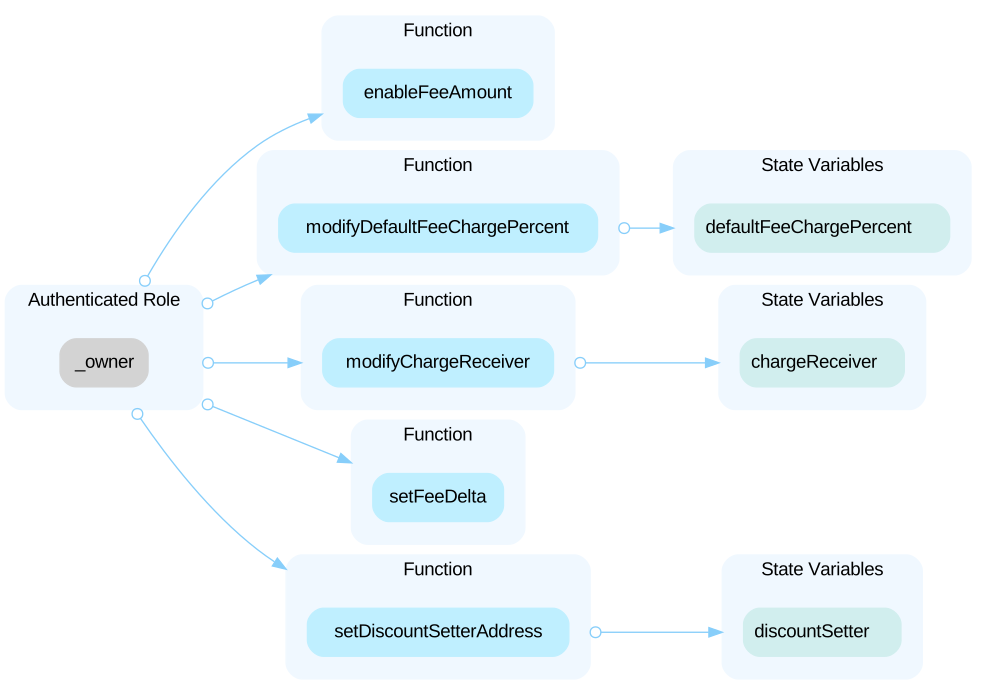 In the contract `BiswapFactoryV3` the role `discountSetter` has authority over the functions shown in the diagram below. Any compromise to the `discountSetter` account may allow the hacker to take advantage of this authority. 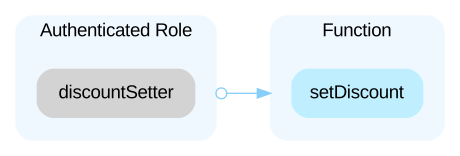 In the contract `LiquidityManager` the role `_owner` has authority over the functions below: - function `setBaseURI` - function `setBonusPoolManager` Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. In the contract BiswapPoolV3, the role `owner` in contract `factory` has authority over the following functions: - function `modifyFeeChargePercent()` Any compromise to the account may allow a hacker to take advantage of this authority. In the contract BiswapPoolV3, the role `chargeReceiver` in contract `factory` has authority over the following functions: - function `collectFeeCharged()` Any compromise to the account may allow a hacker to take advantage of this authority. In the contract FarmsDistributor, the role `DEFAULT_ADMIN_ROLE` has authority over the following functions: - function `init()` - function `pause()` - function `unpause()` - function `emergencyWithdraw()` Any compromise to the account may allow a hacker to take advantage of this authority. In the contract FarmsDistributor, the role `FARMS_MANAGER_ROLE` has authority over the following functions: - function `setFarmsRatio()` Any compromise to the account may allow a hacker to take advantage of this authority.
HighCentralization Risk in Pausable.solOpen
Function `setPause` allows owner to pause the contract. Any functions in contract that inherits Switch.sol and uses notPause modifier can be paused/unpaused by the owner.
Low`liquidities[0]` is emptyOpen
`liquidities` stores mapping from nftId to Liquidity struct. The values in `liquidities[lid]` are firstly assigned in function `mintWithFeeVote. Usually this type of mapping would start from 0, while line 190 initializes `lid` as 1.
LowConfusing `payable` UsageOpen
The team adds a `payable` modifier for function `createPool` in the latest commit, while the function doesn't use `msg.value`.
LowLack Of Access ControlOpen
The function sweepToken can be called by anyone as it has no access restriction. This enables anyone to call this and transfer all tokens from the contract to any address.
LowOut of Scope ImplementationsOpen
There are several unknown implementations in this protocol: - hook(uint256,address,uint128,int24,int24) in bonusPoolManager - MASTER_CHEF.withdraw The contract `bonusPoolManager` and contract `MASTER_CHEF` are out of audit scope.
LowPotential to manipulate the fee rate by flashloanOpen
In Biswap V3, liquidity providers can influence the fee rate of the pool in real-time. A low fee rate would decrease the profits of liquidity providers. Thus the auditors are wondering about the purpose of allowing liquidity providers to change the fee selection range. i.e. why would a liquidity provider select a low fee rate. A user could flash loan a large number of tokens to be the main liquidity provider and vote for a low fee selection range. If the fee for flashloan is lower than the difference between the old and new fee rates in the pool, the user can gain profits from this.
LowThird-Party DependenciesOpen
The contract is serving as the underlying entity to interact with third-party token X and token Y contracts. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. The token transfer calls are executed through the `TokenTransfer` library, using the `.call()` function. ```solidity function transferToken( address tokenAddr, address toAddr, uint256 amount ) internal { (bool ok, bytes memory retData) = tokenAddr.call(abi.encodeWithSelector(IERC20Minimal.transfer.selector, toAddr, amount)); require(ok && (retData.length == 0 || abi.decode(retData, (bool))), 'TNS'); } ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (37)
- contracts/core/liquidity.sol
- contracts/libraries/PointBitmap.sol
- contracts/core/swapX2Y.sol
- contracts/libraries/TwoPower.sol
- contracts/periphery/LimitOrderManager.sol
- contracts/periphery/LiquidityManager.sol
- contracts/libraries/SwapCache.sol
- contracts/libraries/TokenTransfer.sol
- contracts/libraries/Oracle.sol
- contracts/libraries/LimitOrder.sol
- contracts/libraries/SwapMathX2YDesire.sol
- contracts/core/swapY2X.sol
- contracts/core/flash.sol
- contracts/libraries/DeployPool.sol
- contracts/core/BiswapPoolV3.sol
- contracts/libraries/Converter.sol
- contracts/libraries/AmountMath.sol
- contracts/libraries/SwapMathY2XDesire.sol
- contracts/libraries/BytesLib.sol
- contracts/libraries/OrderOrEndpoint.sol
- contracts/core/FarmsDistributor.sol
- contracts/core/limitOrder.sol
- contracts/libraries/Path.sol
- contracts/libraries/Liquidity.sol
- contracts/libraries/MintMath.sol
- contracts/libraries/UserEarn.sol
- contracts/libraries/SwapMathX2Y.sol
- contracts/libraries/LogPowMath.sol
- contracts/libraries/MaxMinMath.sol
- contracts/libraries/BiswapOracle.sol
- contracts/libraries/MulDivMath.sol
- contracts/libraries/State.sol
- contracts/libraries/LimOrderCircularQueue.sol
- contracts/libraries/Point.sol
- contracts/libraries/SwapMathY2X.sol
- contracts/core/BiswapFactoryV3.sol
- contracts/libraries/LimOrder.sol
Part of Biswap’s security record
 Biswap
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us