Incident
Incident,
Source: De.Fi incident database.
- Audits before it
- 1.
- Audits since
- 1, the latest dated 5 Sep 2023.

Biswap has 2 public audit reports from CertiK; the latest is CertiK, 5 Sep 2023; no critical findings reported. It also holds 1 incident (latest 29 Jun 2023).
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Statuses are the security firms’ own
18 findings are still open or acknowledged in the firms’ reports: 2 high, 3 medium, 13 low (all open).
Centralization related Risks
Biswap v3 amm (audit) · CertiK · 5 Sep 2023 · Report ↗
Centralization Risk in Pausable.sol
Biswap v3 amm (audit) · CertiK · 5 Sep 2023 · Report ↗
`add()` function not restricted
Biswap · CertiK · 9 Jun 2021 · Report ↗
Delegation Not Moved Along With `transfer()`
Biswap · CertiK · 9 Jun 2021 · Report ↗
Proper Usage on migrator.migrate()
Biswap · CertiK · 9 Jun 2021 · Report ↗
`liquidities[0]` is empty
Biswap v3 amm (audit) · CertiK · 5 Sep 2023 · Report ↗
Confusing `payable` Usage
Biswap v3 amm (audit) · CertiK · 5 Sep 2023 · Report ↗
Lack Of Access Control
Biswap v3 amm (audit) · CertiK · 5 Sep 2023 · Report ↗
Out of Scope Implementations
Biswap v3 amm (audit) · CertiK · 5 Sep 2023 · Report ↗
Potential to manipulate the fee rate by flashloan
Biswap v3 amm (audit) · CertiK · 5 Sep 2023 · Report ↗
Attached through a shared contract address. Our incident data ends in Nov 2026.
Source: De.Fi incident database.
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Biswap v3 amm (audit) | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 2 high · 6 medium · 16 low 16 fixed · 8 open | skynet.certik.com ↗ |
| Biswap | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 3 medium · 7 low 10 open | skynet.certik.com ↗ |
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 3 | 0 | 6 |
| Low | 13 | 0 | 10 |
In the contract `BiswapFactoryV3` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority . 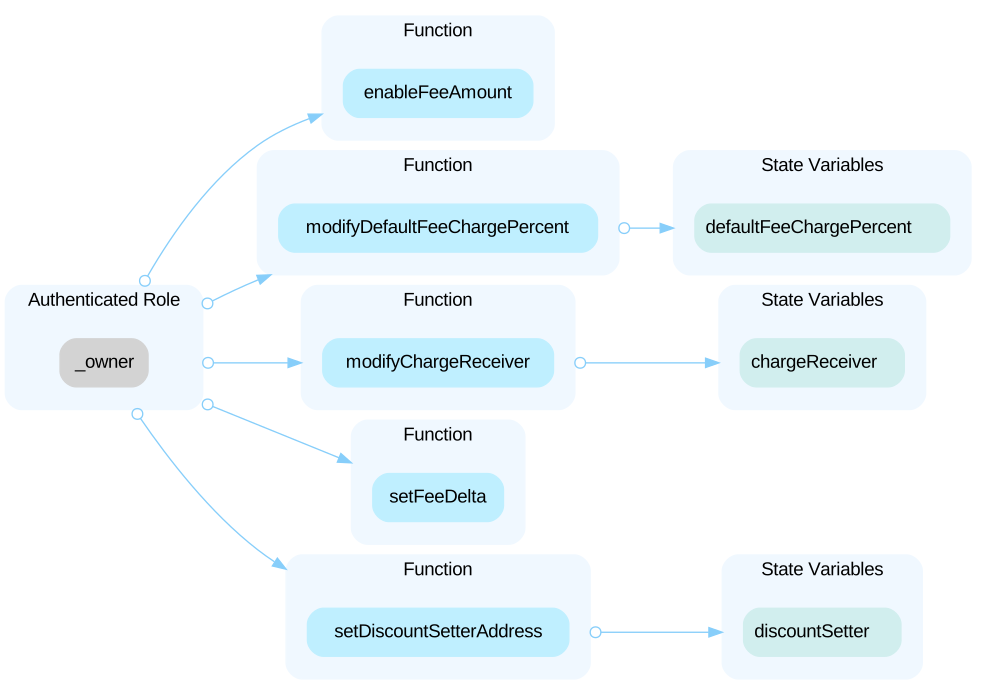 In the contract `BiswapFactoryV3` the role `discountSetter` has authority over the functions shown in the diagram below. Any compromise to the `discountSetter` account may allow the hacker to take advantage of this authority. 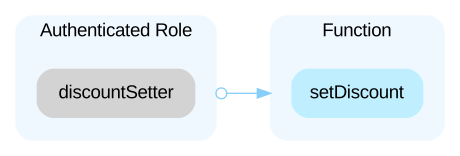 In the contract `LiquidityManager` the role `_owner` has authority over the functions below: - function `setBaseURI` - function `setBonusPoolManager` Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. In the contract BiswapPoolV3, the role `owner` in contract `factory` has authority over the following functions: - function `modifyFeeChargePercent()` Any compromise to the account may allow a hacker to take advantage of this authority. In the contract BiswapPoolV3, the role `chargeReceiver` in contract `factory` has authority over the following functions: - function `collectFeeCharged()` Any compromise to the account may allow a hacker to take advantage of this authority. In the contract FarmsDistributor, the role `DEFAULT_ADMIN_ROLE` has authority over the following functions: - function `init()` - function `pause()` - function `unpause()` - function `emergencyWithdraw()` Any compromise to the account may allow a hacker to take advantage of this authority. In the contract FarmsDistributor, the role `FARMS_MANAGER_ROLE` has authority over the following functions: - function `setFarmsRatio()` Any compromise to the account may allow a hacker to take advantage of this authority.
Open the reportFunction `setPause` allows owner to pause the contract. Any functions in contract that inherits Switch.sol and uses notPause modifier can be paused/unpaused by the owner.
Open the reportThe total amount of reward BSWReward in function `updatePool()` will be incorrectly calculated if the same LP token is added into the pool more than once in function `add()`. However, the code is not reflected in the comment behaviors as there isn’t any valid restriction on preventing this issue. The current implementation relies on the owner's trust to avoid repeatedly adding the same LP token to the pool, as the function will only be called by the owner.
Open the reportThe voting power of delegation is not moved from token sender to token recipient along with the `transfer()`. Current `transfer()` is from `BEP20` protocol and don't invoke `_moveDelegates()`.
Open the report`setMigrator()` function can set migrator contract to any contract that is implemented from `IMigratorChef` interface by the owner. As result, invocation of `migrator.migrate()` in function migrate() may bring dangerous effects as it is unknown to the user. However, the project may lose the ability to upgrade and migrate if `setMigrator()` and `migrate()` are removed.
Open the report`liquidities` stores mapping from nftId to Liquidity struct. The values in `liquidities[lid]` are firstly assigned in function `mintWithFeeVote. Usually this type of mapping would start from 0, while line 190 initializes `lid` as 1.
Open the reportThe team adds a `payable` modifier for function `createPool` in the latest commit, while the function doesn't use `msg.value`.
Open the reportThe function sweepToken can be called by anyone as it has no access restriction. This enables anyone to call this and transfer all tokens from the contract to any address.
Open the reportThere are several unknown implementations in this protocol: - hook(uint256,address,uint128,int24,int24) in bonusPoolManager - MASTER_CHEF.withdraw The contract `bonusPoolManager` and contract `MASTER_CHEF` are out of audit scope.
Open the reportIn Biswap V3, liquidity providers can influence the fee rate of the pool in real-time. A low fee rate would decrease the profits of liquidity providers. Thus the auditors are wondering about the purpose of allowing liquidity providers to change the fee selection range. i.e. why would a liquidity provider select a low fee rate. A user could flash loan a large number of tokens to be the main liquidity provider and vote for a low fee selection range. If the fee for flashloan is lower than the difference between the old and new fee rates in the pool, the user can gain profits from this.
Open the reportThe contract is serving as the underlying entity to interact with third-party token X and token Y contracts. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. The token transfer calls are executed through the `TokenTransfer` library, using the `.call()` function. ```solidity function transferToken( address tokenAddr, address toAddr, uint256 amount ) internal { (bool ok, bytes memory retData) = tokenAddr.call(abi.encodeWithSelector(IERC20Minimal.transfer.selector, toAddr, amount)); require(ok && (retData.length == 0 || abi.decode(retData, (bool))), 'TNS'); } ```
Open the reportThe function that affects the status of sensitive variables should be able to emit events as notifications to customers. - `dev()` - `setMigrator()` - `updateBswPerBlock()`
Open the reportBSWToken is the standard BEP20 implementation that contains the mint functionality with ownership controls, which means whoever obtained access to the minter account would be able to tamper with the integrity of the token economics.
Open the reportThe owner of MasterChef has permission to add and set pools that could update the parameters on rewards without obtaining the consensus of the community.
Open the reportThere's no sanity check to validate if a pool is existing.
Open the reportRole of onlyMinter() is not set correctly, no initial Minter was set.
Open the reportThird party function ISwapFeeReward(swapFeeReward).swap(msg.sender, input, output, amountOut) was called in _swap(). The contract is serving as the underlying entity to interact with third party functions. The scope of the audit would treat those 3rd party entities as black boxes and assume its functional correctness. However in the real world, 3rd parties may be compromised that led to assets lost or stolen.
Open the report_devFee was defined as "uint32" in function setDevFee(uint32 _devFee), while "uint8" in BiswapFactory.sol: function setDevFee(address _pair, uint8 _devFee) external
Open the reportThe reports name a repository or files. Open a report to see its scope.
Trustblock holds 2 public audit reports for Biswap, dated 9 Jun 2021 to 5 Sep 2023. The latest is by CertiK (“Biswap v3 amm (audit)”).
CertiK wrote the 2 reports Trustblock holds for Biswap.
18 findings are still open or acknowledged in the firms’ reports: 2 high, 3 medium, 13 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="biswap"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us