BlackFort Group
CertiK reviewed BXN (BlackFort Group) on 13 Oct 2022: 49 findings, 3 critical; 43 marked fixed, 6 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings49
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 3 |
| High | 1 | 0 | 2 |
| Medium | 1 | 0 | 5 |
| Low | 4 | 0 | 33 |
HighCentralization Related RisksOpen
In the contract `AccessControlHub` the role `DEFAULT_ADMIN_ROLE_ADDRESS` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE_ADDRESS` account may allow the hacker to take advantage of this authority and change the address for privileged roles such as `ACCESS_CONTROL_MANAGER_ROLE`, and any of the roles in contracts that inherit from `SystemAccess` contract. In addition, any compromise to the `ACCESS_CONTROL_MANAGER_ROLE` account may allow the hacker to enable or disable the `transfer()` function for certain contracts. 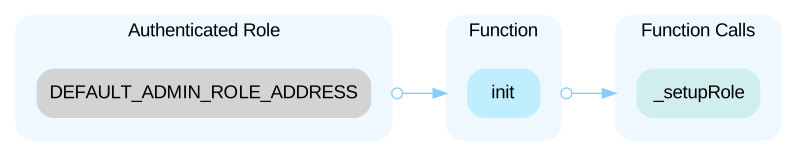 In the contract `System.sol`, any compromise to the `SYSTEM_MANAGER_ROLE` account may allow the hacker to approve any account to use the `transferTo()` function to send any amount of native token to an address of their choosing. Additionally, an address with the `VOTE_MINT_ROLE` can use this same function to mint any amount of `VoteHub` tokens to any address. In the contract `NodeHub`, any compromise to the `NODE_MANAGER_ROLE` account may allow the hacker to set `_baseTokenURI` to any string and use the `lock()` and `unlock()` functions on the underlying token to prevent transfers. In the contract `PollHub` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, modify the information of poll such as its poll options and its deadline. Note that the `_owner` in this case refers to the owner of the specified `tokenId` representing a poll. Each instance of a poll represents a centralization risk. In addition, any compromise to the `POLL_MANAGER_ROLE` account may allow the hacker to reset `_baseTokenURI` and change a poll's price and fee to an unwanted amount. 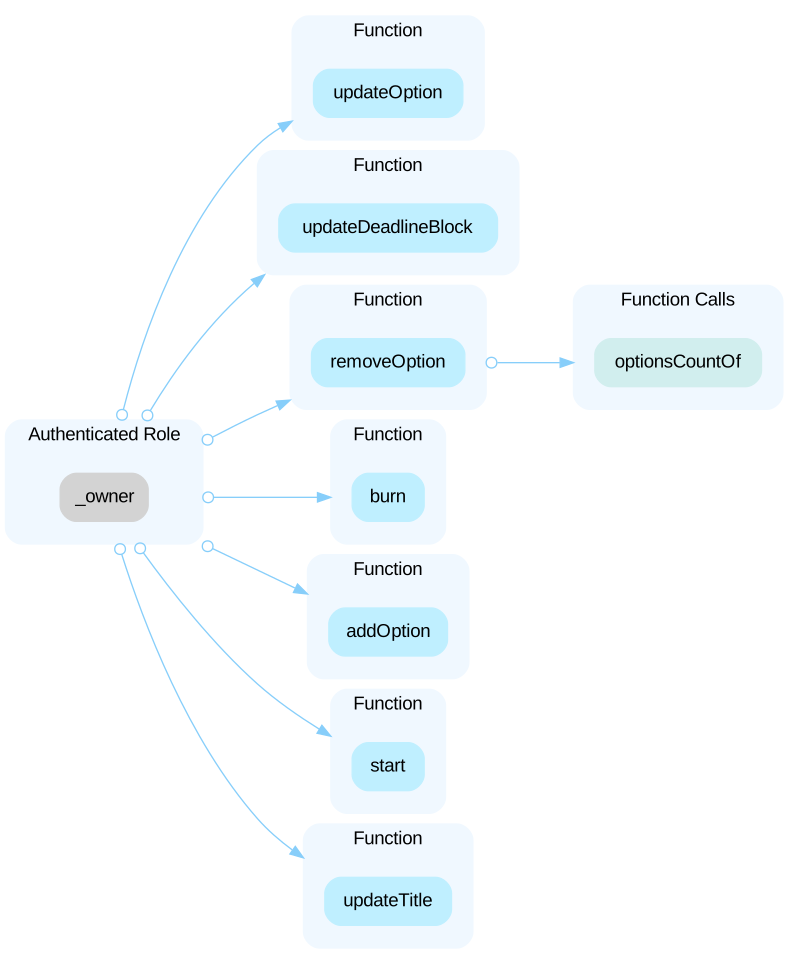 In the contract `BXP20SystemRewardToken` the role `SYSTEM_CONTRACT_ADDRESS` has authority over the functions shown in the diagram below. Any compromise to the `SYSTEM_CONTRACT_ADDRESS` account may allow the hacker to take advantage of this authority and mint any amount of tokens to any address within the contracts that inherit from this base; that is the `DelegatorHub` and `ValidatorHub` contracts 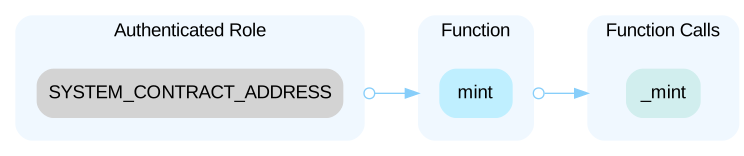 In the contract `BXP20Asset`, which inherits from the contract `BlackList`, any compromise to the `ASSET_BLACKLIST_MANAGER_ROLE` account may allow the hacker to add addresses to the blacklist. The contract `BXP20Asset` also inherits from the contract `Manageable`; any compromise to the `ASSET_MANAGER_ROLE` account may allow the hacker to mint and burn any amount of tokens for any address. The role `VALIDATOR_MANAGER_ROLE` has control over several contracts. In the contract `CandidateHub`, any compromise to the `VALIDATOR_MANAGER_ROLE` account may allow a hacker to add candidates to the validator set, remove candidates maliciously and set `requiredAmount` to any amount. In the contract `SlashingHub`, compromise to this role allows a hacker to use the `slash()` function to penalize rewards for a validator address. In the contract `ValidatorHub`, this may also allow the hacker to use the function `kick()` to remove any validator from the list. In the contract `VoteHub`, any compromise to the `VOTE_MINT_ROLE` account may allow the hacker to mint any amount of `VoteHub` tokens to any account and any compromise to the `VOTE_BURN_ROLE` account may allow the hacker to burn any amount of `VoteHub` tokens. In addition, any compromise to the `VOTE_SPENDER_ROLE` may allow the hacker to spend all the `VoteHub` tokens belonging to any account.
MediumNo Validation for String input in `approve()`Open
In the `approve()` function, an address has an associated string input `name` that the `account` address is associated to in the mapping `_accounts`. There is no validation check that that the mapping `_accounts` for entry `name` is already occupied. From context, it appears the `approve()` function assigns a contract `name` to in-house contracts addresses, to be used for validation checks in other contracts. If an externally owned address is approved through this function, the address can directly interact with the `transferTo()` address, which sends out native BXN tokens to specified addresses. Moreover, any updates to the address corresponding to a given `name` using the `approve()` function causes the previous address to immediately lose privileged access. Lastly, there is no check that the input `name` is a mapping that is used within other contracts. If the `name` is incorrectly input, then the corresponding checks using the `onlyContract` modifier will not allow a contract to interact.
LowCheck Effect Interaction Pattern ViolatedOpen
The order of external calls or transfers and storage manipulation must follow the check-effect-interaction pattern to keep contract logic safe from exploitation. ### External call(s) ```solidity=45 ValidatorHub.join{value:amount}(account); ``` ### State variables written after the call(s) ```solidity=46 _candidatesBonds[account] = _candidatesBonds[account].sub(amount); ``` --- ### External call(s) ```solidity=169 VoteHub.mint(owner, nodePrice.div(100)); ``` ### State variables written after the call(s) ```solidity=180 amount = amount.sub(nodePrice); ``` --- ### External call(s) ```solidity=244 delegate(address(0), tokenId); ``` * This function call executes the following external call(s). * In `NodeHub.delegate`, * `DelegatorHub.burnExtraFor(tokenId)` * In `NodeHub.delegate`, * `DelegatorHub.decreaseDelegatedAmountFor(currentValidator,tokenId)` * In `NodeHub.delegate`, * `DelegatorHub.increaseDelegatedAmountFor(validatorAddress,tokenId)` * This call sends Ether. ```solidity=247 _burnFrom(from, reward - burnedByFrom); ``` * This function call executes the following external call(s). * In `NodeHub._burnFrom`, * `_getSystemContractInstance().transferTo(owner,amount)` * This call sends Ether. ### State variables written after the call(s) ```solidity=253 super._beforeTokenTransfer(from, to, tokenId); ``` * This function call executes the following assignment(s). * In `BXP721Enumerable._addTokenToAllTokensEnumeration`, * `_allTokens.push(tokenId)` * In `BXP721Enumerable._removeTokenFromAllTokensEnumeration`, * `_allTokens[tokenIndex] = lastTokenId` * In `BXP721Enumerable._removeTokenFromAllTokensEnumeration`, * `_allTokens.pop()` ```solidity=253 super._beforeTokenTransfer(from, to, tokenId); ``` * This function call executes the following assignment(s). * In `BXP721Enumerable._addTokenToAllTokensEnumeration`, * `_allTokensIndex[tokenId] = _allTokens.length` * In `BXP721Enumerable._removeTokenFromAllTokensEnumeration`, * `_allTokensIndex[lastTokenId] = tokenIndex` * In `BXP721Enumerable._removeTokenFromAllTokensEnumeration`, * `delete _allTokensIndex[tokenId]` ```solidity=253 super._beforeTokenTransfer(from, to, tokenId); ``` * This function call executes the following assignment(s). * In `BXP721Enumerable._addTokenToOwnerEnumeration`, * `_ownedTokensIndex[tokenId] = length` * In `BXP721Enumerable._removeTokenFromOwnerEnumeration`, * `_ownedTokensIndex[lastTokenId] = tokenIndex` * In `BXP721Enumerable._removeTokenFromOwnerEnumeration`, * `delete _ownedTokensIndex[tokenId]` --- ### External call(s) ```solidity=54 (bool result,) = account.call{value:amount}(""); ``` ### State variables written after the call(s) ```solidity=56 _candidatesBonds[account] = _candidatesBonds[account].sub(amount); _candidates.remove(account); ``` --- ### External call(s) ```solidity=173 VoteHub.burn(msg.sender, amountOfVote.sub(fee)); VoteHub.transferFrom(msg.sender, ownerOf(tokenId), fee); VoteHub.burn(ownerOf(tokenId), fee); ``` ### State variables written after the call(s) ```solidity=177 _pollVoteAmount[tokenId][optionId] = _pollVoteAmount[tokenId][optionId].add(amountOfVote); _pollTotalVoteAmount[tokenId] = _pollTotalVoteAmount[tokenId].add(amountOfVote); ```
LowLogic issue when adding users to candidatesOpen
A user can send the `requiredAmount` of BXN to the contract `CandidateHub` to become a candidate. Since the function `receive()` only checks the identity of a validator, candidates can trigger this function more than once. Although the validation on sent value `amount` is to check the cumulative total amount sent from a user, `_candidatesBonds[account]` is actually equal to 0 when a user triggers the function for the first time, meaning that a user has to pay at least the `requiredAmount` of BXN the first time. After that, they can send any amount they want to increase their bonds while adding a user to a candidate would be performed multiple times with `false` returned each time. We speculate that this validation is supposed to allow the user to send tokens multiple times before becoming a candidate until the required number is reached at which point, they will be added to the candidates set. ```solidity=25 receive() external payable { address account = msg.sender; uint256 amount = msg.value; IValidatorHub ValidatorHub = IValidatorHub(_getAddressOf("VALIDATOR_HUB")); require(!ValidatorHub.isValidator(msg.sender), "CandidateHub: you're already validator"); require( _candidatesBonds[account].add(amount) >= requiredAmount, "CandidateHub: you don't have enough amount of tokens to become candidate" ); _candidates.add(account); _candidatesBonds[account] = _candidatesBonds[account].add(amount); } ```
LowNon-adherence to `AccessControl` instructionsOpen
The method for checking an address has a role is set up to use a string input in the function `hasRole()` within `SystemAccess`. This function calls into `AccessControlHub` which inherits from OpenZeppelin's `AccessControl` contract. The function `hasStringRole()` in `AccessControlHub` calls `hasRole()` from `AccessControl` by first taking the string input `role`, converting it to bytes, then applying `keccak256` hash to the outcome. This method is inefficient since this conversion must take place each time a privileged role is checked in a contract that inherits from `SystemAccess`. Worse, there could be unforeseen vulnerabilities as a result of bypassing the instructions for set up in `AccessControl`.
LowUnderflow Vulnerability through use of signed intOpen
The `balanceOf()` function is overridden from the base `BXP20` contract, where the balance is calculated by first adding the amount minted and amount recorded in `_balances` for an account as signed integers. This value is converted to an unsigned integer and the amount burned by the address is subtracted. If the contract logic allows for the absolute value of `_balances[account]` to be larger than the value of `mintedBy(account)` while `_balances[account]` is a negative value, this will lead to an underflow. Consider the following set up: Let `_balances[account]` = -2 and `mintedBy(account)` = 1. The sum of the two values is -1 and when that value is converted to an unsigned integer, it causes an underflow, reading the value as 2^256 - 1 instead. The account accomplishing this now has access to an amount larger than what they actually own.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (33)
- contracts/BXP/BXP165.sol
- contracts/System.sol
- contracts/BXP/BXP721.sol
- contracts/interfaces/ISlashingHub.sol
- contracts/extensions/SystemAccess.sol
- contracts/VoteHub.sol
- contracts/interfaces/IValidatorHub.sol
- contracts/CandidateHub.sol
- contracts/extensions/BXP20SystemRewardToken.sol
- contracts/BXP/interfaces/IBXP20Metadata.sol
- contracts/DelegatorHub.sol
- contracts/BXP/BXP20.sol
- contracts/BXP/WBXN.sol
- contracts/extensions/ExtendedMath.sol
- contracts/ValidatorHub.sol
- contracts/interfaces/IDelegatorHub.sol
- contracts/BXP/BXP20Asset.sol
- contracts/BXP/interfaces/IBXP721.sol
- contracts/BXP/interfaces/IBXP721Metadata.sol
- contracts/BXP/interfaces/IBXP20.sol
- contracts/NodeHub.sol
- contracts/interfaces/IAccessControlHub.sol
- contracts/BXP/interfaces/IBXP721Receiver.sol
- contracts/BXP/interfaces/IBXP721Enumerable.sol
- contracts/interfaces/IBXP20SystemRewardToken.sol
- contracts/BXP/interfaces/IBXP165.sol
- contracts/interfaces/INodeHub.sol
- contracts/interfaces/ISystem.sol
- contracts/PollHub.sol
- contracts/SlashingHub.sol
- contracts/interfaces/IVoteHub.sol
- contracts/AccessControlHub.sol
- contracts/BXP/BXP721Enumerable.sol
Part of BXN’s security record
 BXN
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us