Solv Protocol stUSD - Audit
CertiK reviewed Solv Protocol (Solv Protocol stUSD - Audit) on 28 Dec 2023: 8 findings, 0 critical; 4 marked fixed, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings8
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 1 |
| Medium | 1 | 0 | 1 |
| Low | 1 | 0 | 2 |
HighCentralization Related RisksOpen
In the contract `GovernorControl` the role `governor` has authority over the functions shown in the diagram below. Any compromise to the `governor` account may allow the hacker to take advantage of this authority and set the pending governor's address. 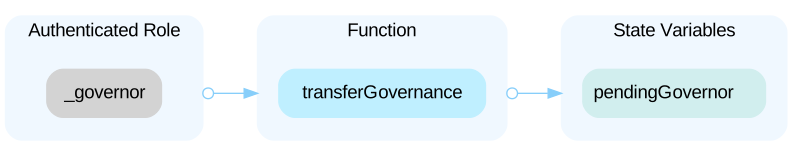 In the contract `GovernorControl` the role `pendinggovernor` has authority over the functions shown in the diagram below. Any compromise to the `pendinggovernor` account may allow the hacker to take advantage of this authority and set the governor's address. 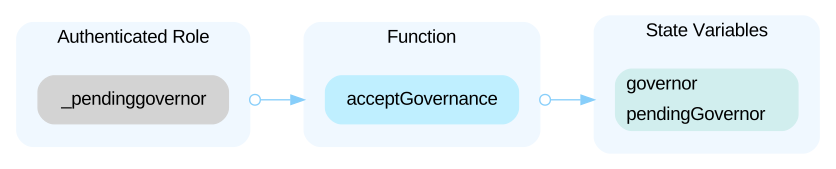 ----- In the contract `AdminControl` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and set the pending admin's address. 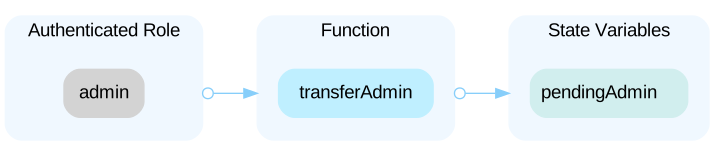 In the contract `AdminControl` the role `pendingAdmin` has authority over the functions shown in the diagram below. Any compromise to the `pendingAdmin` account may allow the hacker to take advantage of this authority and set the admin's address. 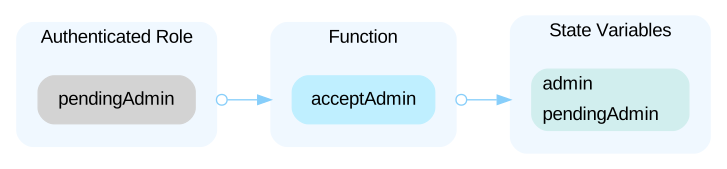 ----- In the contract `SftWrappedTokenFactory` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and - set the implementation address - deploy the Beacon proxy - upgrade the implementation of the Beacon proxy - transfer the ownership of the Beacon proxy to the new owner 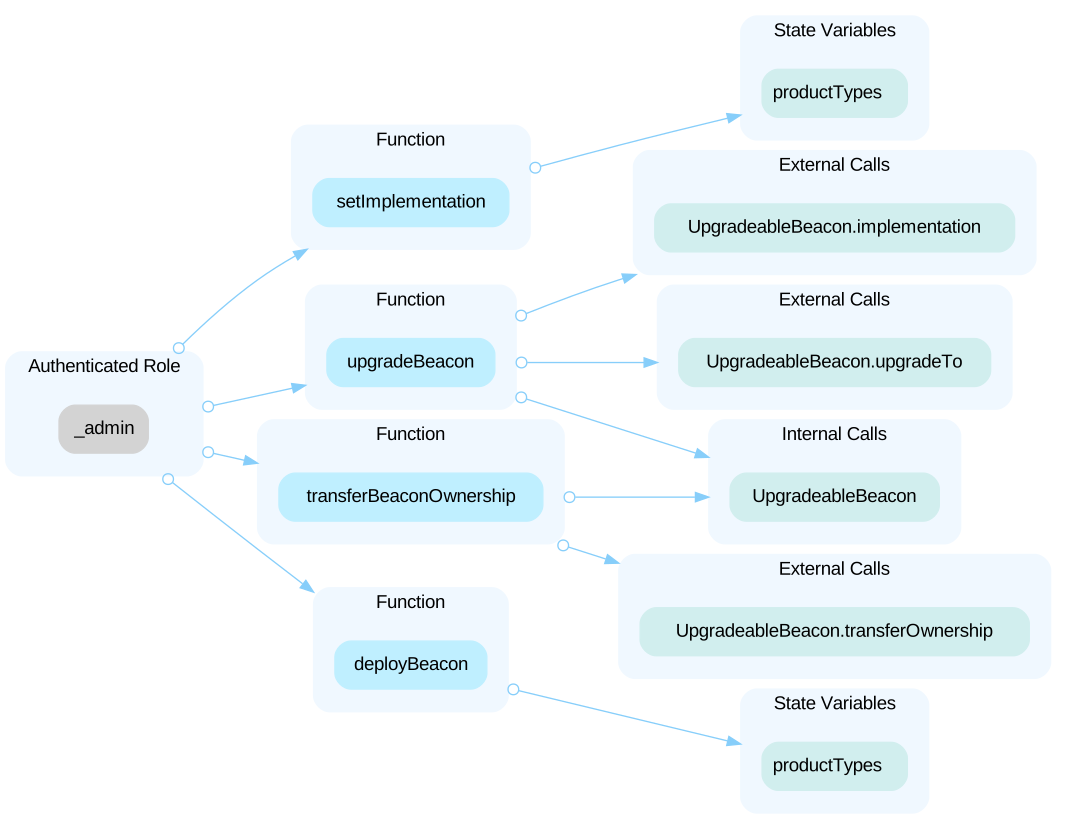 In the contract `SftWrappedTokenFactory` the role `governor` has authority over the functions shown in the diagram below. Any compromise to the `governor` account may allow the hacker to take advantage of this authority and deploy/remove product proxy. 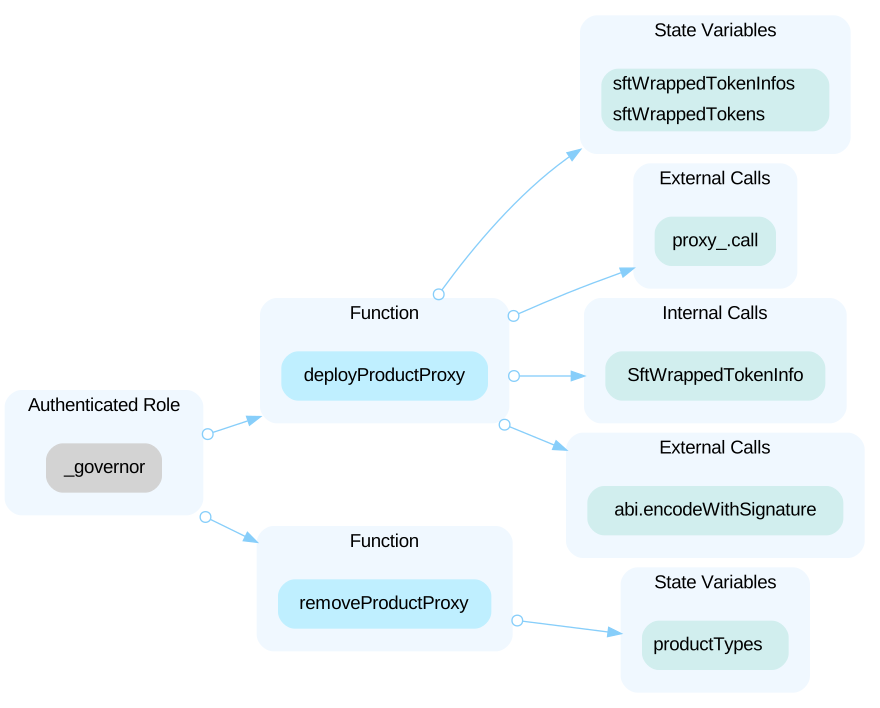
HighCentralized Control of Contract UpgradeOpen
In the contract `SftWrappedToken`, the role `admin` of the proxy has the authority to update the implementation contract behind the proxy contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
MediumThird-Party Dependency UsageOpen
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=43 address public wrappedSftAddress; ``` - The contract `SftWrappedToken` interacts with third party contract with `IERC3525` interface via `wrappedSftAddress`. --- ```solidity=45 address public navOracle; ``` - The contract `SftWrappedToken` interacts with third party contract with `INavOracle` interface via `navOracle`.
LowThe Design of the contract `SftWrappedToken`Open
When a user calls `mint()` and the passed amount equals the balance of `sftId_`, the ownership of `sftId_` transfers to the contract. The initial assignment is to `holdingValueSftId`, and the remainder is inserted into `_holdingEmptySftIds`. Subsequently, when a user calls `burn()`, and if `_holdingEmptySftIds` is empty, a new ID regenerates, and ownership remains with the current user. No ownership of `holdingValueSftId` is reclaimed. However, if `_holdingEmptySftIds` is not empty, the last ID is taken and removed. This results in the ownership of the contract transferring to the user. Nevertheless, the number of contracts may not match those initially transferred. Consequently, there will be a discrepancy in the token IDs between the `burn()` and `mint()` operations. Different ERC-3225 token IDs may exhibit varying value differences, potentially leading to losses.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (6)
- contracts/SftWrappedTokenFactory.sol
- contracts/access/GovernorControl.sol
- contracts/utils/ERC3525TransferHelper.sol
- contracts/access/AdminControl.sol
- contracts/SftWrappedToken.sol
- contracts/ISftWrappedToken.sol
Part of Solv Protocol’s security record
 Solv Protocol
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us