
Solv Protocol security record
As of 19 Nov 2026, Solv Protocol has 6 audit reports by 3 security firms on Trustblock; the latest is by Quantstamp, dated 15 Dec 2025. Those reports list no open critical findings. It also holds 2 deployed contracts on 1 chain.
Record last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Audits6
Newest first
| Report | Security firm | Date | Scope | Critical findings | Source |
|---|---|---|---|---|---|
| Solv Protocol - BTC Redemption | Security firm: Quantstamp | Date: | Scope: Not recorded; see the report | None open | certificate.quantstamp.com ↗ |
| Audit Report (SolvBTC) | Security firm: Paladin | Date: | Scope: 2 addresses on Ethereum | None open | IPFS ↗ |
| Solv Protocol - SolvBTC | Security firm: Quantstamp | Date: | Scope: Repository at commit eafc741 | None open | certificate.quantstamp.com ↗ |
| Solv Yield - Bearing Tokens | Security firm: CertiK | Date: | Scope: Files listed | None open | skynet.certik.com ↗ |
| Solv Protocol- Vault Guardian | Security firm: Quantstamp | Date: | Scope: Repository at commit 80300ac | None open | certificate.quantstamp.com ↗ |
| Solv Protocol stUSD - Audit | Security firm: CertiK | Date: | Scope: Files listed | None open | skynet.certik.com ↗ |
Findings55
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed | Mitigated |
|---|---|---|---|---|
| Critical | 0 | 0 | 0 | 0 |
| High | 2 | 1 | 4 | 0 |
| Medium | 1 | 0 | 3 | 2 |
| Low | 4 | 11 | 15 | 0 |
HighCentralization Related RisksSolv Protocol stUSD - Audit · CertiK · 28 Dec 2023Open
In the contract `GovernorControl` the role `governor` has authority over the functions shown in the diagram below. Any compromise to the `governor` account may allow the hacker to take advantage of this authority and set the pending governor's address. 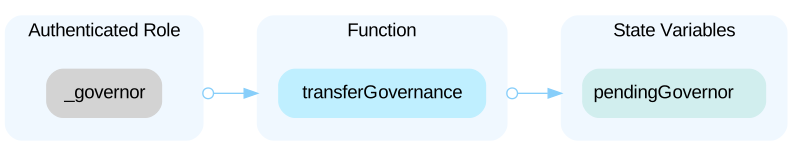 In the contract `GovernorControl` the role `pendinggovernor` has authority over the functions shown in the diagram below. Any compromise to the `pendinggovernor` account may allow the hacker to take advantage of this authority and set the governor's address. 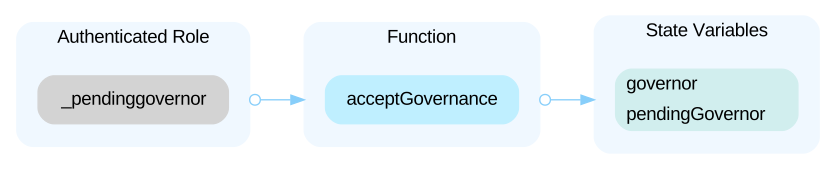 ----- In the contract `AdminControl` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and set the pending admin's address. 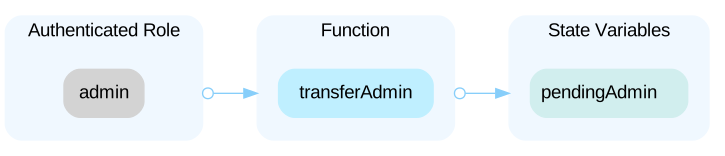 In the contract `AdminControl` the role `pendingAdmin` has authority over the functions shown in the diagram below. Any compromise to the `pendingAdmin` account may allow the hacker to take advantage of this authority and set the admin's address. 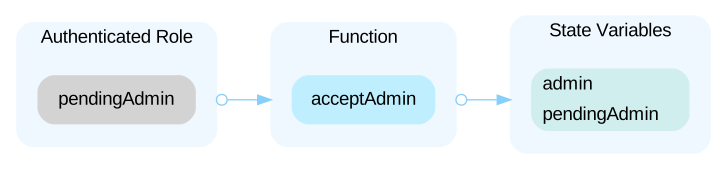 ----- In the contract `SftWrappedTokenFactory` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and - set the implementation address - deploy the Beacon proxy - upgrade the implementation of the Beacon proxy - transfer the ownership of the Beacon proxy to the new owner 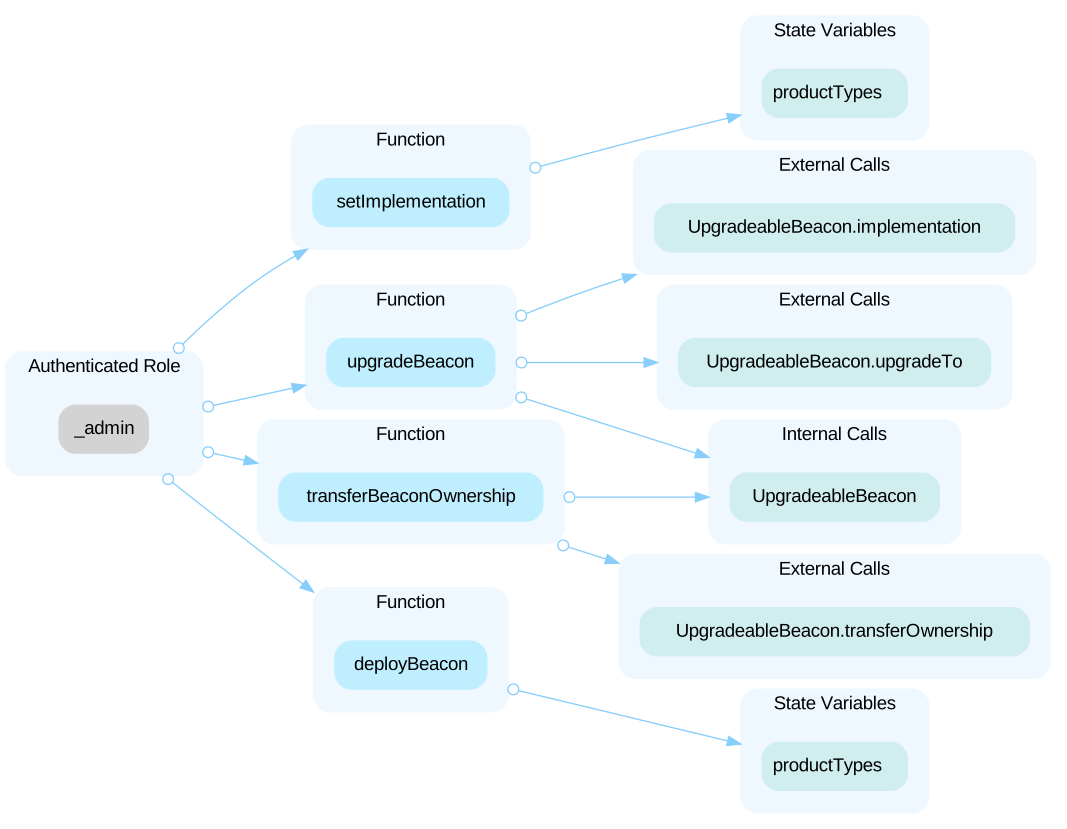 In the contract `SftWrappedTokenFactory` the role `governor` has authority over the functions shown in the diagram below. Any compromise to the `governor` account may allow the hacker to take advantage of this authority and deploy/remove product proxy. 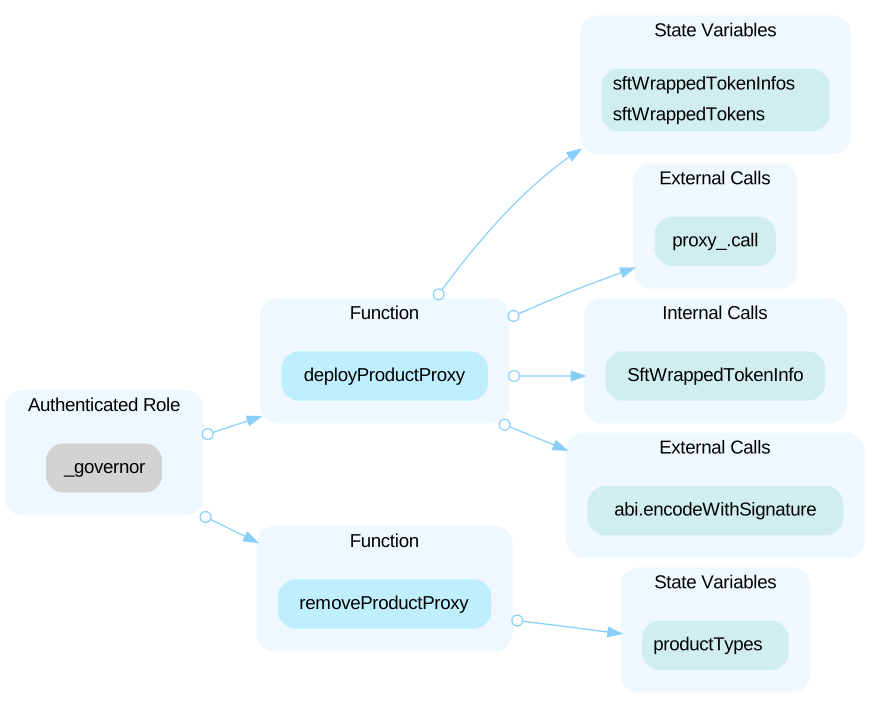
Open the reportHighCentralized Control of Contract UpgradeSolv Protocol stUSD - Audit · CertiK · 28 Dec 2023Open
In the contract `SftWrappedToken`, the role `admin` of the proxy has the authority to update the implementation contract behind the proxy contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
Open the reportMediumThird-Party Dependency UsageSolv Protocol stUSD - Audit · CertiK · 28 Dec 2023Open
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=43 address public wrappedSftAddress; ``` - The contract `SftWrappedToken` interacts with third party contract with `IERC3525` interface via `wrappedSftAddress`. --- ```solidity=45 address public navOracle; ``` - The contract `SftWrappedToken` interacts with third party contract with `INavOracle` interface via `navOracle`.
Open the reportLowTypographical issuesAudit Report (SolvBTC) · Paladin · 9 Dec 2024Open
The report gives no description here.
Open the reportLowOut-of-Scope DependenciesSolv Yield - Bearing Tokens · CertiK · 8 Apr 2024Open
The contract is serving as the underlying entity to interact with the out-of-scope contracts `IOpenFundMarket` and deposit tokens to the `IOpenFundMarket`. The scope of the audit treats these entities as black boxes and assumes their functional correctness. However, in the real world, external dependencies and out-of-scope contracts can be compromised and this may lead to lost or stolen assets.
Open the reportLowUnused InheritancesSolv Yield - Bearing Tokens · CertiK · 8 Apr 2024Open
The `SftWrapRouter` inherits `AdminControlUpgradeable` and `GovernorControlUpgradeable`, which are initiated but never used. This could potentially lead to confusion and inefficiency in contract deployment and interaction.
Open the reportLowThe Design of the contract `SftWrappedToken`Solv Protocol stUSD - Audit · CertiK · 28 Dec 2023Open
When a user calls `mint()` and the passed amount equals the balance of `sftId_`, the ownership of `sftId_` transfers to the contract. The initial assignment is to `holdingValueSftId`, and the remainder is inserted into `_holdingEmptySftIds`. Subsequently, when a user calls `burn()`, and if `_holdingEmptySftIds` is empty, a new ID regenerates, and ownership remains with the current user. No ownership of `holdingValueSftId` is reclaimed. However, if `_holdingEmptySftIds` is not empty, the last ID is taken and removed. This results in the ownership of the contract transferring to the user. Nevertheless, the number of contracts may not match those initially transferred. Consequently, there will be a discrepancy in the token IDs between the `burn()` and `mint()` operations. Different ERC-3225 token IDs may exhibit varying value differences, potentially leading to losses.
Open the reportContracts2
| Address | Chain | Source code |
|---|---|---|
| 0x2265a8e449ea5ff78ee4c115370e9b5957358a68 | Chain: Ethereum | Source code: Verified source |
| 0xb12979ff302ac903849948037a51792cf7186e8e | Chain: Ethereum | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="solv-protocol"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us