Valinity Audit
CertiK reviewed Valinity (Valinity Audit) on 7 Feb 2023: 9 findings, 0 critical; 4 marked fixed, 5 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings9
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 4 | 0 | 1 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 3 |
HighCentralization RisksOpen
In the contract `BEP20` the role `_owner` has authority over the functions shown in the diagram below. 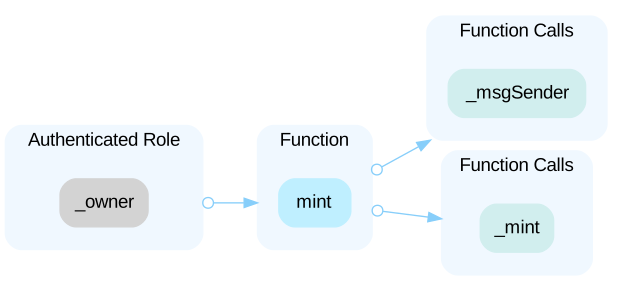 In the contract `MFCToken` the role `_adminAgents` has authority over the functions shown in the diagram below. 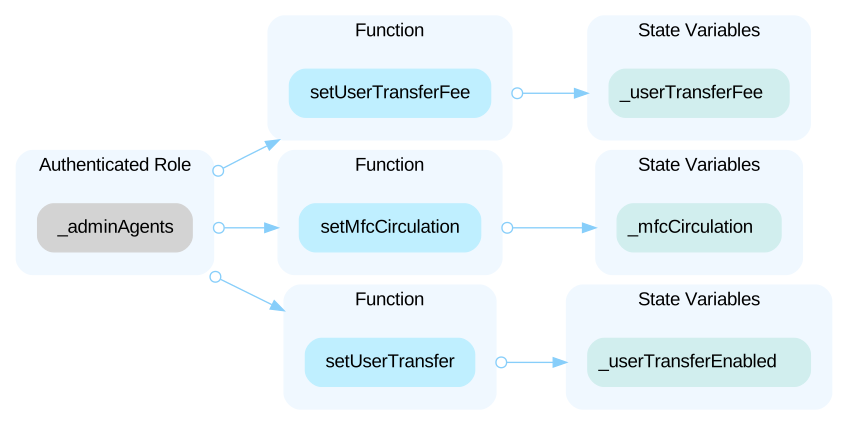 In the contract `MFCToken` the role `_backendAgents` has authority over the functions shown in the diagram below. 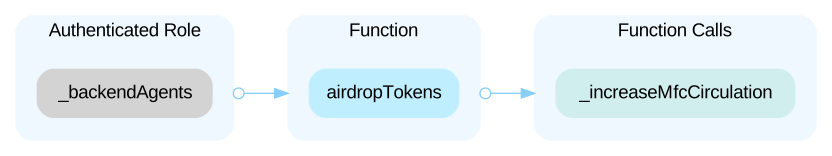 In the contract `MFCToken` the role `_mfcExchangeCap` has authority over the functions shown in the diagram below. 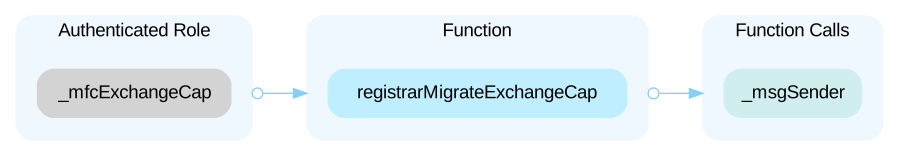 In the contract `BUSDT` the role `_adminGovAgents` has authority over the functions shown in the diagram below. 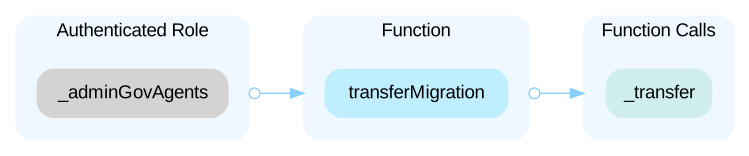 In the contract `BUSDT` the role `_governanceAddress` has authority over the functions shown in the diagram below. 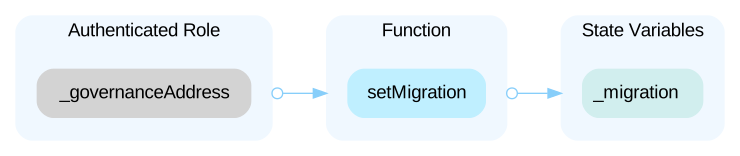 In the contract `BUSDT` the role `_mfcExchangeFloor` has authority over the functions shown in the diagram below. 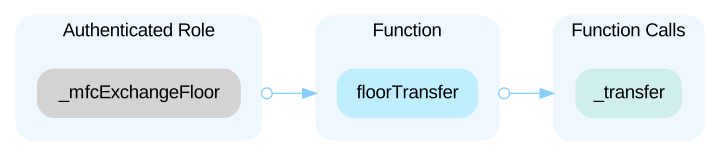 In the contract `RegistrarMigrator` the role `_adminAgents` has authority over the functions shown in the diagram below. 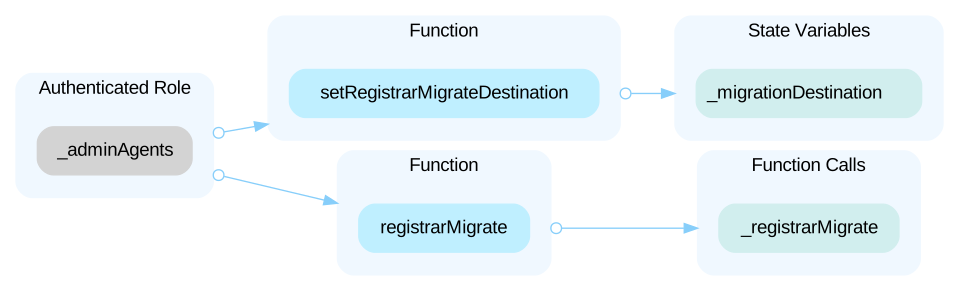 In the contract `Registrar` the role `_adminAgents` has authority over the functions shown in the diagram below. 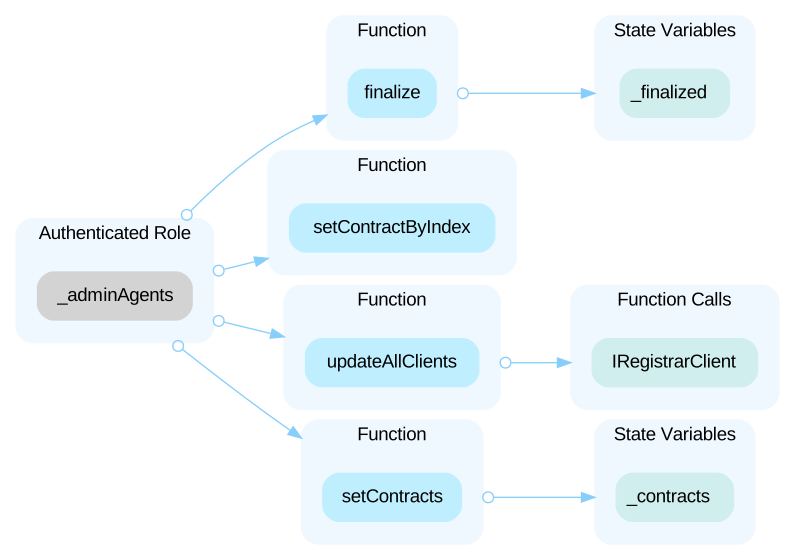 In the contract `MultiSig` the role `executor` has authority over the functions shown in the diagram below. 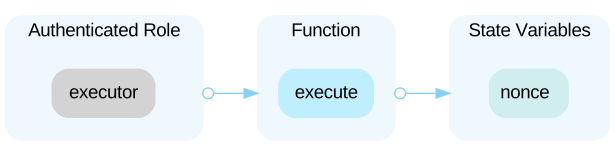 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 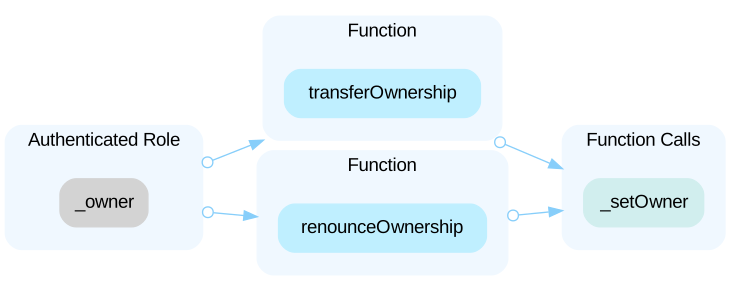 In the contract `AccessControl` the role `account` has authority over the functions shown in the diagram below. 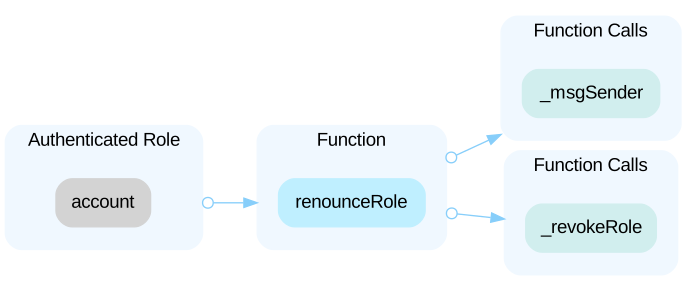 In the contract `BackendAgent` the role `_backendAdminAgents` has authority over the functions shown in the diagram below. 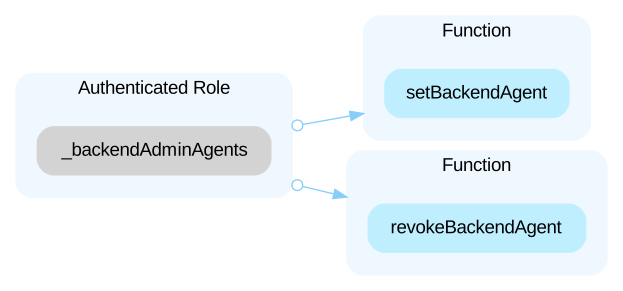 In the contract `WithdrawAgent` the role `_withdrawAdminAgents` has authority over the functions shown in the diagram below. 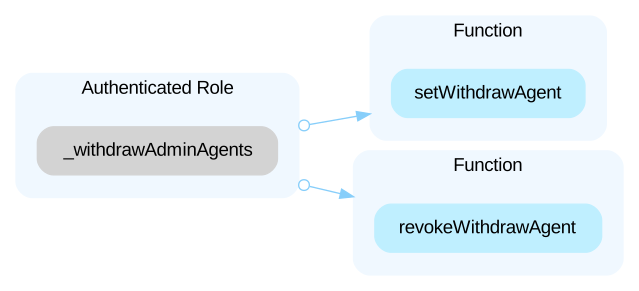 In the contract `WithdrawAgent` the role `_withdrawAgents` has authority over the functions shown in the diagram below. 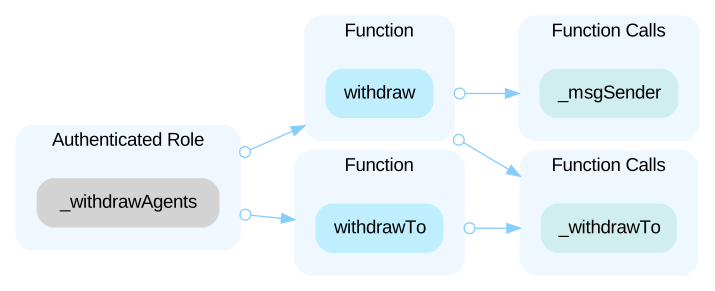 Any compromise to the privileged accounts may allow the hacker to take advantage of this authority and switch owners, withdraw tokens, and modify critical configurations of the contracts.
HighCentralization RisksOpen
In the contract `exchange/MFCExchange.sol`, `exchange/MFCExchangeFloor.sol`, `exchange/MFCExchangeCap.sol`, `governance/MFCGovernance.sol`, `MFCCollateralLoan.sol`, `MFCTradingLicense.sol`, `token/MFCToken.sol` and `treasury/BUSDT.sol`, the role `_registrar` has authority over the following functions: - updateAddresses() In the contract `lib/access/AccessControl.sol`, the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() In the contract `token/MFCToken.sol`, the role `MINTER_ROLE` has authority over the following functions: - mint() - grantOwnerRole() - grantMinterRole() - grantWhitelisterRole() - revokeOwnerRole() - revokeMinterRole() - revokeWhitelisterRole() - whitelistUser() - whitelistUserBatch() - whitelistAgent() - revokeWhitelistedUser() - revokeWhitelistedAgent() Any compromise to the privileged accounts may allow the hacker to take advantage of this authority and switch owners, withdraw tokens, and modify critical configurations of the contracts.
HighCentralization RisksOpen
In the contract `MFCCollateralLoan` the role `_adminGovAgents` has authority over the functions shown in the diagram below. 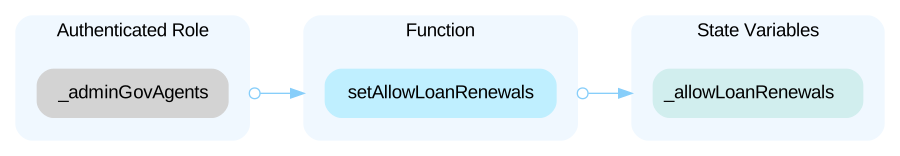 In the contract `MFCCollateralLoan` the role `_backendAdminAgents` has authority over the functions shown in the diagram below. 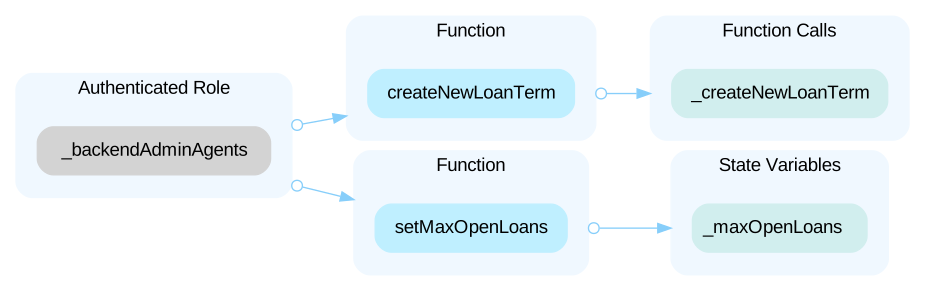 In the contract `MFCCollateralLoan` the role `_backendAgents` has authority over the functions shown in the diagram below. 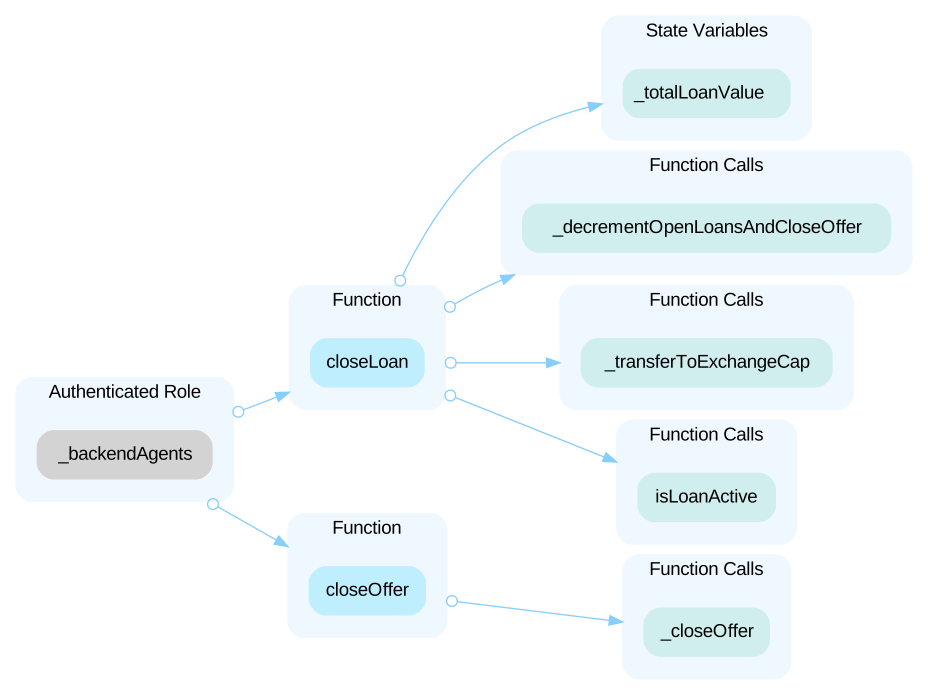 In the contract `MFCCollateralLoan` the role `_deployer` has authority over the functions shown in the diagram below. 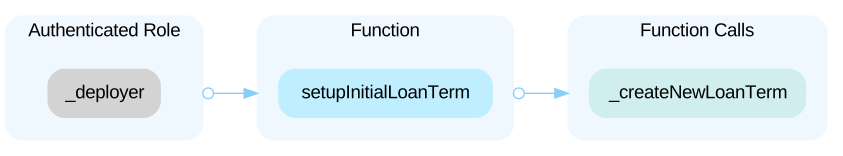 In the contract `MFCGovernance` the role `_adminAgents` has authority over the functions shown in the diagram below. 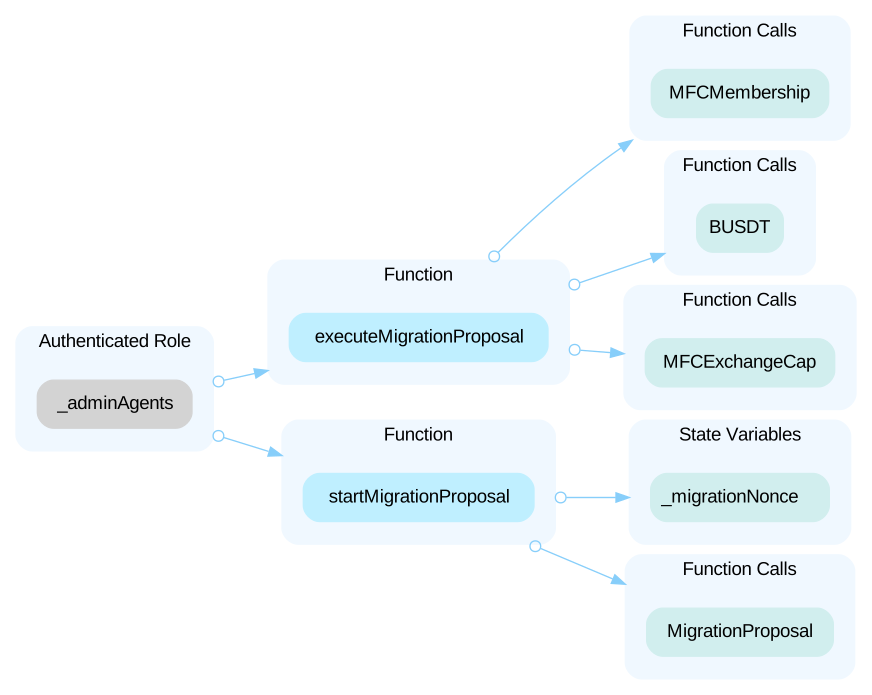 In the contract `MFCExchange` the role `_backendAgents` has authority over the functions shown in the diagram below. 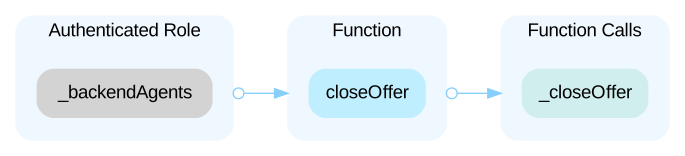 In the contract `MFCExchangeCap` the role `_adminGovAgents` has authority over the functions shown in the diagram below. 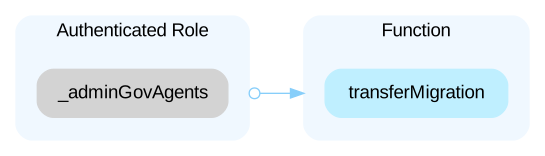 In the contract `MFCExchangeCap` the role `_backendAgents` has authority over the functions shown in the diagram below. 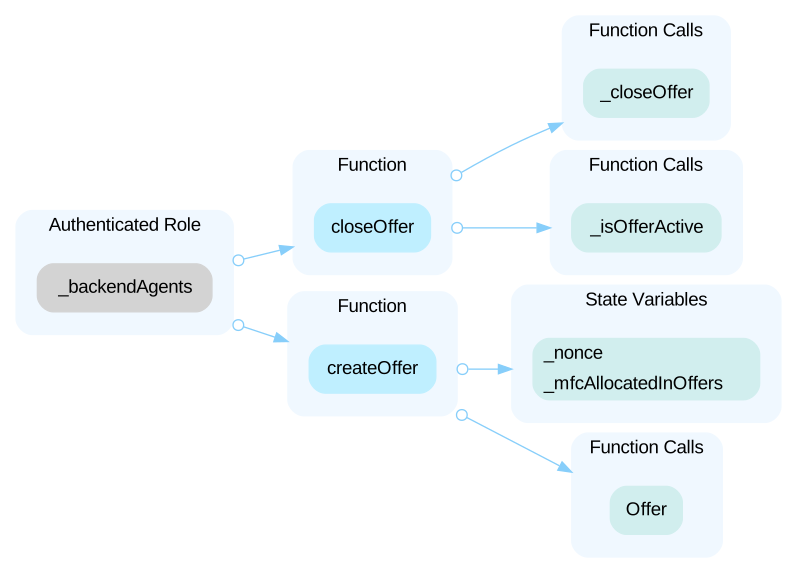 In the contract `MFCExchangeCap` the role `_governanceAddress` has authority over the functions shown in the diagram below. 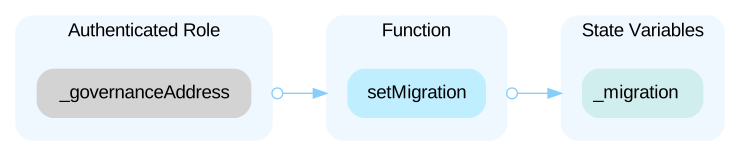 In the contract `MFCExchangeFloor` the role `_deployer` has authority over the functions shown in the diagram below. 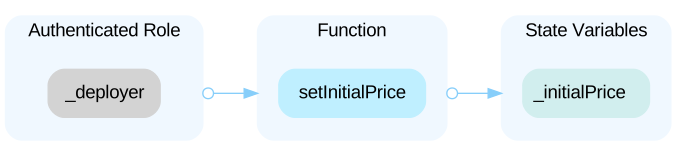 In the contract `MFCTradingLicense` the role `_adminAgents` has authority over the functions shown in the diagram below. 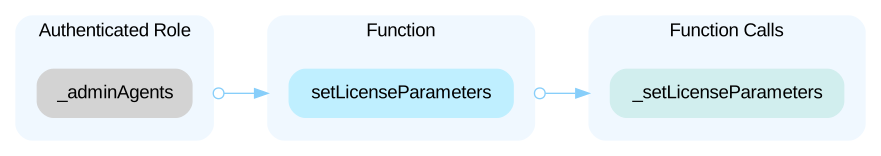 In the contract `MFCTradingLicense` the role `_adminGovAgents` has authority over the functions shown in the diagram below. 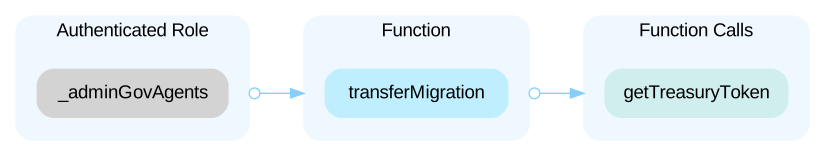 In the contract `MFCTradingLicense` the role `_deployer` has authority over the functions shown in the diagram below. 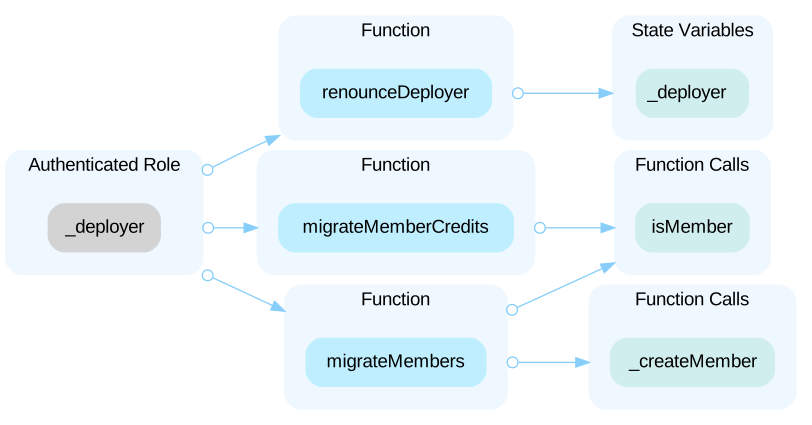 In the contract `MFCTradingLicense` the role `_governanceAddress` has authority over the functions shown in the diagram below. 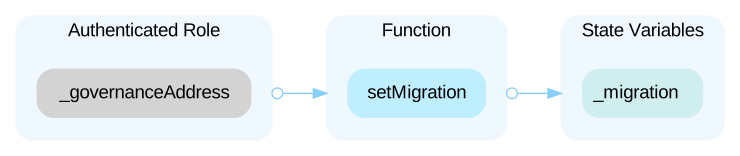 Any compromise to the privileged accounts may allow the hacker to take advantage of this authority and switch owners, withdraw tokens, and modify critical configurations of the contracts.
HighPotential Price Manipulation by Privilege RolesOpen
```solidity=115 function _getPrice() private view returns (uint256) { uint256 mfcCirculation = _mfc.getMfcCirculation(); uint256 busdBalance = _busdt.getBusdtValue(); if (busdBalance == 0) { return 0; } if (mfcCirculation > 0) { return MULTIPLIER * mfcCirculation / busdBalance; } else { return _initialPrice; } } ``` In contract `MFCExchangeFloor`, function `_getPrice()` returns the price of MFC that equals `MULTIPLIER * mfcCirculation / busdBalance` (when `mfcCirculation` > 0). Which means MFC is backed by BUSD in the treasury. So the following functions in contract `MFCToken` can be used to manipulate the price of MFC by changing `mfcCirculation`: - `setMfcCirculation()` - `airdropTokens()` The role `_adminAgents` can call `setMfcCirculation()` and set `_mfcCirculation` to any value. The role `_bankendAgents` can call `airdropTokens()` and mint tokens to addresses without increasing MFC's circulation by setting `updateCirculation` to false.
LowMissing Zero Address ValidationOpen
Addresses should be checked before assignment or external call to make sure they are not zero addresses. ```solidity=163 _busdComptrollerAddress = busdComptrollerAddress_; ``` - `busdComptrollerAddress_` is not zero-checked before being used. --- ```solidity=70 _busdAddress = busdAddress_; ``` - `busdAddress_` is not zero-checked before being used. --- ```solidity=71 _busdComptrollerAddress = busdComptrollerAddress_; ``` - `busdComptrollerAddress_` is not zero-checked before being used. --- ```solidity=56 _busdComptrollerAddress = busdComptrollerAddress_; ``` - `busdComptrollerAddress_` is not zero-checked before being used.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (30)
- contracts/treasury/BUSDT.sol
- contracts/MFCMembership.sol
- contracts/lib/utils/introspection/IERC165.sol
- contracts/lib/access/AccessControl.sol
- contracts/lib/utils/Strings.sol
- contracts/lib/utils/Context.sol
- contracts/lib/access/IAccessControl.sol
- contracts/Registrar.sol
- contracts/governance/Governable.sol
- contracts/MFCCollateralLoan.sol
- contracts/RegistrarClient.sol
- contracts/treasury/Treasury.sol
- contracts/MFCTradingLicense.sol
- contracts/lib/utils/Multisig.sol
- contracts/token/MFCToken.sol
- contracts/lib/utils/introspection/ERC165.sol
- contracts/exchange/MFCExchangeCap.sol
- contracts/access/AdminAgent.sol
- contracts/access/AdminGovernanceAgent.sol
- contracts/lib/token/BEP20/BEP20.sol
- contracts/lib/token/BEP20/IBEP20.sol
- contracts/exchange/MFCExchange.sol
- contracts/governance/MFCGovernance.sol
- contracts/access/WithdrawAgent.sol
- contracts/lib/access/Ownable.sol
- contracts/exchange/ExchangeCheck.sol
- contracts/RegistrarMigrator.sol
- contracts/lib/token/BEP20/MFCBEP20.sol
- contracts/access/BackendAgent.sol
- contracts/exchange/MFCExchangeFloor.sol
Part of Valinity’s security record
 Valinity
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us