0x073e152efbdbd6cbc20bb5f14893dc2969539210
As of 21 Nov 2026, Trustblock’s record holds 0x073e152efbdbd6cbc20bb5f14893dc2969539210 on BNB Chain as a contract of Vite. 1 audit report on Trustblock lists this address: CertiK, 28 Jun 2024. 3 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
3 High. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Ownable` the role `_owner` has authority over the functions. - renounceOwnership(), Leaves the contract without an owner. - transferOwnership(), Transfers contract ownership to a new account. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and manage the privileged role. In the contract `VITEDAO` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following things. - pause/unpause the contract. - mint tokens to any account at will. 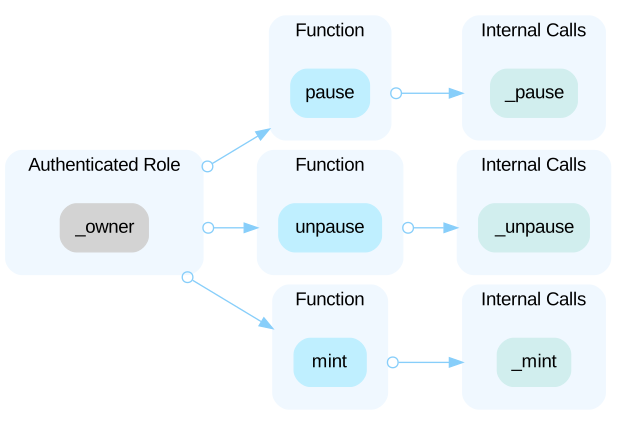
The audit on Trustblock · Open the reportIn the contract `VITEDAO`, the role owner has the authority to update the token balance of an arbitrary account without sanity restriction. Any compromise to the `owner` account may allow a hacker to take advantage of this authority and manipulate users' balances. For example, the hacker could also update his/her balance to a large number, sell these tokens, and cause the token price to drop.
The audit on Trustblock · Open the reportAll of the `VDAO` tokens are sent to the `initialOwner` address. This is a centralization risk because the `initialOwner` can distribute tokens without obtaining the consensus of the community. Any compromise to the addresse may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportThe Vite security record · Every Vite address · This address on the explorer