0x15ea6b8481bf1c991ac3dc8e67279d31651a56fe
As of 21 Nov 2026, Trustblock’s record holds 0x15ea6b8481bf1c991ac3dc8e67279d31651a56fe on BNB Chain as a contract of Cylum Finance. 1 audit report on Trustblock lists this address: CertiK, 19 Apr 2022. 5 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Cylum Finance | CertiK | Not recorded (see the report) | Open |
3 High, 2 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `CYLUM` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 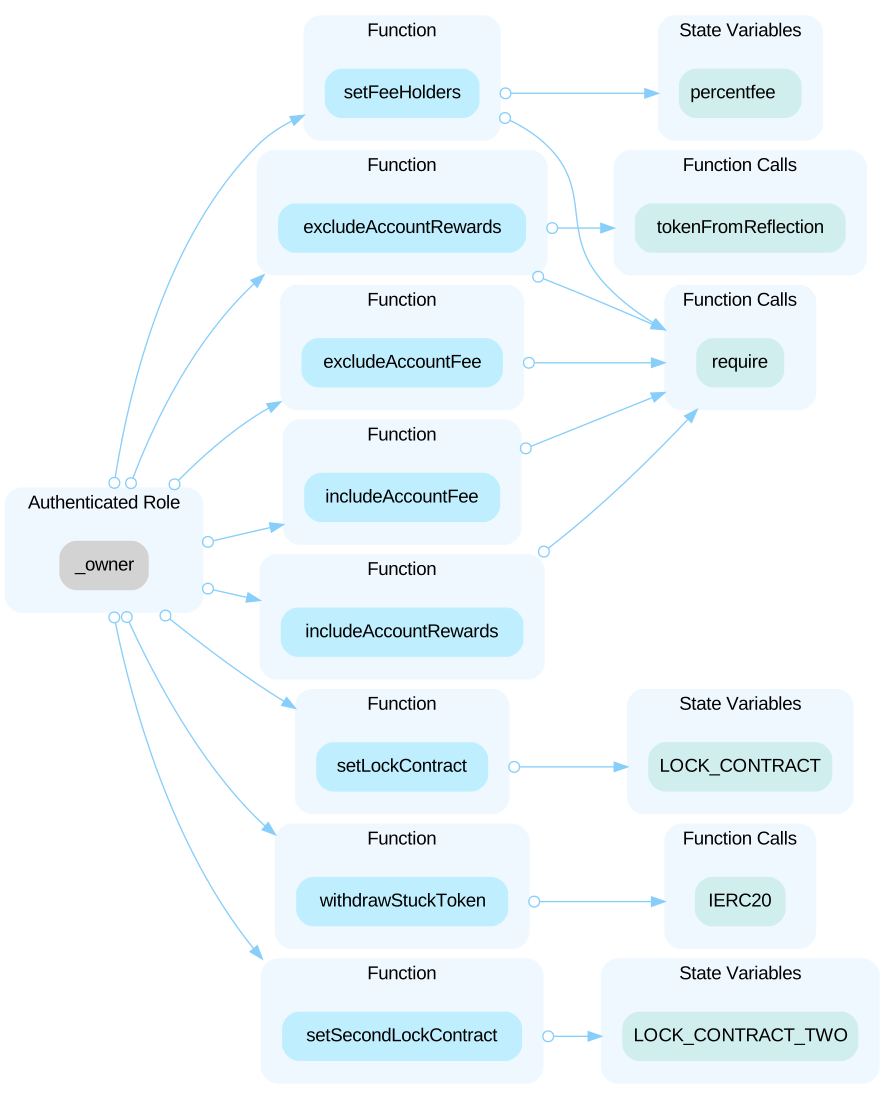
The audit on Trustblock · Open the reportAll of the CYM tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute CYM tokens without obtaining the consensus of the community.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with third party ILockContract. The scope of the audit treats 3rd party entities as black boxes and assume their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts, such as increasing fees of 3rd parties, migrating to new LP pools, etc.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportFunction `_transferFromExcluded`, `_transferToExcluded`, `_transferBothExcluded` can all be replaced by `_transferNoFee`.
The audit on Trustblock · Open the reportThe Cylum Finance security record · Every Cylum Finance address · This address on the explorer