0x16243911e0c7eb0b6a7b089c79ac74572232eb68
As of 21 Nov 2026, Trustblock’s record holds 0x16243911e0c7eb0b6a7b089c79ac74572232eb68 on BNB Chain as a contract of LGT-NFT. 1 audit report on Trustblock lists this address: CertiK, 26 Sep 2022. 23 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
3 High, 1 Medium, 19 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `LGToken` the role `_owner` has authority over the functions shown in the diagram below. 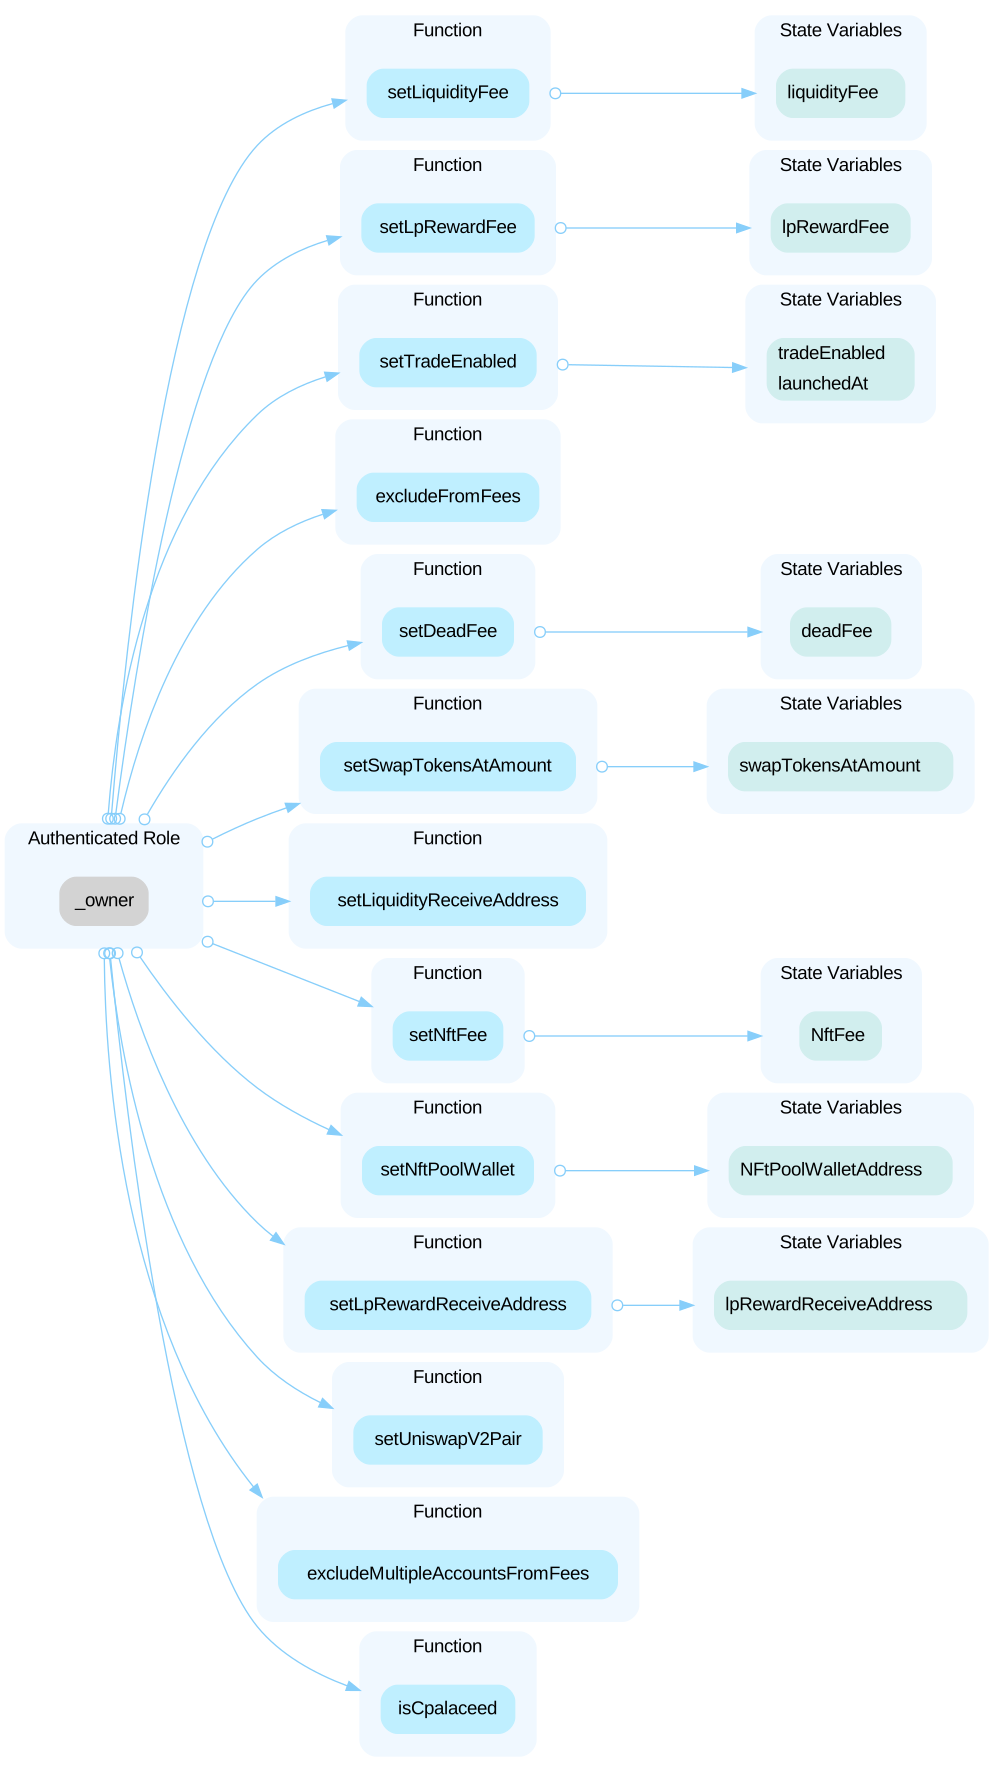 In the contract `LiquidityBackHelper` the role `_owner` has authority over the functions shown in the diagram below. 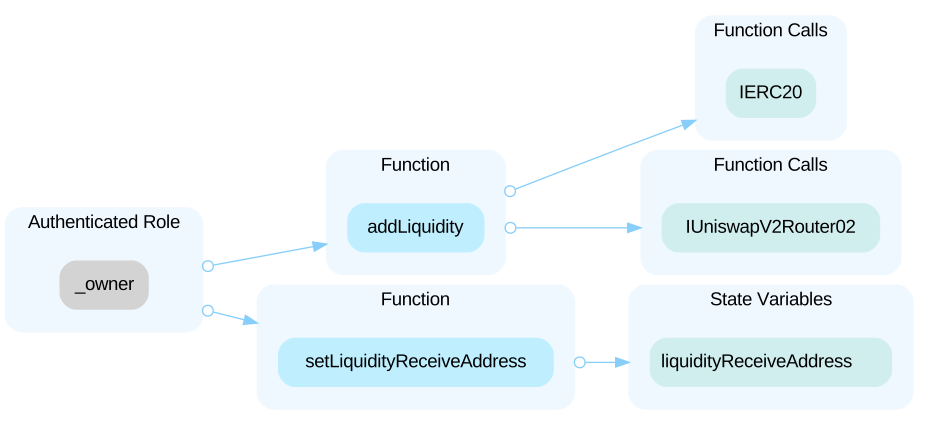 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 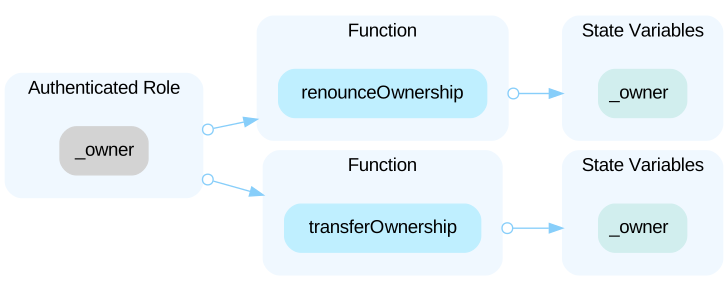 Any compromise to the privileged accounts may allow the hacker to take advantage of this authority.
The audit on Trustblock · Open the report```solidity=603 function addLiquidity(uint256 tokenAmount, uint256 usdtAmount) external onlyOwner { IERC20(token).approve(address(router), tokenAmount); IERC20(usdt).approve(address(router), usdtAmount); IUniswapV2Router02(router).addLiquidity( token, usdt, tokenAmount, usdtAmount, 0, 0, liquidityReceiveAddress, block.timestamp ); } ``` The `addLiquidity()` function calls the `uniswapV2Router.addLiquidity` function with the `to` address specified as `liquidityReceiveAddress` for acquiring the generated LP tokens from the `LGT-USDT` pool. As a result, over time the `liquidityReceiveAddress` address will accumulate a significant portion of LP tokens. If the `liquidityReceiveAddress` is an EOA (Externally Owned Account), mishandling of its private key can have devastating consequences to the project as a whole.
The audit on Trustblock · Open the reportAll of the `LGT` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute `LGT` tokens without obtaining the consensus of the community.
The audit on Trustblock · Open the reportThe `swapAndLiquify()` function converts half of the `AmountLiquidityFee` `LGT` tokens to `BUSD`. The other half of `LGT` tokens and part of the converted `BUSD` are deposited into the `LGT-BUSD` pool on pancakeswap as liquidity. For every `swapAndLiquify()` function call, a small amount of `BUSD` leftover in the `liquidityBackHelper` contract. This is because the price of `LGT` drops after swapping the first half of `LGT` tokens into `BUSD`, and the other half of `LGT` tokens require less than the converted `BUSD` to be paired with it when adding liquidity. The `liquidityBackHelper` contract doesn't appear to provide a way to withdraw those `BUSD`, and they will be locked in the contract forever.
The audit on Trustblock · Open the reportThere is a risk that the owner casually calls the function `setTradeEnabled()` with `_enabled` as `false`, and `launchedAt` will be assigned a value(and `launchedAt` can just be assigned once). `launchedAt` only makes sense when `tradeEnabled` is true. ```solidity=754 function setTradeEnabled(bool _enabled) public onlyOwner { tradeEnabled = _enabled; if (launchedAt == 0) launchedAt = block.number; } ```
The audit on Trustblock · Open the reportThe approval function of the ERC20 standard possesses a well-known vulnerability whereby two consecutive approvals can be exploited to instead “reset” the approval by consuming the approval that is meant to be replaced with a new one.
The audit on Trustblock · Open the reportThe functions which are never called internally within the contract should have external visibility for gas optimization. ```solidity=243 function renounceOwnership() public virtual onlyOwner { ``` --- ```solidity=248 function transferOwnership(address newOwner) public virtual onlyOwner { ``` --- ```solidity=339 function name() public view virtual override returns (string memory) { ``` --- ```solidity=347 function symbol() public view virtual override returns (string memory) { ``` --- ```solidity=364 function decimals() public view virtual override returns (uint8) { ``` --- ```solidity=371 function totalSupply() public view virtual override returns (uint256) { ``` --- ```solidity=378 function balanceOf(address account) public view virtual override returns (uint256) { ``` --- ```solidity=390 function transfer(address recipient, uint256 amount) public virtual override returns (bool) { ``` --- ```solidity=398 function allowance(address owner, address spender) public view virtual override returns (uint256) { ``` --- ```solidity=409 function approve(address spender, uint256 amount) public virtual override returns (bool) { ``` --- ```solidity=427 function transferFrom( ``` --- ```solidity=449 function increaseAllowance(address spender, uint256 addedValue) public virtual returns (bool) { ``` --- ```solidity=468 function decreaseAllowance(address spender, uint256 subtractedValue) public virtual returns (bool) { ``` --- ```solidity=618 function setLiquidityReceiveAddress(address newAddress) public onlyOwner { ``` --- ```solidity=691 function setUniswapV2Pair(address pair, bool val) public onlyOwner { ``` --- ```solidity=701 function isCpalaceed(address account, bool excluded) public onlyOwner { ``` --- ```solidity=707 function excludeMultipleAccountsFromFees(address[] calldata accounts, bool excluded) public onlyOwner { ``` --- ```solidity=719 function setSwapTokensAtAmount(uint256 amount) public onlyOwner { ``` --- ```solidity=723 function setLiquidityFee(uint256 val) public onlyOwner { ``` --- ```solidity=727 function setNftFee(uint256 val) public onlyOwner { ``` --- ```solidity=732 function setDeadFee(uint256 val) public onlyOwner { ``` --- ```solidity=736 function setLpRewardFee(uint256 val) public onlyOwner { ``` --- ```solidity=740 function isExcludedFromFees(address account) public view returns(bool) { ``` --- ```solidity=744 function setLiquidityReceiveAddress(address newAddress) public onlyOwner { ``` --- ```solidity=747 function liquidityReceiveAddress() public view returns(address) { ``` --- ```solidity=751 function setLpRewardReceiveAddress(address newAddress) public onlyOwner { ``` --- ```solidity=754 function setTradeEnabled(bool _enabled) public onlyOwner { ```
The audit on Trustblock · Open the reportAccording to the code, `_isCpalaceed` is a bit like a sniper list. If buyers buy `LGT` within 40 blocks of the start of the launch block, the associated accounts will be pushed into `_isCpalaceed` which means they can not transfer `LGT` out later. However, 40 blocks seems like a lot. In bsc, 40 blocks means 120 seconds. In eth, 40 blocks take more time. ```solidity=779 if (block.number - launchedAt < 40) { _isCpalaceed[to] = true; } ```
The audit on Trustblock · Open the report```solidity=596 constructor(address token_, address usdt_, address router_, address liquidityReceiveAddress_){...} ``` In the constructor of the contract `LiquidityBackHelper`, the fourth parameter is named `liquidityReceiveAddress_`. However, `lpRewardReceiveAddress_` is passed as the corresponding parameter in the constructor of the contract `LGToken`. ```solidity=655 constructor( string memory name_, string memory symbol_, uint256 totalSupply_, address NftPoolWalletAddr_, address liquidityReceiveAddress_, address lpRewardReceiveAddress_ ) payable ERC20(name_, symbol_) { ... liquidityBackHelper = new LiquidityBackHelper(address(this), USDT, address(_uniswapV2Router), lpRewardReceiveAddress_); ... } ```
The audit on Trustblock · Open the reportThe contract has one or more payable functions, but does not have a function to withdraw the fund. ```solidity=655 constructor(...) payable ... ``` ```solidity=688 receive() external payable {} ```
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportAddresses should be checked before assignment or external call to make sure they are not zero addresses. ```solidity=230 _owner = msgSender; ``` - `msgSender` is not zero-checked before being used. --- ```solidity=597 token = token_; ``` - `token_` is not zero-checked before being used. --- ```solidity=598 usdt = usdt_; ``` - `usdt_` is not zero-checked before being used. --- ```solidity=599 router = router_; ``` - `router_` is not zero-checked before being used. --- ```solidity=600 liquidityReceiveAddress = liquidityReceiveAddress_; ``` - `liquidityReceiveAddress_` is not zero-checked before being used. --- ```solidity=619 liquidityReceiveAddress = newAddress; ``` - `newAddress` is not zero-checked before being used. --- ```solidity=675 NFtPoolWalletAddress = NftPoolWalletAddr_; ``` - `NftPoolWalletAddr_` is not zero-checked before being used. --- ```solidity=676 lpRewardReceiveAddress = lpRewardReceiveAddress_; ``` - `lpRewardReceiveAddress_` is not zero-checked before being used. --- ```solidity=715 NFtPoolWalletAddress = wallet; ``` - `wallet` is not zero-checked before being used. --- ```solidity=752 lpRewardReceiveAddress = newAddress; ``` - `newAddress` is not zero-checked before being used.
The audit on Trustblock · Open the reportThe `LGToken` contract needs the collaboration of contract `LiquidityBackHelper` to complete the `swapAndLiquify` process. The two privileged functions `addLiquidity()` and `setLiquidityReceiveAddress()` are both called by the `LGToken` contract. Hence the owner of `LiquidityBackHelper` should be the contract `LGToken`, otherwise, the entire `LGT` ecosystem will not run properly.
The audit on Trustblock · Open the reportA sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by front running (before the transaction being attacked) a transaction to purchase one of the assets and make profits by back running (after the transaction being attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `swapTokensForUSDT()` - `swapAndLiquify()` calls `swapTokensForUSDT()` The following line ***851*** is set to the slippage to **0**. ```solidity=843 function swapTokensForUSDT(uint256 tokenAmount, address to) private { address[] memory path = new address[](2); path[0] = address(this); path[1] = USDT; _approve(address(this), address(uniswapV2Router), tokenAmount); uniswapV2Router.swapExactTokensForTokensSupportingFeeOnTransferTokens( tokenAmount, 0, path, to, block.timestamp ); } ```
The audit on Trustblock · Open the reportThe owner is exempt from fees and transaction limits by default. Yet when ownership is reset through `renounceOwnership()` or `transferOwnership()`, the exemptions are not granted to the new owner nor are they revoked from the previous owner.
The audit on Trustblock · Open the reportThe change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
The audit on Trustblock · Open the reportState variables that never change should be declared as `constant` to save gas. ```solidity=640 address public USDT = 0x55d398326f99059fF775485246999027B3197955; ``` - `USDT` should be declared `constant`. --- ```solidity=648 address public deadWallet = 0x000000000000000000000000000000000000dEaD; ``` - `deadWallet` should be declared `constant`.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=593 address public router; ``` - The contract `LiquidityBackHelper` interacts with third party contract with `IUniswapV2Router02` interface via `router`. --- ```solidity=627 IUniswapV2Router02 public uniswapV2Router; ``` - The contract `LGToken` interacts with third party contract with `IUniswapV2Router02` interface via `uniswapV2Router`.
The audit on Trustblock · Open the reportThe contract has unlocked compiler version. An unlocked compiler version in the source code of the contract permits the user to compile it at or above a particular version. This, in turn, leads to differences in the generated bytecode between compilations due to differing compiler version numbers. This can lead to an ambiguity when debugging as compiler specific bugs may occur in the codebase that would be hard to identify over a span of multiple compiler versions rather than a specific one.
The audit on Trustblock · Open the reportThe `SafeMath` library is used unnecessarily. With Solidity compiler versions 0.8.0 or newer, arithmetic operations will automatically revert in case of integer overflow or underflow. ```solidity=255 library SafeMath { ``` - An implementation of `SafeMath` library is found. --- ```solidity=311 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `ERC20` contract. ```solidity=433 _approve(sender, _msgSender(), _allowances[sender][_msgSender()].sub(amount, "ERC20: transfer amount exceeds allowance")); ``` - `SafeMath.sub` is called in `transferFrom` function of `ERC20` contract. *Note: Only a sample of 2 `SafeMath` library usage in this contract (out of 11) are shown above.* --- ```solidity=589 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `LiquidityBackHelper` contract. --- ```solidity=311 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `ERC20` contract. ```solidity=810 uint256 DFee = amount.mul(deadFee).div(100); ``` - `SafeMath.mul` is called in `takeAllFee` function of `LGToken` contract.
The audit on Trustblock · Open the reportThe return value of an external call is not stored in a local or state variable. ```solidity=604 IERC20(token).approve(address(router), tokenAmount); ``` --- ```solidity=605 IERC20(usdt).approve(address(router), usdtAmount); ``` --- ```solidity=606 IUniswapV2Router02(router).addLiquidity( token, usdt, tokenAmount, usdtAmount, 0, 0, liquidityReceiveAddress, block.timestamp ); ```
The audit on Trustblock · Open the reportThe linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
The audit on Trustblock · Open the reportThe LGT-NFT security record · Every LGT-NFT address · This address on the explorer