0x3ab1a5f76e12202d1ad1548a08a799501581da4e
As of 21 Nov 2026, Trustblock’s record holds 0x3ab1a5f76e12202d1ad1548a08a799501581da4e on BNB Chain as a contract of DIN. 1 audit report on Trustblock lists this address: CertiK, 14 Jan 2025. 15 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
3 High, 1 Medium, 11 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `OwnableUpgradeable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add a manager, renounce ownership of the contract, transfer the contract ownership, or remove a manager. 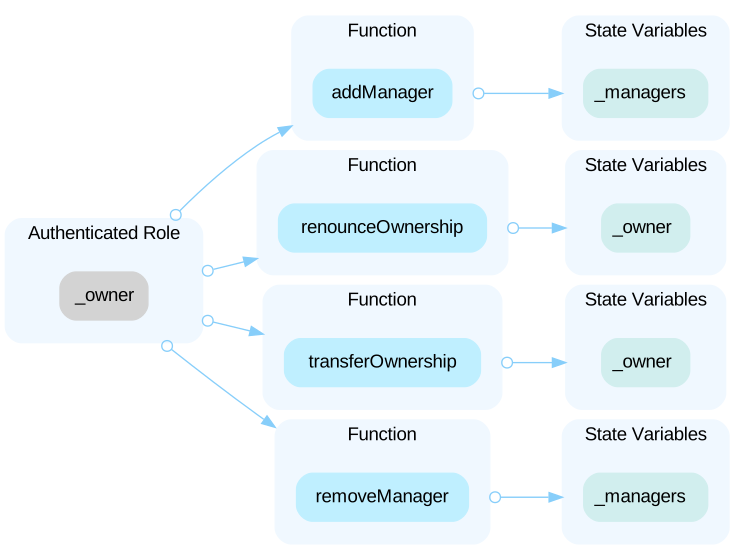 ----- In the contract `DIN`, the role `_manager` has authority over the functions shown in the diagram below. Any compromise to the `_manager` account may allow the hacker to take advantage of this authority and mint tokens to a specified address. 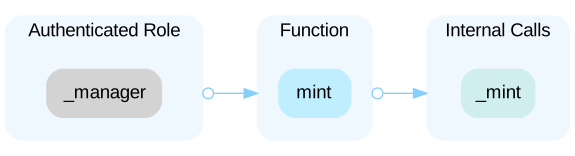 In the contract `DIN`, the role `_managers` has authority over the functions shown in the diagram below. Any compromise to the `_managers` account may allow the hacker to take advantage of this authority and mint tokens to a specified address. 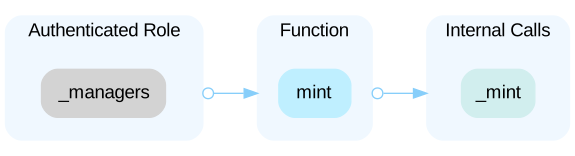 In the contract `DIN`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and mint tokens for a given address. 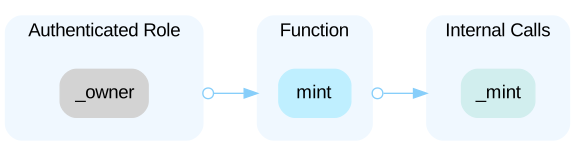 ----- In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the contract ownership, remove a manager, renounce contract ownership, or add a manager. 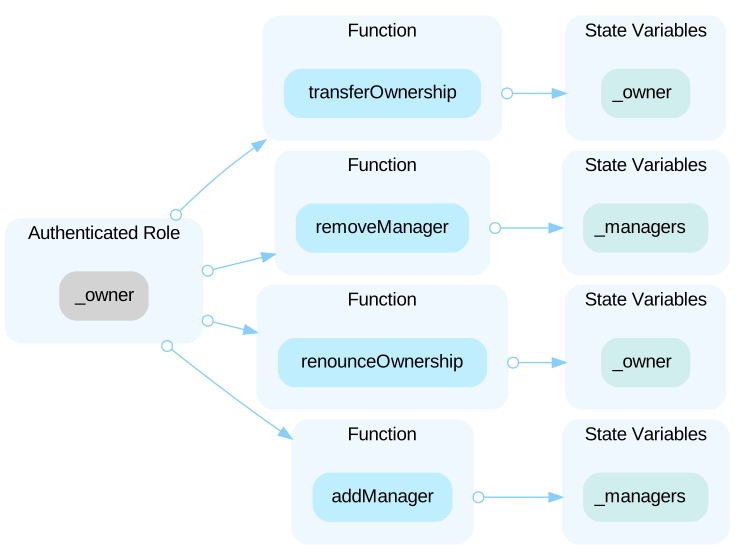 ----- In the contract `NodeStakingConvertor`, the role `_manager` has authority over the functions shown in the diagram below. Any compromise to the `_manager` account may allow the hacker to take advantage of this authority and unregister nodes, update global power status, and register and update node power and weight. 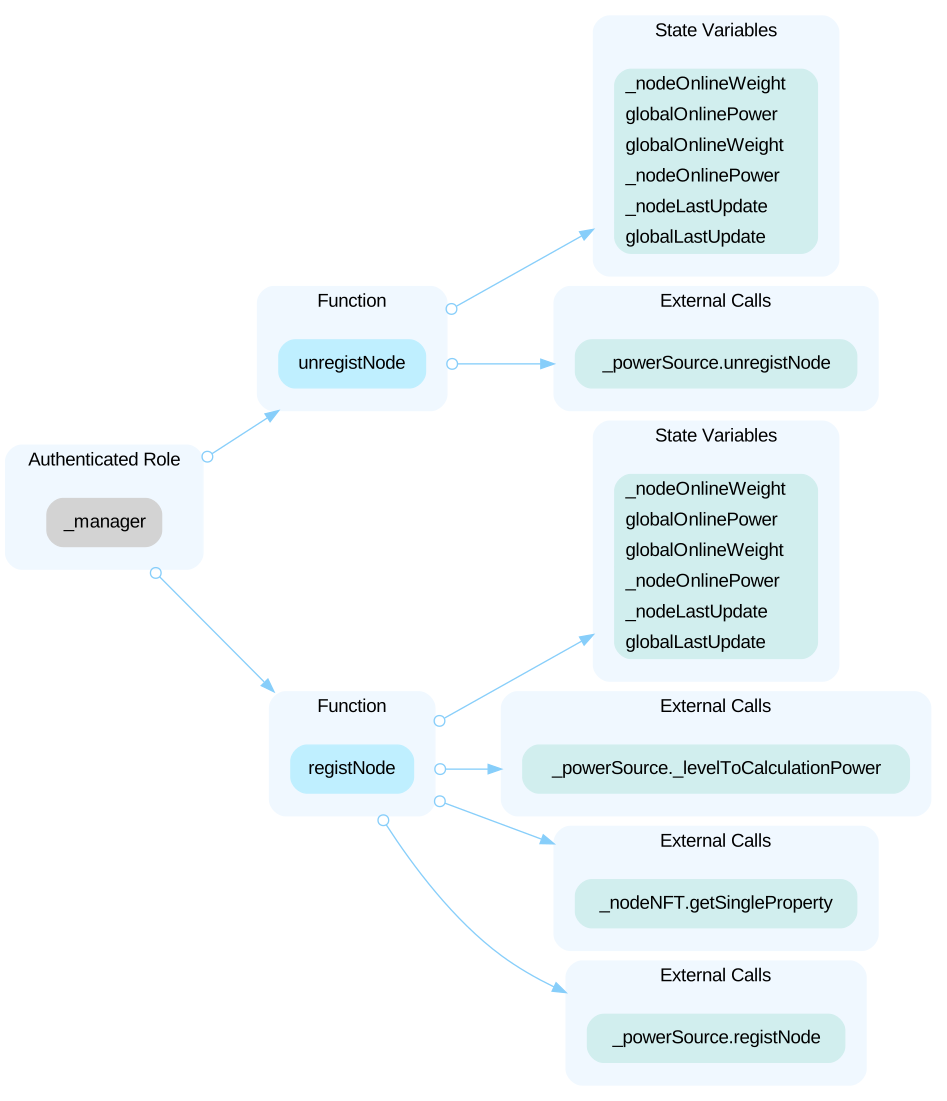 In the contract `NodeStakingConvertor`, the role `_managers` has authority over the functions shown in the diagram below. Any compromise to the `_managers` account may allow the hacker to take advantage of this authority and register nodes with NFT IDs, update power attributes, and unregister nodes with given NFT IDs. 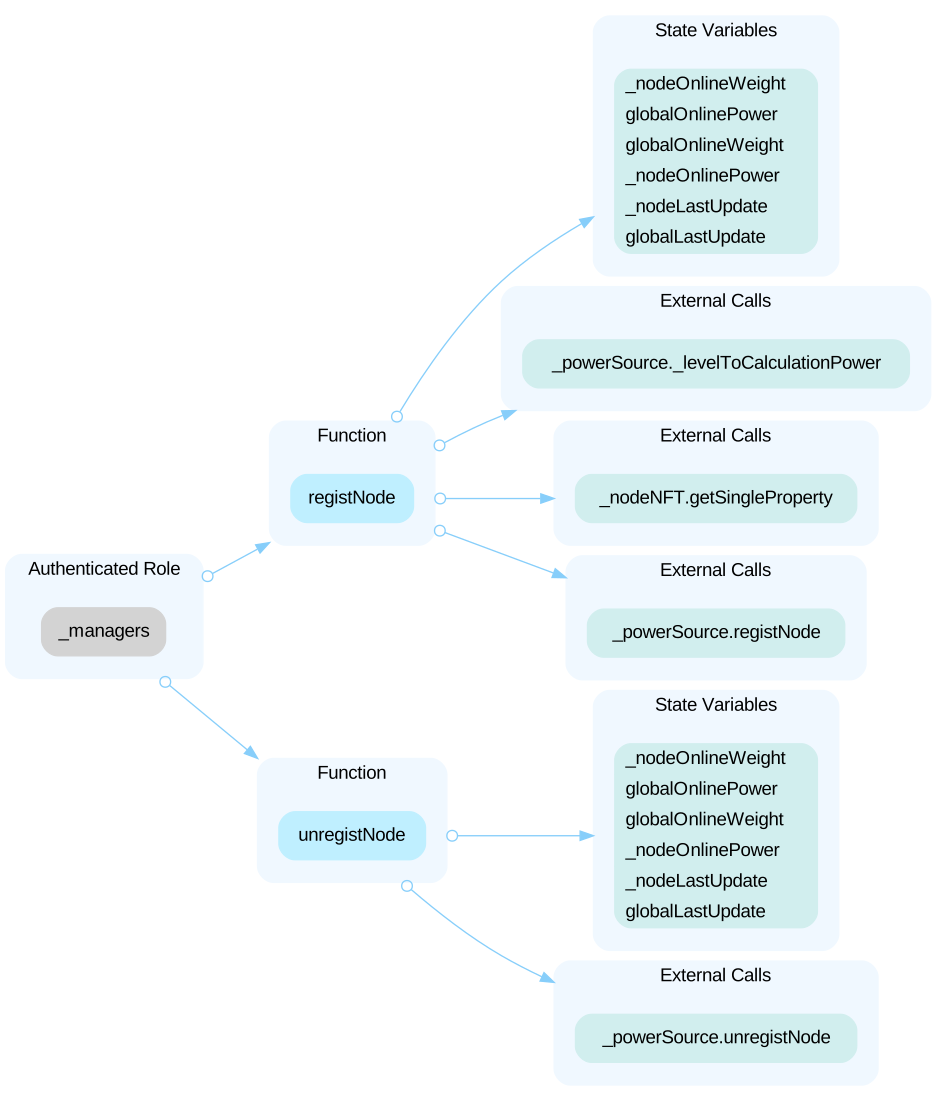 In the contract `NodeStakingConvertor`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change fundamental contract addresses, unregister nodes using provided nftIds, register power nodes with nft identifiers, and change reward configuration settings. 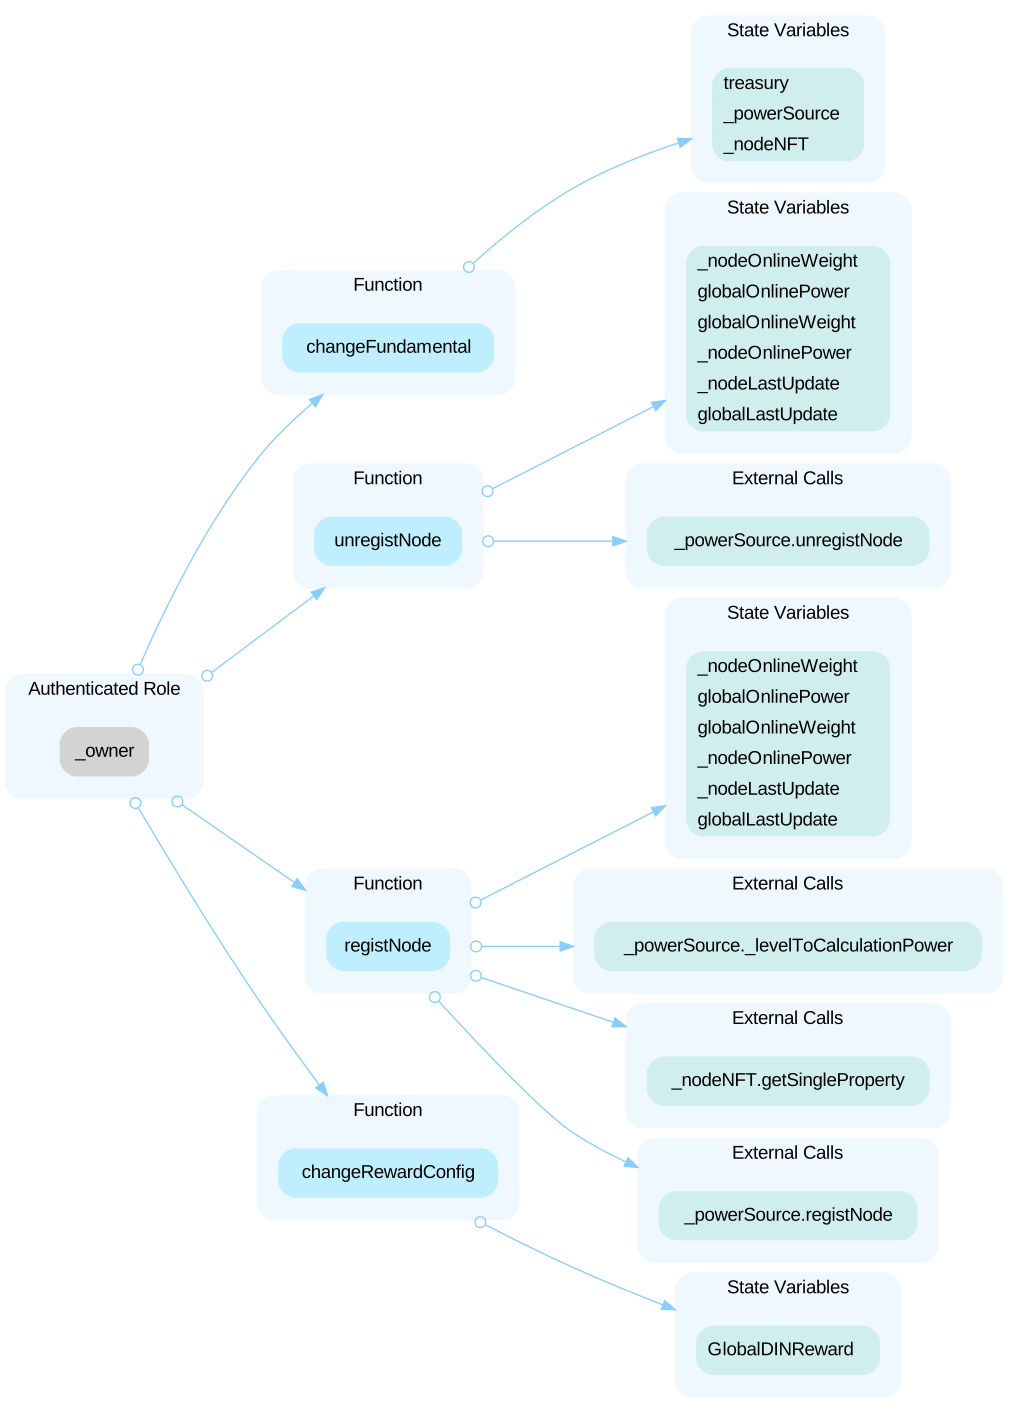 In the contract `OwnableUpgradeable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add a manager to the managers list, renounce ownership rights, transfer contract ownership to a new address, or remove a manager. 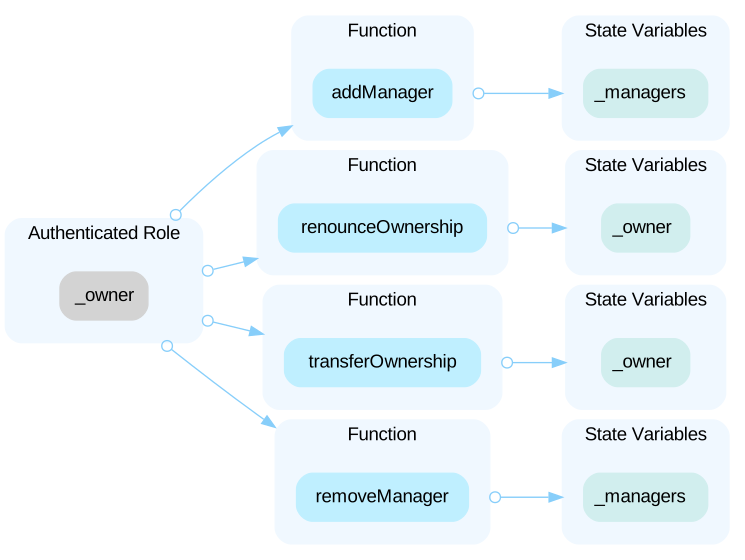 ----- In the contract `NFTAirdrop`, the role `_owner` has authority over the functions shown in the diagram below. The `_owner` role is tasked with defining the anticipated schedule for each power level, which includes setting the `amount`, `tgePercent`, `tgeTimestamp`, and `duration`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the console configuration or update the schedule type for a specific power level, which may affect the released amounts. 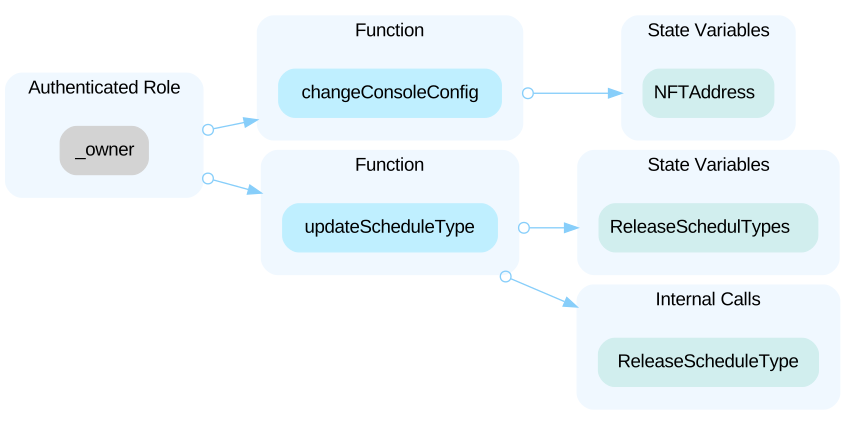 In the contract `OwnableUpgradeable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advanta
The audit on Trustblock · Open the reportIn the contract `DIN`, the role `onlyManager` has the authority to mint the token balance of an arbitrary account without sanity restriction. ```solidity function mint(address receipt, uint256 amount) public onlyManager { _mint(receipt, amount); } ``` Any compromise to the `onlyManager` role may allow a hacker to take advantage of this authority and manipulate users' balances.
The audit on Trustblock · Open the reportIn the contracts `CurveStaking`, `newStakingNative`, `NFTAirdropNative` and `xDINConvertingNative`, the role `admin` has the authority to update the implementation contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
The audit on Trustblock · Open the reportBased on the design of the staking-related contracts outlined above, the reward amounts used for calculation and distribution are fixed at the time of contract initialization. To ensure that users can claim rewards successfully, we would like to confirm with the team when the rewards will be transferred to the contract and whether the transferred amounts align with the initially specified reward amounts. Specifically, in the `CurveStaking` contract, where the staking token and reward token are the same, if rewards are not promptly transferred to the contract, claims may deplete other users' staked tokens. Besides, if enough rewards are sent to the contracts, there is also no function to withdraw the undistributed rewards.
The audit on Trustblock · Open the reportWhen calculating rewards for a specific `tokenId` in the `NFTAirdrop` contract, its corresponding `powerLevel` is determined based on the `tokenId`. Each level has unique reward release methods. If multiple `tokenIds` share the same `powerLevel`, this could lead to rewards being incorrectly calculated, potentially causing claims to exceed the intended allocation for that `powerLevel`.
The audit on Trustblock · Open the reportInitializer functions invoked separately from contract creation, such as in minimal proxies, may be reentered if they make an untrusted non-view external call. This reentrancy can lead to unexpected behaviors, breaking the expectation of a single execution.
The audit on Trustblock · Open the reportThe `stake()` functions attempt to ensure the successful transfer of ERC20 tokens by checking the return value of the `transfer()`/`transferFrom()` function. It assumes that `transfer()`/`transferFrom()` returns a `bool` indicating success or failure. However, some non-standard ERC20 tokens, such as [OMG](https://etherscan.io/address/0xd26114cd6ee289accf82350c8d8487fedb8a0c07#code#L97) and [USDT](https://etherscan.io/token/0xdac17f958d2ee523a2206206994597c13d831ec7#code#L340), do not return a `bool` for the `transfer()`/`transferFrom()` function. This discrepancy can cause the function to fail, leading to tokens being locked within the contract.
The audit on Trustblock · Open the reportIn contracts `NodeStakingConvertor` and `xDINConverting`, users can claim native tokens, however, the comments and related function names, such as in the following code, refer to `DIN` token. ```solidity // How much xDIN in exchange for // return how much DIN function depositXDIN(uint256 xDINAmount) public returns (uint256) { uint256 DINRewardAmount = estiamteExchangeDINAmount(xDINAmount); IERC20(xDINAddress).transferFrom(_msgSender(), address(this), xDINAmount); IERC20Authorized(xDINAddress).burn(xDINAmount); // mint DIN reward addClaim(_msgSender(), DINRewardAmount, nextClaimId); nextClaimId += 1; return DINRewardAmount; } ```
The audit on Trustblock · Open the reportThe `stake` function in the **CurveStaking** contract is responsible for allowing users to deposit a specific `amount` of tokens for staking. However, if the `amount` is not properly validated, it can lead to two potential issues: If a user stakes an extremely small `amount`, the resulting weight (`amount * time`) may become negligible due to the limitations of integer precision in Solidity (e.g., if the result rounds down to `0`).This can cause the user's shares of staking weight to be effectively `0`, making them ineligible to receive any rewards. Additionally, if a user stakes an extremely large `amount`, the calculation of `amount * time` (used to compute the user's staking weight) may exceed the maximum value that can be stored in a `uint256` variable, potentially causing an integer overflow or preventing more users to stake.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportThe `requestClaim()` function in the `NodeStakingConvertor` contract does not validate the length of the provided `nftIds`. Even if the `nftIds` array is empty, the function will still create a `ClaimSchedule` for `msg.sender` and allocate the `nextClaimId`, leading to unnecessary gas consumption.
The audit on Trustblock · Open the reportIn the `depositXDIN()` function of `xDINConverting` contract, user rewards are calculated based on the provided `xDIN` amount, followed by burning the transferred tokens. However, due to the absence of `DINRewardAmount` verification, the function burns the user's tokens even when the calculated `DINRewardAmount` is zero.
The audit on Trustblock · Open the reportThe cited address input is missing a check that it is not `address(0)`.
The audit on Trustblock · Open the reportThe change of `owner` by function `transferOwnership()` overrides the previously set `owner` with the new one without guaranteeing the new `owner` has the ability to actuate transactions on-chain.
The audit on Trustblock · Open the reportThe `CurveStaking` logic contract does not protect the initializer. An attacker can front-run the `initialize` call and assume ownership of the logic contract. Once in control, the attacker can perform privileged operations, misleading users into believing that they are interacting with the legitimate owner of the upgradeable contract.
The audit on Trustblock · Open the reportThe DIN security record · Every DIN address · This address on the explorer