0x3b058a6aa3d2abacf914971ef23423118e23c085
As of 21 Nov 2026, Trustblock’s record holds 0x3b058a6aa3d2abacf914971ef23423118e23c085 on BNB Chain as a contract of META GAUGE. 1 audit report on Trustblock lists this address: CertiK, 16 Dec 2022. 7 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Meta Gauge | CertiK | Not recorded (see the report) | Open |
3 High, 4 Low. In the firm’s own words; statuses are the firm’s, from each report.
The contract uses the users' allowances to the `owner` to represent swap balance, which allows the owner to call the function `transferFrom()` to control the part of the money. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and withdraw money from any wallet.
The audit on Trustblock · Open the reportIn the contract `AccessControl` the role `account` has authority over the functions shown in the diagram below. Any compromise to the `account` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 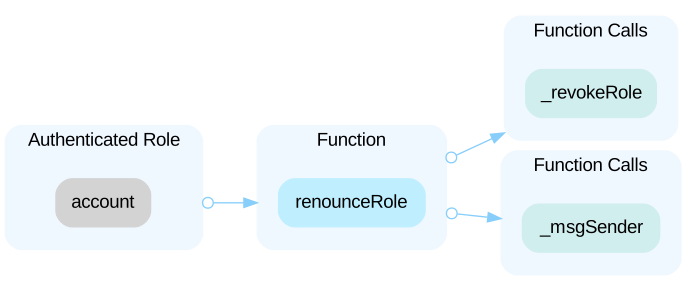 In the contract `MGRToken` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 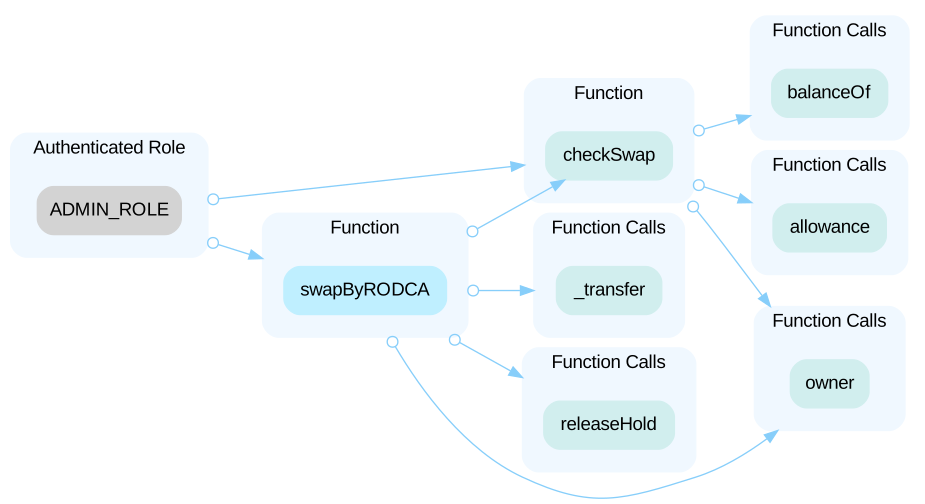 In the contract `MGRToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 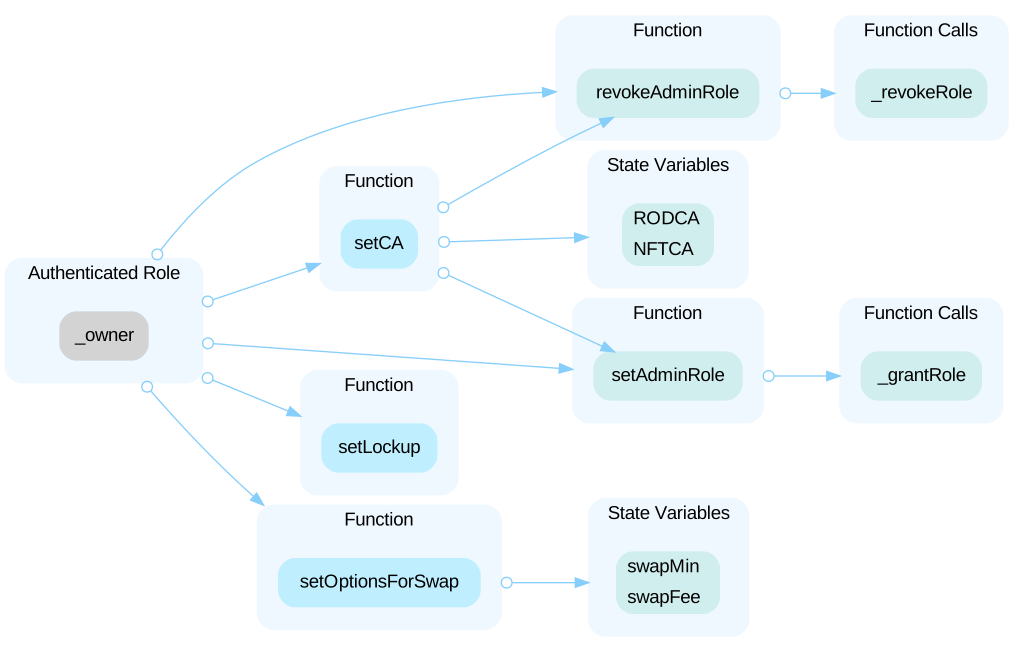 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 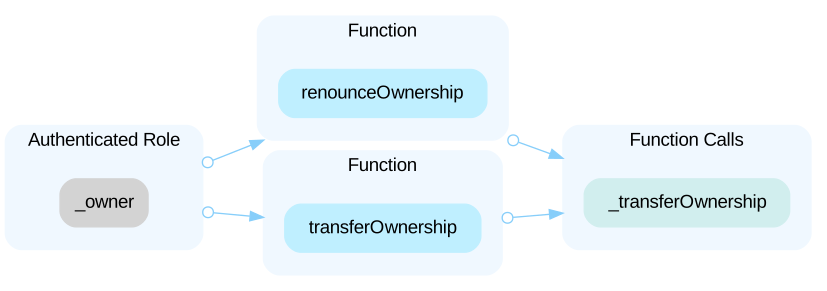
The audit on Trustblock · Open the reportAll **MGR** tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute **MGR** tokens without the consensus of the community.
The audit on Trustblock · Open the reportThe function `transfer()` and `transferFrom()` allow users to transfer to themselves. So the check at line 1248 may be not proper for such situation.
The audit on Trustblock · Open the reportFunctions that update state variables should emit relevant events as notifications.
The audit on Trustblock · Open the reportThe contract only process the MGR cost of the swap and the part of logic that proceed `rod` token transfers belongs to the `RODCA` contract.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with **RODCA** protocol whose implementation is not in the audit scope. The audit scope treats such dependencies as black boxes and assumes their functional correctness.
The audit on Trustblock · Open the reportThe META GAUGE security record · Every META GAUGE address · This address on the explorer