0x4481a01d7f5c8ec65ce963cb15d5bcfa05110524
As of 21 Nov 2026, Trustblock’s record holds 0x4481a01d7f5c8ec65ce963cb15d5bcfa05110524 on BNB Chain as a contract of Avrora. 1 audit report on Trustblock lists this address: CertiK, 23 Aug 2023. 10 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
4 High, 6 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `OwnableUpgradeable` the role `_owner` has authority over the functions shown in the diagram below. 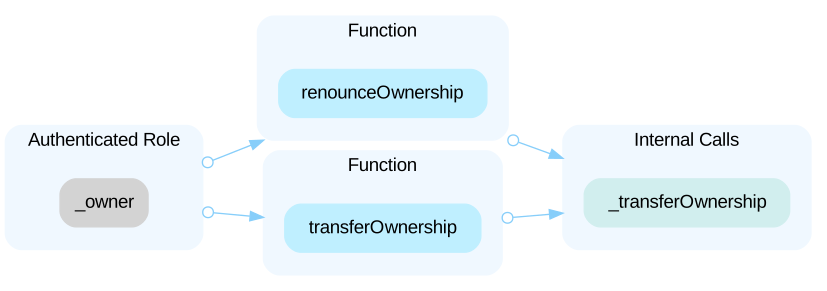 - `renounceOwnership()`: Allows the current owner to relinquish control of the contract. This will leave the contract without an owner and functions marked with the `onlyOwner` modifier will no longer be callable. The owner has exclusive access to this function. - `transferOwnership(address newOwner)`: Allows the current owner to transfer control of the contract to a newOwner. The owner has exclusive access to this function. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project --- In the contract `mAVRToken` the role `_owner` has authority over the functions shown in the diagram below. 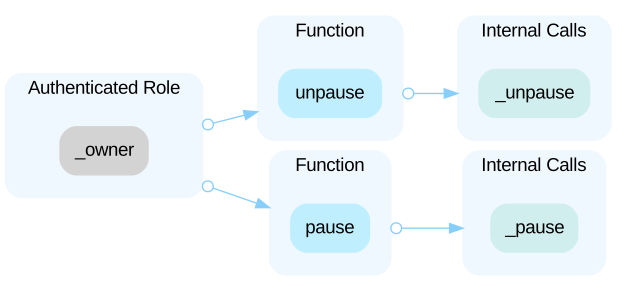 - `_pause()`: Triggers stopped state. The contract must not be paused. Can only be called by the owner. - `_unpause()`: Returns the contract to a normal state. The contract must be paused. Can only be called by the owner. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project
The audit on Trustblock · Open the reportIn the AVR protocol, the role `admin` has the authority to update the implementation contract behind the proxy contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
The audit on Trustblock · Open the reportAll of the `AVR` tokens are sent to several external addresses(listed below). This is a centralization risk because the owner(s) of the addresses can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project. - `_withdrawalsContractAddress` - `teamRevenue_` - `marketingWithdrawal_` - `liquidWithdrawal_` - `firstEOALiquidWithdrawal_` - `reserveWithdrawal_`
The audit on Trustblock · Open the reportAll of the `mAVR` tokens are sent to the contract deployer and several external addresses(listed below). This is a centralization risk because the deployer or the owner(s) of the addresses can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project. - `PlayToEarn` - `team` - `marketing` - `liquidity` - `reserve`
The audit on Trustblock · Open the reportPerforming integer division before multiplication truncates the low bits, losing the precision of calculation. ```solidity=783 _balances[msg.sender] = accountBalance - amount.div(100).mul(91); ``` --- ```solidity=785 _totalSupply -= amount.div(100).mul(91); ``` --- ```solidity=788 transfer(_withdrawalsContractAddress, amount.div(100).mul(9)); ``` ----- Performing integer division before multiplication truncates the low bits, losing the precision of calculation. ```solidity=1515 _balances[msg.sender] = accountBalance - amount.div(100).mul(90); ``` --- ```solidity=1516 _totalSupply -= amount.div(100).mul(90); ``` --- ```solidity=1517 transfer(_PlayToEarn, amount.div(100).mul(10)); ```
The audit on Trustblock · Open the reportAddresses are not validated before assignment or external calls, potentially allowing the use of zero addresses and leading to unexpected behavior or vulnerabilities. For example, transferring tokens to a zero address can result in a permanent loss of those tokens. ```solidity=763 _withdrawalsContractAddress = withdrawalsContractAddress_; ``` - `withdrawalsContractAddress_` is not zero-checked before being used. ```solidity=1482 _PlayToEarn = PlayToEarn; ``` - `PlayToEarn` is not zero-checked before being used.
The audit on Trustblock · Open the reportThe `require` check in the `burn()` function is redundant as it checks that `msg.sender` is not the zero address, but in reality, the zero address cannot initialize any transactions or calls.
The audit on Trustblock · Open the reportThe `initialize` function in the `mAVRToken` contract is responsible for the initial distribution of tokens to different addresses. However, it should be noted that the `initialize` function is not automatically called immediately after the deployment of the contract. This might lead to a potential front-running issue where a malicious actor can see the transaction that calls `initialize` before it is mined and then tries to take advantage of this situation.
The audit on Trustblock · Open the reportThe `SafeMath` library is used unnecessarily. With Solidity compiler versions 0.8.0 or newer, arithmetic operations will automatically revert in case of integer overflow or underflow. ```solidity=18 library SafeMath { ``` - An implementation of `SafeMath` library is found. --- ```solidity=747 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `AVR` contract. ```solidity=19 library SafeMath { ``` - An implementation of `SafeMath` library is found. --- ```solidity=1460 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `mAVRToken` contract.
The audit on Trustblock · Open the reportSome state variables are not used in the codebase. This can lead to incomplete functionality or potential vulnerabilities if these variables are expected to be utilized. Variable `_decimals` in `AVR` is never used in `AVR`. ```solidity=748 uint8 private _decimals; ``` ```solidity=745 contract AVR is ERC20 { ```
The audit on Trustblock · Open the reportThe Avrora security record · Every Avrora address · This address on the explorer