0x51a183d8d79df6892ab7b8f57b33ba70599515d4
As of 21 Nov 2026, Trustblock’s record holds 0x51a183d8d79df6892ab7b8f57b33ba70599515d4 on BNB Chain as a contract of Empire. 1 audit report on Trustblock lists this address: CertiK, 1 Mar 2023. 14 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
4 High, 3 Medium, 7 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Bridge` the role `validator` has authority over the functions below: - function `redeem()`: to transfer tokens to another chain. Any compromise to the `validator` account may allow the hacker to take advantage of this authority. In the contract `Bridge` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 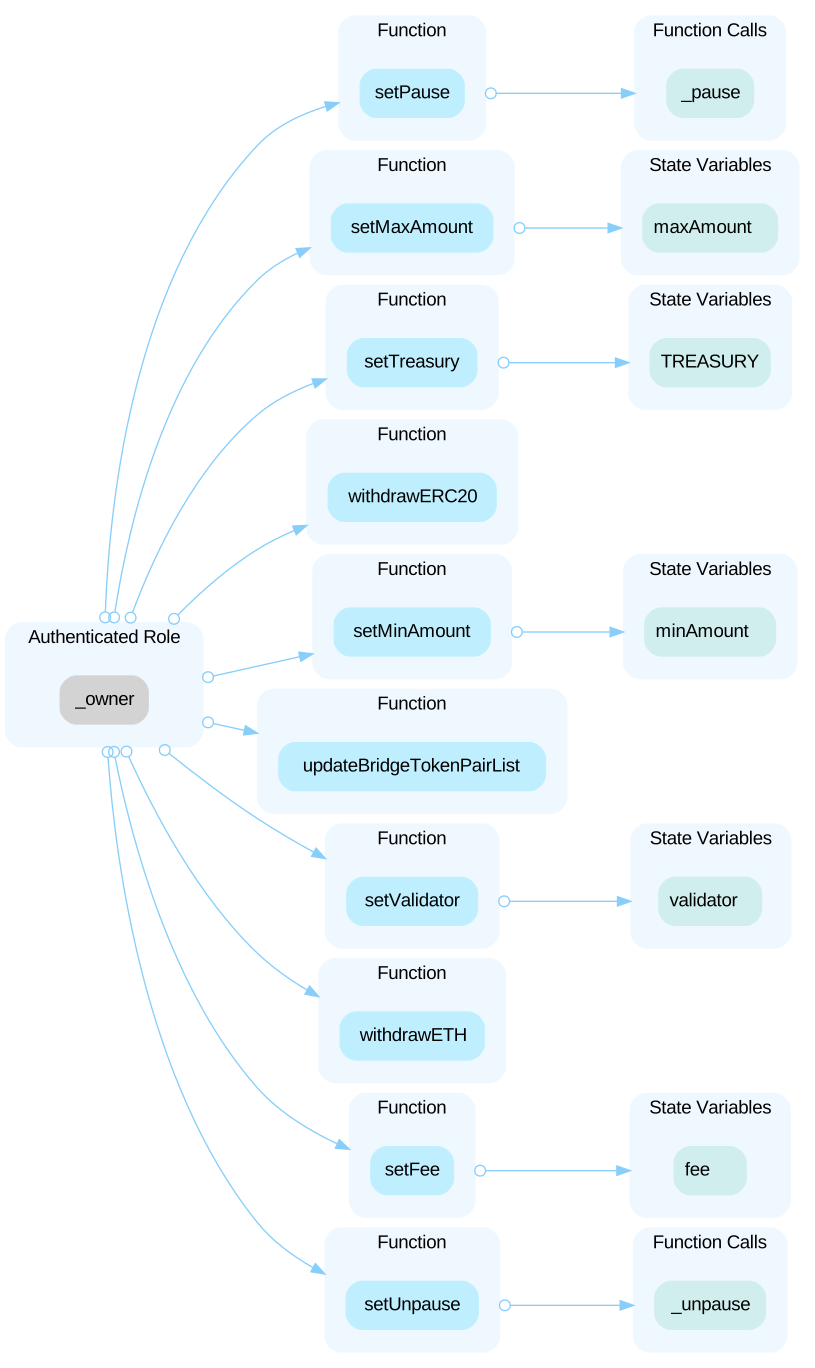
The audit on Trustblock · Open the reportIn the contract `EmpireToken` the role `_owner` has authority over the functions shown in the diagram below. 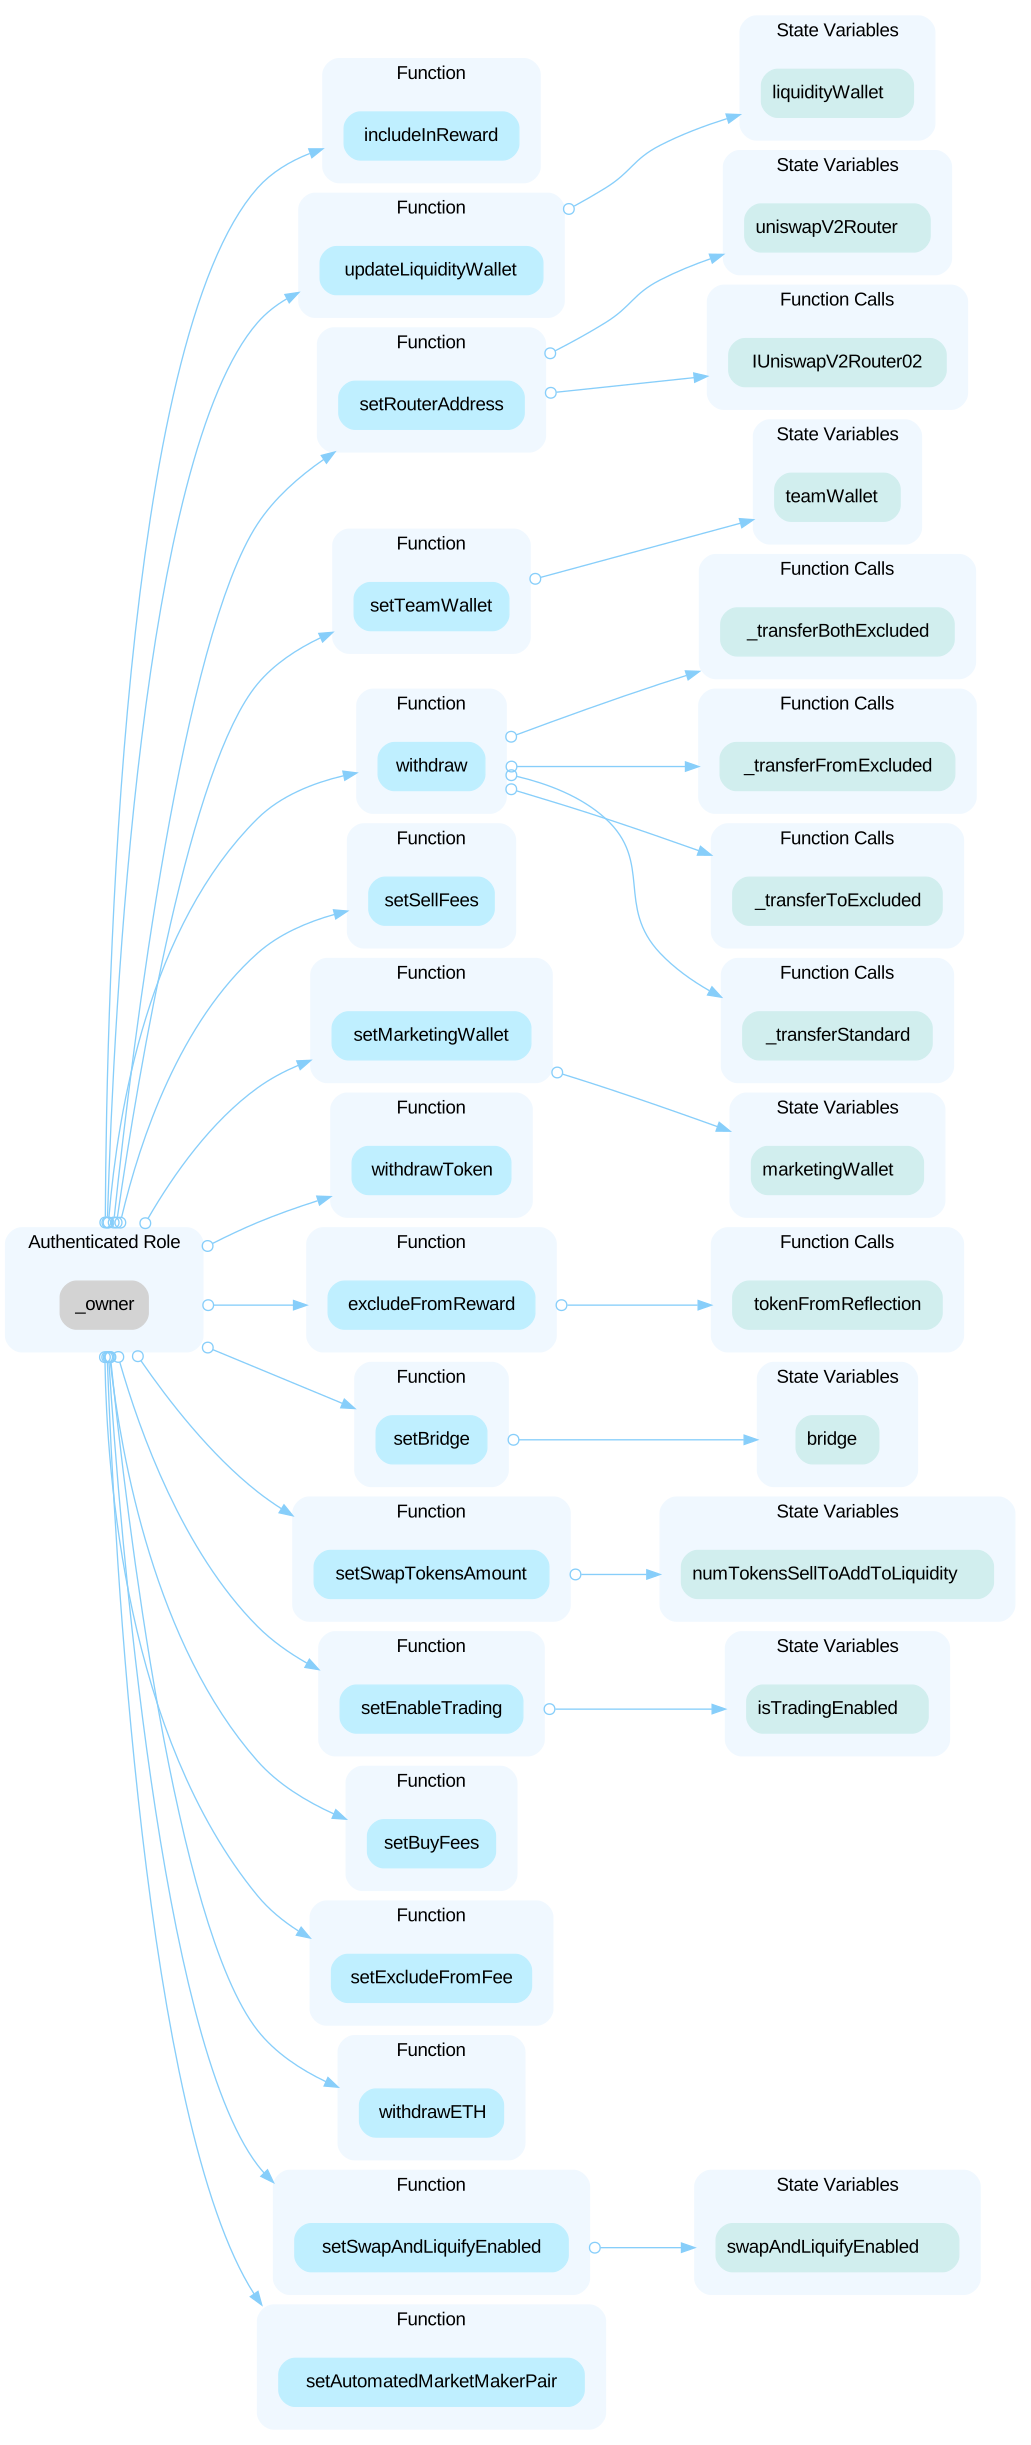 Besides, the role `_owner` also has authority over the function `setBridgeVault()`, which is used to set the `bridgeVault` by the owner. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. In the contract `EmpireToken` the role `bridge` has authority over the functions shown in the diagram below. 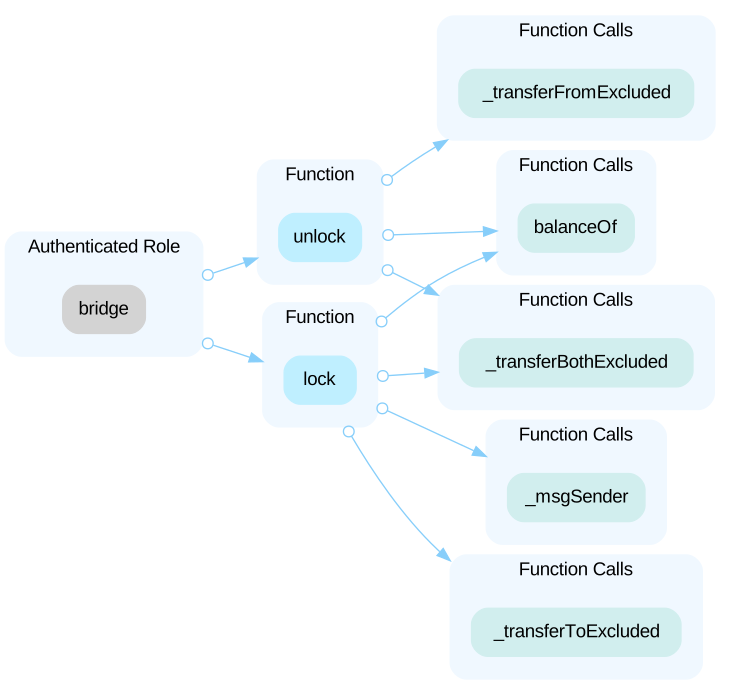 Any compromise to the `bridge` account may allow the hacker to take advantage of this authority.
The audit on Trustblock · Open the reportThe `addLiquidity` function calls the `uniswapV2Router.addLiquidityETH` function with the `to` address specified as `liquidityWallet` for acquiring the generated LP tokens from the `EmpireToken-BNB` pool. As a result, over time the `liquidityWallet` address will accumulate a significant portion of LP tokens. If the `liquidityWallet` is an EOA (Externally Owned Account), mishandling its private key can have devastating consequences for the project. ```solidity= function addLiquidity(uint256 tokenAmount, uint256 ethAmount) private { _approve(address(this), address(uniswapV2Router), tokenAmount); uniswapV2Router.addLiquidityETH{value: ethAmount}( address(this), tokenAmount, 0, 0, liquidityWallet, block.timestamp ); } ```
The audit on Trustblock · Open the reportThe logic ensures the cross-chain transaction atomicity is not implemented in the contract. The `validator` could be a message server host by the owner or an intermediate 3rd party application, hence the parameters in the `redeem()` function could not be guaranteed to correspond to the `swap()`. The scope of the audit treats the above-mentioned application entities as black boxes and assumes their functional correctness. However, in the real world, 3rd parties can be compromised, which may lead to lost or stolen assets. Suppose the cross-chain transaction atomicity is not guaranteed properly. In that case, the user deposits tokens into the source chain, but not be able to redeem the correct token amount from the target chain.
The audit on Trustblock · Open the reportThe implementation of the `isContract` check can not cover all scenarios. The check can be bypassed if the call is from the constructor of a smart contract or when the contract is destroyed. Because, in that case, the code size will also be zero.
The audit on Trustblock · Open the reportGenerally, deflationary tokens are incompatible with DEX and special rules need to be coded for DEX addresses eg. excluding them from reward. Otherwise, a hacker can exploit the protocol using the reflection mechanism. The balance of accounts that include rewards is calculated by `rAmount/rate`, where the rate is determined base on the total supply. If the `deliver()` function is executed with significant input, it can significantly decrease `rTotal`, thereby allowing for manipulation of the rate.
The audit on Trustblock · Open the report```solidity function includeInReward(address account) external onlyOwner() { require(account != bridgeVault, "Bridge Vault can't receive reward"); require(_isExcluded[account], "Account is already included"); for (uint256 i = 0; i < _excluded.length; i++) { if (_excluded[i] == account) { _excluded[i] = _excluded[_excluded.length - 1]; _tOwned[account] = 0; _isExcluded[account] = false; _excluded.pop(); break; } } } ``` Variable `_rOwned[account]` is not updated in the function `includeInReward()`, which will make the accounts included siphon off the tokens out of the balances of all token holders. The Rate was higher at the moment of the `excludeFromReward(account)` call, so the `_rOwned[account] / _tOwned[account]` ratio is bigger than expected for accounts included in the reward.
The audit on Trustblock · Open the reportThe **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
The audit on Trustblock · Open the reportIt is recommended to add the max transaction amount check as many other deflation tokens(e.g. Safemoon) do to prevent the big whale.
The audit on Trustblock · Open the reportPotential sandwich attacks could happen if calling `uniswapV2Router.swapExactTokensForETHSupportingFeeOnTransferTokens` and `uniswapV2Router.addLiquidityETH` without setting restrictions on slippage. For example, when we want to make a transaction of swapping 100 A Token for 1 Eth, an attacker could raise the price of Eth by adding A Token into the pool before the transaction so we might only get 0.1 Eth. After the transaction, the attacker would be able to withdraw more than he deposited because the total value of the pool increases by 0.9 Eth.
The audit on Trustblock · Open the reportSolidity version >=0.8.0 includes checked arithmetic operations and underflow/overflow by default, making SafeMath redundant.
The audit on Trustblock · Open the reportThe function `deliver` can be called by anyone. It accepts an uint256 number parameter `tAmount`. The function reduces the Empire token balance of the caller by `rAmount`, which is `tAmount` reduces the transaction fee. Then, the function adds `tAmount` to variable `_tFeeTotal`, which represents the contract's total transaction fee.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with third-party protocol, including: - `uniswapV2Router` The scope of the audit would treat those 3rd party entities as black boxes and assume their functional correctness. However, in the real world, 3rd parties may be compromised that led to assets being lost or stolen.
The audit on Trustblock · Open the reportThe return value of an external call is not stored in a local or state variable. ```solidity=809 uniswapV2Router.addLiquidityETH{value: ethAmount}( address(this), tokenAmount, 0, 0, liquidityWallet, block.timestamp ); ```
The audit on Trustblock · Open the reportThe Empire security record · Every Empire address · This address on the explorer