0x659049786cb66e4486b8c0e0ccc90a5929a21162
As of 21 Nov 2026, Trustblock’s record holds 0x659049786cb66e4486b8c0e0ccc90a5929a21162 on BNB Chain as a contract of TTcoin Network. 1 audit report on Trustblock lists this address: CertiK, 5 Nov 2024. 8 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
1 High, 1 Medium, 6 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `FreezableMintableToken`, the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and arbitrarily mint and freeze tokens until the specified date. 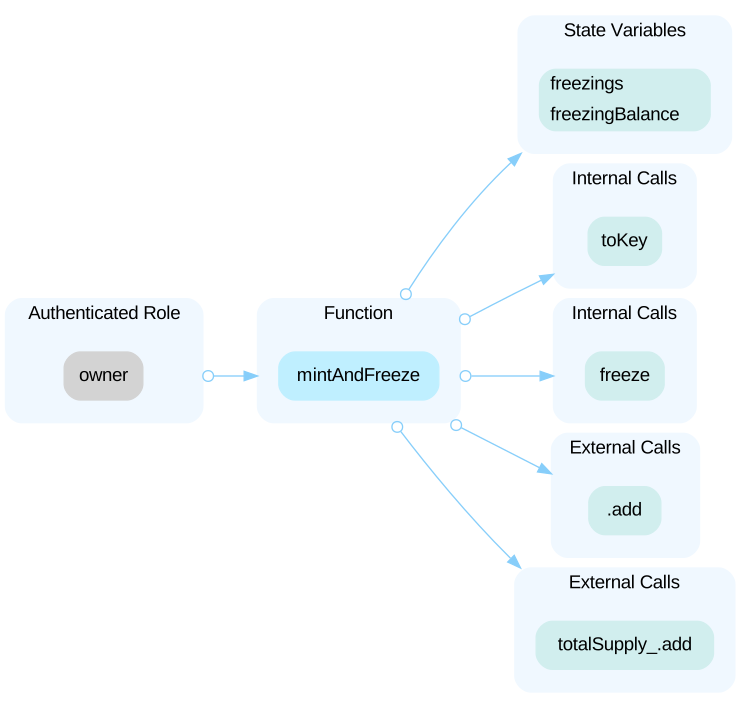 In the contract `MintableToken`, the role `owner` has authority over the functions shown in the diagram below.Any compromise of the owner account could enable the hacker to take advantage of this authority, permanently disable the contract's mint function, or arbitrarily mint tokens to others. 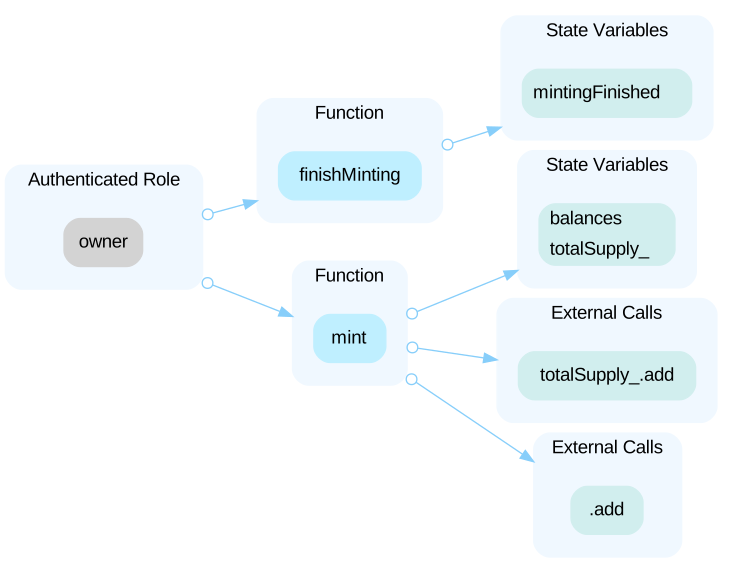 In the contract `Ownable`, the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and transfer ownership to a new owner or renounce the contract ownership. 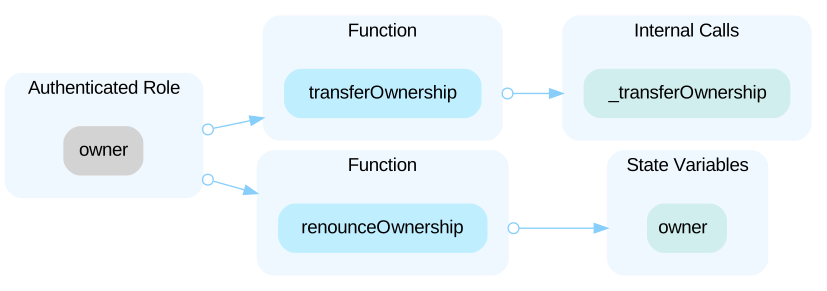 In the contract `Pausable`, the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and pause or unpause the contract. 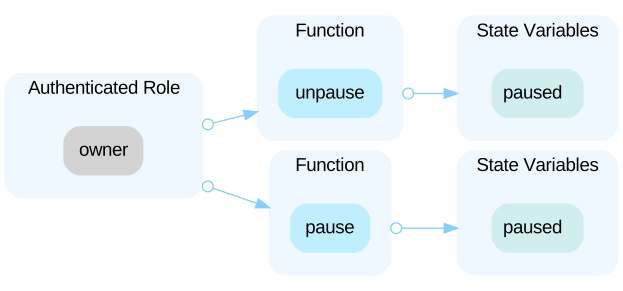 ---------------- Additionally, the contract's TARGET_USER and the initial allocation address for tokens are both the same address (0xfa3f237e89afa723d3e2b2907933f8b48354d189), which is not a contract wallet but an externally owned account (EOA).This could be a centralization risk as the owner can distribute `TTcoin` tokens without obtaining the consensus of the community.
The audit on Trustblock · Open the reportIn the `MainToken` contract, the functions `burn()`, `freezeTo()`, `releaseOnce()`, and `releaseAll()` can all be called by any user after the owner pauses the contract. This could allow users to modify the contract's variables even after the owner has halted its operation. Additionally, after the owner pauses the contract, although `transfer` and `transferFrom` cannot be called, any user can still transfer tokens in a short period using `freezeTo()` and `releaseOnce()` or `releaseAll()`, rendering the pause on `transfer` and `transferFrom` ineffective.
The audit on Trustblock · Open the reportThe cited address input is missing a check that it is not `address(0)`.
The audit on Trustblock · Open the reportThe logical vulnerability lies in the `freezeTo` function, which allows any user to freeze tokens to any address without a requirement that the `_amount` is greater than zero. If the victim has a pending release amount with a release date of `block.timestamp + p` and no earlier release amounts, the attacker can insert `p-1` nodes into the release chain, causing the victim to incur significantly higher gas costs when releasing. Specifically, the attacker can insert nodes in reverse order from `block.timestamp + p - 1`, `block.timestamp + p - 2`, ... to `block.timestamp`, achieving O(1) time complexity. Additionally, by setting the amount in `freezeTo()` to 0, the attacker can insert nodes at a low cost without holding the token.
The audit on Trustblock · Open the reportThe change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
The audit on Trustblock · Open the reportThe smart contract contains one or more values that are not used, which can lead to unnecessary complexity and reduced maintainability. ```solidity=536 parent = next; ``` - The variable `parent` is never used after this assignment.
The audit on Trustblock · Open the reportThe linked functions are equivalent to the compiler-generated getter functions for the respective variables.
The audit on Trustblock · Open the reportIn `mintAndFreeze`, the `Transfer` event should correspond to the minting style, namely `Transfer(address(0), _to, _amount)`. However, the event here is incorrect: `MainToken.sol` ```solidity=649 emit Mint(_to, _amount); emit Freezed(_to, _until, _amount); emit Transfer(msg.sender, _to, _amount); ```
The audit on Trustblock · Open the reportThe TTcoin Network security record · Every TTcoin Network address · This address on the explorer