0x6cdd08de79231a1957f205a3fe5cf9dbf4b0c454
As of 21 Nov 2026, Trustblock’s record holds 0x6cdd08de79231a1957f205a3fe5cf9dbf4b0c454 on BNB Chain as a contract of Baby Neiro. 1 audit report on Trustblock lists this address: CertiK, 20 Dec 2024. 15 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Baby Neiro | CertiK | Not recorded (see the report) | Open |
2 High, 5 Medium, 8 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `BabyNeiro`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and enable trading with a deadline, update the transaction limit, set fee exemption status for an address, update the sell tax rates, update developer address, update the marketing address, update wallet limit, update the buy tax rates, remove transaction and wallet limits, remove the transfer delay, set exemption from limits for an address, and update the swap token amount. 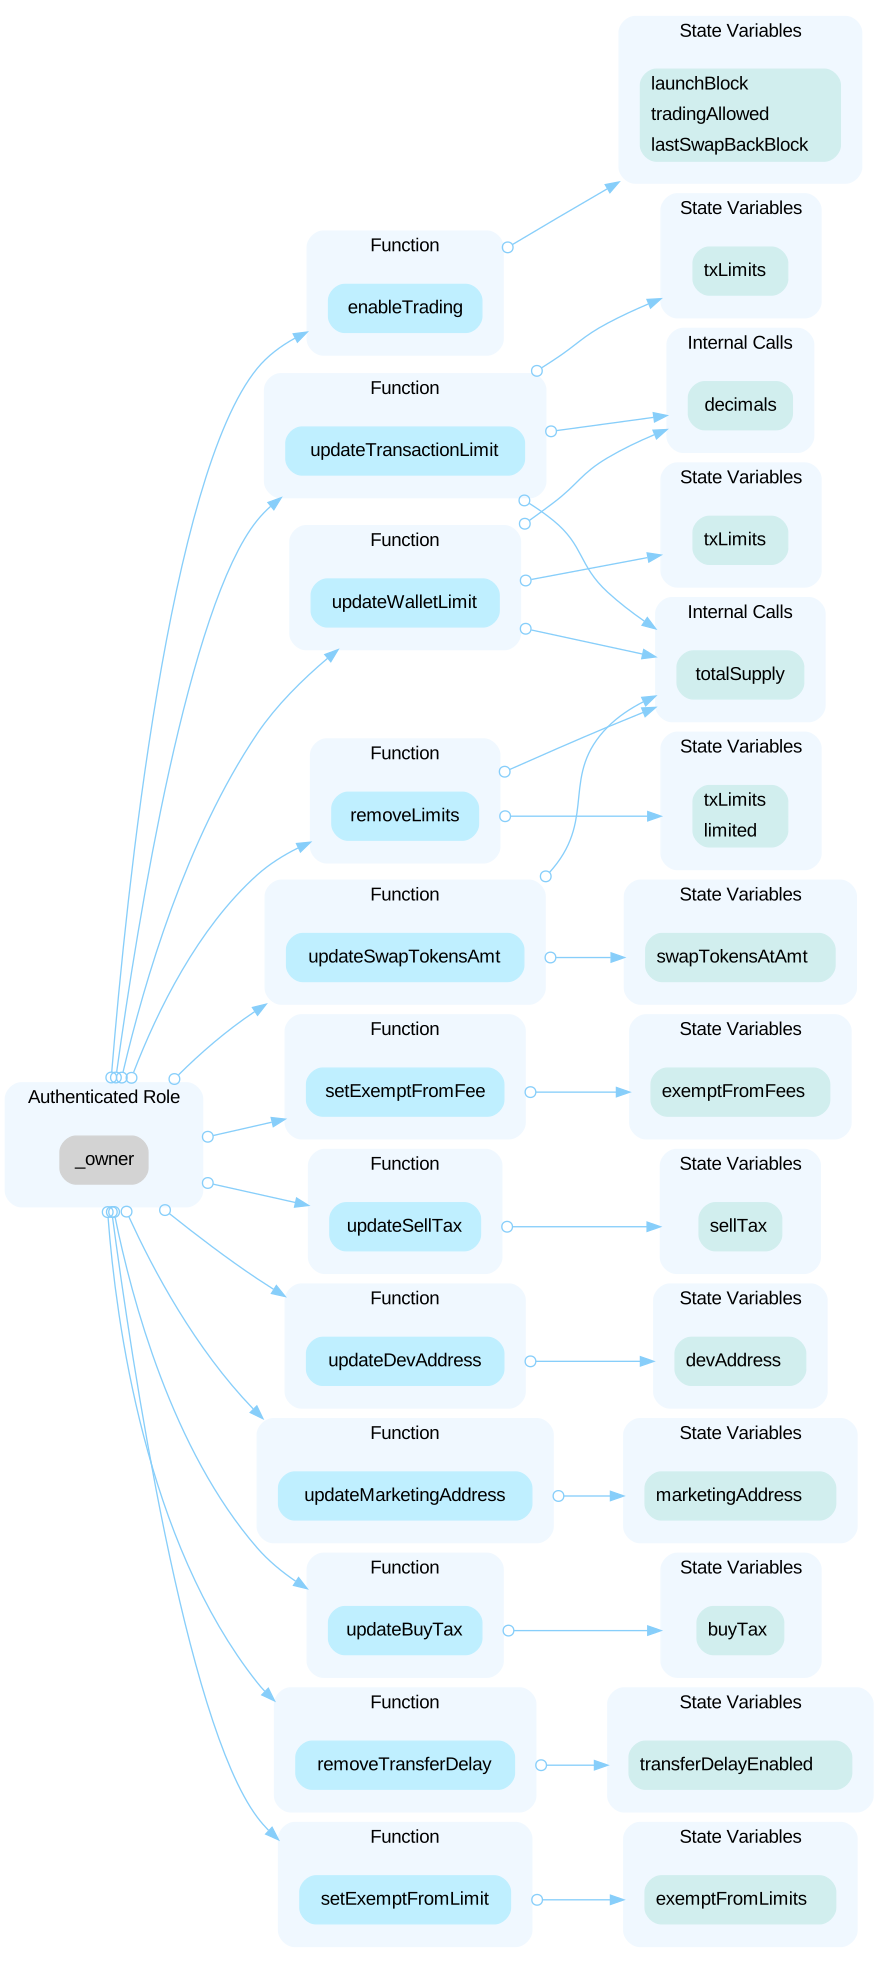 In the contract `BabyNeiro`, the role `devAddress` has authority over the functions shown in the diagram below. Any compromise to the `devAddress` account may allow the hacker to take advantage of this authority and move any amount of any ERC20 token the contract holds to the developer's address. 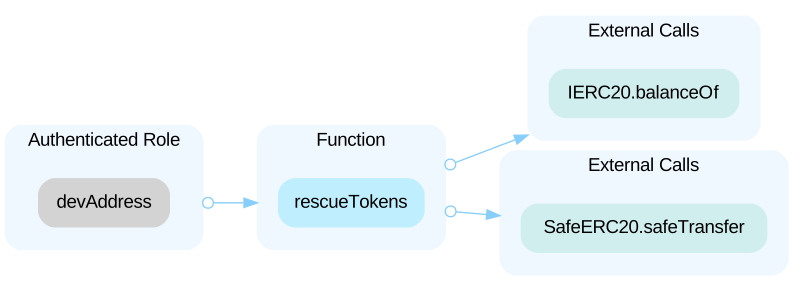 In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer contract ownership, renounce the contract ownership. 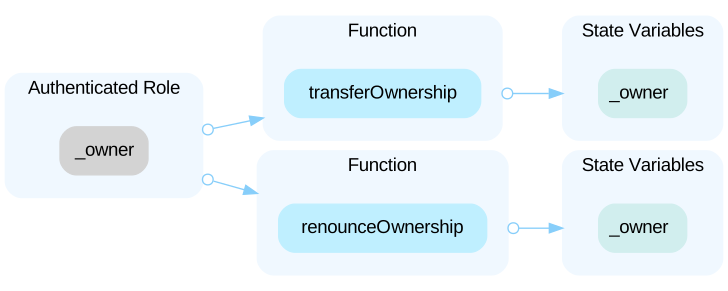
The audit on Trustblock · Open the reportAll of the `BabyNeiro` tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportTry-Catch is used when calling `addLiquidityETH()`, with a revert caught and returning instead of reverting the transaction. However, prior to this call, an amount of tokens are swapped for native tokens. This action will not be reverted and this amount of native token will remain in the contract. While this amount can be rescued, it is not ensured to be allocated to liquidity. In addition, the accounting variables `tokensForTax` are not adjusted, so that they do not handle the amount of tokens that were converted and not succesfully added to liquidity.
The audit on Trustblock · Open the reportSome restrictions can be bypassed by swapping tokens to the router and then getting tokens from the router. When the tokens are transferred to the router, the attacker uses the feature of the router function ***`removeLiquidityETHSupportingFeeOnTransferTokens`***, which will send all the specified tokens in the router to a specified address. Because the router is not supposed to receive tokens for any user other than remove liquidity.
The audit on Trustblock · Open the reportThe check `require(_holderLastTransferBlock[tx.origin] + 30 < block.number, "Transfer Delay");` is used to try to delay transfers. However, as `tx.origin` is used, a user can avoid this delay by giving approval to different accounts, which can then transfer tokens on their behalf via `transferFrom()`. As the other accounts execute a transaction to call `transferFrom()`, they will be the `tx.origin`, and thus not be subjected to the delay of others.
The audit on Trustblock · Open the reportThe linked statement transfers the native token leftovers in `BabyNeiro` contract. Because the `address.call()` function returns false if the aforementioned transaction is failed, the local variable `success` should be checked or using `address.transfer()` which reverts when transaction is failed.
The audit on Trustblock · Open the reportThe smart contract does not check or store the return value of an external call in a local or state variable, which may introduce vulnerabilities due to the unhandled outcome. ```solidity=856 try dexRouter.addLiquidityETH{value: newBalance}( address(this), secondMath, 0, 0, DEAD, block.timestamp ){} catch {return;} ```
The audit on Trustblock · Open the reportThe transaction may be charged fees, so the max holding of the receiver should be the sum of the held tokens and the amount received from the transfer. The fees should not necessarily be included in the max holding. ```solidity=768 require(amount + balanceOfTo <= _txLimits.walletLimit, "Max Wallet"); ``` - Max holding is checked. ```solidity=746 amount -= handleTax(from, to, amount); ``` - Receiving amount is adjusted. ```solidity=302 _balances[to] += amount; ``` - Balance is increased by the adjusted amount.
The audit on Trustblock · Open the reportPrivileged functions should include emittance of corresponding events.
The audit on Trustblock · Open the reportA sandwich attack can occur when an attacker notices a transaction involving token swaps or liquidity additions that lacks slippage restrictions or minimum output amount settings. The attacker can exploit this by frontrunning the transaction to purchase one of the assets, thereby manipulating the exchange rate, and then backrunning the transaction to sell the asset for a profit. The referenced functions are invoked without setting slippage restrictions or minimum output amounts, making transactions that trigger these functions particularly vulnerable to sandwich attacks, especially when large input amounts are involved.
The audit on Trustblock · Open the reportIf `newNumInTokens` is too high in functions `updateWalletLimit()` or `updateTransactionLimit()` then the multiplication of the value by `10**decimals()` will cause an overflow when casting the value to type `uint128`.
The audit on Trustblock · Open the reportTransaction limits are only checked if one of the addresses involved in the transfer are not exempt from fees. Some addresses may be set to be exempt from fees but still have a transaction limit. For example, the `dexRouter` is set to be exempt from fees, but is not exempt from transaction limits.
The audit on Trustblock · Open the reportValue `doNothing` is initialized at 0 and can be updated by anyone to add a value of 2 to its previous state each time it is called. It appears variable `doNothing` is not used within the contract. It appears variable `antiMevEnabled` is not used within the contract.
The audit on Trustblock · Open the reportThe smart contract contains one or more values that are not used, which can lead to unnecessary complexity and reduced maintainability. ```solidity=866 totalTokensToSwap -= tokensForTaxMem.tokensForLiquidity; ``` - The variable `totalTokensToSwap` is never used after this update.
The audit on Trustblock · Open the reportIf the call to `addLiquidityETH` fails during the try-catch logic, then the function `convertTaxes()` will return without further update. This will cause an inconsistency because `contractBalance` and `totalTokensToSwap` will not be updated even though about half of the `liquidityTokens` has been removed through the prior call to `swapTokensForETH(firstmath)`.
The audit on Trustblock · Open the reportThe Baby Neiro security record · Every Baby Neiro address · This address on the explorer