0x72b6887a46043c1299d3dae707893123d47cf73d
As of 21 Nov 2026, Trustblock’s record holds 0x72b6887a46043c1299d3dae707893123d47cf73d on BNB Chain as a contract of Qrkita. 1 audit report on Trustblock lists this address: CertiK, 30 May 2023. 4 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Qrkita Exchange | CertiK | Not recorded (see the report) | Open |
2 High, 2 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `QrkitaToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and include/exclude account from fee/reward, enable/disable fees and `swap and liqufy` process, withdraw BNB from the contract, and change marketing wallet address. 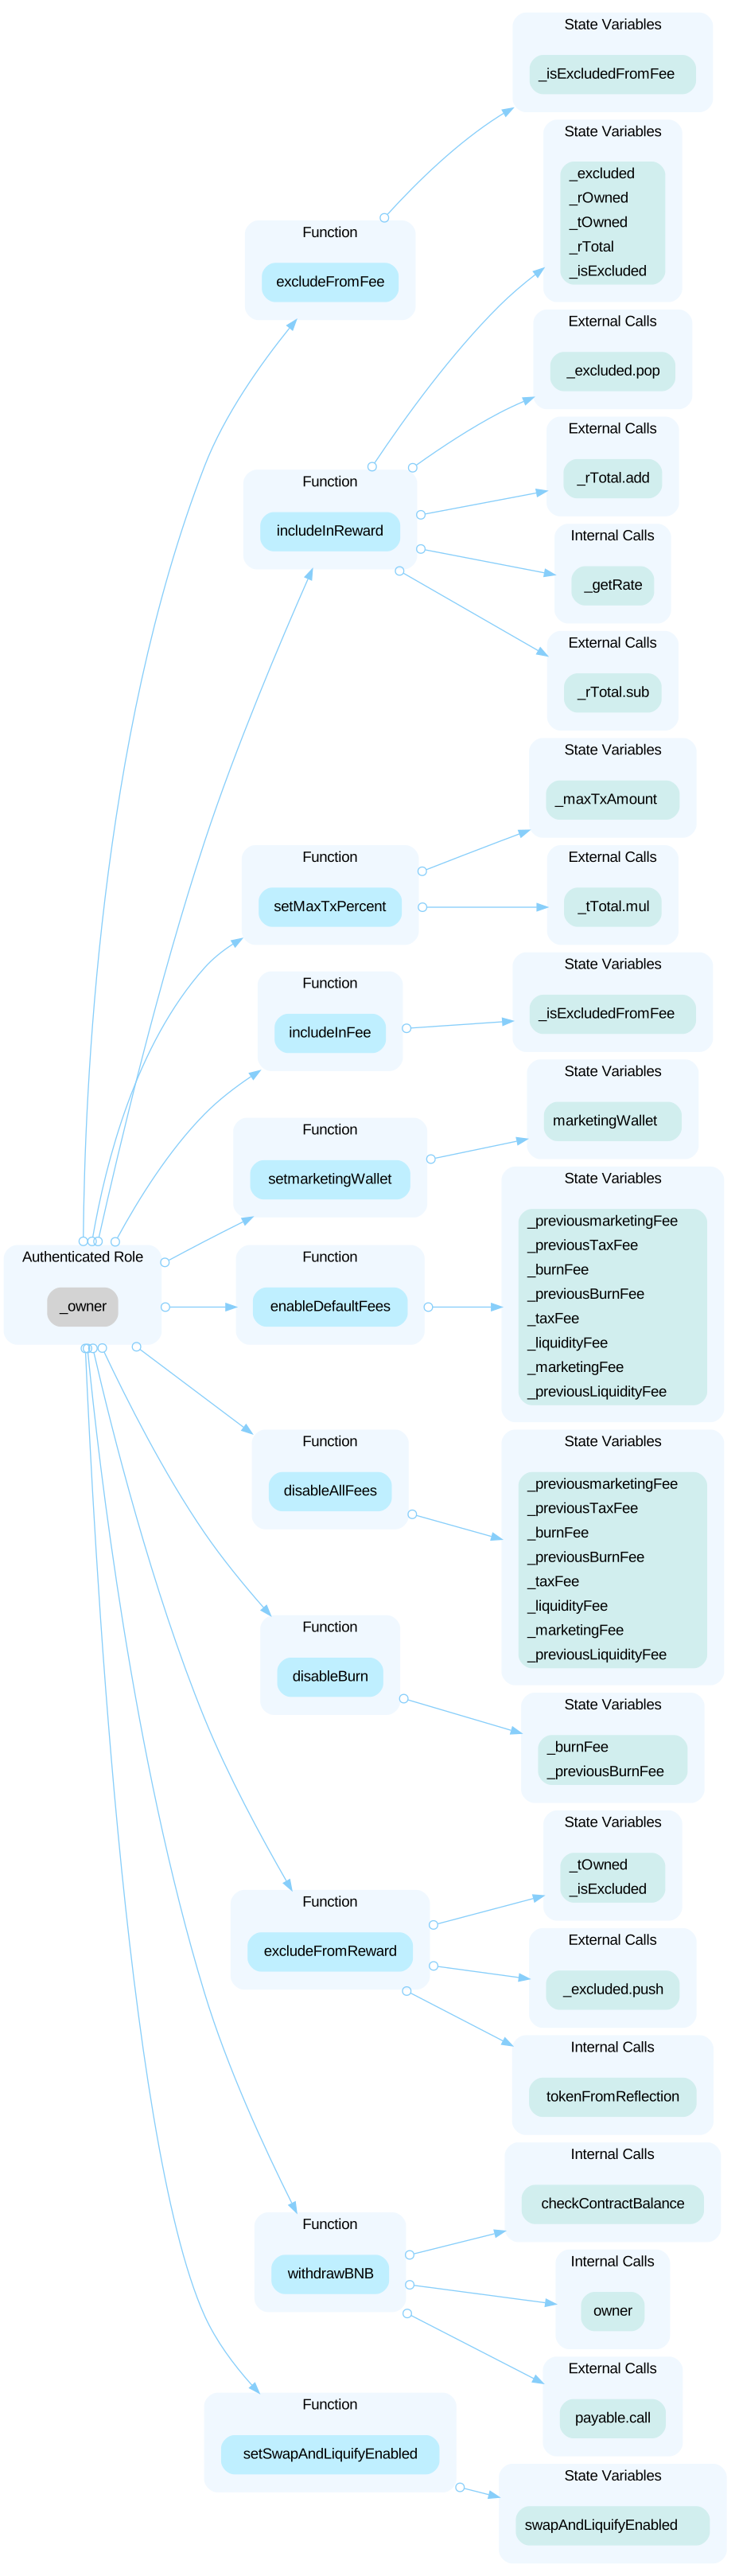
The audit on Trustblock · Open the reportAll TQRT tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute TQRT tokens without the consensus of the community.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with third party PancakeSwap protocols. The scope of the audit treats 3rd party entities as black boxes and assume their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts, such as increasing fees of 3rd parties, migrating to new LP pools, etc.
The audit on Trustblock · Open the reportThe LP token is sent to the contract address. But there is no way to retrieve the token from the contract.
The audit on Trustblock · Open the reportThe Qrkita security record · Every Qrkita address · This address on the explorer