0x7d18f3fe6e638fad0adacc5db1a47f871a2c2cc4
As of 21 Nov 2026, Trustblock’s record holds 0x7d18f3fe6e638fad0adacc5db1a47f871a2c2cc4 on BNB Chain as a contract of DollarMoon. 1 audit report on Trustblock lists this address: CertiK, 30 May 2023. 15 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Dollarmoon - Audit 1 | CertiK | Not recorded (see the report) | Open |
4 High, 1 Medium, 10 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `DollarMoonDividendTracker` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 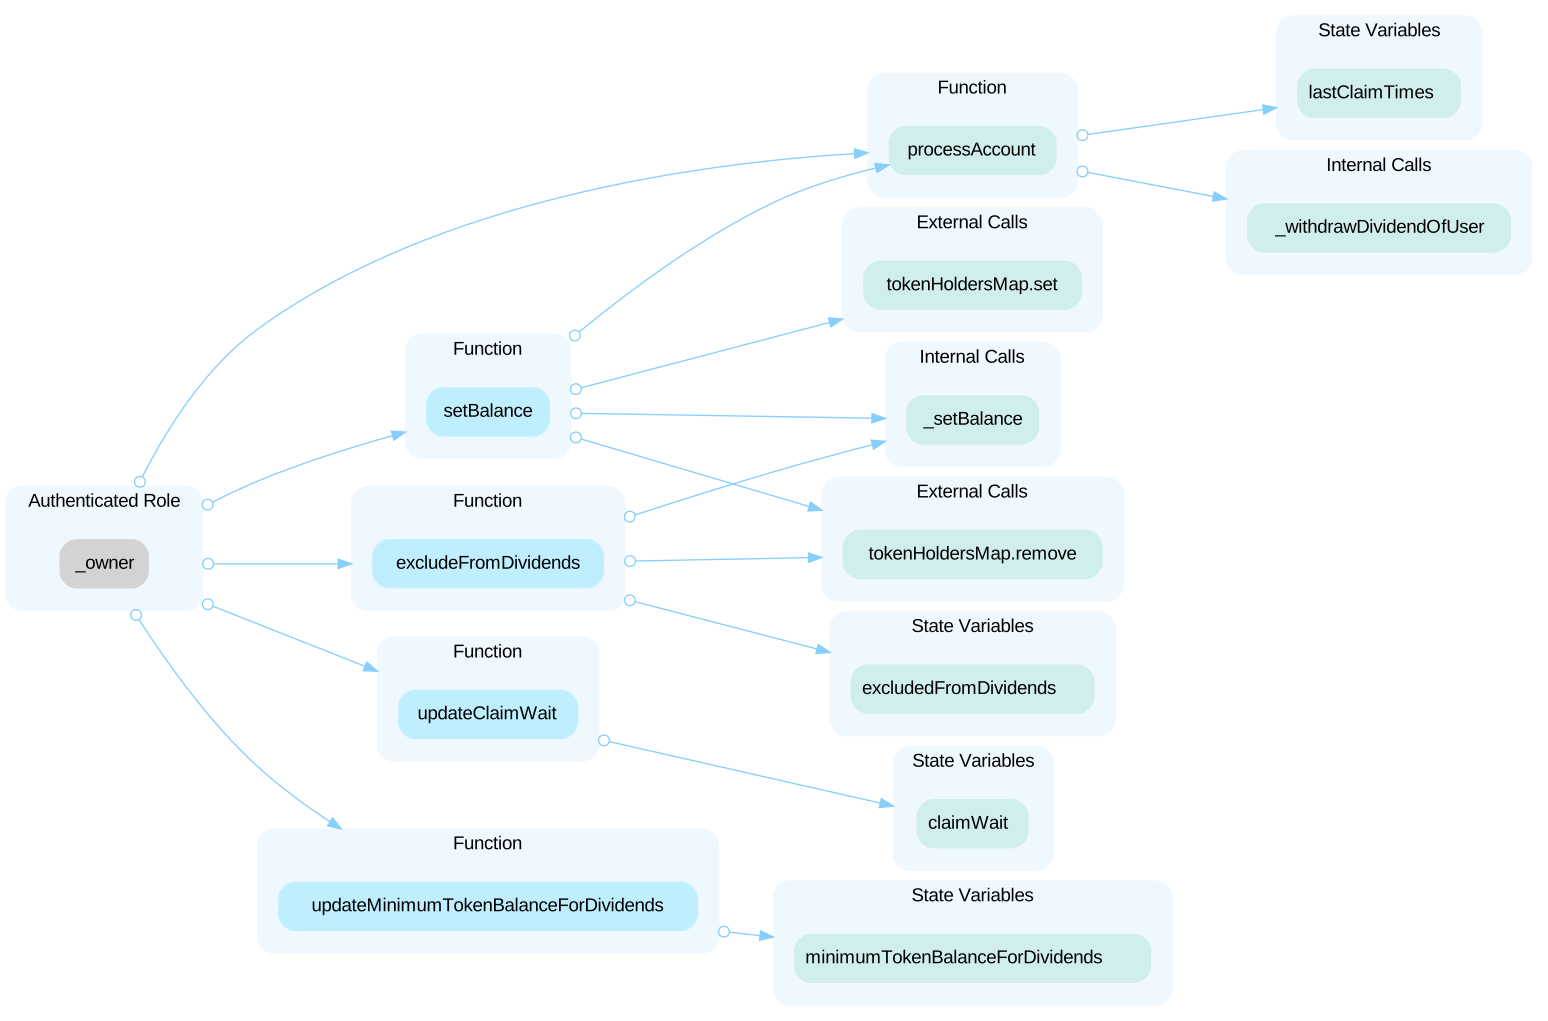 In the contract `DollarMoon` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 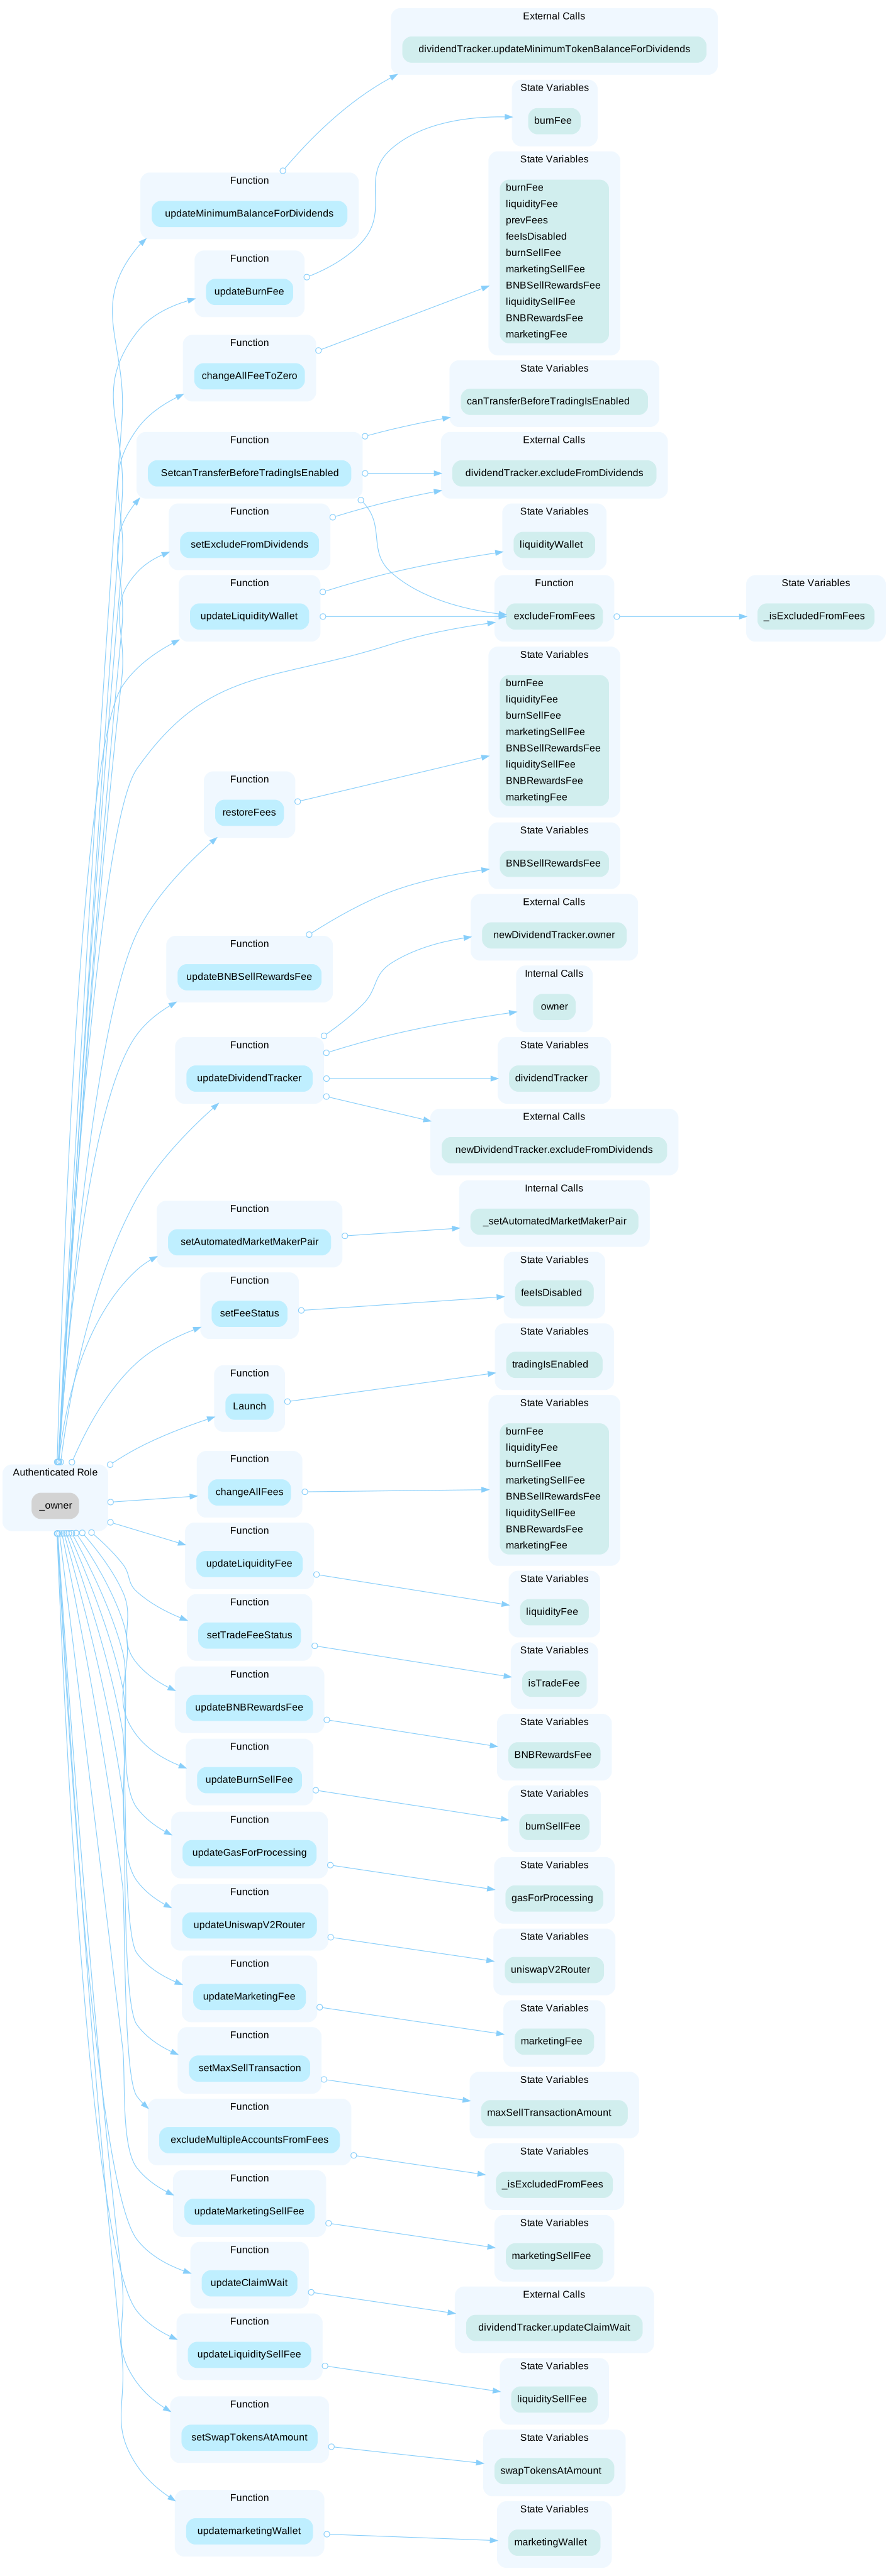
The audit on Trustblock · Open the reportAll 200000000 Dmoon tokens are sent to the contract deployer 0x3dd83aa46ed8549c9905ee943fac70ea7391ab66 when deploying the contract. This is a potential centralization risk as the deployer can distribute Dmoon tokens without the consensus of the community.
The audit on Trustblock · Open the reportIf the user has called the `transfer()` function, the dividend of the user will be recorded and the user will get the dividend token. But if the owner calls `updateDividendTracker` to change the dividend tracker address to a new address, the records of all dividends will be lost and the reward can not withdrawn.
The audit on Trustblock · Open the reportIn the `_transfer` function, there is a restriction when the user tries to sell this token to a AMM pair, as in the following statement. ```solidity=1634 require(amount <= maxSellTransactionAmount, "Sell transfer amount exceeds the maxSellTransactionAmount."); ``` While in the `setMaxSellTransaction` function, there's no restriction in setting `maxSellTransactionAmount`. If the owner sets `maxSellTransactionAmount` as 0, users would not be able to sell tokens.
The audit on Trustblock · Open the report```solidity=1252 gasForProcessing = 300000; ``` ```solidity=1707 uint256 gas = gasForProcessing; try dividendTracker.process(gas) returns ( ``` At the last step of the function `_transfer`, function `dividendTracker.process` was called with constant gas limitation `300000`. But there may be not enough 300000 gas till this step. EVM may revert this call and return the out-of-gas exception.
The audit on Trustblock · Open the reportThe `uniswapV2Router` is excluded from receiving dividend at contract deployment, but will start receiving dividend when `uniswapV2Router` is updated.
The audit on Trustblock · Open the reportThe `DEAD` address is not excluded from dividends. In this case, the burned tokens still sharing dividends, and the dividends will be left over to the `DividendTracker` contract.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportThe **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
The audit on Trustblock · Open the reportA sandwich attack may happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (executing before the target) a transaction to purchase one of the assets and make profits by backrunning (executing after the target) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `swapTokensForEth()` - `swapAndSendMarketingBNB()`
The audit on Trustblock · Open the reportState variables that never change should be declared as `constant` to save gas. ```solidity=1232 address public deadAddress = 0x000000000000000000000000000000000000dEaD; ``` - `deadAddress` should be declared `constant`.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=1219 IUniswapV2Router02 public uniswapV2Router; ``` - The contract `DollarMoon` interacts with third party contract with `IUniswapV2Router02` interface via `uniswapV2Router`.
The audit on Trustblock · Open the reportThe return value of an external call is not stored in a local or state variable. ```solidity=1592 dividendTracker.processAccount(msg.sender, false); ``` --- ```solidity=1813 uniswapV2Router.addLiquidityETH{value: ethAmount}( address(this), tokenAmount, 0, // slippage is unavoidable 0, // slippage is unavoidable liquidityWallet, block.timestamp ); ```
The audit on Trustblock · Open the reportOne or more state variables are never used in the codebase. Variable `MAX_INT256` in `SafeMathInt` is never used in `SafeMathInt`. ```solidity=408 int256 private constant MAX_INT256 = ~(int256(1) << 255); ``` ```solidity=406 library SafeMathInt { ```
The audit on Trustblock · Open the reportThe linked functions are equivalent to the compiler-generated getter functions for the respective variables.
The audit on Trustblock · Open the reportThe DollarMoon security record · Every DollarMoon address · This address on the explorer