0x860e3012a005eb30e634f3bc787a36a405ac42b9
As of 21 Nov 2026, Trustblock’s record holds 0x860e3012a005eb30e634f3bc787a36a405ac42b9 on BNB Chain as a contract of Leaven Network. 1 audit report on Trustblock lists this address: CertiK, 29 Sep 2022. 20 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Leaven Network - Audit | CertiK | Not recorded (see the report) | Open |
2 High, 18 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `LeavenVaultV6` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify contract parameters such as fees and strategies. 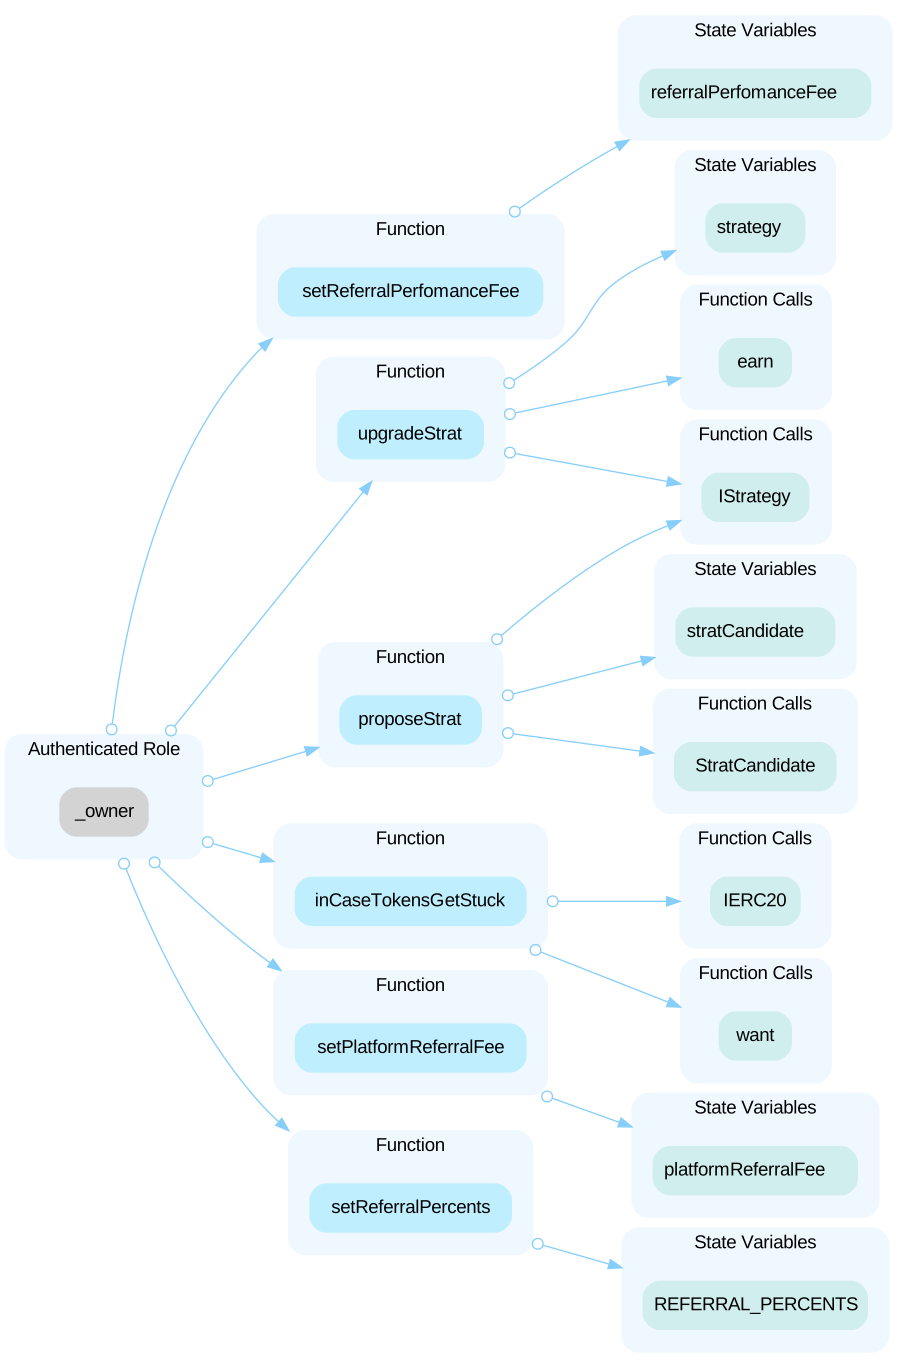 Furthermore, the role `_owner` has authority over the functions `transferOwnership()` and `renounceOwnership()`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the `_owner` address. 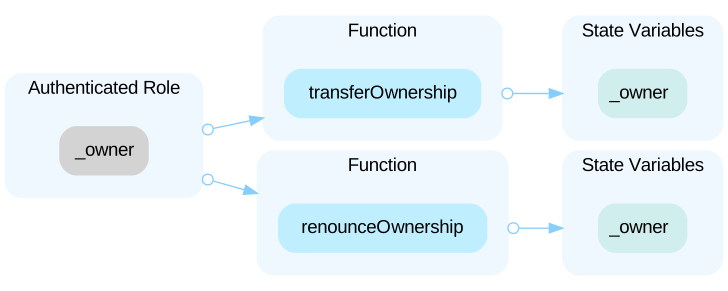
The audit on Trustblock · Open the reportIn the contract `StrategyCakeBoostedLP`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update several contract settings such as the fee recipient. 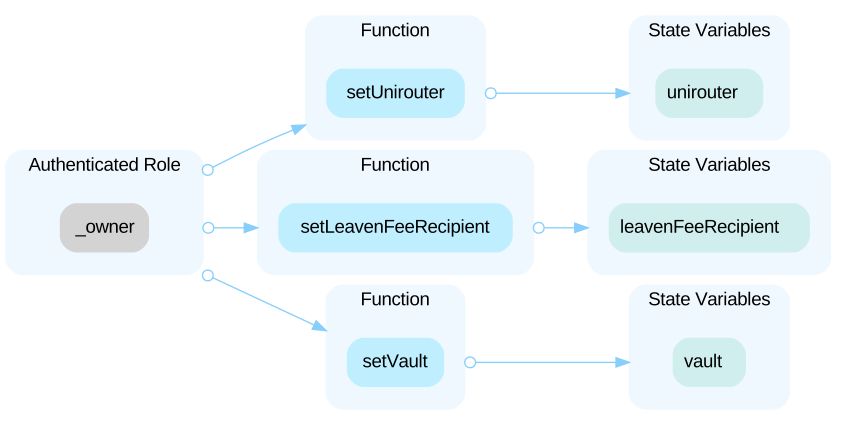 Furthermore, the role `_owner` has authority over the function `setBoostStaker()`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and configure the `BoostStaker`. Additionally, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the owner (`_owner` address) of the contract. 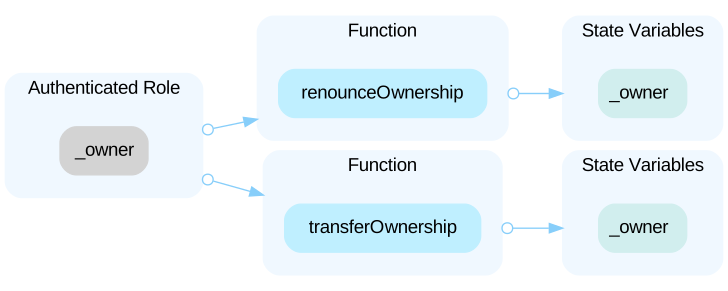 The role `keeper` has authority over the functions shown in the diagram below. Any compromise to the `keeper` account may allow the hacker to take advantage of this authority and pause or unpause the deposits and withdrawals and update other harvest parameters. 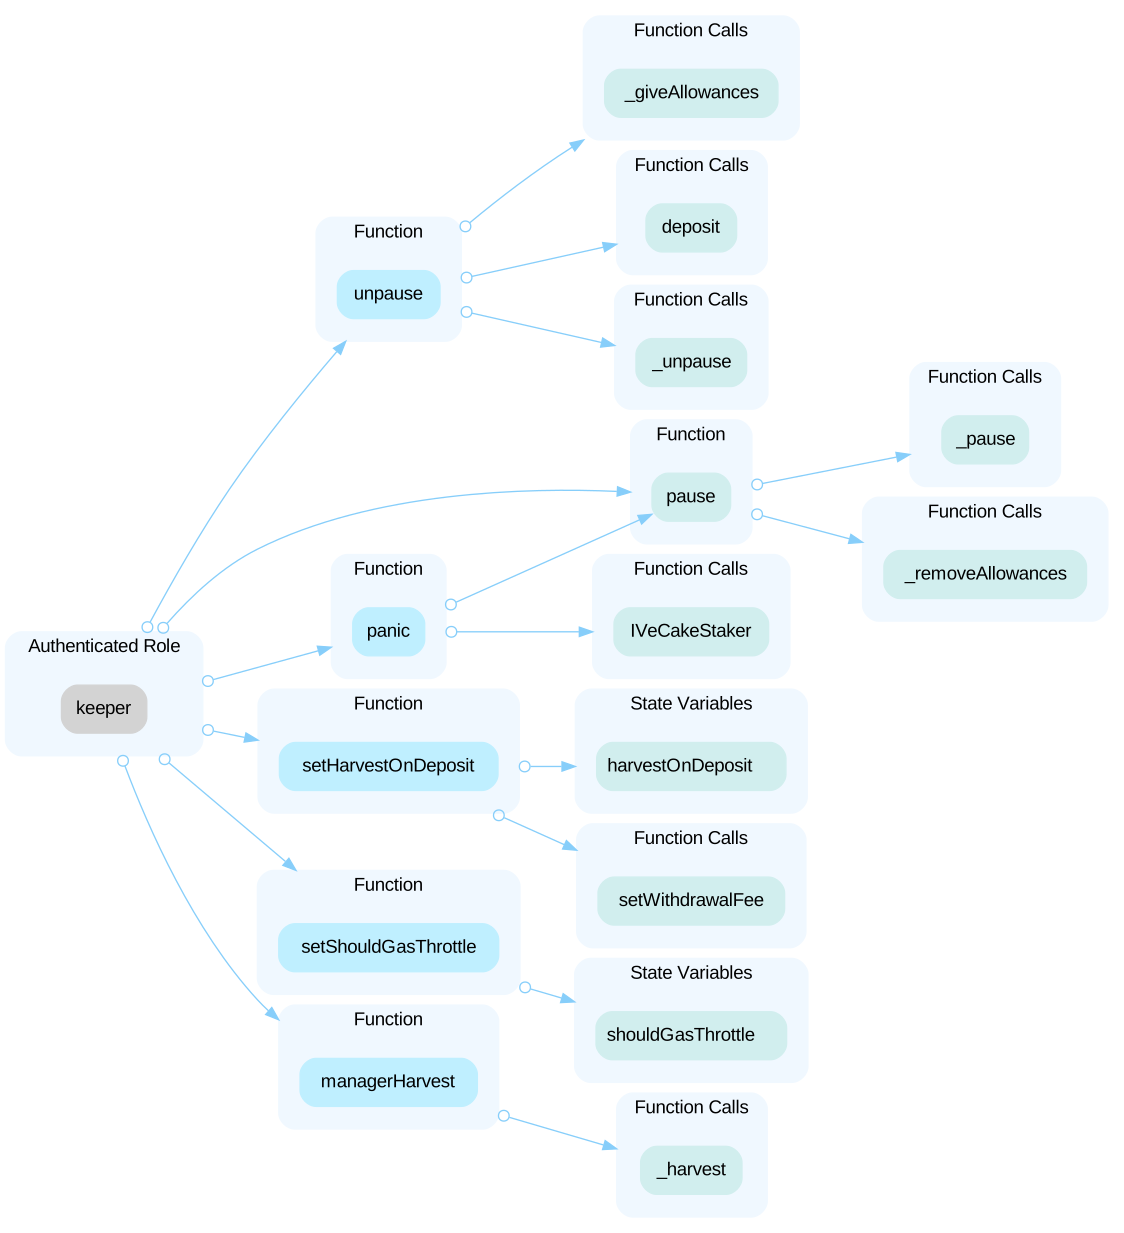 Furthermore, the role `keeper` has authority over the functions shown in the diagram below. Any compromise to the `keeper` account may allow the hacker to take advantage of this authority and update fee settings. 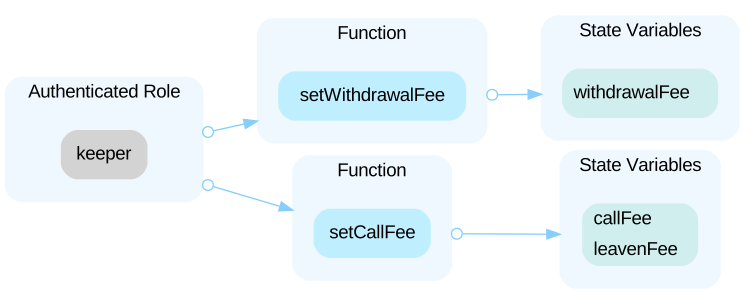 Additionally, the role `keeper` has authority over the function `setKeeper()`. Any compromise to the `keeper` account may allow the hacker to take advantage of this authority and update the `keeper` address. The role `strategist` has authority over the function `setStrategist()`. Any compromise to the `strategist` account may allow the hacker to take advantage of this authority and update the `strategist` address. Finally, the role `vault` has authority over the functions shown in the diagram below. Any compromise to the `vault` account may allow the hacker to take advantage of this authority and withdraw strategy funds. 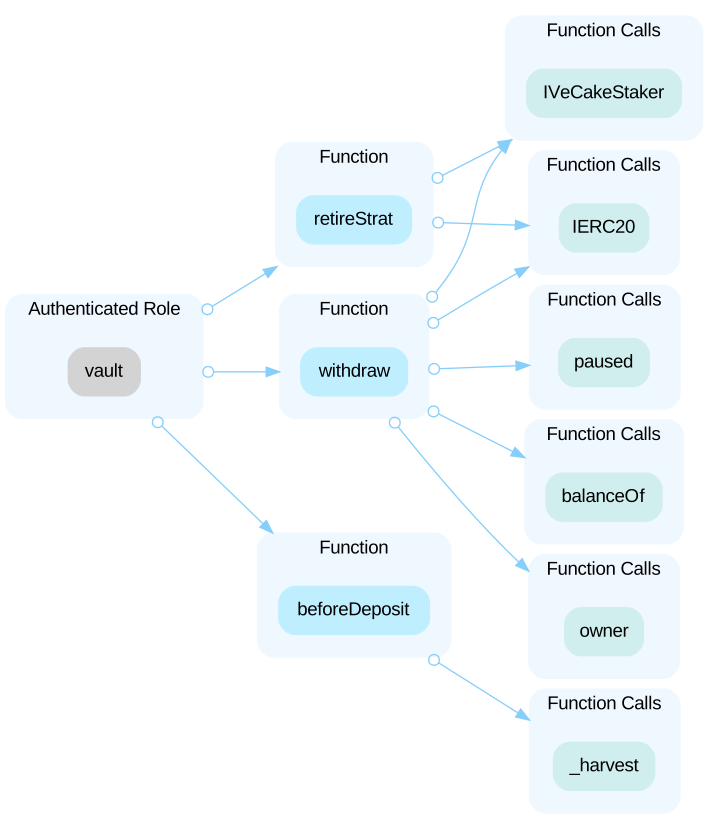
The audit on Trustblock · Open the reportPerforming integer division before multiplication truncates the low bits, losing the precision of calculation. ```solidity=1511 return _nativeBal.mul(45).div(1000).mul(callFee).div(MAX_FEE); ```
The audit on Trustblock · Open the reportContract code is missing natspec comments, which helps understand the code and all the function's parameters. It also increases code readability which is always welcomed. Together with the lack of documentation and unit tests, it makes the whole project difficult to review.
The audit on Trustblock · Open the reportThe `addLiquidity()` function converts half of a tokens to another token. The other half of tokens and part of the converted tokens are deposited into the `lpToken0-lpToken1` pool as liquidity. For every `addLiquidity()` function call, a small amount of tokens could be leftover in the contract. This is because the price of the token drops after swapping the first half of one token into the other, and the other half of token require less than the converted token to be paired with it when adding liquidity.
The audit on Trustblock · Open the reportAddresses should be checked before assignment or external call to make sure they are not zero addresses.
The audit on Trustblock · Open the reportIt is highly recommended NOT to include OpenZeppelin library code directly in source code, but import the original library to minimize risk because even slight changes to the library code may lead to critical/major vulnerabilities/bugs. For Solidity version 0.6.x, the latest OpenZeppelin version 3.4.2 should be used.
The audit on Trustblock · Open the reportA sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (before the transaction being attacked) a transaction to purchase one of the assets and make profits by backrunning (after the transaction being attacked) a transaction to sell the asset. The `swapExactTokensForTokens()` function is called without setting restrictions on slippage or minimum output amount, so transactions triggering this function are vulnerable to sandwich attacks, especially when the input amount is large.
The audit on Trustblock · Open the reportThe change of `owner` by function `transferOwnership()` overrides the previously set `owner` with the new one without guaranteeing the new `owner` has the ability to actuate transactions on-chain. Furthermore, the `setKeeper()` and `setStrategist()` functions of the `StratManager` contract are also not requiring the new `keeper` or `strategist` addresses to accept the change.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=1137 address public unirouter; ``` - The contract `StratManager` interacts with third party contract with `IUniswapRouterETH` interface via `unirouter`. --- ```solidity=1315 address public want; ``` - The contract `StrategyCakeBoostedLP` interacts with third party contract with `IUniswapV2Pair` interface via `want`. --- ```solidity=1320 address public boostStaker; ``` - The contract `StrategyCakeBoostedLP` interacts with third party contract with `IVeCakeStaker` interface via `boostStaker`. --- ```solidity=1323 address public chef; ``` - The contract `StrategyCakeBoostedLP` interacts with third party contract with `ICakeChefV2` interface via `chef`.
The audit on Trustblock · Open the reportLiterals with many digits are difficult to read and review.
The audit on Trustblock · Open the reportThe return value of the ERC20 `transfer()` call is not checked. ```solidity=1536 IERC20(want).transfer(vault, wantBal); ```
The audit on Trustblock · Open the report- Local variable `_nativeBal` could be used before being initialized if `_outputBal` is 0: ```solidity=1504 uint256 _nativeBal; ```
The audit on Trustblock · Open the reportThe contract has unlocked compiler version. An unlocked compiler version in the source code of the contract permits the user to compile it at or above a particular version. This, in turn, leads to differences in the generated bytecode between compilations due to differing compiler version numbers. This can lead to an ambiguity when debugging as compiler specific bugs may occur in the codebase that would be hard to identify over a span of multiple compiler versions rather than a specific one. Additionally, it was found that multiple Solidity versions are used in the codebase.
The audit on Trustblock · Open the report```solidity=1118 interface IWrappedNative is IERC20 { ``` - `IWrappedNative` is declared but never used. --- ```solidity=1303 interface IGasPrice { ``` - `IGasPrice` is declared but never used.
The audit on Trustblock · Open the reportThe return value of an external call is not stored in a local or state variable. ```solidity=1447 IUniswapRouterETH(unirouter).swapExactTokensForTokens(toNative, 0, outputToNativeRoute, address(this), now); ``` --- ```solidity=1468 IUniswapRouterETH(unirouter).swapExactTokensForTokens(outputHalf, 0, outputToLp0Route, address(this), now); ``` --- ```solidity=1472 IUniswapRouterETH(unirouter).swapExactTokensForTokens(outputHalf, 0, outputToLp1Route, address(this), now); ``` --- ```solidity=1477 IUniswapRouterETH(unirouter).addLiquidity(lpToken0, lpToken1, lp0Bal, lp1Bal, 1, 1, address(this), now); ```
The audit on Trustblock · Open the reportContracts that authorize accounts using the `tx.origin` variable are typically vulnerable to phishing attacks which can trick users into performing authenticated actions on the vulnerable contract. Besides the issue with authorization, there is a chance that `tx.origin` will be removed from the Ethereum protocol in the future, so code that uses `tx.origin` won't be compatible with future releases. For more information, see: https://consensys.github.io/smart-contract-best-practices/development-recommendations/solidity-specific/tx-origin/
The audit on Trustblock · Open the reportThe highlighted numbers are not clear enough. Defining them in constants would highly improve readability.
The audit on Trustblock · Open the reportThe linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
The audit on Trustblock · Open the reportThe Leaven Network security record · Every Leaven Network address · This address on the explorer