0x8d1427a32f0a4c4bf052252e68e7ff1b2ba80c01
As of 21 Nov 2026, Trustblock’s record holds 0x8d1427a32f0a4c4bf052252e68e7ff1b2ba80c01 on BNB Chain as a contract of Rimaunangis Digital LLC. 1 audit report on Trustblock lists this address: CertiK, 26 Oct 2022. 5 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Rimaunangis - Audit | CertiK | Not recorded (see the report) | Open |
2 High, 3 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `CoinToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to mint tokens to a predefined account using the `mint()` function. 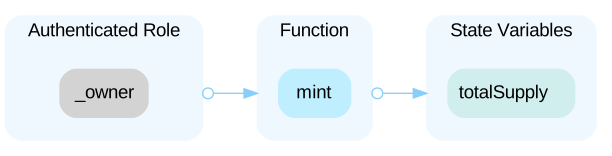 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to transfer ownership of contracts using the `transferOwnership()` function. 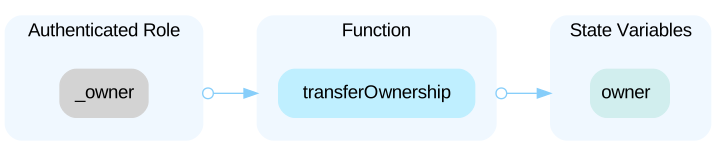 In the contract `Pausable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to pause and unpause contracts using the `pause()` and `unpause()` functions. 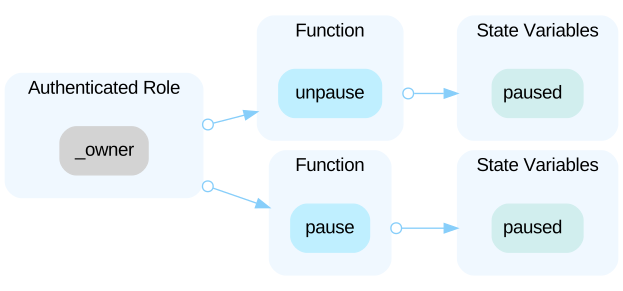 In the contract `PausableToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to add or remove addresses from the blacklist via the `blackListAddress()` function. 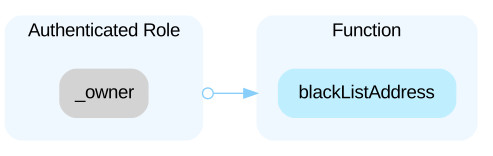
The audit on Trustblock · Open the reportIn the current implementation, the total `totalSupply` is minted to the `tokenOwner`. This introduces a possible centralization risk that all tokens are controlled by a single person. Any compromise to the private keys of the `tokenOwner` could lead to the loss of assets.
The audit on Trustblock · Open the reportCurrently both the `transfer()` and `transferFrom()` functions check that the `msg.sender` is not blacklisted (as shown in the example below). ```solidity require(tokenBlacklist[msg.sender] == false); ``` However, it might also be beneficial to ensure that the `_to` address, or the receiver, of the tokens is also not on the blacklist to prevent tokens from being locked up within the addresses of blacklisted addresses that can no longer send out tokens.
The audit on Trustblock · Open the reportThe **require** statement can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
The audit on Trustblock · Open the reportSolidity frequently releases new compiler versions. Using an old version prevents access to new Solidity security features. Also, recent versions may be too early to be trusted. solc-0.4.24 is not recommended for deployment ```solidity=1 pragma solidity ^0.4.24; ```
The audit on Trustblock · Open the reportThe Rimaunangis Digital LLC security record · Every Rimaunangis Digital LLC address · This address on the explorer