0x979305a29d0458809c4cc698cadaec2610309ae8
As of 21 Nov 2026, Trustblock’s record holds 0x979305a29d0458809c4cc698cadaec2610309ae8 on BNB Chain as a contract of BitBase World. 1 audit report on Trustblock lists this address: CertiK, 7 Dec 2023. 6 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| BitbaseWorld - audit | CertiK | Not recorded (see the report) | On Trustblock |
3 High, 3 Low. In the firm’s own words; statuses are the firm’s, from each report.
The `swapToken()` function calls the `_swapRouter.addLiquidity()` function using `_lpsAddress` as the `to` address specified for acquiring the generated LP tokens from the pool when adding liquidity to it. As a result, over time the `_lpsAddress` address will accumulate significant portion of LP tokens. Since `_lpsAddress` is an EOA address at [0xd2279630D68629de6B4968e4835F4735700497D0](https://bscscan.com/address/0xd2279630D68629de6B4968e4835F4735700497D0), mishandling of its private key can have devastating consequences to the project.
The audit on TrustblockIn the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer or renounce the ownership. 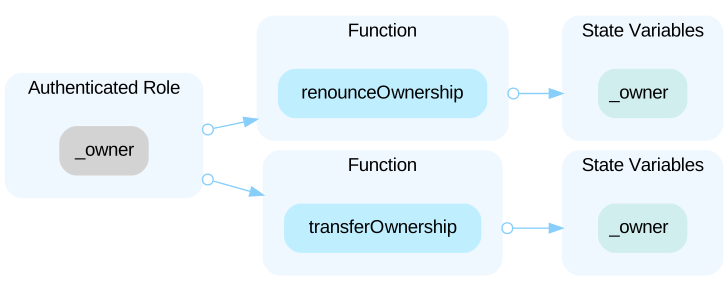 In the contract `BBTCToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and view private variables, set fee rates, fee recipients, swap threshold amount, whitelisted addresses from fees, and pair addresses. It is important to note that the `_owner` is able to withdraw BBTC6 tokens from the contract. 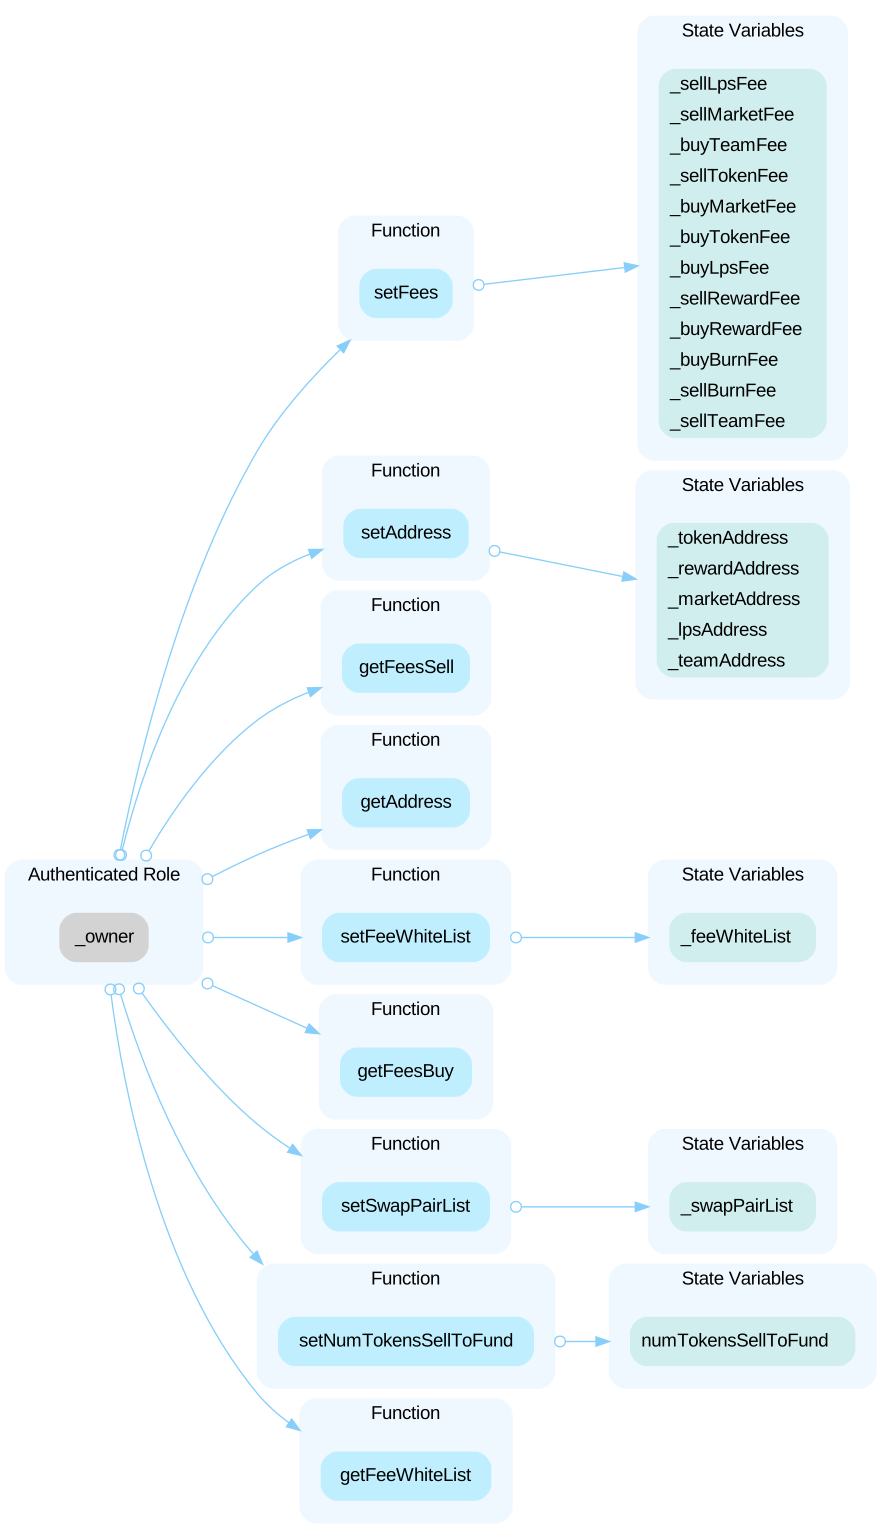
The audit on TrustblockAll of the BBTC tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to the address may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on TrustblockThe `swapAccmul()` function in the `PandaToken` contract can add liquidity to the pair address under specific conditions and is intended to be executed during both buy and sell operations of BBTC6 tokens. However, a reentrancy issue arises when buying BBTC6 tokens from the pair. The external calls made to the `_swapRouter` within the `swapToken()` function trigger a reentrancy back to functions protected by the `lock` modifier in the pair address. This reentrancy results in the external calls reverting. While the `PandaToken` contract employs `try...catch...` blocks to manage such reverts, enabling the primary buy operation to proceed, this reentrancy behavior presents a noteworthy issue in the contract logic.
The audit on TrustblockSome restrictions can be bypassed by swapping tokens to the router and then getting tokens from the router. When the tokens are transferred to the router, the attacker uses the feature of the router function **`removeLiquidityETHSupportingFeeOnTransferTokens()`**, which will send all the specified tokens in the router to a specified address.
The audit on TrustblockThe contract is serving as the underlying entity to interact the [`PancakeRouter`](https://bscscan.com/address/0x10ED43C718714eb63d5aA57B78B54704E256024E) and [BSC-USD token](https://bscscan.com/address/0x55d398326f99059fF775485246999027B3197955). The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts.
The audit on TrustblockThe BitBase World security record · Every BitBase World address · This address on the explorer