0x9cec03362d759ceca736e5918e8ba7636e2bd64e
As of 21 Nov 2026, Trustblock’s record holds 0x9cec03362d759ceca736e5918e8ba7636e2bd64e on BNB Chain as a contract of Decimal. 1 audit report on Trustblock lists this address: CertiK, 24 May 2023. 3 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Decimalchain - audit | CertiK | Not recorded (see the report) | Open |
2 High, 1 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `AccessControl` the role `ADMIN_ROLE` has authority over the functions: - revokeRole() - grantRole() Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority. In the contract `DERC20` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 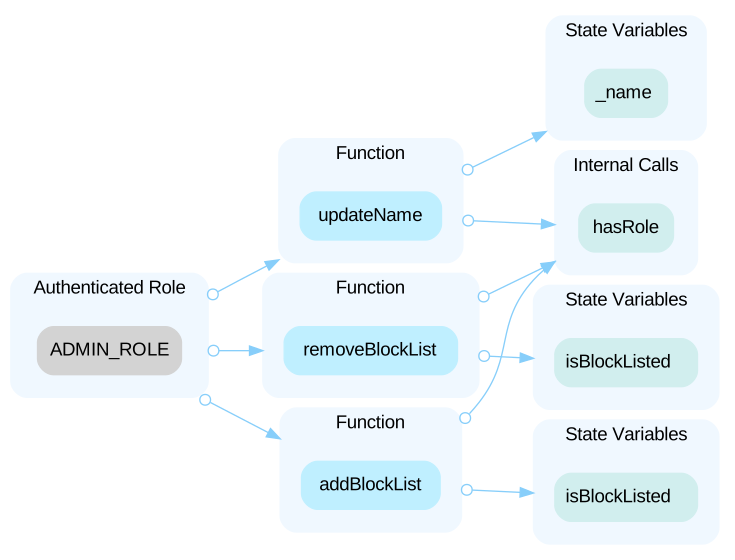 In the contract `DERC20` the role `BURNER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BURNER_ROLE` account may allow the hacker to take advantage of this authority. 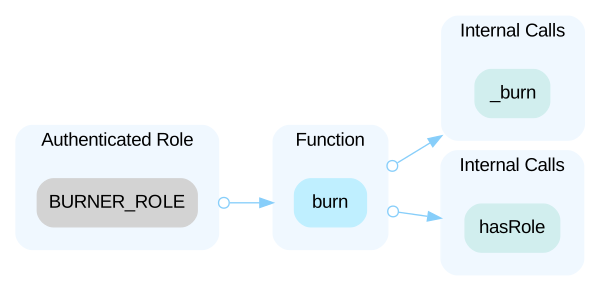 In the contract `DERC20` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority. 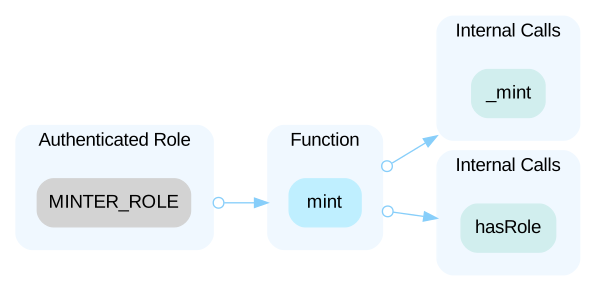 In the contract `DERC20` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority. 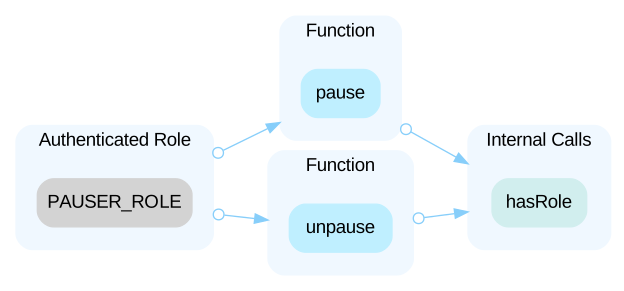
The audit on Trustblock · Open the reportIn the contract DERC20, the role `MINTER_ROLE` has the authority to update the token balance of an arbitrary account without sanity restriction. Any compromise to the `MINTER_ROLE` account may allow a hacker to take advantage of this authority and manipulate users' balances. The hacker could also update his/her balance to a large number, sell these tokens, and cause the token price to drop.
The audit on Trustblock · Open the reportThe codebase contains multiple Solidity versions, which can lead to unexpected behavior, potential vulnerabilities, difficulties in maintaining the code, and inconsistencies in the execution of the smart contract. Using different versions may also result in increased complexity during code auditing, as different security features and bug fixes are present in different versions of the compiler. Versions used: `^0.8.0` `^0.8.0` is used in DERC20.sol file. ```solidity=702 pragma solidity ^0.8.0; ```
The audit on Trustblock · Open the reportThe Decimal security record · Every Decimal address · This address on the explorer