0xa03110800894b3ccf8723d991d80875561f96777
As of 21 Nov 2026, Trustblock’s record holds 0xa03110800894b3ccf8723d991d80875561f96777 on BNB Chain as a contract of Bit Game Verse Token. 2 audit reports on Trustblock list this address, from CertiK and Cyberscope; the newest is CertiK, 16 Nov 2022. 19 findings in them are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Anil Yadav - Audit | CertiK | Not recorded (see the report) | Open | |
| BIT GAME VERSE TOKEN | Cyberscope | Not recorded (see the report) | Open |
2 Critical, 4 Medium, 13 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `BitGameVerse` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, set the Tax & Wallet Limit, withdraw BNB or Other BEP20 tokens, change wallet router & pair address, blacklist, change reward & fee list, and change cooldown time & transfer allowance list. 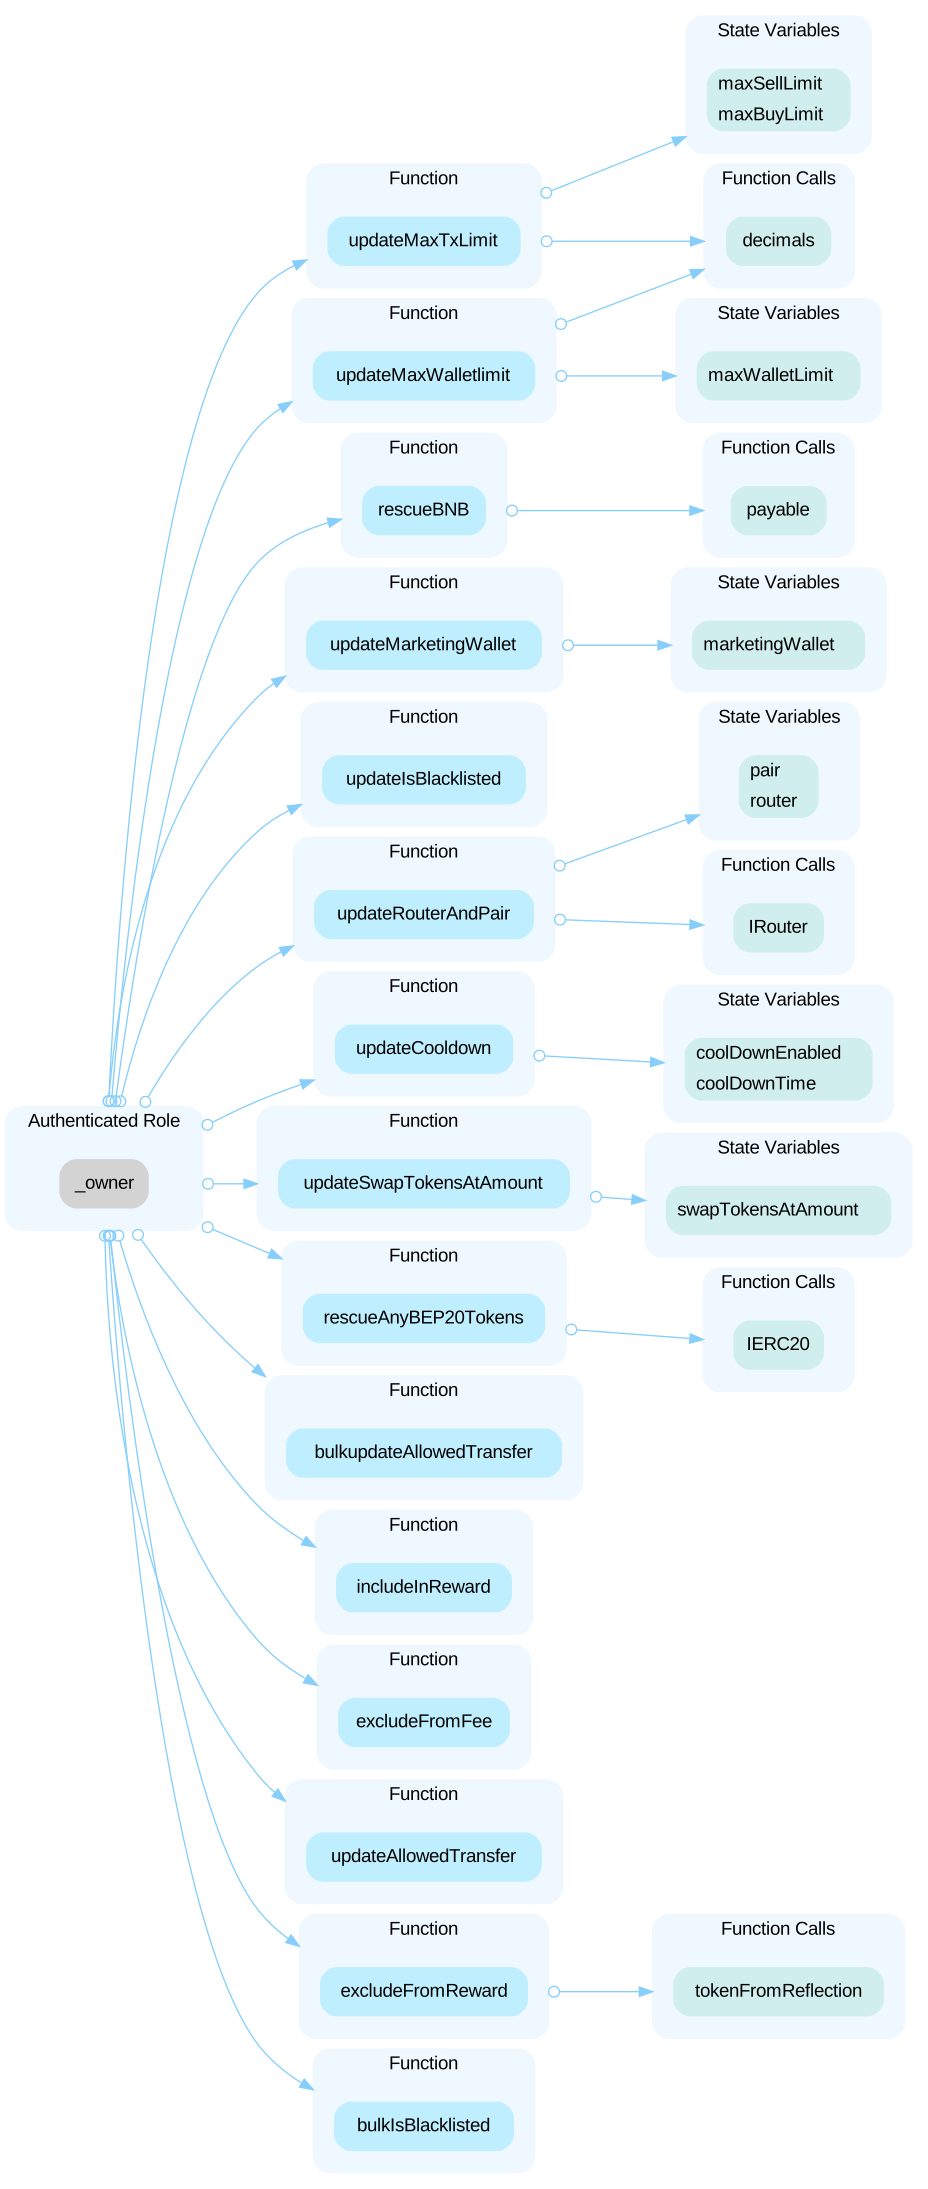 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the ownership. 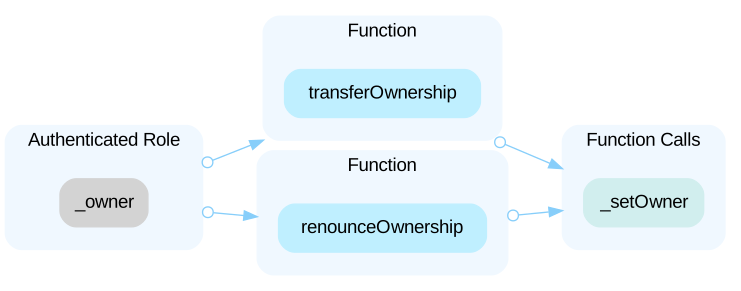
The audit on Trustblock · Open the reportVariable `_rOwned` is not updated in function `includeInReward()`, which means previously excluded accounts can be included again and continue to receive holder rewards. Details of this finding can be seen in this article from Pera Finance: [Link]https://perafinance.medium.com/safemoon-is-it-safe-though-a-detailed-explanation-of-frictionless-yield-bug-338710649846
The audit on Trustblock · Open the reportA sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (before the transaction being attacked) a transaction to purchase one of the assets and make profits by backrunning (after the transaction being attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `addLiquidity()` - `swapExactTokensForETHSupportingFeeOnTransferTokens()`
The audit on Trustblock · Open the reportThe `transferFrom` function transfers tokens before updating the storage variables. This does not follow the Checks-Effects-Interactions pattern.
The audit on Trustblock · Open the reportThe event `FeesChanged`, `UpdatedRouter` is present but never emitted.
The audit on Trustblock · Open the reportAddresses should be checked before assignment or external call to make sure they are not zero addresses. ```solidity=218 pair = _pair; ``` - `_pair` is not zero-checked before being used. --- ```solidity=659 marketingWallet = newWallet; ``` - `newWallet` is not zero-checked before being used. --- ```solidity=703 pair = newPair; ``` - `newPair` is not zero-checked before being used.
The audit on Trustblock · Open the reportTo the best of understanding, the reward of a specific account should stop accumulating while in the range of being excluded from reward after calling `excludeFromReward()`. In L531, the current `_tOwned` balance of the `account` is recorded and any reward starting from this point should not be accumulated after calling the function `excludeFromReward()`. However, when calling the function `includeInReward()` to include the excluded `account` for reward, `_rOwned` should be calculated with current `_tOwned` value.
The audit on Trustblock · Open the reportThe `approve` function could be used in a Front-Running attack that allows a spender to transfer more tokens than the owner of the tokens ever wanted to allow the spender to transfer. Here is a possible attack scenario: Alice allows Bob to transfer N of Alice's tokens (N>0) by calling approve method on Token smart contract passing Bob's address and N as method arguments After some time, Alice decides to change from N to M (M>0) the number of Alice's tokens Bob is allowed to transfer, so she calls approve method again, this time passing Bob's address and M as method arguments Bob notices Alice's second transaction before it was mined and quickly sends another transaction that calls ·transferFrom· method to transfer N Alice's tokens somewhere If Bob's transaction will be executed before Alice's transaction, then Bob will successfully transfer N Alice's tokens and will gain the ability to transfer another M tokens Before Alice noticed that something went wrong, Bob calls ·transferFrom· method again, this time to transfer M Alice's tokens. So, Alice's attempt to change Bob's allowance from N to M (N>0 and M>0) made it possible for Bob to transfer N+M of Alice's tokens, while Alice never wanted to allow so many of her tokens to be transferred by Bob. ERC20 API: An Attack Vector on [Approve/TransferFrom Methods](https://docs.google.com/document/d/1YLPtQxZu1UAvO9cZ1O2RPXBbT0mooh4DYKjA_jp-RLM/edit#heading=h.m9fhqynw2xvt)
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=146 IRouter public router; ``` - The contract `BitGameVerse` interacts with third-party contract with uniswap `IRouter` interface via `router`.
The audit on Trustblock · Open the reportThe return value of the transfer()/transferFrom() call is not checked. ```solidity=717 IERC20(_tokenAddr).transfer(_to, _amount); ```
The audit on Trustblock · Open the reportThe follwoing variables are used without being initialized in the constructor, impacts the `_tokenTransfer` function. ```solidity=161 uint256 private deadline; ``` - `deadline` is never initialized, but used in `BitGameVerse._tokenTransfer`. --- ```solidity=177 Taxes private launchtax; ``` - `launchtax` is never initialized, but used in `BitGameVerse._getTValues`.
The audit on Trustblock · Open the reportThe return value of an external call is not stored in a local or state variable. ```solidity=631 router.addLiquidityETH{ value: bnbAmount }( address(this), tokenAmount, 0, // slippage is unavoidable 0, // slippage is unavoidable owner(), block.timestamp ); ```
The audit on Trustblock · Open the reportIt is not recommended to use Solidity's `transfer()` and `send()` functions for transferring Ether/BNB, since some contracts may not be able to receive the funds. Those functions forward only a fixed amount of gas (2300 specifically) and the receiving contracts may run out of gas before finishing the transfer. Also, EVM instructions' gas costs may increase in the future. Thus, some contracts that can receive now may stop working in the future due to the gas limitation. ```solidity=709 payable(msg.sender).transfer(weiAmount); ``` - `BitGameVerse.rescueBNB` uses `transfer()`.
The audit on Trustblock · Open the reportThe Bit Game Verse Token security record · Every Bit Game Verse Token address · This address on the explorer