0xb7dacf54a54bfea818f21472d3e71a89287841a7
As of 21 Nov 2026, Trustblock’s record holds 0xb7dacf54a54bfea818f21472d3e71a89287841a7 on BNB Chain as a contract of WealthSecrets. 1 audit report on Trustblock lists this address: CertiK, 17 Feb 2023. 18 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| WealthSecrets | CertiK | Not recorded (see the report) | Open |
1 High, 3 Medium, 14 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 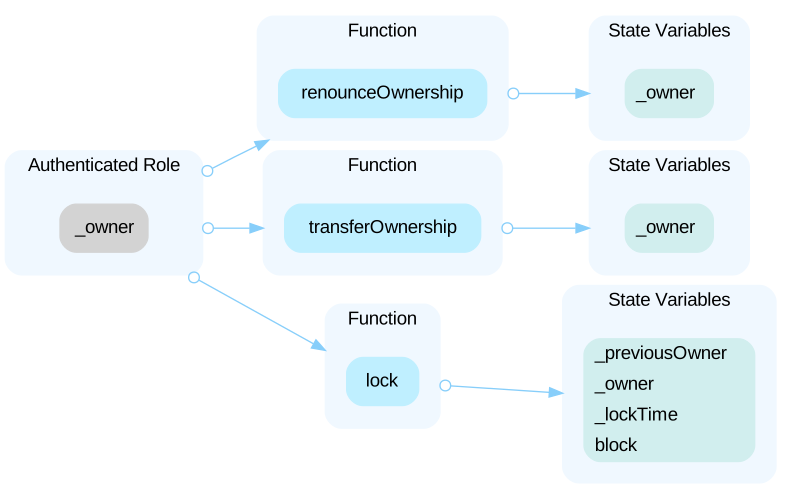 In the contract `Ownable` the role `_previousOwner` has authority over the functions shown in the diagram below. Any compromise to the `_previousOwner` account may allow the hacker to take advantage of this authority. 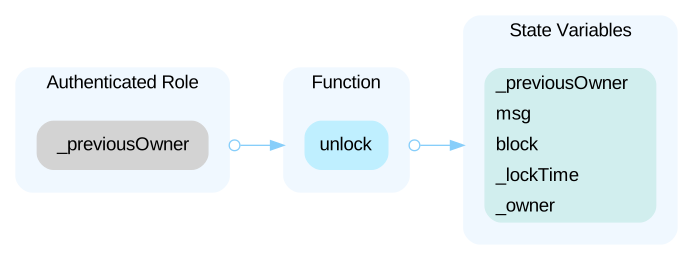 In the contract `Token` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 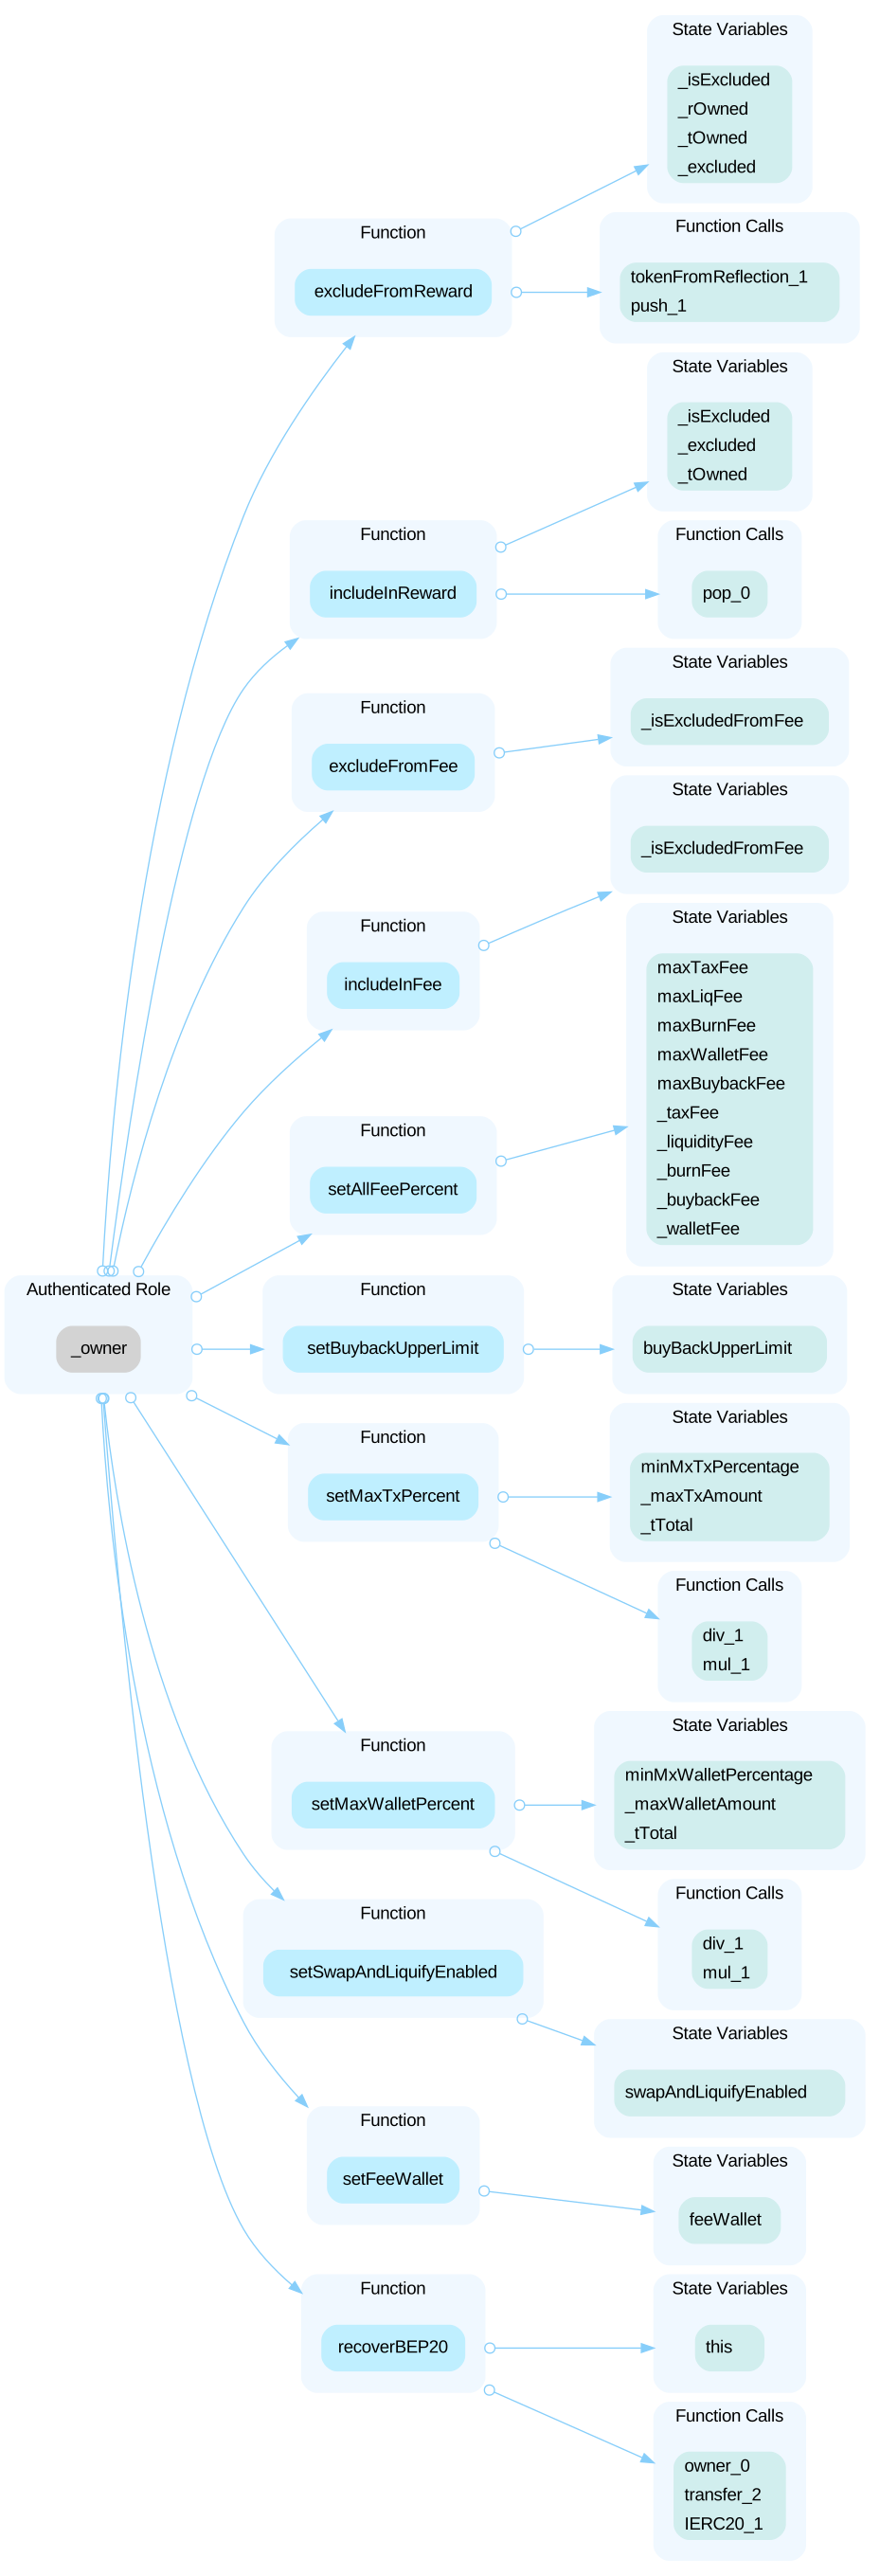
The audit on Trustblock · Open the reportThe variable `_maxTxAmount` and `_maxWalletAmount` could be set arbitrarily when deploying the contract `Token`, also, the variable `buyBackLimit` does not have reasonable boundaries when setting it. More seriously, setting `buyBackLimit` to a very small value may lead to the failure of buying back tokens.
The audit on Trustblock · Open the reportAccording to the following codes: ```solidity uint256 balance = address(this).balance; if (buyBackEnabled && balance > uint256(1 * 10**18)) { if (balance > buyBackUpperLimit) balance = buyBackUpperLimit; buyBackTokens(balance.div(100)); } ``` Nothing will be used to buy back tokens if `balance` is smaller than 1 BNB. If `balance` is greater than `buyBackUpperLimit`, 1% of `buyBackUpperLimit` amount will be used to buy back tokens each time this function is called. Since the BuyBackToken contract will continuously accumulate liquidity fees, only a small portion of the liquidity fees will be used to buy back tokens. Additionally, the `buyBackUpperLimit` can be modified by the admin and has no limitations. So they can be set to a relatively small number. Hence the percentage of buying back may be very small. More seriously, the percentage of `buybackFee` could be zero, so almost all converted BNBs in the current contract could be kept in the contract, however, the contract doesn't appear to provide a way to withdraw those BNBs.
The audit on Trustblock · Open the reportAccording to the following code: ```solidity function _transfer( address from, address to, uint256 amount ) private { ... uint256 balance = address(this).balance; if (balance > uint256(1 * 10**18)) { if (balance > buyBackUpperLimit) balance = buyBackUpperLimit; buyBackTokens(balance.div(100)); } ... } ``` ,in the function `_transfer()`, the 1%`buyBackUpperLimit` amount of BNBs were bought back when requirements are met, while some BNBs are still left in the contract, however, the contract doesn't appear to provide a way to withdraw those BNBs, and they will be locked in the contract forever.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with third party PancakeSwap protocols. The scope of the audit would treat those 3rd party entities as black boxes and assume its functional correctness. However in the real world, 3rd parties may be compromised that led to assets lost or stolen.
The audit on Trustblock · Open the reportPerforming integer division before multiplication truncates the low bits, losing the precision of calculation.
The audit on Trustblock · Open the report`public` functions that are never called by the contract could be declared as `external`. `external` functions are more efficient than `public` functions.
The audit on Trustblock · Open the reportThe error message in `require(_isExcluded[account], "Already excluded")` does not describe the error correctly.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportAn owner is possible to gain ownership of the contract even if he calls function `renounceOwnership` to renounce the ownership. This can be achieved by performing the following operations: 1. Call `lock` to lock the contract. The variable `_previousOwner` is set to the current owner. 2. Call `unlock` to unlock the contract. 3. Call `renounceOwnership` to leave the contract without an owner. 4. Call `unlock` to regain ownership.
The audit on Trustblock · Open the reportA reentrancy attack can occur when the contract creates a function that makes an external call to another untrusted contract before resolving any effects. If the attacker can control the untrusted contract, they can make a recursive call back to the original function, repeating interactions that would have otherwise not run after the external call resolved the effects. Function `_transfer()` is risky to reentrancy attack. The function call of `swapAndLiquify()` would eventually send `ethAmount` via `pcsV2Router.addLiquidityETH()`, and state variable `_rOwned` is massively changed later in the function call of `_tokenTransfer()`. Since the real implementation of the external function is unclear, and the address behind the interface is not clear, reentrancy is possible to take place.
The audit on Trustblock · Open the reportA sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (before the transaction being attacked) a transaction to purchase one of the assets and make profits by back running (after the transaction being attacked) a transaction to sell the asset. Potential sandwich attacks could happen if calling `pcsV2Router.swapExactTokensForETHSupportingFeeOnTransferTokens` and `pcsV2Router.addLiquidityETH` without setting restrictions on slippage. For example, when we want to make a transaction of swapping 100 AToken for 1 ETH, an attacker could raise the price of ETH by adding AToken into the pool before the transaction so we might only get 0.1 ETH. After the transaction, the attacker would be able to withdraw more than he deposited because the total value of the pool increases by 0.9 ETH.
The audit on Trustblock · Open the reportThe condition `!_isExcluded[sender] && !_isExcluded[recipient]` can be included in `else`, besides, `mintedByMudra` is defined but not used.
The audit on Trustblock · Open the reportSolidity version >=0.8.0 includes checked arithmetic operations and underflow/overflow by default, making SafeMath redundant.
The audit on Trustblock · Open the reportThe return values of function `addLiquidityETH` are not properly handled. ```solidity= pcsV2Router.addLiquidityETH{value: ethAmount}( address(this), tokenAmount, 0, // slippage is unavoidable 0, // slippage is unavoidable dead, block.timestamp ); ```
The audit on Trustblock · Open the reportThe function `deliver` can be called by anyone. It accepts an uint256 number parameter `tAmount`. The function reduces the SafeMoon token balance of the caller by `rAmount`, which is `tAmount` reduces the transaction fee. Then, the function adds `tAmount` to variable `_tFeeTotal`, which represents the contract's total transaction fee. We wish the team could explain more on the purpose of having such functionality.
The audit on Trustblock · Open the reportThere are several typos in the code and comments. 1. In the following code snippet, `tokensIntoLiqudity` should be `tokensIntoLiquidity`. ```solidity= event SwapAndLiquify( uint256 tokensSwapped, uint256 ethReceived, uint256 tokensIntoLiqudity ); ``` 2. `recieve` should be `receive` and `swaping` should be `swapping` in the line of comment `//to recieve ETH from pcsV2Router when swaping` 3. Function name is mistakenly set as `geUnlockTime()`, which should be `getUnlockTime()`.
The audit on Trustblock · Open the reportThe linked variables could be declared as `constant` since these state variables are never modified.
The audit on Trustblock · Open the reportThe WealthSecrets security record · Every WealthSecrets address · This address on the explorer