0xbc6488c75b47daff2cddd64003a203540b3112e4
As of 21 Nov 2026, Trustblock’s record holds 0xbc6488c75b47daff2cddd64003a203540b3112e4 on BNB Chain as a contract of DEBT Box. 1 audit report on Trustblock lists this address: CertiK, 6 Mar 2023. 13 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| The Debt Box (BGLD, NATG, ALUM, XPLR) | CertiK | Not recorded (see the report) | Open |
2 High, 2 Medium, 9 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Explore` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the configuration of the contract and mint tokens to himself. 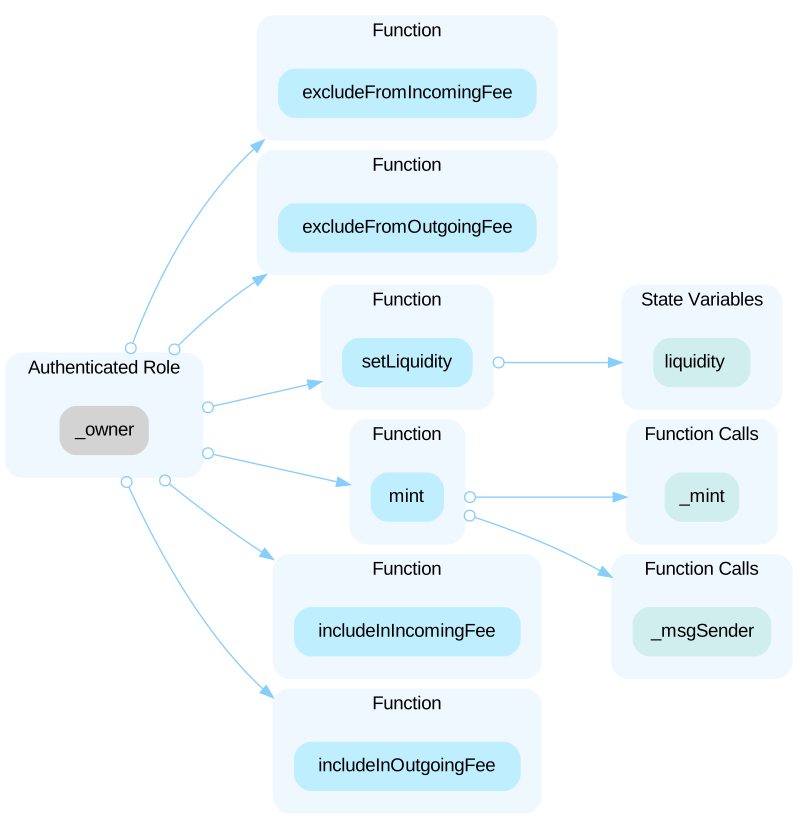 In the contract `Aluminum` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the configuration of the contract and mint tokens to himself. 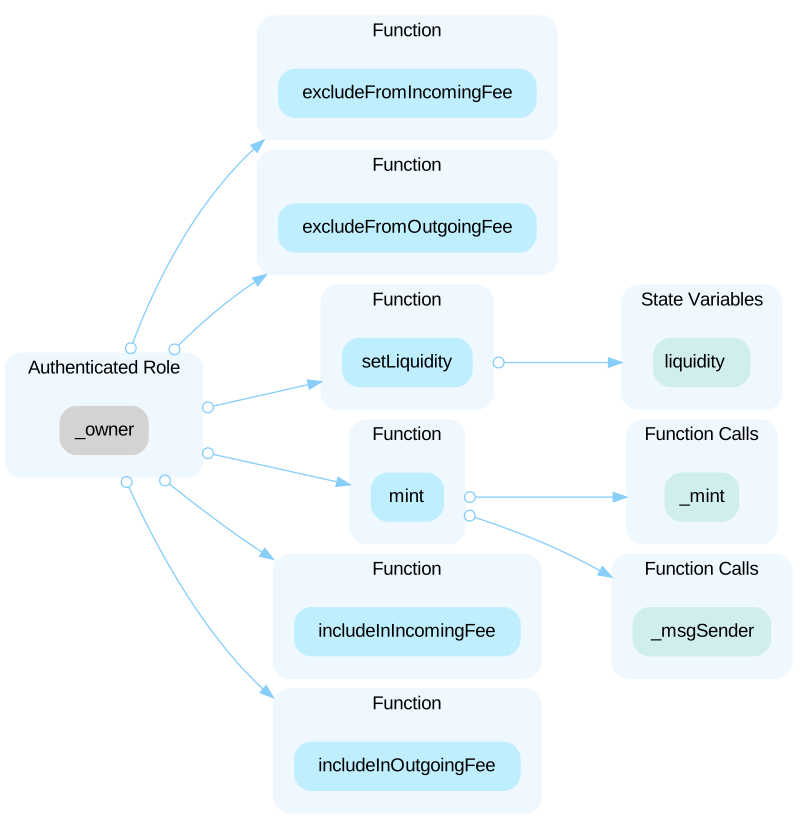 In the contract `BlackGold` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the configuration of the contract and mint tokens to himself. 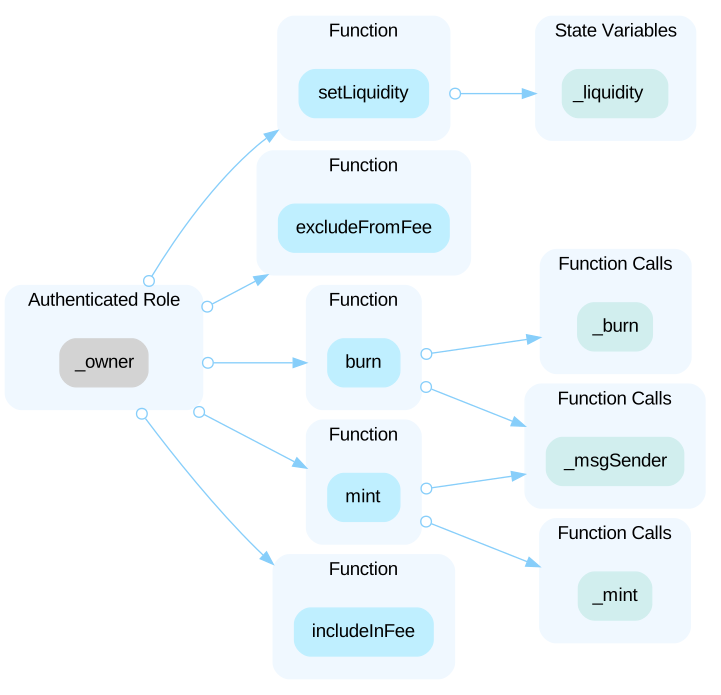 In the contract `NaturalGas` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the configuration of the contract and mint tokens to himself. 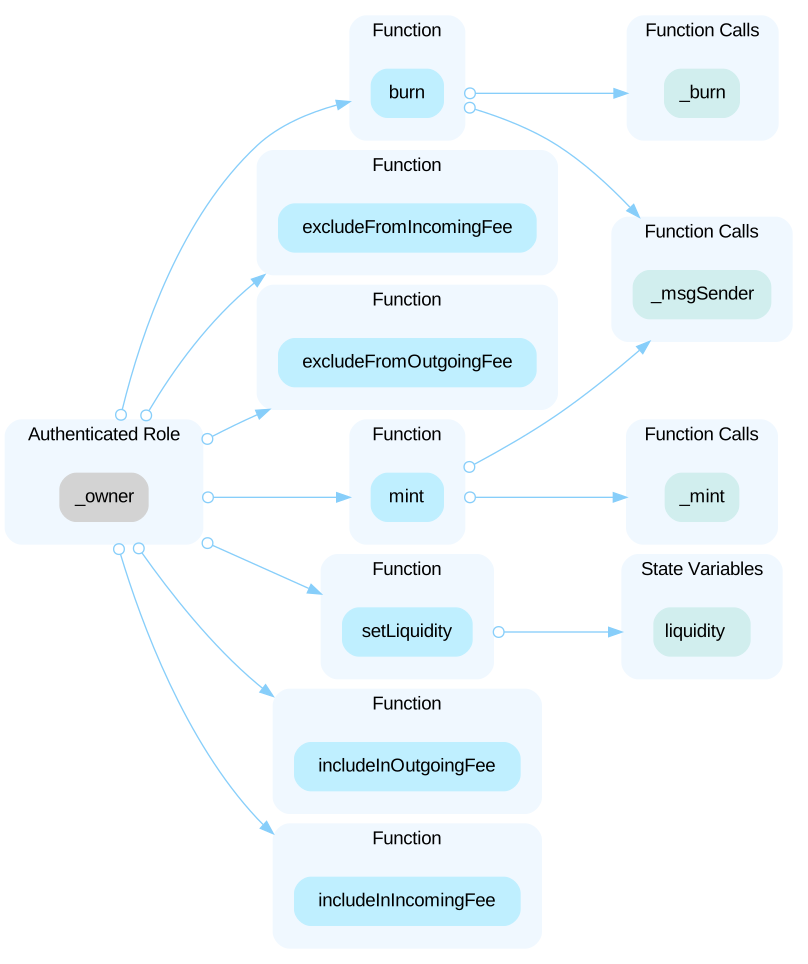
The audit on Trustblock · Open the reportThe contract owner can set the liquidity address to any address. The target address can be an EOA address or a smart contract. The implementation of the liquidity address is unknown, and whether the collected tokens will be used to provide liquidity is unknown.
The audit on Trustblock · Open the reportThe audited token contracts burn additional tokens from the sender's address during a token transfer. This behavior can potentially be exploited if the token's liquidity exists in Uniswap V2 (and its forks), and the liquidity pair address is not excluded from such a fee. The unique 'Skim()' and 'Sync()' functions in the Uniswap V2 pair contract enable such an attack. Please see the 'Scenario' section to understand how this issue can be exploited.
The audit on Trustblock · Open the reportThe contract uses the `pragma solidity 0.5.17` directive. This indicates that an outdated version of the compiler is used, which is prone to several disclosed bugs.
The audit on Trustblock · Open the report10% of the transfer fee will deduct from the sender's wallet, on top of the transfer amount. If user A approves user B 200 tokens and user B uses the "TransferFrom" function to transfer 100 A's tokens, A's balance will deduct by 110, and the "allowance" will only deduct by 100. The allowance reduction in the "TransferFrom" function doesn't put the "Fee" into consideration.
The audit on Trustblock · Open the reportMathematical operations in the aforementioned function perform divisions before multiplications. Performing multiplication before division can sometimes avoid loss of precision.
The audit on Trustblock · Open the reportLine 646 only checks if the sender is excluded from the fee: ```sol=646 " if (!_isExcludedFromFee[sender]) {" ``` But line 661 checks if both the sender and recipient are excluded from the fee: ```sol=661 if (!_isExcludedFromFee[sender] && !_isExcludedFromFee[recipient]) { ``` The fee check logic is inconsistent across two "if" statements.
The audit on Trustblock · Open the reportThe linked code is to transfer the "liquidityFee" to the "liquidity" address, but the value used in the `Transfer` event is "miningFee" instead of the "liquidityFee". ```sol=537 _balances[sender] = _balances[sender] - liquidityFee; _balances[liquidity] = _balances[liquidity] + liquidityFee; emit Transfer(sender, liquidity, miningFee); ```
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportMultiple OpenZeppelin libraries are included in the source code file. It is highly recommended NOT to include OpenZeppelin library code directly in the source code because even slight changes to the library code may lead to major vulnerabilities/bugs.
The audit on Trustblock · Open the reportThe DEBT Box security record · Every DEBT Box address · This address on the explorer