0xc19c1bdc6e4f2d3350a63b4846399010a1ded751
As of 21 Nov 2026, Trustblock’s record holds 0xc19c1bdc6e4f2d3350a63b4846399010a1ded751 on BNB Chain as a contract of Singularity Hubs. 1 audit report on Trustblock lists this address: CertiK, 1 Aug 2022. 16 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Singularity | CertiK | Not recorded (see the report) | Open |
5 High, 2 Medium, 9 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `EneToken` the role `_owner` has authority over the functions shown in the diagram below.\ Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do any of the following: - steal all the tokens from every future transfer by setting the `burnAddress` to an address he/she controls and setting the `burnRate` to 100 - have complete control over all future tokens minted by setting themselves as the only `minter` and minting an unlimited amount of tokens to an address he/she controls 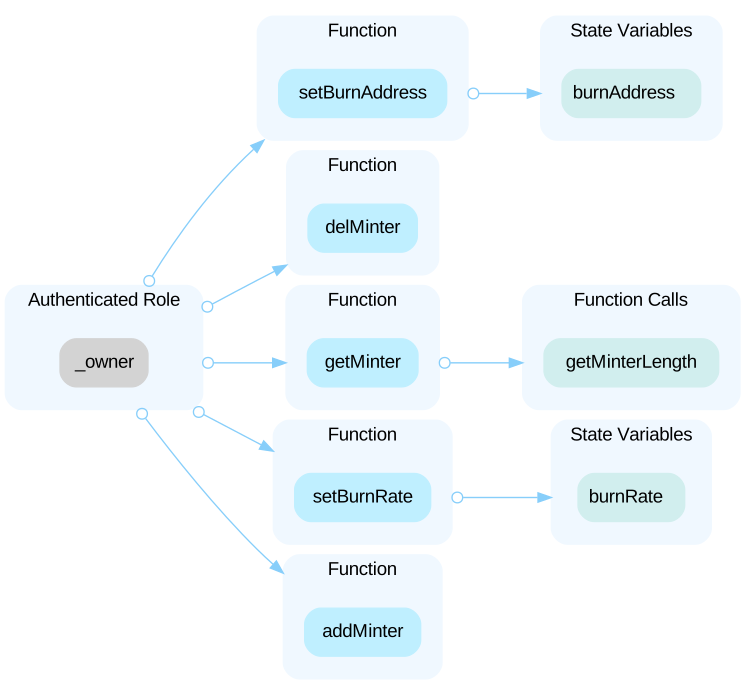 ---- In the contract `EneToken` the role `minter` has authority over the function `mint()`. Any compromise to a `minter` account may allow the hacker to take advantage of this authority and mint an unlimited amount of tokens to an address he/she controls until their privilege is revoked by the `_owner`.
The audit on Trustblock · Open the reportIn the contract `Pledge` the role `_owner` has authority over the functions shown in the diagram below.\ Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do any of the following: - set the `sgtAddress`, `eneAddress`, and `lpAddress` to incompatible addresses, which can disrupt contract functionality - arbitrarily set `plan`s, which can disrupt contract functionality or allow the hacker to create any `plan` they could possibly benefit from 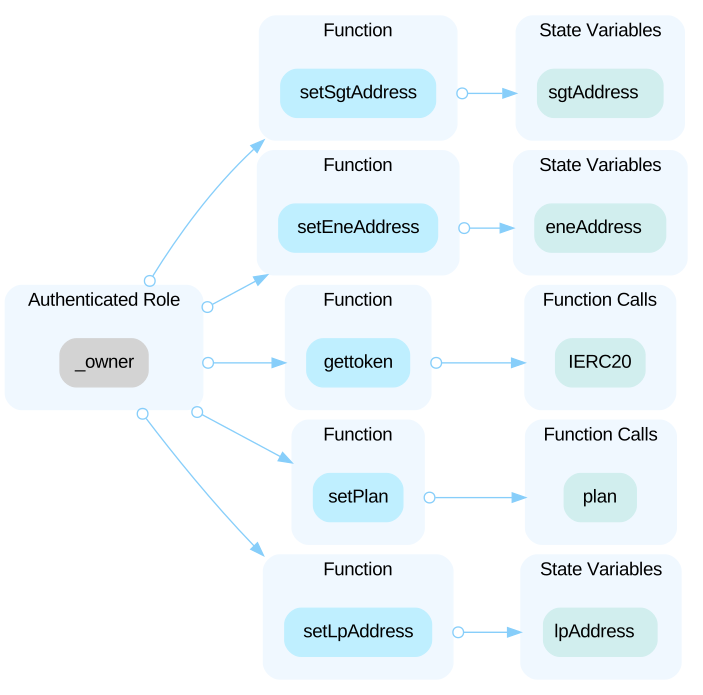
The audit on Trustblock · Open the reportIn the contract `SGT` the role `_owner` has authority over the functions shown in the diagram below.\ Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do any of the following: - drain the funds from the `withdrawFrom` address by setting their own `withdrawInfo` arbitrarily and performing `withdraw`s - prevent any user from performing `withdraw`s by calling `cancelWithdraw()` with the user's address - burn any amount of tokens from any account 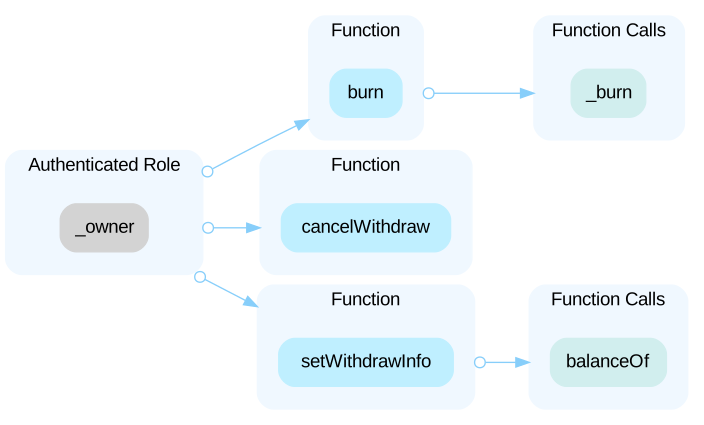
The audit on Trustblock · Open the reportAll of the `SGT` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute `SGT` tokens without obtaining the consensus of the community.
The audit on Trustblock · Open the reportAll of the tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute tokens without obtaining the consensus of the community.
The audit on Trustblock · Open the reportThe owner can set the `_burnRate` in function `setBurnRate` and there is no upper limit on what the rate can be. In the extreme case, the rate can be as high as 100%, which would imply that users cannot get any token back in transferring operation.
The audit on Trustblock · Open the reportThe return value of an external call is not stored in a local or state variable.
The audit on Trustblock · Open the reportPre-set staking plans are created upon contract deployment. The function `setPlan` allows the contract owner to create new staking plans. \ However, there is no check to ensure previous plans are not overridden, which could disrupt contract functionality.
The audit on Trustblock · Open the reportBoolean constants can be used directly and do not need to be compared to true or false.
The audit on Trustblock · Open the reportThe functions which are never called internally within the contract should have external visibility for gas optimization.
The audit on Trustblock · Open the reportThe contracts `SGT`, `Pledge`, and `EneToken` lack comments explaining the methodology and the reasoning behind the calculation and implementation. Detailed documentation could benefit future code reviewers and improve the project's transparency.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportAddresses should be checked before assignment or external call to make sure they are not zero addresses.
The audit on Trustblock · Open the reportThe logic behind the `setWithdrawInfo()` function is unclear and seems to be very centralized. It appears that the owner of the `SGT.sol` contract, which is an externally owned account, must use `setWithdrawInfo()` to create `pendingBalances` for every user that wants to interact with the contract. However, users cannot interact with the `SGT.sol` contract directly, and must first choose a staking plan within the `Pledge.sol` contract to receive SGT tokens as a reward. It seems that receiving this reward would not work, since the owner of `SGT.sol` has authority over many of the functions; or receiving the reward would depend on whether the owner has created a `pendingBalances` for a specific address.
The audit on Trustblock · Open the reportThe linked functions are equivalent to the compiler-generated getter functions for the respective variables.
The audit on Trustblock · Open the reportThe linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
The audit on Trustblock · Open the reportThe Singularity Hubs security record · Every Singularity Hubs address · This address on the explorer