0xc9dbcff0448d330aaf1dd78fc204370e5e54a797
As of 21 Nov 2026, Trustblock’s record holds 0xc9dbcff0448d330aaf1dd78fc204370e5e54a797 on BNB Chain as a contract of PoodleFi. 1 audit report on Trustblock lists this address: CertiK, 3 Sep 2022. 13 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| PoodleFi - Audit | CertiK | Not recorded (see the report) | Open |
3 High, 1 Medium, 9 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `PoodleFi` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set fee address to hacker affiliated address and alter other critical parameters of the project. 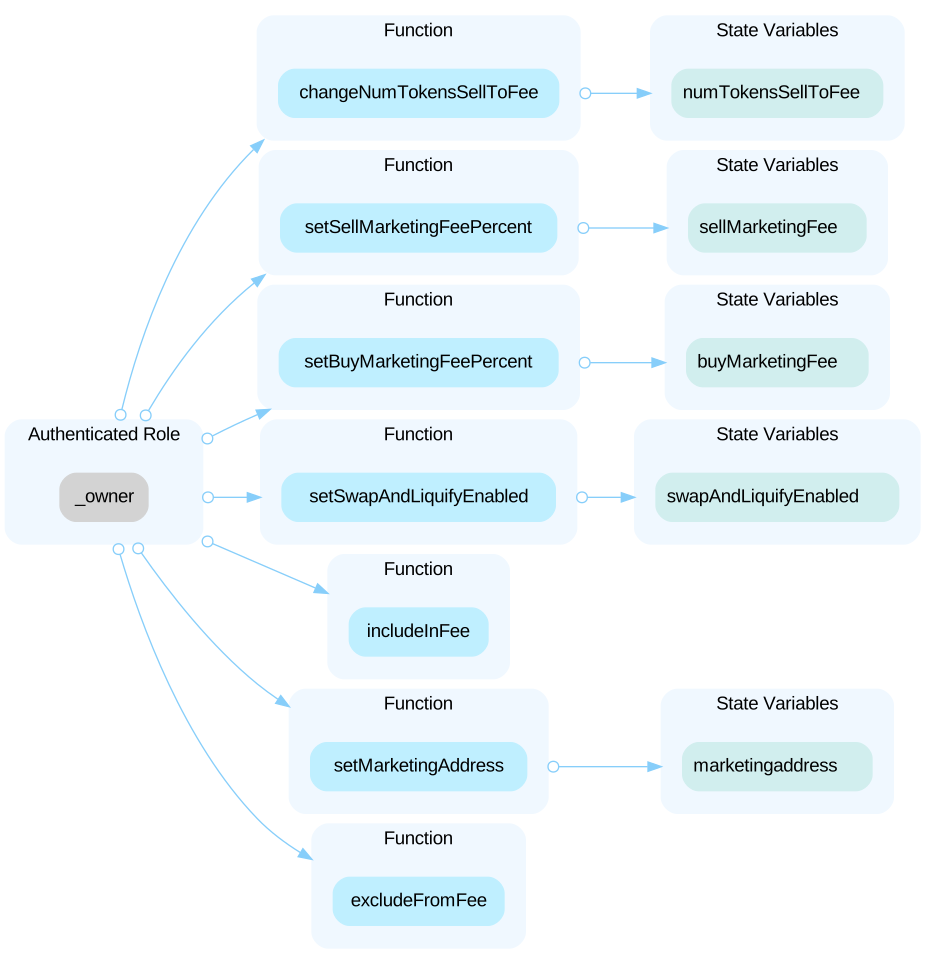
The audit on Trustblock · Open the reportThe code comment in line 540 indicates that the `swapAndLiquify()` function is used to "add liquidity". However, the implementation of the `swapAndLiquify()` function swaps the token to BNB and send it to the privileged `marketingaddress`.
The audit on Trustblock · Open the reportAll of the PFI tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute PFI tokens without obtaining the consensus of the community.
The audit on Trustblock · Open the reportA state variable is shadowing another component defined in a parent contract. Variable `_owner` in `PoodleFi` shadows the variable `_owner` in `Ownable`. ```solidity=423 address private _owner; ``` ```solidity=67 address private _owner; ```
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportA sandwich attack might happen when an attacker observes a transaction swapping tokens without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by front-running (before the transaction is attacked) a transaction to purchase one of the assets and make profits by back-running (after the transaction is attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `uniswapV2Router.swapExactTokensForETHSupportingFeeOnTransferTokens()`
The audit on Trustblock · Open the reportThe owner is exempt from fees and transaction limits by default. Yet when ownership is reset through `renounceOwnership()` or `transferOwnership()`, the exemptions are not granted to the new owner nor are they revoked from the previous owner.
The audit on Trustblock · Open the reportThe change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with third party PancakeSwap protocol. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=389 IUniswapV2Router02 public immutable uniswapV2Router; ``` - The contract `PoodleFi` interacts with third party contract with `IUniswapV2Router02` interface via `uniswapV2Router`.
The audit on Trustblock · Open the reportThe `SafeMath` library is used unnecessarily. With Solidity compiler versions 0.8.0 or newer, arithmetic operations will automatically revert in case of integer overflow or underflow. ```solidity=19 library SafeMath { ``` - An implementation of `SafeMath` library is found. --- ```solidity=151 using SafeMath for uint; ``` - `SafeMath` library is used for `uint256` type in `SafeBEP20` contract. --- ```solidity=387 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `PoodleFi` contract. ```solidity=466 _approve(sender, _msgSender(), _allowances[sender][_msgSender()].sub(amount, "BEP20: transfer amount exceeds allowance")); ``` - `SafeMath.sub` is called in `transferFrom` function of `PoodleFi` contract. *Note: Only a sample of `SafeMath` library usage in this contract (out of 12) are shown above.*
The audit on Trustblock · Open the reportIt is not recommended to use Solidity's `transfer()` and `send()` functions for transferring Ether, since some contracts may not be able to receive the funds. Those functions forward only a fixed amount of gas (2300 specifically) and the receiving contracts may run out of gas before finishing the transfer. Also, EVM instructions' gas costs may increase in the future. Thus, some contracts that can receive now may stop working in the future due to the gas limitation. ```solidity=581 payable(marketingaddress).transfer(address(this).balance); ``` - `PoodleFi.swapAndLiquify` uses `transfer()`.
The audit on Trustblock · Open the reportThe linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
The audit on Trustblock · Open the reportThe PoodleFi security record · Every PoodleFi address · This address on the explorer