0xd04301b19e74efc656548be601a4f1fd37a822a0
As of 21 Nov 2026, Trustblock’s record holds 0xd04301b19e74efc656548be601a4f1fd37a822a0 on BNB Chain as a contract of Aeterna. 1 audit report on Trustblock lists this address: CertiK, 27 Sep 2023. 7 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
3 High, 4 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Aeterna` the role `_owner` has authority over the functions shown in the diagram below. - `startLaunchSequence()`, to initiate and start Aeterna. - `setRewardYield()`, to set the reward yield and the rebase frequency. - `setTaxes()`, to set fees, including `liquidityFee`, `aeternaTreasuryFee`, `aeternaDefenceFee` and `sellFee`. - `setFeeReceivers()`, to set the reception addresses for `aeternaTreasuryFee` and `aeternaDefenceFee`. - `setAutoRebase()`, to enable/disable auto rebase, if enabled, reset the `_lastRebasedTime` to `block.timestamp`. - `setRebasePairTokens()`, to enable/disable burning increased tokens in DEX pair after the rebase. - `setTransferFeeStatus()`, to enable/disable charging fees for the token transfers. - `setSellLimits()`, to enable/disable the token selling limit and the selling threshold. - `setMaxTxPercent()`, to set the maximum transaction limit. - `setSwapBackSettings()`, to set the `swapThreshold`, `swapAndLiquifyEnabled` and `swapAndLiquifyByLimitOnly`. - `setWhitelist()`, to add/remove an account to the fee exempt list. - `setAuthorized()`, to add/remove an account to the authorized list. The accounts on the authorization list will have no transaction limits or sales threshold restrictions. - `setBotBlacklist()`, to add/remove a contract address to the blacklist. - `setPairAddress()`, to change DEX pair contract address. - `manualSync()`, to sync the balance and reserve in the DEX pair. - `manualRebase()`, to rebase and adjust the token supply. - `withdrawAllToTreasury()`, to swap all fees to BNB and transfer to the EOA `aeternaTreasuryAddress`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 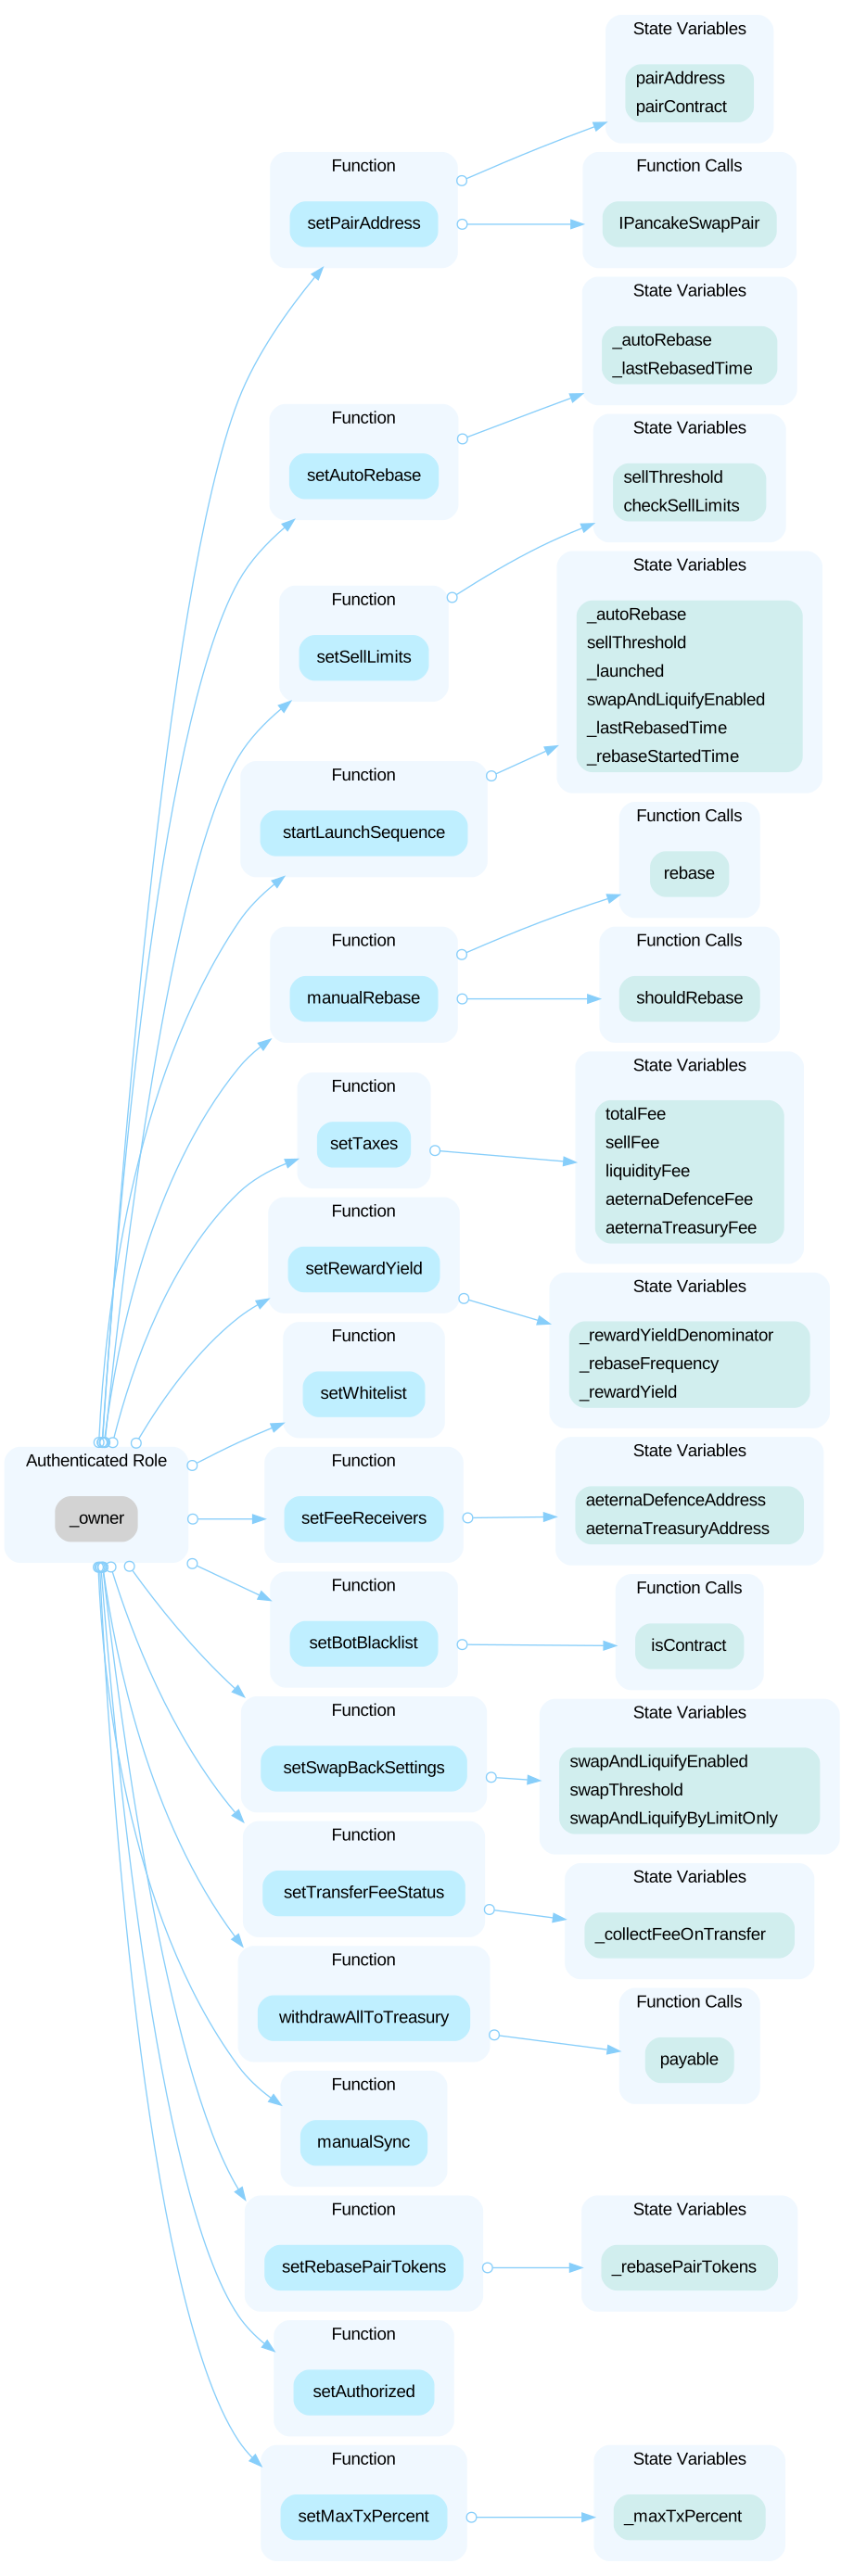 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. - `waiveOwnership()`, to renounce the ownership. - `transferOwnership()`, to transfer ownership to a new address. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 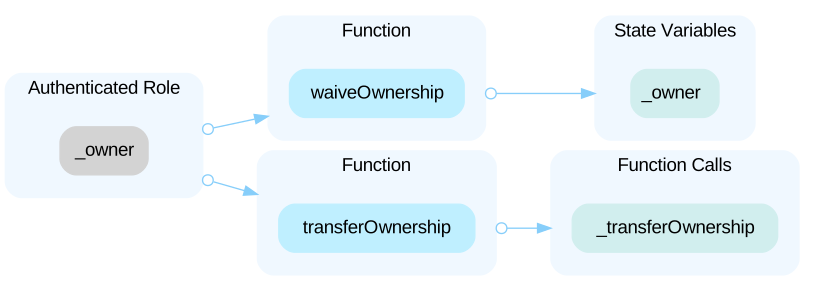
The audit on Trustblock · Open the reportThe `addLiquidity` function calls the `router.addLiquidityETH` function with the `to` address specified as `owner` for acquiring the generated LP tokens from the pair. As a result, over time, the `owner` address will accumulate a significant portion of LP tokens. If the `owner` is an EOA (Externally Owned Account), mishandling its private key can have devastating consequences for the project as a whole.
The audit on Trustblock · Open the reportAll of the tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute all tokens without obtaining the consensus of the community.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportA sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (before the transaction is attacked) a transaction to purchase one of the assets and make profits by back running (after the transaction is attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `swapTokensForBNB()` - `addLiquidity()` - `withdrawAllToTreasury()`
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with third-party PancakeSwap protocols. The scope of the audit treats 3rd party entities as black boxes and assumes their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts, such as increasing fees of 3rd parties, migrating to new LP pools, etc.
The audit on Trustblock · Open the reportThe return value of an external call is not stored in a local or state variable. File: Aeterna.sol (Line 861-868, Function `Aeterna.addLiquidity`) ```solidity router.addLiquidityETH{value: bnbAmount}( address(this), tokenAmount, 0, 0, owner(), block.timestamp ); ```
The audit on Trustblock · Open the reportThe Aeterna security record · Every Aeterna address · This address on the explorer