0xe615c5e7219f9801c3b75bc76e45a4dab3c38e51
As of 21 Nov 2026, Trustblock’s record holds 0xe615c5e7219f9801c3b75bc76e45a4dab3c38e51 on BNB Chain as a contract of Vemate. 1 audit report on Trustblock lists this address: CertiK, 22 Sep 2022. 2 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
2 High. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the address of `_owner` to another contract or user. 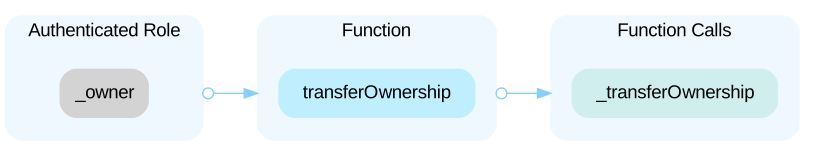 In the contract `Vemate` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and completely change features of this contract, such as adjusting fee amounts, draining the funds (in BNB and the contract token) from the contract and sending them to their preferred address, adjusting timelock settings, maliciously updating `maxTxAmount`, `tokenPerBNB`, or `setMinTokenToSwapAndLiquify` to undesirable values. The attacker would also be able to change the router address, adjust the `swapSlippageTolerancePercent` to be as high as 100%, and update the `_isPrivileged` status of any address they want. 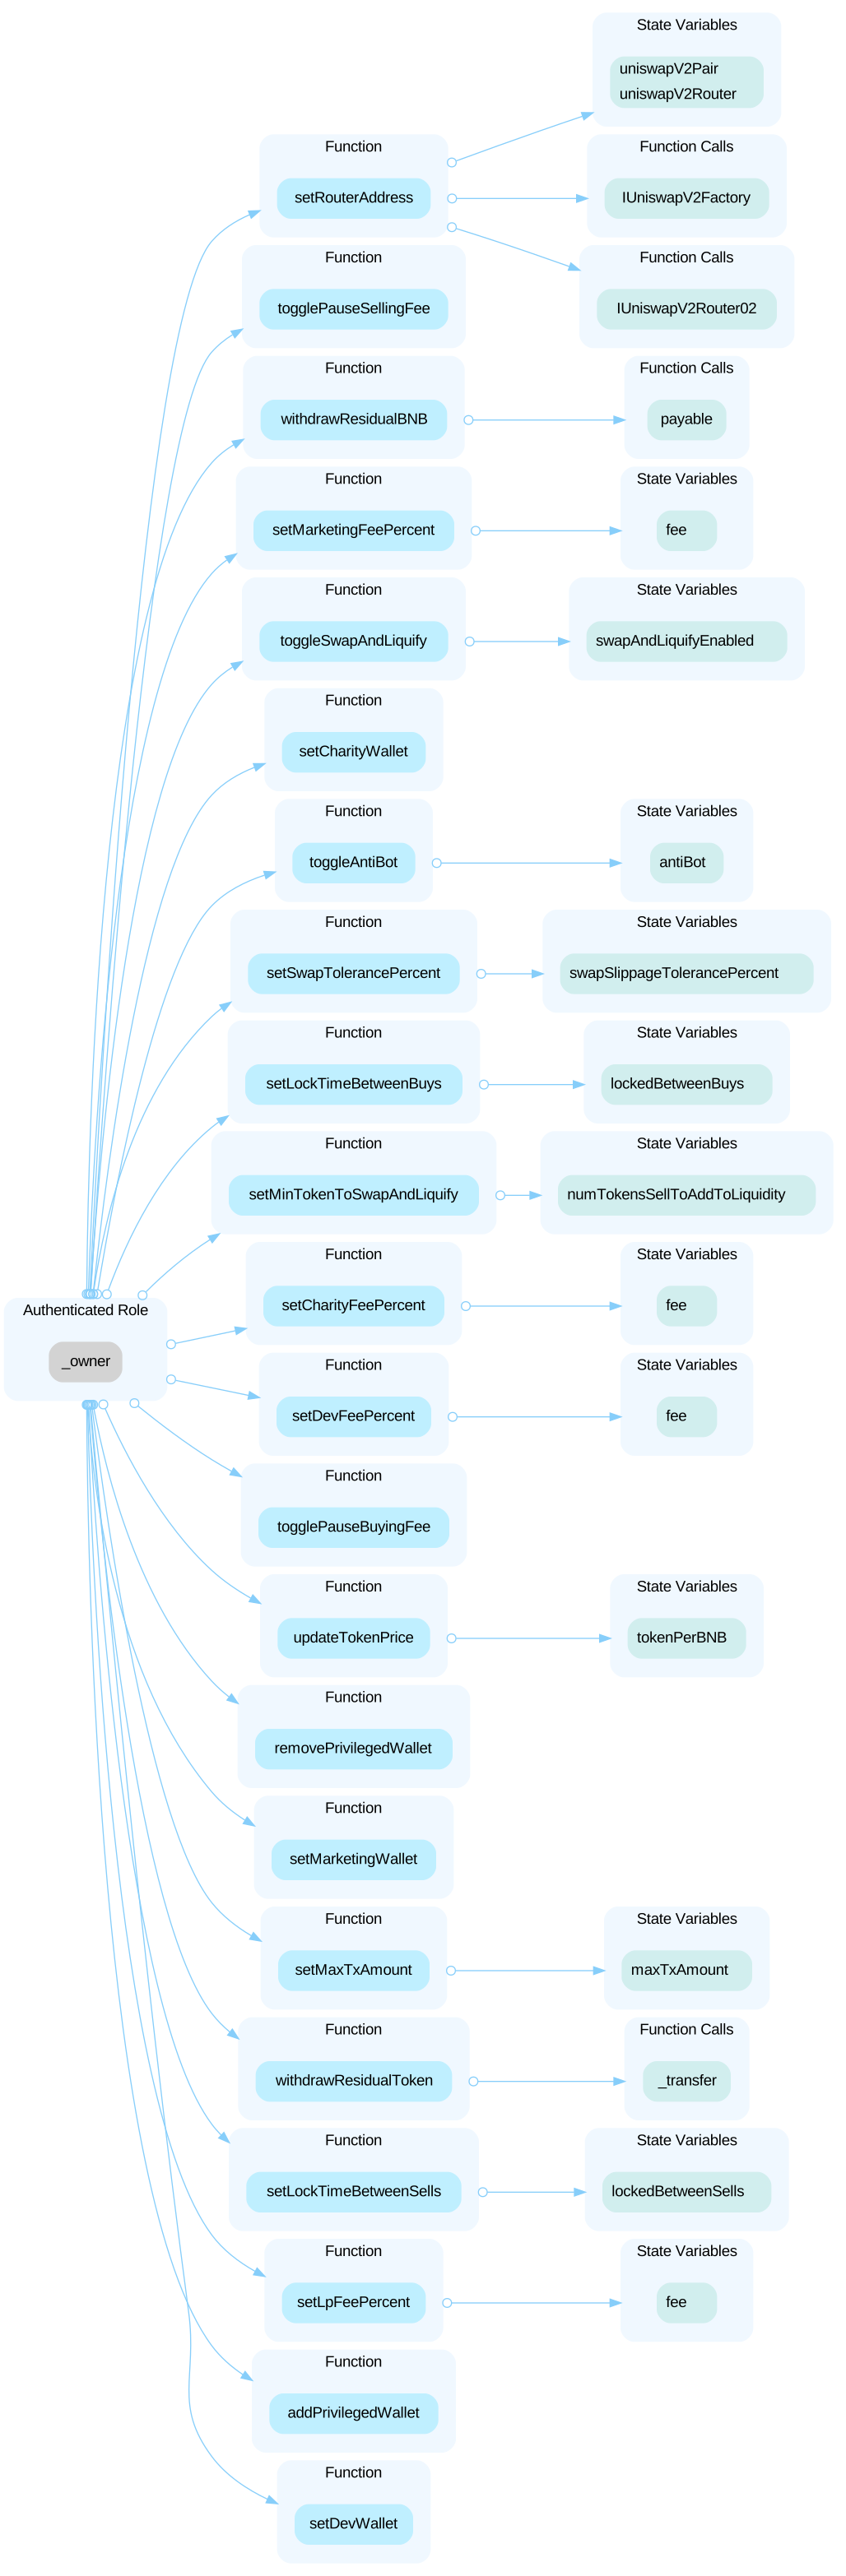
The audit on Trustblock · Open the reportUpon deployment of the contract, the `_totalSupply` for the contract token is held solely by the `_owner` of the contract. This could be a centralization risk as the deployer can distribute tokens without obtaining the consensus of the community.
The audit on Trustblock · Open the reportThe Vemate security record · Every Vemate address · This address on the explorer