0x26ebb8213fb8d66156f1af8908d43f7e3e367c1d
As of 21 Nov 2026, Trustblock’s record holds 0x26ebb8213fb8d66156f1af8908d43f7e3e367c1d on Ethereum as a contract of Retik Finance. 1 audit report on Trustblock lists this address: CertiK, 9 Jan 2024. 8 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Retik Finance | CertiK | Not recorded (see the report) | Open |
2 High, 6 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to transfer ownership. 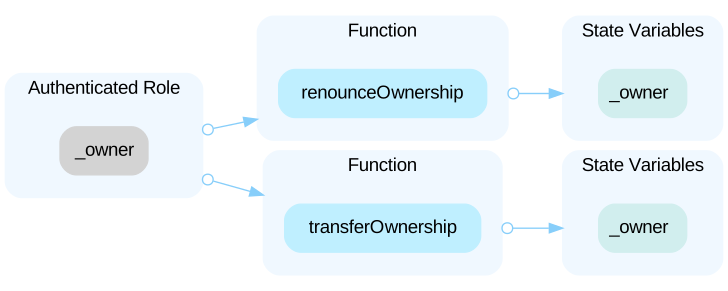 In the contract `Retik_Finance` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to interfere with governance processes. 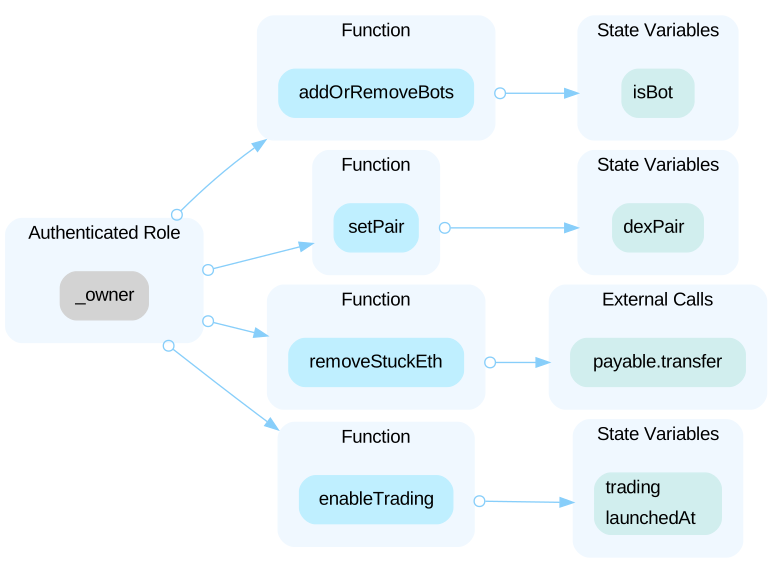
The audit on Trustblock · Open the report`1_000_000_000 * 1e18` `RETIK` tokens were sent to the `owner` when deploying the contract. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportThe Anti-Bot mechanism is unable to protect against the initial entry of bots. In lines 292 to 296 of the code, it identifies and flags the "from" and "to" addresses as Bots. Due to the order of operations, where the check for whether an address is a bot occurs prior to this section, it can result in a situation where even if the "from" or "to" address is flagged as a bot during the current transaction, the transaction can still proceed normally. ```solidity=283 require(!isBot[from], "RETIK: Bot detected"); if (from != owner() && to != owner()) { // trading disable till launch require(trading, "RETIK: trading is disable"); // antibot if ( block.timestamp < launchedAt + snipingTime ) { if (dexPair == from) { isBot[to] = true; } else if (dexPair == to) { isBot[from] = true; } } } ``` The question we want to discuss is whether we need to penalize bots or block transactions the first time they enter.
The audit on Trustblock · Open the reportThere should always be events emitted in sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportThe change of `owner` by function `transferOwnership()` overrides the previously set `owner` with the new one without guaranteeing the new `owner` has the ability to actuate transactions on-chain.
The audit on Trustblock · Open the reportSolidity version >=0.8.0 includes checked arithmetic operations and underflow/overflow by default, making SafeMath redundant.
The audit on Trustblock · Open the reportThe event `SwapAndLiquify` is declared but the current code logic does not use this information.
The audit on Trustblock · Open the reportThe values of `_name`,`_symbol`,`_decimals`,`_totalSupply` and `snipingTime` are never changed after assignment, so they can be declared as `constant`. A big advantage of constant variables is that reading them is significantly cheaper than reading from regular state variables.
The audit on Trustblock · Open the reportThe Retik Finance security record · Every Retik Finance address · This address on the explorer