0x28bd01e51a9f6b47d7826c6e1d8a0fbbf57fc2a0
As of 21 Nov 2026, Trustblock’s record holds 0x28bd01e51a9f6b47d7826c6e1d8a0fbbf57fc2a0 on Ethereum as a contract of WFCA Infrastructure. 1 audit report on Trustblock lists this address: CertiK, 14 Sep 2023. 4 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
3 High, 1 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `TokenERC20` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set critical variables. 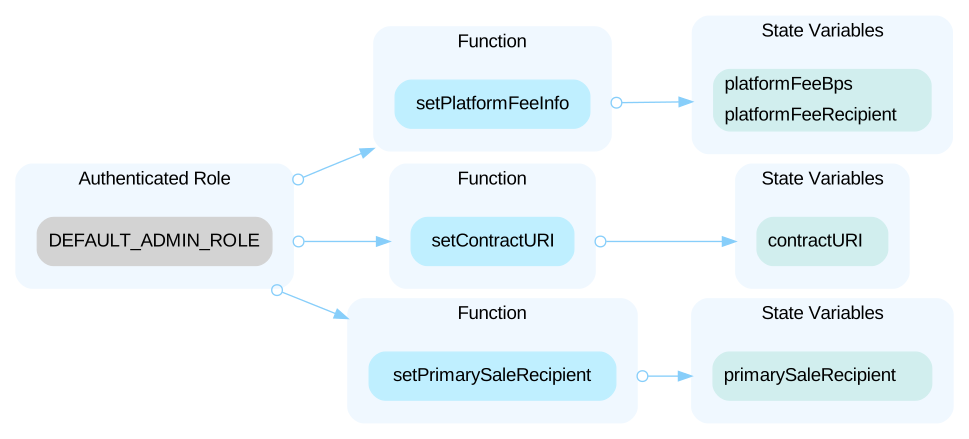 --- In the contract `TokenERC20` the role `MINTER_ROLE` has authority over the function shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint tokens. 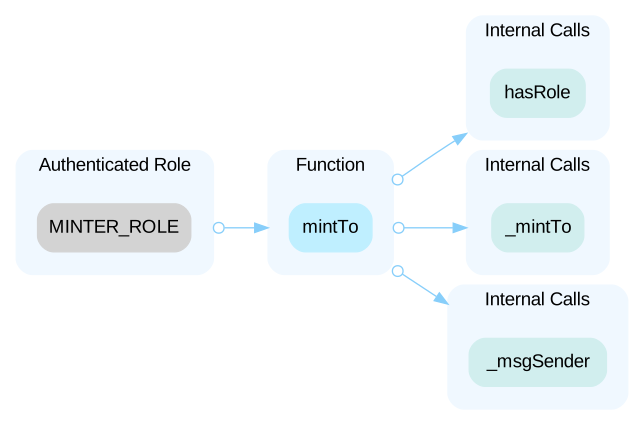 --- In the contract `AccessControlUpgradeable` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. --- In the contract `AccessControlUpgradeable` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts.
The audit on Trustblock · Open the reportThe `TokenERC20` contract inherits from the `ERC2771ContextUpgradeable` contract. This design enables designated accounts, known as `_trustedForwarders`, to execute calls on behalf of any other account. If a `_trustedForwarder` is compromised, it could allow unauthorized actions on the contract, including operations associated with the `DEFAULT_ADMIN_ROLE`. Reference: [EIP-2771](https://eips.ethereum.org/EIPS/eip-2771)
The audit on Trustblock · Open the reportOn Sep 12, 2023, the addresses 0x4955b9aCfBAe877295965B73d08BD679D30fDa2e and 0x97224595072094aA8a2730cbB4261D42c70ab378 have all the WFCA tokens. This is a centralization risk because these addresses can distribute tokens without obtaining the consensus of the community. Any compromise to the addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportAddresses are not validated before assignment or external calls, potentially allowing the use of zero addresses and leading to unexpected behavior or vulnerabilities. For example, transferring tokens to a zero address can result in a permanent loss of those tokens. ```solidity=94 primarySaleRecipient = _primarySaleRecipient; ``` - `_primarySaleRecipient` is not zero-checked before being used. --- ```solidity=95 platformFeeRecipient = _platformFeeRecipient; ``` - `_platformFeeRecipient` is not zero-checked before being used. --- ```solidity=179 primarySaleRecipient = _saleRecipient; ``` - `_saleRecipient` is not zero-checked before being used. --- ```solidity=191 platformFeeRecipient = _platformFeeRecipient; ``` - `_platformFeeRecipient` is not zero-checked before being used.
The audit on Trustblock · Open the reportThe WFCA Infrastructure security record · Every WFCA Infrastructure address · This address on the explorer