0x75198d07d7d6514efad683b635e967c55ca4ded8
As of 21 Nov 2026, Trustblock’s record holds 0x75198d07d7d6514efad683b635e967c55ca4ded8 on Ethereum as a contract of ZELIX. 1 audit report on Trustblock lists this address: CertiK, 18 Aug 2023. 3 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| ZELIX-Audit | CertiK | Not recorded (see the report) | Open |
2 High, 1 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `ERC20Lockable` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority to unlock tokens for any account and call `transferWithLockUp()` to transfer tokens and create a lock for the recipient. 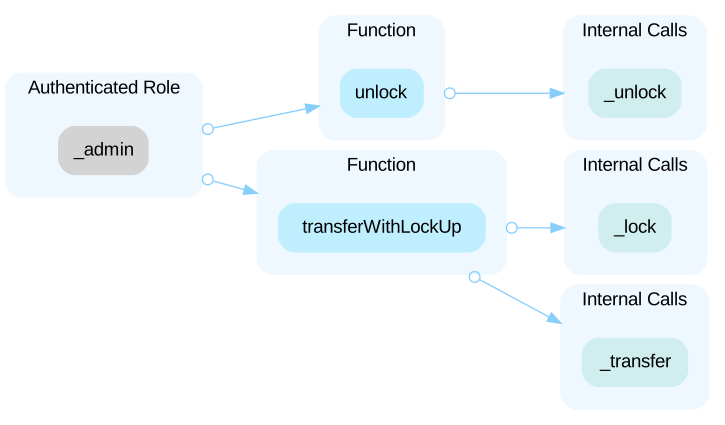 In the contract `ERC20Lockable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set admin accounts. 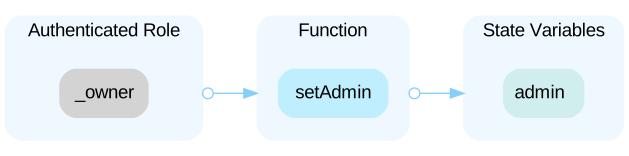 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 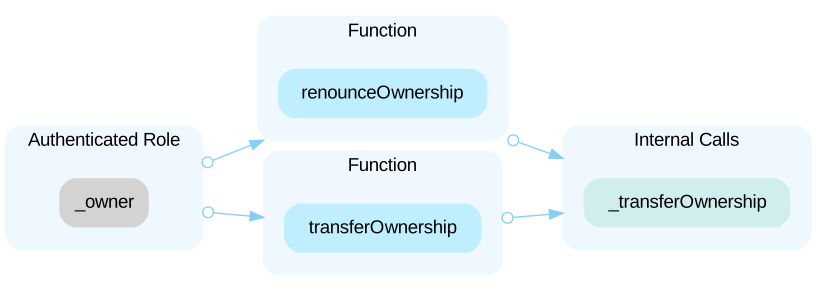 In the contract `ZELIX` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and blacklist any account from transferring tokens. 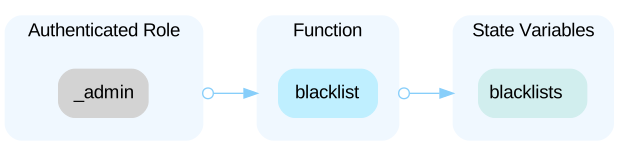
The audit on Trustblock · Open the reportAll of the ZELIX tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportVariables are written but never read and subsequently written again, suggesting potential inefficiencies or logic errors in the code. This may lead to confusion when analyzing the code or impact the performance of the smart contract during execution. `success` is written twice, but not used in-between. ```solidity=265 success = _burn(msg.sender, amount); ``` ```solidity=267 success = true; ```
The audit on Trustblock · Open the reportThe ZELIX security record · Every ZELIX address · This address on the explorer