0x83389cb4e4f0bff39915efa839cb827460e70d26
As of 21 Nov 2026, Trustblock’s record holds 0x83389cb4e4f0bff39915efa839cb827460e70d26 on Ethereum as a contract of AnyDex. 1 audit report on Trustblock lists this address: CertiK, 10 Oct 2024. 4 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
2 High, 2 Low. In the firm’s own words; statuses are the firm’s, from each report.
**In `anydex_v3.sol`:** In the contract `Anydex` the role `isTxLimitExempt` has authority over the function shown in the diagram below. Any compromise to the `isTxLimitExempt` account may allow the hacker to take advantage of this authority and transfer tokens excluding ANYDEX from the contract. 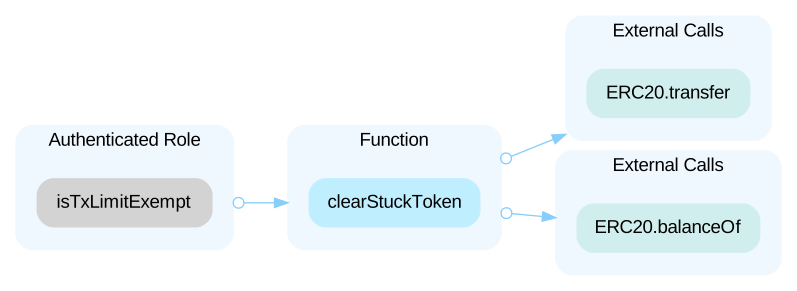 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer or renounce the ownership. 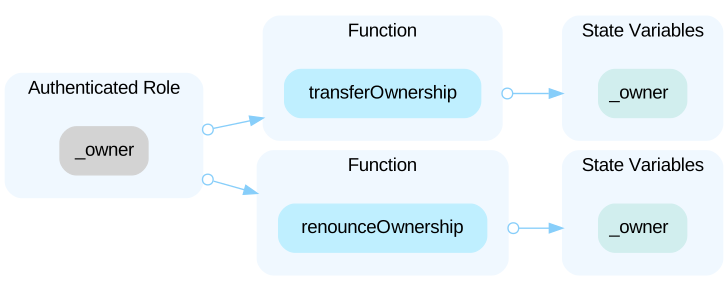 In the contract `Anydex` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set max holding amount limit, max transfer amount limit, remove max holding amount and max transfer amount limit, enable trading, set fee and transfer amount exempt accounts, update buy/sell fee rates, update `marketingFeeReceiver` and `teamFeeReceiver`, enable/disable swapping, and setting swap threshold. 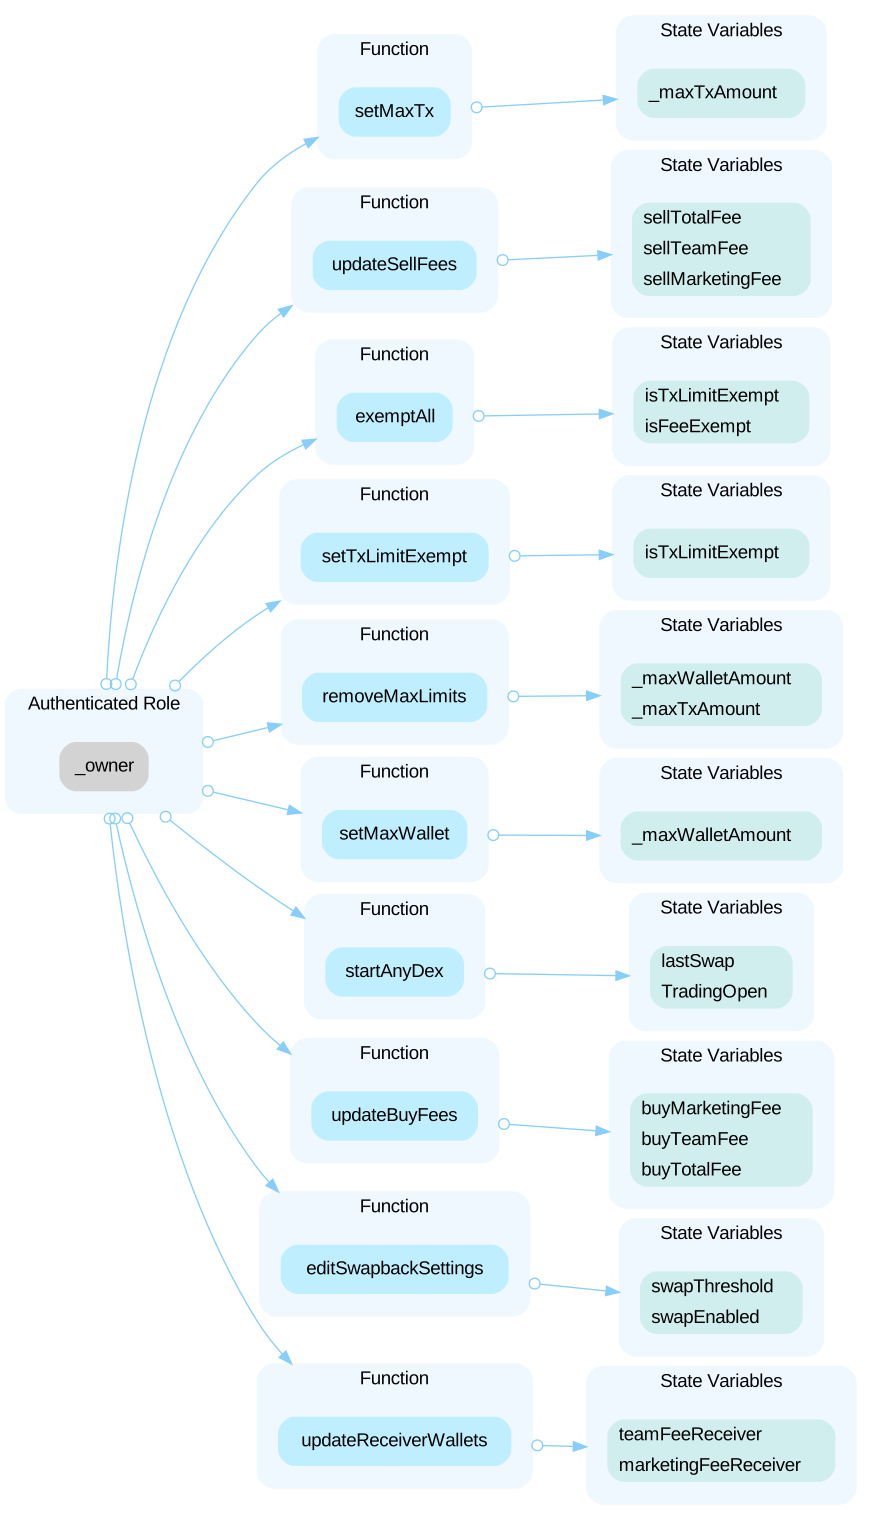 In the contract `Anydex`, the role `_owner` can transfer tokens before trading is enabled and can make the receiver bypass the wallet amount limit check. In the contract `Anydex`, the role `isTxLimitExempt` can transfer tokens without considering the max transfer amount limit. --- **In `anydex_v4.sol`:** The `clearStuckToken()` function is changed such that only `marketingFeeReceiver` and `teamFeeReceiver` can call it.
The audit on Trustblock · Open the reportAll of the ANYDEX tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to the address may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportA sandwich attack may happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (executing before the target) a transaction to purchase one of the assets and make profits by backrunning (executing after the target) a transaction to sell the asset. The cited function is called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large. ```solidity=360 router.swapExactTokensForETHSupportingFeeOnTransferTokens( amountToSwap, 0, path, address(this), block.timestamp ); ```
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity IDEXRouter public router; router = IDEXRouter(0x7a250d5630B4cF539739dF2C5dAcb4c659F2488D); ``` - The contract `Anydex` interacts with third party contract with `IDEXRouter` interface via `router`. --- ```solidity=153 InterfaceLP private pairContract; ``` - The contract `Anydex` interacts with third party contract with `InterfaceLP` interface via `pairContract`.
The audit on Trustblock · Open the reportThe AnyDex security record · Every AnyDex address · This address on the explorer