0xd073e6341a3aa6c4d94c4f8f20fbd1ede572b0da
As of 21 Nov 2026, Trustblock’s record holds 0xd073e6341a3aa6c4d94c4f8f20fbd1ede572b0da on Ethereum as a contract of METACENE. 1 audit report on Trustblock lists this address: CertiK, 4 Dec 2024. 3 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| MetaCene-addendum | CertiK | Not recorded (see the report) | Open |
2 High, 1 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Ownable`, the role `_owner` has authority over the following function: - `renounceOwnership()` Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and renounce ownership of the contract. ----- In the contract `Ownable2Step`, the role `_owner` has authority over the following function: - `transferOwnership()` Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the `_pendingOwner` role. In the contract `Ownable2Step`, the role `_pendingOwner` has authority over the following function: - `acceptOwnership()` Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and accept the ownership. ----- In the contract `MakToken`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and remove or add an operator role. 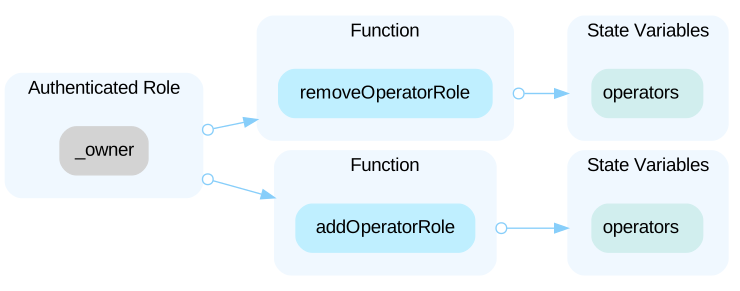 In the contract `MakToken`, the role `operators` has authority over the functions shown in the diagram below. Any compromise to the `operators` account may allow the hacker to take advantage of this authority and add or remove addresses from the receive and transfer blacklists. 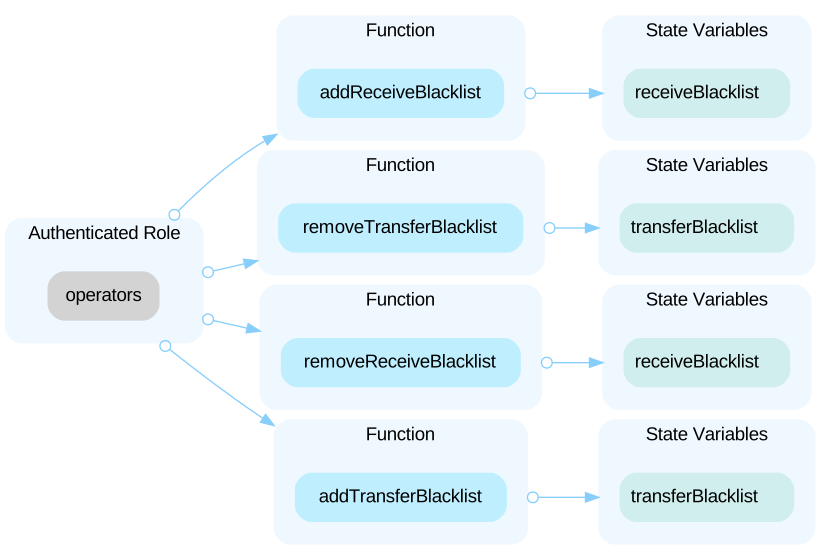
The audit on Trustblock · Open the reportThe MAK tokens are being transferred to the `vestingContract` located at address `0x7B2681846bFCA910Ada6ebd8590481910388d037`. This contract is currently unverified. Based on its name, it appears to be a vesting contract. A vesting contract usually allows privileged addresses to distribute tokens without requiring community consensus. If any of these privileged addresses are compromised, an attacker could potentially steal and liquidate the tokens, causing significant harm to the project.
The audit on Trustblock · Open the reportThe **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
The audit on Trustblock · Open the reportThe METACENE security record · Every METACENE address · This address on the explorer