0x3cf64cc11b0437fd4156cb3e331cd59aaffc45f8
As of 21 Nov 2026, Trustblock’s record holds 0x3cf64cc11b0437fd4156cb3e331cd59aaffc45f8 on Polygon (POS) as a contract of Runy. 1 audit report on Trustblock lists this address: CertiK, 3 Mar 2023. 3 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Polygon (POS).
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Runiverse - Audit | CertiK | Not recorded (see the report) | Open |
1 High, 2 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Runiverse` derived from `RuniverseAdministrative` the role `_owner` has authority over the functions shown in the diagram below. 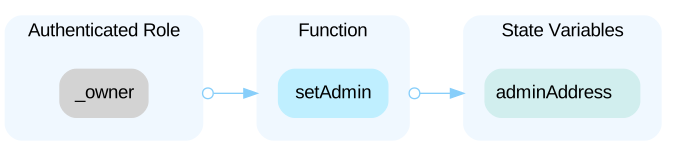 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the `adminAddress`. In the contract `Runiverse` derived from `CryptorunModifier` the role `adminAddress` has authority over the functions shown in the diagram below. 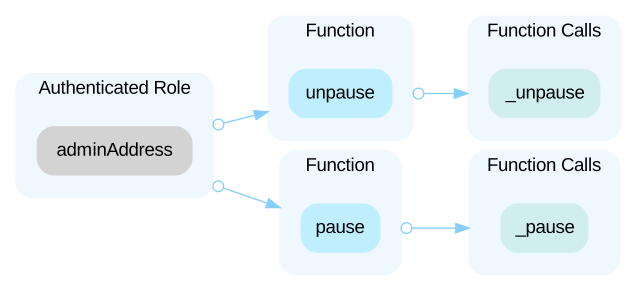 In the contract `Runiverse` derived from `CryptorunNFTLinker` the role `adminAddress` has authority over the functions shown in the diagram below. 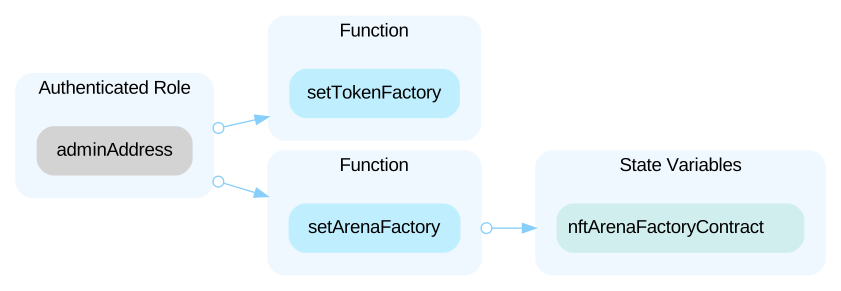 In the contract `Runiverse` derived from `RuniverseFeeSharer` the role `adminAddress` has authority over the functions shown in the diagram below. 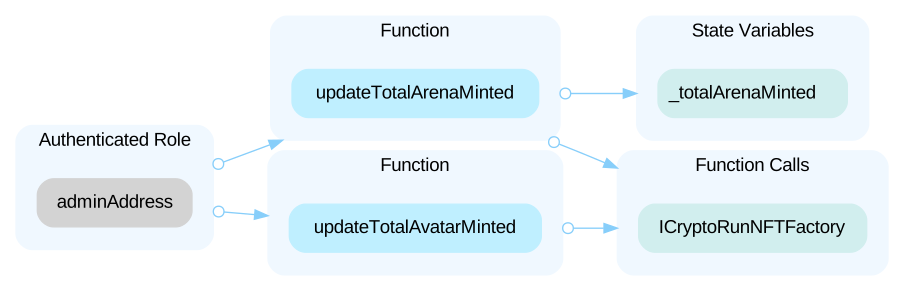 In the contract `Runiverse` derived from `RuniverseAdministrative` the role `adminAddress` has authority over the functions shown in the diagram below. 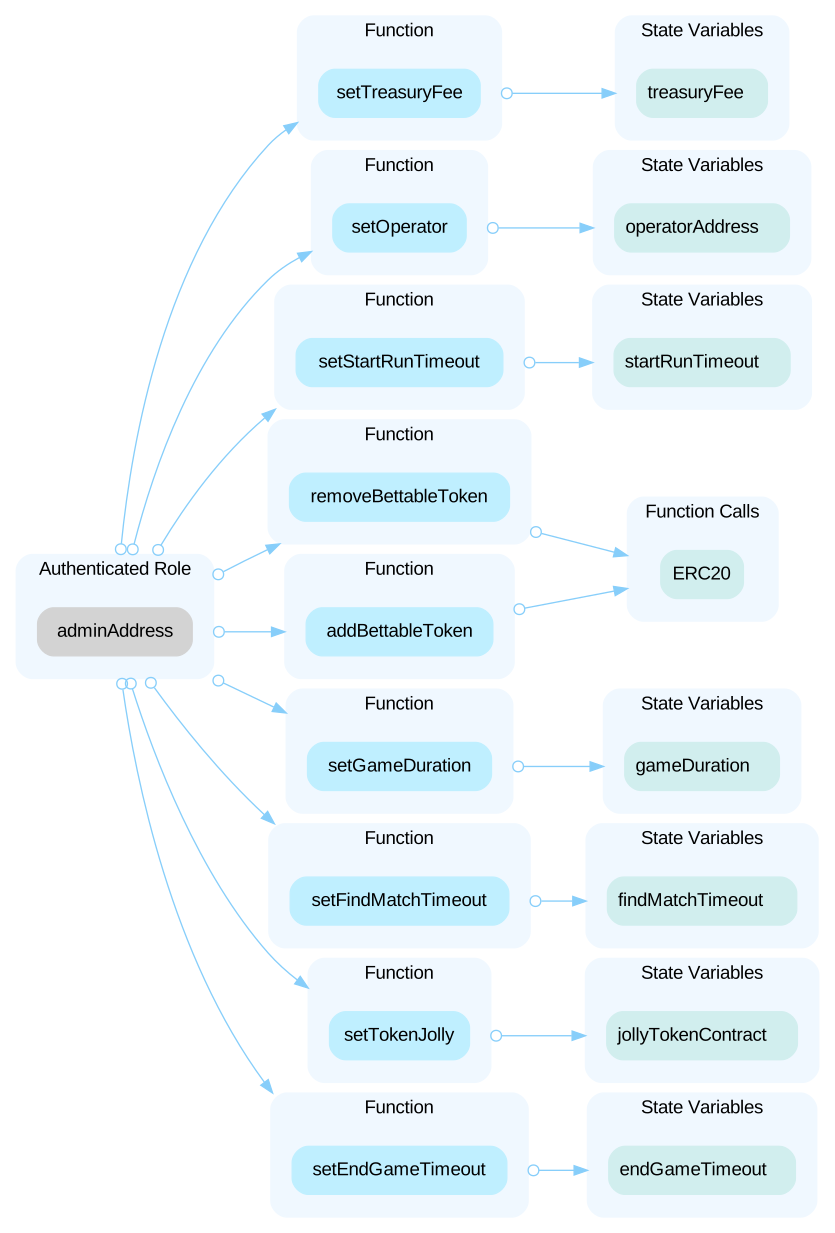 Any compromise to the `adminAddress` account may allow the hacker to take advantage of this authority and update state variables. In the contract `Runiverse` derived from `CryptorunModifier` the role `operatorAddress` has authority over the functions shown in the diagram below. 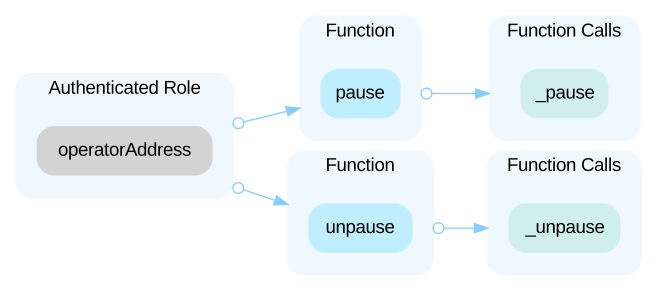 In the contract `Runiverse` derived from `RuniverseFeeSharer` the role `operatorAddress` has authority over the functions shown in the diagram below. 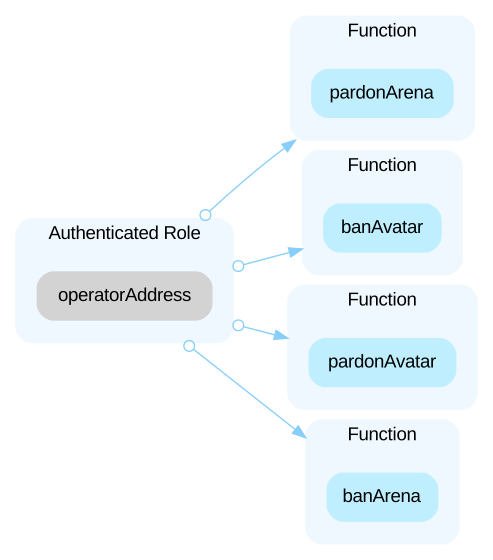 In the contract `Runiverse` derived from `RuniverseAdministrative` the role `operatorAddress` has authority over the functions shown in the diagram below. 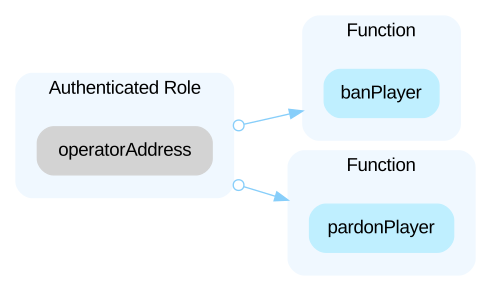 Any compromise to the `operatorAddress` account may allow the hacker to take advantage of this authority and pause/unpause the contract. In the contract `Runiverse` the role `endRunOperatorAddress` has authority over the functions shown in the diagram below. Any compromise to the `endRunOperatorAddress` account may allow the hacker to take advantage of this authority and call the `endRun` function. 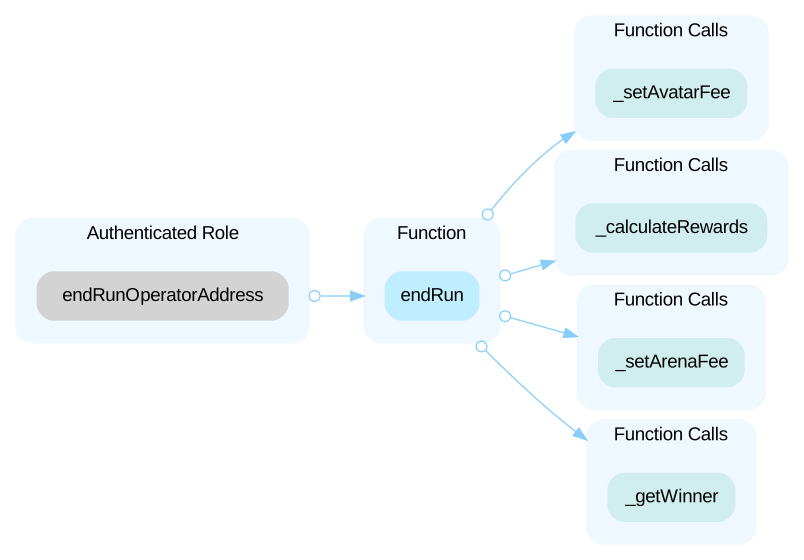 **Note: this finding is based on Certik Syntactic Analyzer.** **Please review the client's code to see if any modification is required.** In the contract `Runiverse` the role `startRunOperatorAddress` has authority over the functions shown in the diagram below. Any compromise to the `startRunOperatorAddress` account may allow the hacker to take advantage of this authority and call the `startRun` function. 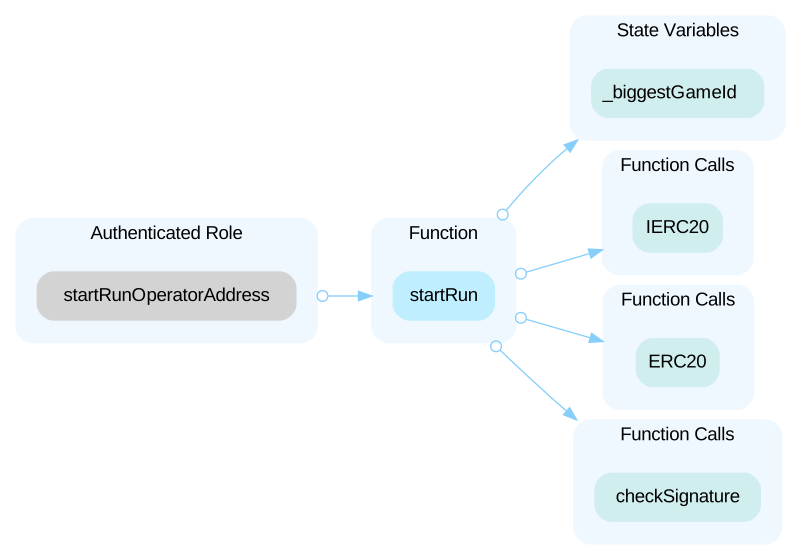
The audit on Trustblock · Open the reportThe `_setArenaFee` function checks if `distributionArenaFeesCounter` is greater than `_totalArenaMinted`, but the `_totalArenaMinted` is updated by the admin asynchronously. If the admin does not update the `_totalArenaMinted` in time, the latest `arenaID` will not get fees. The same issue also happens in the `_setAvatarFee` function, where `_totalAvatarMinted[avatarCurrency]` should be checked synchronously.
The audit on Trustblock · Open the reportThe state variable `findMatchTimeout` and `startRunTimeout` are never used in the contract logic.
The audit on Trustblock · Open the reportThe Runy security record · Every Runy address · This address on the explorer