0x52afcd78c3ba1cd6187c1d13fe12d5fc5d0fb3e2
As of 21 Nov 2026, Trustblock’s record holds 0x52afcd78c3ba1cd6187c1d13fe12d5fc5d0fb3e2 on Polygon (POS) as a contract of Peerblue Exchange. 1 audit report on Trustblock lists this address: CertiK, 19 Jan 2023. 5 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Polygon (POS).
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| PBX - PBMaticPrediction | CertiK | Not recorded (see the report) | Open |
1 High, 1 Medium, 3 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 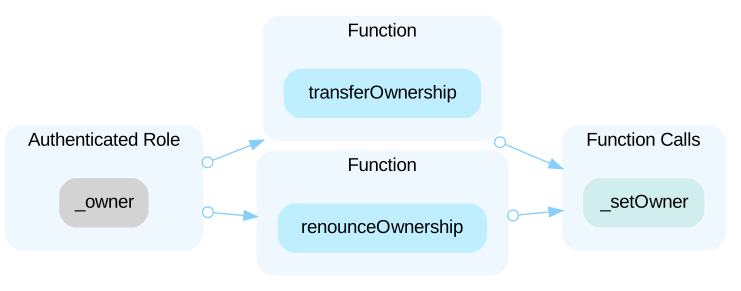 In the contract `PBMaticPrediction` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 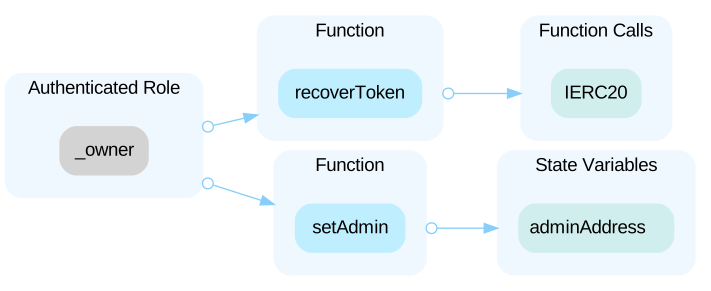 In the contract `PBMaticPrediction` the role `adminAddress` has authority over the functions shown in the diagram below. Any compromise to the `adminAddress` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 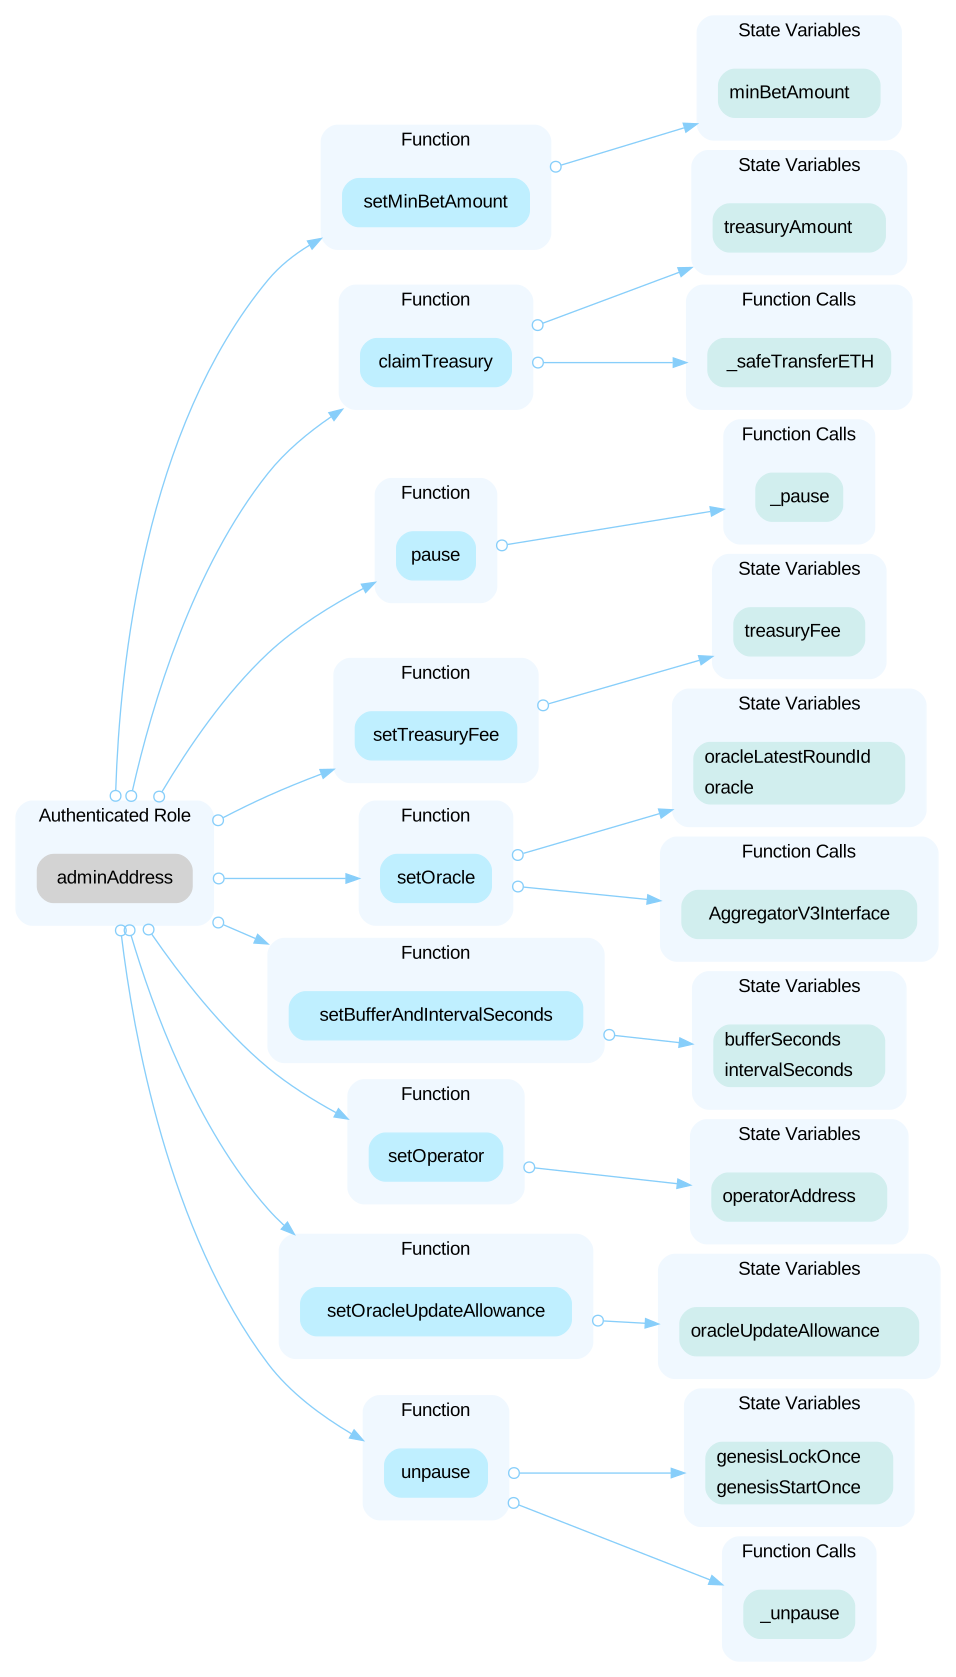 In the contract `PBMaticPrediction` the role `operatorAddress` has authority over the functions shown in the diagram below. Any compromise to the `operatorAddress` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 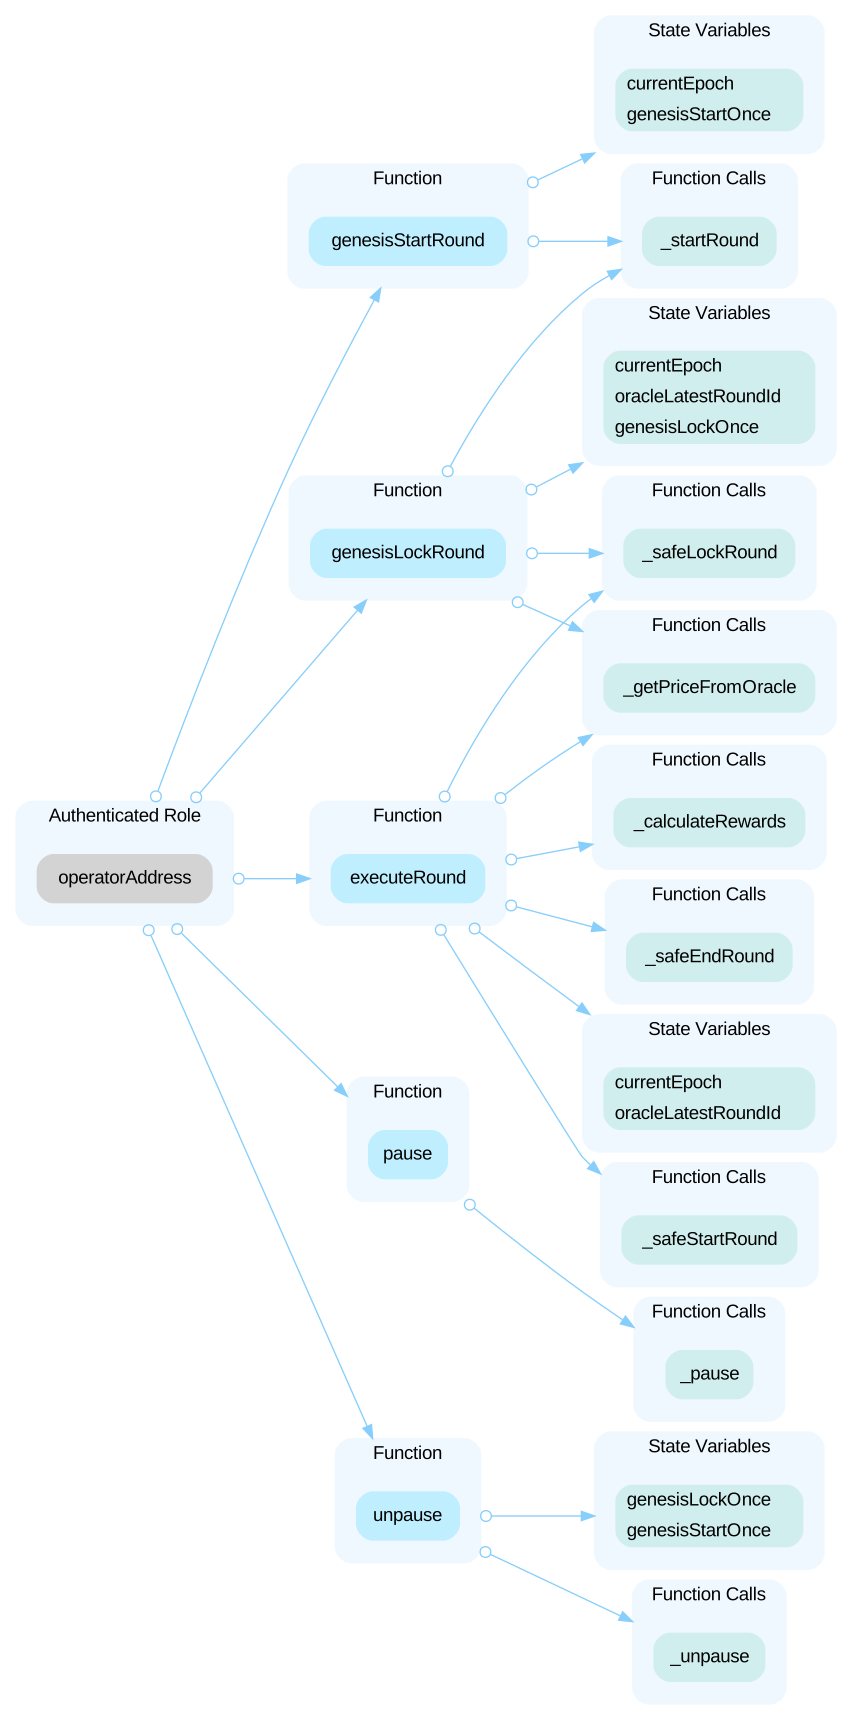
The audit on Trustblock · Open the reportAs long as more than one side is offered, no more than 10% of the total bet will always go to the treasury. This increases the possibility that, even if a bet is successful, the principal may not be refunded, which might be a problem.
The audit on Trustblock · Open the reportThe call was definitely initiated by an external account when the smart contract checked **msg.sender == tx.origin** and found the result was true (EOA: Externally Owned Account). Hence the `isContract` check is redundant here.
The audit on Trustblock · Open the reportThe check for `oracleCalled` in the claim function is unnecessary if `oracleCalled` is a factor in determining whether the user is claimable or not. The oracleCalled check is required, though, if the two tests are independent of one another.
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=752 AggregatorV3Interface public oracle; ``` - The contract `PBMaticPrediction` interacts with third-party contract with `AggregatorV3Interface` interface via `oracle`. --- ```solidity=1224 function recoverToken(address _token, uint256 _amount) external onlyOwner { ``` - The function `PBMaticPrediction.recoverToken` interacts with third-party contract with `IERC20` interface via `_token`.
The audit on Trustblock · Open the reportThe Peerblue Exchange security record · Every Peerblue Exchange address · This address on the explorer