0x82cb0ec6a31bc92e9483c08fdcbe2e6f3cc28100
As of 21 Nov 2026, Trustblock’s record holds 0x82cb0ec6a31bc92e9483c08fdcbe2e6f3cc28100 on Polygon (POS) as a contract of IBS. 1 audit report on Trustblock lists this address: CertiK, 30 May 2024. 5 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Polygon (POS).
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| IBStoken - Audit | CertiK | Not recorded (see the report) | Open |
2 High, 1 Medium, 2 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Pausable` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and pause/unpause token transfers. 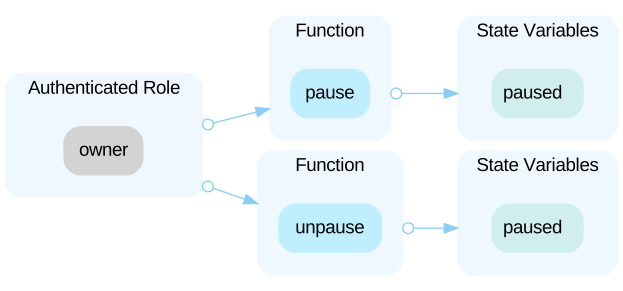
The audit on Trustblock · Open the reportAll of the IBSTokens are sent to the contract owner which is an externally-owned account (EOA) address on deployment. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportThe blacklist feature is designed to prevent the blacklisted users from transferring the `IBSToken` to others by validating the following **require** statement: ```solidity=145 function transferFrom(address _from, address _to, uint256 _value) public returns (bool) { require(tokenBlacklist[msg.sender] == false); ``` The **require** statement prohibits the blacklisted users from calling `transfer()` and `transferFrom()` to move their funds by requiring the `msg.sender` not blacklisted. However, this feature can be bypassed by using a combination of the `approve()`/`increaseAllowance()` and `transferFrom()` functions. The blacklisted user could approve another account to transfer his tokens on his behalf.
The audit on Trustblock · Open the reportThe data type of the decimals state variable should be `uint8` to adhere to the EIP-20 standard. Currently, some smart contracts interacting with this ERC-20 token will result in a failure. Reference: [Specification of the `decimals()` Method](https://github.com/ethereum/ercs/blob/master/ERCS/erc-20.md#decimals)
The audit on Trustblock · Open the reportThe change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
The audit on Trustblock · Open the reportThe IBS security record · Every IBS address · This address on the explorer