0xb0891671943e0d500fe0c3e5bba8f0c6c08dcf61
As of 21 Nov 2026, Trustblock’s record holds 0xb0891671943e0d500fe0c3e5bba8f0c6c08dcf61 on Polygon (POS) as a contract of Bounty Temple. 1 audit report on Trustblock lists this address: CertiK, 1 Mar 2024. 2 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Polygon (POS).
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Bounty Temple - Audit | CertiK | Not recorded (see the report) | Open |
2 High. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. - `renounceOwnership()`: Leaves the contract without owner. - `transferOwnership()`: Transfers the ownership to a new account. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the ownership. 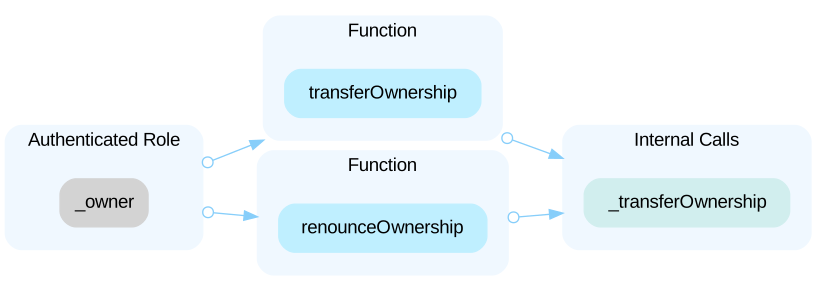 In the contract `Vesting` the role `_owner` has authority over the functions shown in the diagram below. - `removeVesting()`: Removes the user's claimed information and update the Merkle root. - `updateSignerAddress()`: Updates the signer address. - `pause()`: Pauses the functions. - `unpause()`: Resumes the functions. - `withdrawTokens()`: Withdraws the tokens. - `updateMerkleRoot()`: Updates the Merkle root. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, change the configuration, and withdraw tokens. 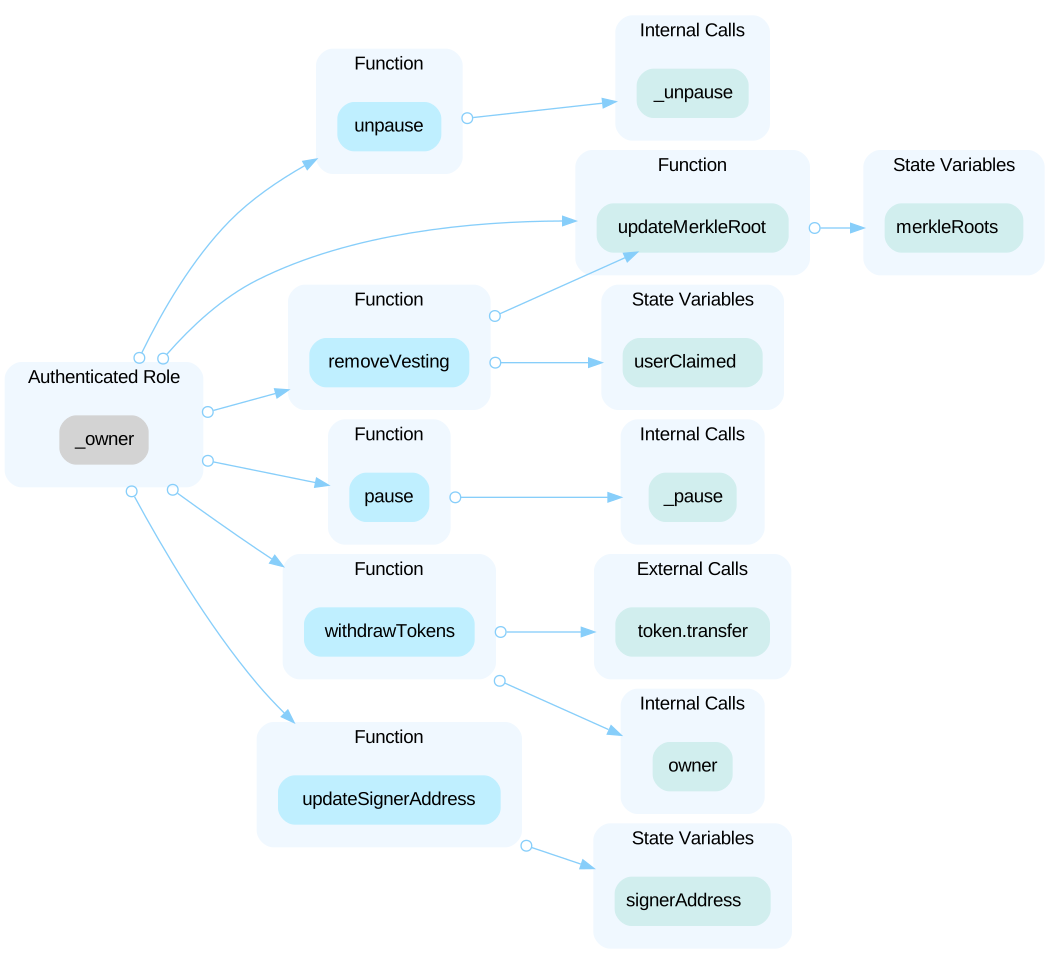 Additionally, the amount of the claimable amount for a user is determined by the "signer" role. Due to the issue mentioned in VES-03, the existing implementation lacks constraints to ensure user claimable amounts no more than the `_totalTokens` limitation. Therefore, if the signer is compromised, the attacker may create multiple signatures to claim more tokens than expected.
The audit on Trustblock · Open the reportIt is noted that the `_owner` role has the authority to update the status of the `_paused` and further pause/resume the users' claims. Any compromise to the private key of the `_owner` may allow hackers to take advantage of this authority and allow/prevent user access to the claim functionality.
The audit on Trustblock · Open the reportThe Bounty Temple security record · Every Bounty Temple address · This address on the explorer