0xfb7f8a2c0526d01bfb00192781b7a7761841b16c
As of 21 Nov 2026, Trustblock’s record holds 0xfb7f8a2c0526d01bfb00192781b7a7761841b16c on Polygon (POS) as a contract of LandRocker. 1 audit report on Trustblock lists this address: CertiK, 18 Jun 2024. 2 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Polygon (POS).
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| LandRocker - Audit | CertiK | Not recorded (see the report) | Open |
1 High, 1 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `LRT` the role `_distributor` has authority over the functions shown in the diagram below. Any compromise to the `_distributor` account may allow the hacker to take advantage of this authority and distribute tokens from the contract to any address. 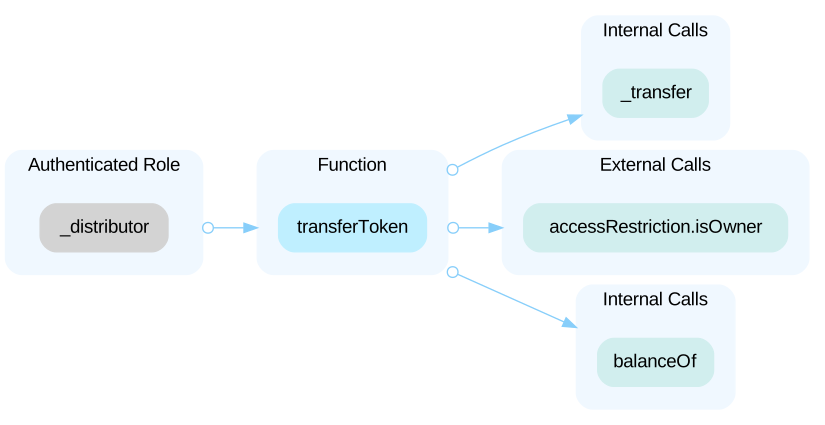
The audit on Trustblock · Open the reportThe contract is serving as the underlying entity to interact with one or more out of scope protocols. The scope of the audit treats these entities as black boxes and assumes their functional correctness. However, in the real world, those contracts can be compromised and this may lead to lost or stolen assets. I ```solidity=26 IAccessRestriction public immutable accessRestriction; ``` - The contract `LRT` interacts with out of scope contract with `IAccessRestriction` interface via `accessRestriction`.
The audit on Trustblock · Open the reportThe LandRocker security record · Every LandRocker address · This address on the explorer