0x1617851311055b8c984b9949d1d3309275fcc6cb
As of 21 Nov 2026, Trustblock’s record holds 0x1617851311055b8c984b9949d1d3309275fcc6cb on BNB Chain as a contract of Ecoin Finance. 1 audit report on Trustblock lists this address: CertiK, 11 Nov 2022. 4 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Ecoin Finance | CertiK | Not recorded (see the report) | Open |
2 High, 2 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `EcoinToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and implement a few attacks. We list the attacks below: 1. A compromised owner may first wipe the contract's ether balance by calling the function `safeWithdraw()`. 2. A hacker may pause the swapping mechanism and stake by calling the functions `setPausedSwapPool()` and `setPausedStake()`. 3. Set the minimum amount to swap to an inordinate amount. 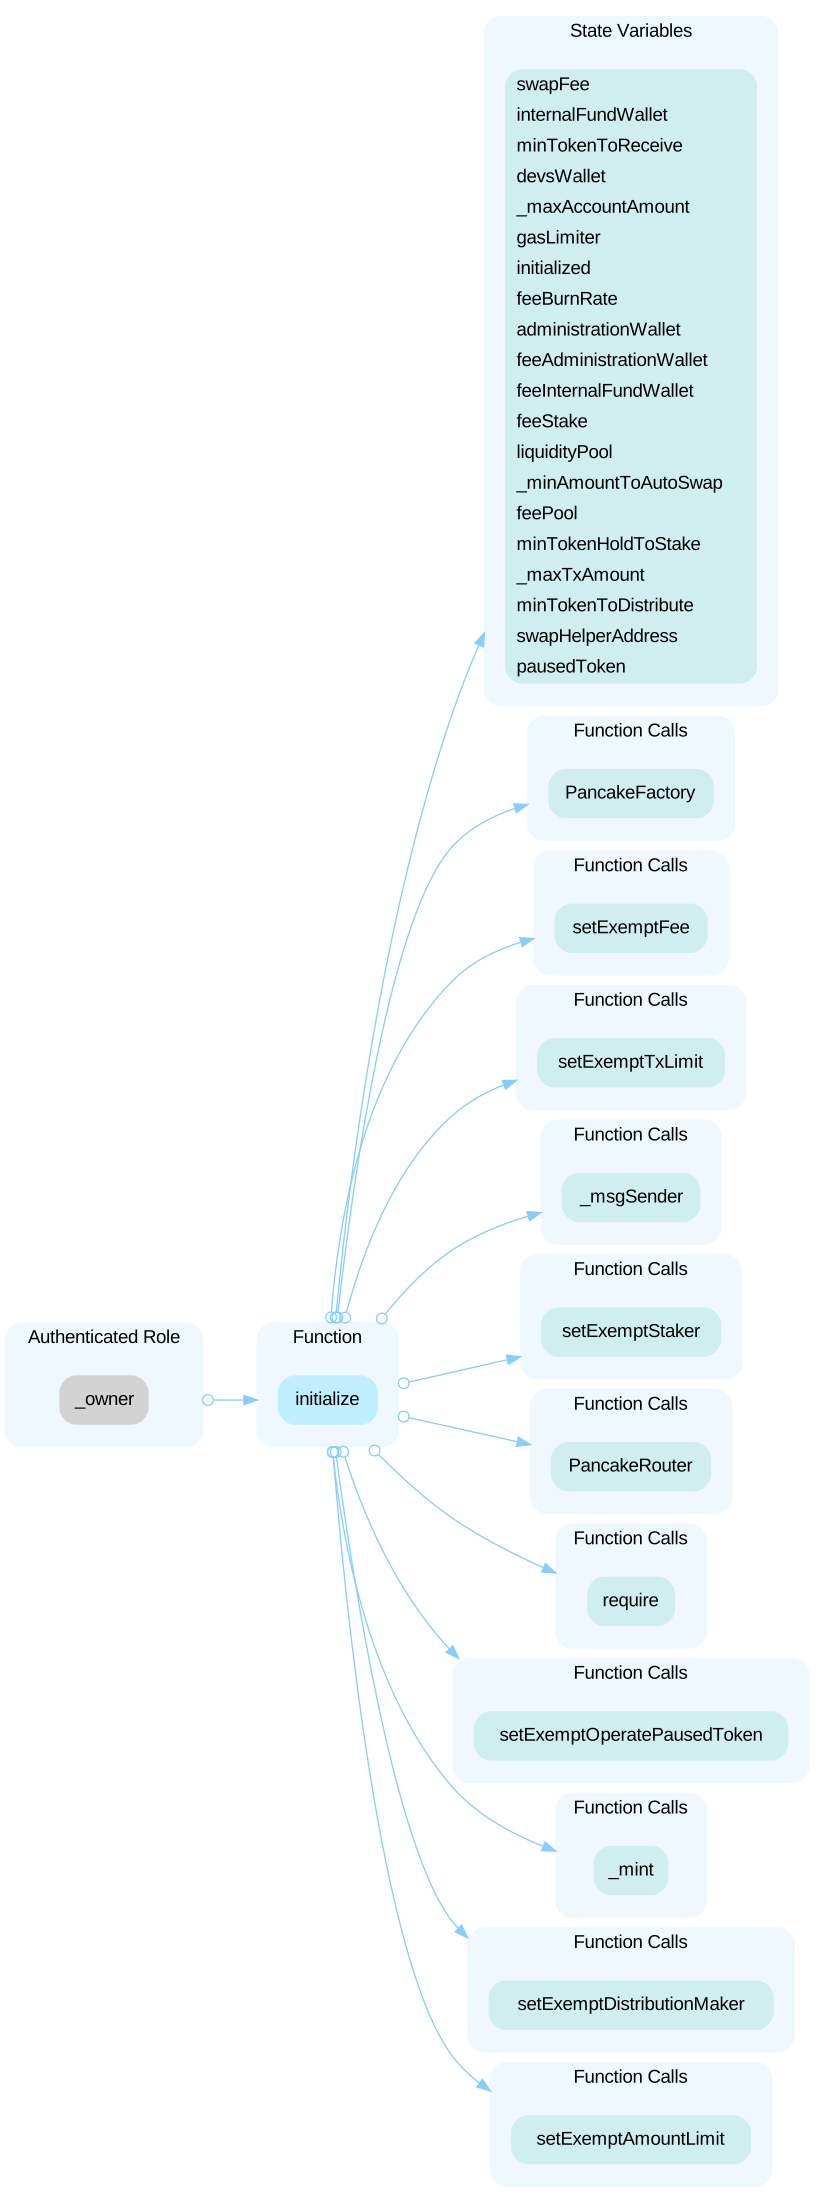
The audit on Trustblock · Open the reportAll of the [Ecoin] tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute [Ecoin] tokens without obtaining the consensus of the community.
The audit on Trustblock · Open the reportFunctions that affect the status of sensitive variables should emit events as notifications for the community.
The audit on Trustblock · Open the reportThe linked statements are reinitialized to the same value when `initialize()` is called. Therefore the linked statements in the `initialized()` function do not affect the functionality of the codebase.
The audit on Trustblock · Open the reportThe Ecoin Finance security record · Every Ecoin Finance address · This address on the explorer