Ecoin Finance
CertiK reviewed Ecoin Finance on 11 Nov 2022: 10 findings, 1 critical; 6 marked fixed, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings10
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 2 | 0 | 5 |
HighCentralization Risks in Ecoin.solOpen
In the contract `EcoinToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and implement a few attacks. We list the attacks below: 1. A compromised owner may first wipe the contract's ether balance by calling the function `safeWithdraw()`. 2. A hacker may pause the swapping mechanism and stake by calling the functions `setPausedSwapPool()` and `setPausedStake()`. 3. Set the minimum amount to swap to an inordinate amount. 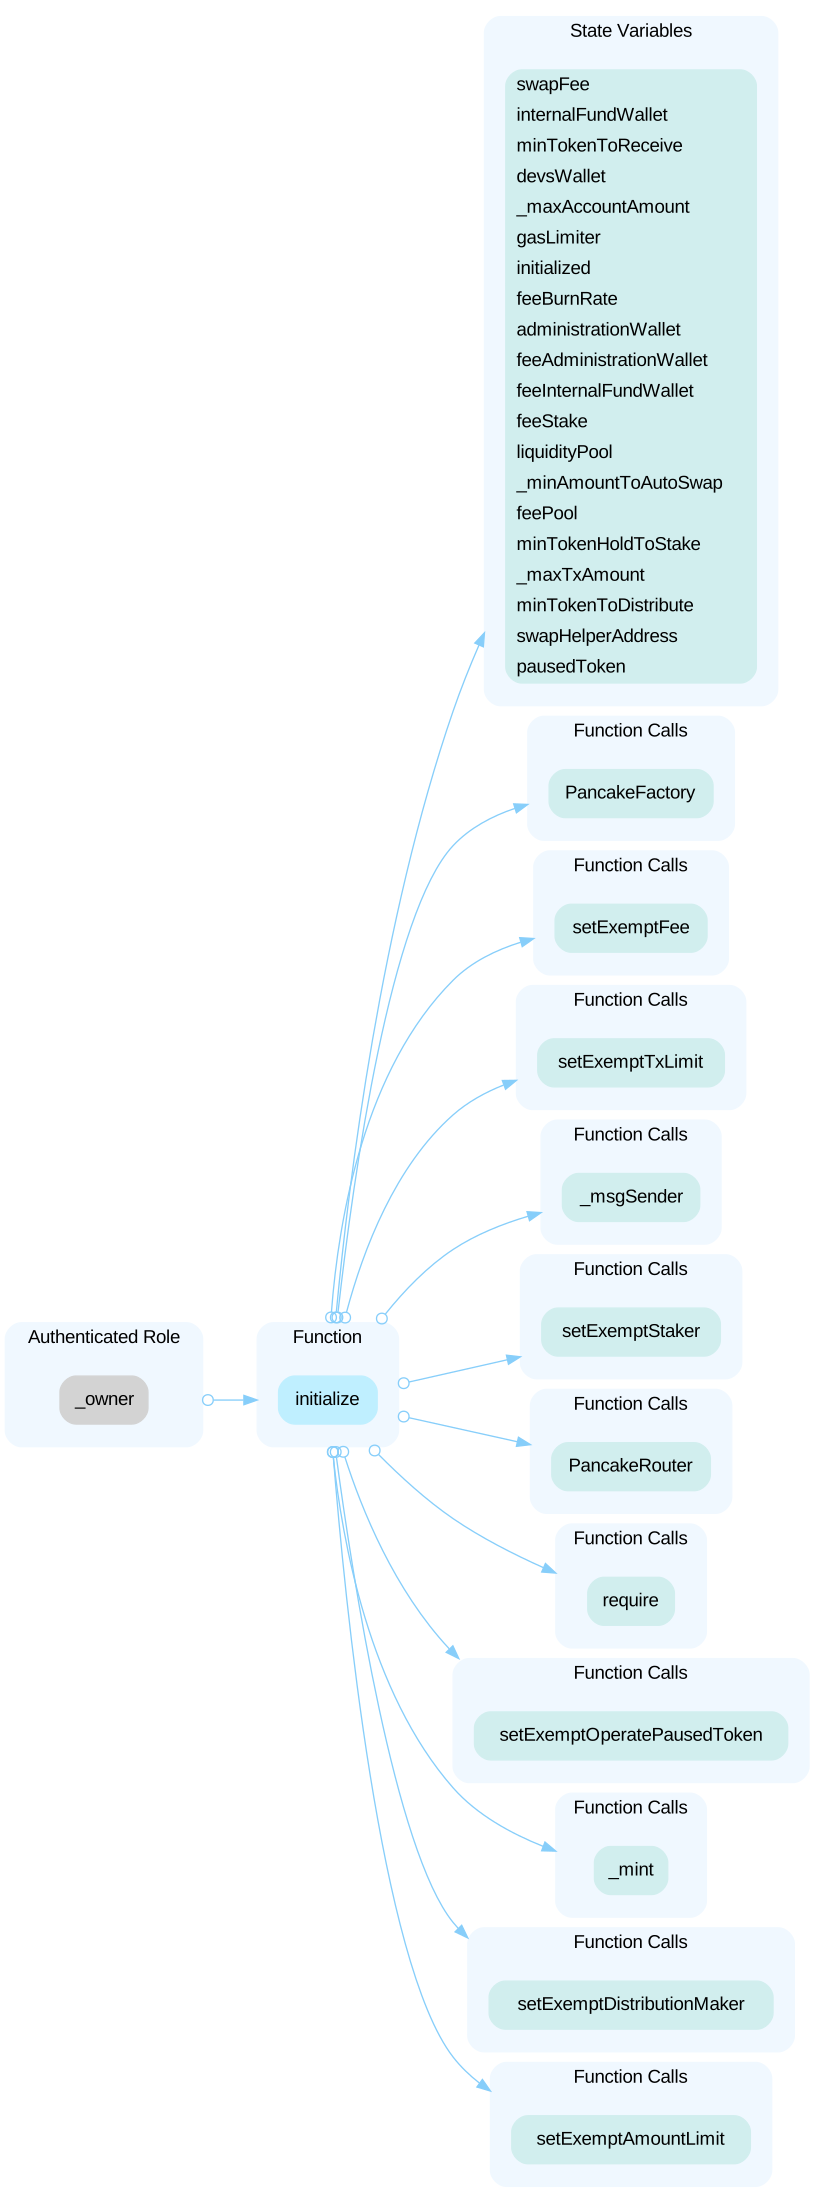
HighInitial Token DistributionOpen
All of the [Ecoin] tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute [Ecoin] tokens without obtaining the consensus of the community.
LowMissing Emit EventsOpen
Functions that affect the status of sensitive variables should emit events as notifications for the community.
LowRedundant StatementsOpen
The linked statements are reinitialized to the same value when `initialize()` is called. Therefore the linked statements in the `initialized()` function do not affect the functionality of the codebase.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x1617851311055b8c984b9949d1d3309275fcc6cb | Chain: BNB Chain | Source code: Verified source |
Part of Ecoin Finance’s security record
 Ecoin Finance
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us