0xa7ffb399d44eb830f01751052c75d14f0b47e779
As of 21 Nov 2026, Trustblock’s record holds 0xa7ffb399d44eb830f01751052c75d14f0b47e779 on BNB Chain as a contract of Grok X. 1 audit report on Trustblock lists this address: CertiK, 20 Dec 2023. 10 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Grok X - Audit | CertiK | Not recorded (see the report) | On Trustblock |
2 High, 8 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `GROKX` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to change the market address and send tokens in the contract to the contract owner. 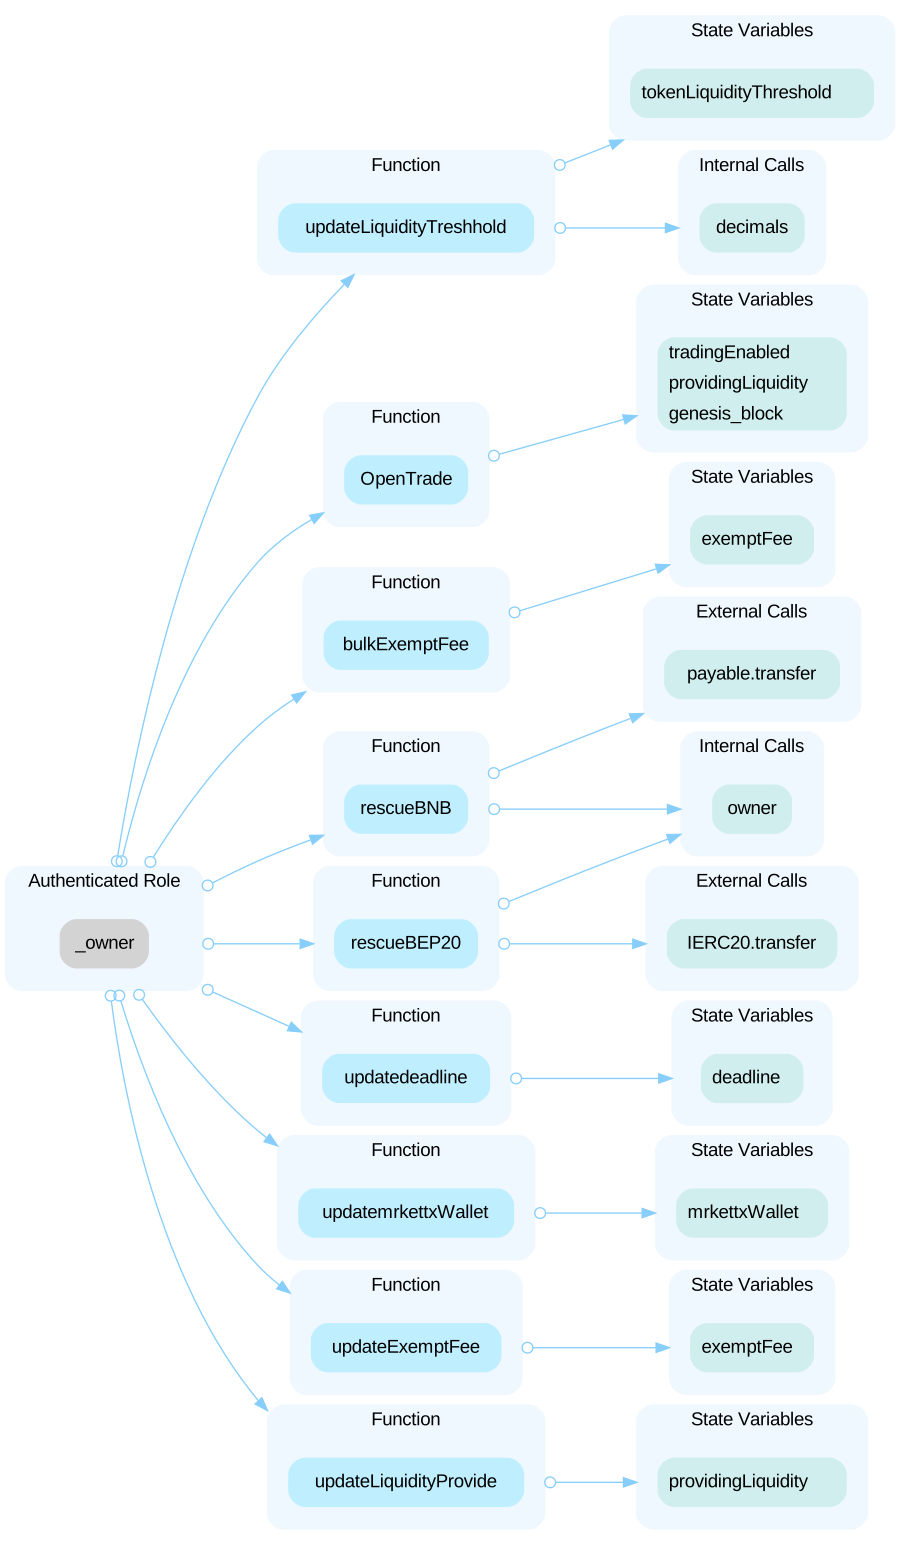 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to transfer ownership. 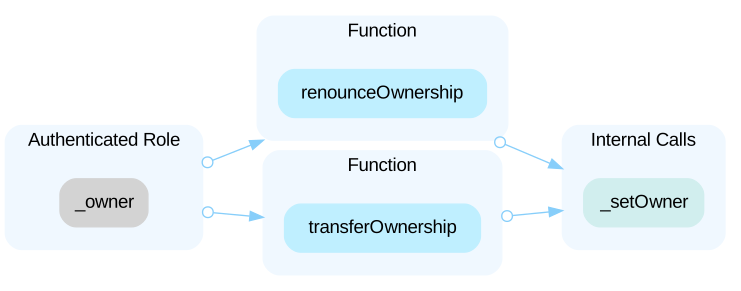
The audit on TrustblockAll of the `Grok X` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the anonymous deployer can distribute tokens without obtaining the consensus of the community. Any compromise to the deployer account that holds undistributed tokens may allow the attacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on TrustblockThe `_transfer()` function in the contract includes a fee charging mechanism. These fees are stored within the contract. Once the accumulated fees reach the `tokenLiquidityThreshold`, the main logic of the `Liquify` is triggered. At this point, the accumulated fees are distributed to both the liquidity pool and the market address based on the predetermined `swapTaxes`. The `swapTaxes` could be one of `taxes` and `sellTaxes`, which are initialized during deployment and remain unchanged thereafter. It is important to note that both the `liquidity` of taxes and sellTaxes are set to 0. This indicates that no tokens will be transferred to the liquidity pool, and instead, all the accumulated fees will be transferred to the market address. In addition, using the data from the latest transaction to determine the allocation of the accumulated fee is not suitable or appropriate. We would like to confirm with the team if it aligned with the original design.
The audit on TrustblockIf the `deadline` value is zero, the `useLaunchFee` variable will always be false because `block.number` is always greater than or equal to the `genesis_block`. The default value of `deadline` is zero and can only be modified before the `openTrade()` function is called. Even if a positive value is set for `deadline` and `useLaunchFee` is true, the fee will still be zero because the `launchTax` is also zero. Therefore, this mechanism is unable to effectively prevent bots from front-running. We would like to confirm with the team if it aligned with the original design.
The audit on TrustblockIt is expected that non-reverting invocations of `transfer(recipient, amount)` that return `true` and where the address in `recipient` equals the address of `msg.sender` (i.e. self-transfers) do not change the balance of address `msg.sender`. However, in `GROKX.transfer` the balance of address `msg.sender` is changed by executing a self-transfer.
The audit on TrustblockIt is expected that non-reverting invocations of `transferFrom(from, dest, amount)` that return `true` and where the address in `from` equals the address in `dest` (i.e. self-transfers) do not change the balance entry of the address in `from` (which equals `dest`). However, in `GROKX.transferFrom`, at least one balance entry of the addresses provided in the `from` or `dest` input parameters is changed when executing a self-transfer.
The audit on TrustblockThere are many hardcoded addresses in current contract. Please ensure these addresses are configured correctly when deploying.
The audit on TrustblockA sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (before the transaction being attacked) a transaction to purchase one of the assets and make profits by backrunning (after the transaction being attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - router.swapExactTokensForETHSupportingFeeOnTransferTokens - router.addLiquidityETH
The audit on TrustblockThe contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=444 IRouter public router; ``` - The contract `GROKX` interacts with third party contract with `IRouter` interface via `router`.
The audit on TrustblockThe return values of the `transfer()` and `transferFrom()` calls in the smart contract are not checked. Some ERC-20 tokens' transfer functions return no values, while others return a bool value, they should be handled with care. If a function returns `false` instead of reverting upon failure, an unchecked failed transfer could be mistakenly considered successful in the contract. ```solidity=723 IERC20(tokenAdd).transfer(owner(), amount); ```
The audit on TrustblockThe Grok X security record · Every Grok X address · This address on the explorer