0xee5b03b769ca6c690d140cafb52fc8de3f38fc28
As of 21 Nov 2026, Trustblock’s record holds 0xee5b03b769ca6c690d140cafb52fc8de3f38fc28 on BNB Chain as a contract of Hyperchain X. 1 audit report on Trustblock lists this address: CertiK, 9 Mar 2023. 11 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on BNB Chain.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| HyperChainX-Audit | CertiK | Not recorded (see the report) | Open |
2 High, 9 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `HYPERCHAIN` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 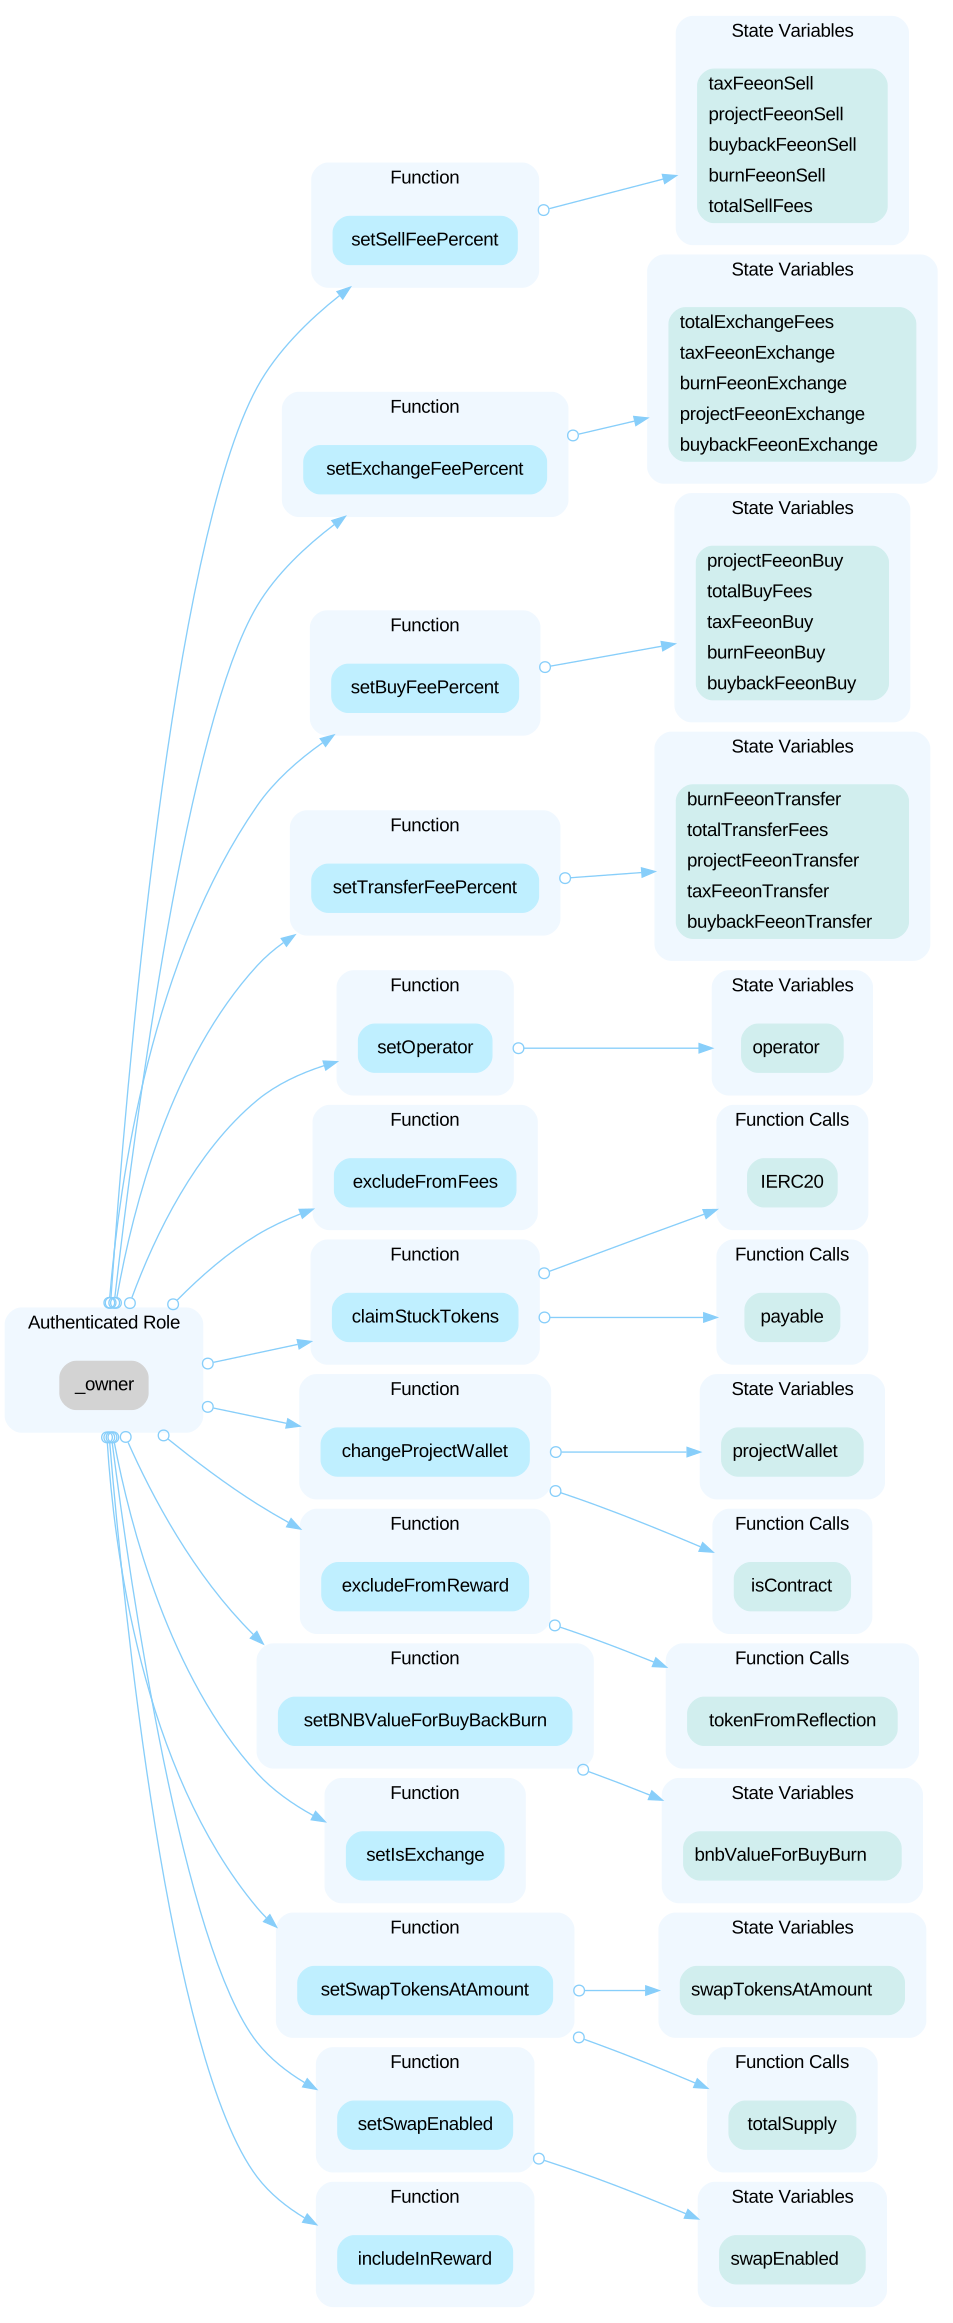 In the contract `HYPERCHAIN` the role `operator` has authority over the functions shown in the diagram below. Any compromise to the `operator` account may allow the hacker to take advantage of this authority. 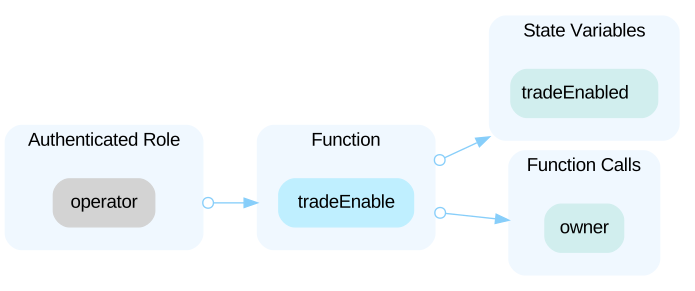 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 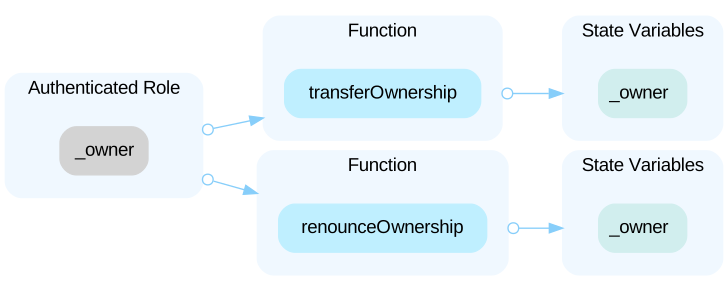
The audit on Trustblock · Open the reportAll of the `HYPER` tokens are sent to the `operator` when deploying the contract. This could be a centralization risk as the `operator` can distribute tokens without obtaining the consensus of the community. Since the privilege of the `operator`, it is possible of being maliciously manipulated by hackers if the account of the owner was compromised.
The audit on Trustblock · Open the reportThe `isContract` check cannot cover all scenarios. The check can be bypassed if the call is from the constructor of a contract or when the contract is destroyed. In that case, `isContract` will return `false` because its `codesize` will be zero. The comment in the `isContract` implementation from the OpenZeppelin library also says that "it is unsafe to assume that an address for which this function returns false is an externally-owned account (EOA) and not a contract." - Reference: https://github.com/OpenZeppelin/openzeppelin-contracts/blob/3dac7bbed7b4c0dbf504180c33e8ed8e350b93eb/contracts/utils/Address.sol ```solidity=935 require(!isContract(newProjectWallet), "Cannot be contract address"); ```
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportAddresses should be checked before assignment or external call to make sure they are not zero addresses. ```solidity=394 operator = _operator; ``` - `_operator` is not zero-checked before being used.
The audit on Trustblock · Open the reportA sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (before the transaction is attacked) a transaction to purchase one of the assets and make profits by back running (after the transaction is attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `uniswapV2Router.swapExactTokensForETHSupportingFeeOnTransferTokens()` - `uniswapV2Router.swapExactETHForTokensSupportingFeeOnTransferTokens()`
The audit on Trustblock · Open the reportThe condition `!_isExcluded[sender] && !_isExcluded[recipient]` can be included in `else` .
The audit on Trustblock · Open the reportState variables that never change should be declared as `constant` to save gas. ```solidity=275 string private _name = "HYPERCHAIN"; ``` - `_name` should be declared `constant`. --- ```solidity=276 string private _symbol = "HYPER"; ``` - `_symbol` should be declared `constant`. --- ```solidity=277 uint8 private _decimals = 7; ``` - `_decimals` should be declared `constant`.
The audit on Trustblock · Open the reportThe return value of the transfer()/transferFrom() call is not checked. ```solidity=514 ERC20token.transfer(msg.sender, balance); ```
The audit on Trustblock · Open the reportVariable `_rOwned[account]` is not updated in the function `includeInReward()`, which will make the accounts included siphon off the tokens out of the balances of all token holders. The Rate was higher at the moment of the `excludeFromReward(account)` call, so the `_rOwned[account] / _tOwned[account]` ratio is bigger than expected for accounts included in the reward. ```solidity=491 function includeInReward(address account) external onlyOwner() { require(_isExcluded[account], "Account is already included"); for (uint256 i = 0; i < _excluded.length; i++) { if (_excluded[i] == account) { _excluded[i] = _excluded[_excluded.length - 1]; _tOwned[account] = 0; _isExcluded[account] = false; _excluded.pop(); break; } } } ```
The audit on Trustblock · Open the reportThe linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
The audit on Trustblock · Open the reportThe Hyperchain X security record · Every Hyperchain X address · This address on the explorer