0x0e933b304c9585b35546fe0ae6d0b01a72f0fdcf
As of 21 Nov 2026, Trustblock’s record holds 0x0e933b304c9585b35546fe0ae6d0b01a72f0fdcf on Ethereum as a contract of DeepLink. 1 audit report on Trustblock lists this address: CertiK, 26 Sep 2024. 6 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
2 High, 4 Low. In the firm’s own words; statuses are the firm’s, from each report.
**Address 0xD610Be30b06A3828A27D608a38F1E85faAFdEDcC:** In the contract `DeepLink`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and claim stuck tokens to owner, update wallet lock block, disable the lock permanently, transfer and lock tokens. 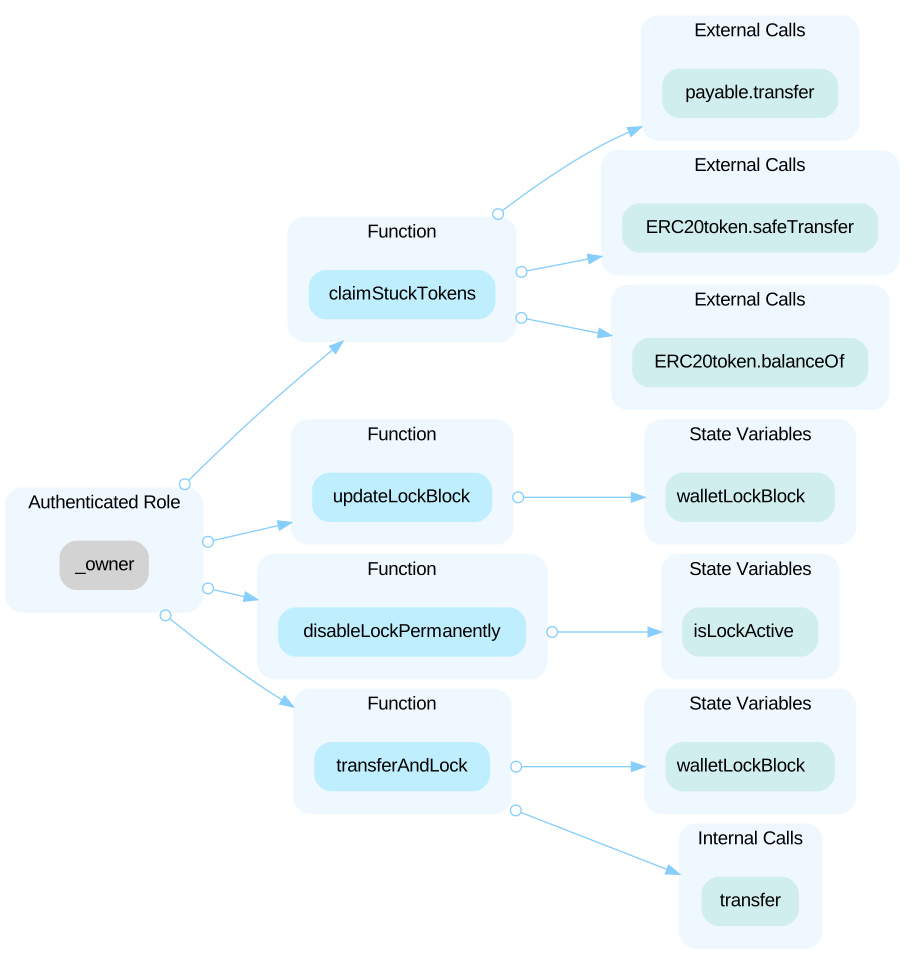 In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership, renounce ownership. 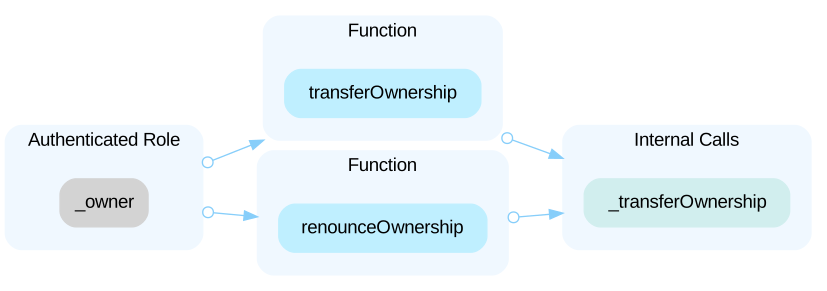 ----- **Address 0x0e933b304C9585B35546FE0aE6D0B01A72f0FdCF:** In the contract `DeepLink` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and enable trading, enable/disable addresses from transferring tokens before trading enabled. 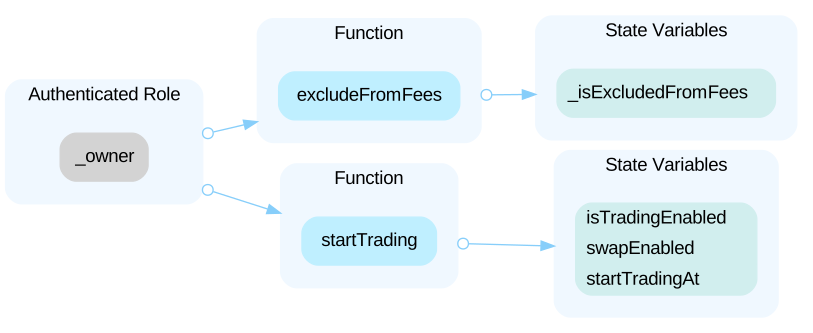 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership, renounce ownership. 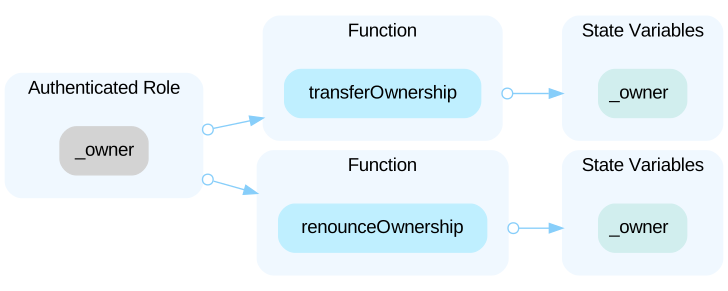
The audit on Trustblock · Open the reportAll of the DLC tokens are sent to the corresponding contract owner. This is a centralization risk because the owners can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportThe contract has a `receive()` function or payable functions, making it able to receive native tokens. However, it does not have a function to withdraw the funds, which can lead to permanently locked tokens within the contract. ```solidity=675 receive() external payable {} ```
The audit on Trustblock · Open the reportState variables that never change should be declared as `constant` to save gas. ```solidity=640 address private DEAD = 0x000000000000000000000000000000000000dEaD; ``` - `DEAD` should be declared `constant`.
The audit on Trustblock · Open the reportIt is not recommended to use Solidity's `transfer()` and `send()` functions for transferring native tokens, since some contracts may not be able to receive the funds. Those functions forward only a fixed amount of gas (2300 specifically) and the receiving contracts may run out of gas before finishing the transfer. Also, EVM instructions' gas costs may increase in the future. Thus, some contracts that can receive now may stop working in the future due to the gas limitation. ```solidity=769 payable(msg.sender).transfer(address(this).balance); ``` - `DeepLink.claimStuckTokens` uses `transfer()`.
The audit on Trustblock · Open the reportThe linked variable assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
The audit on Trustblock · Open the reportThe DeepLink security record · Every DeepLink address · This address on the explorer